When Microsoft Teams Becomes The Initial Access Vector: Detecting RMM-Based Intrusions
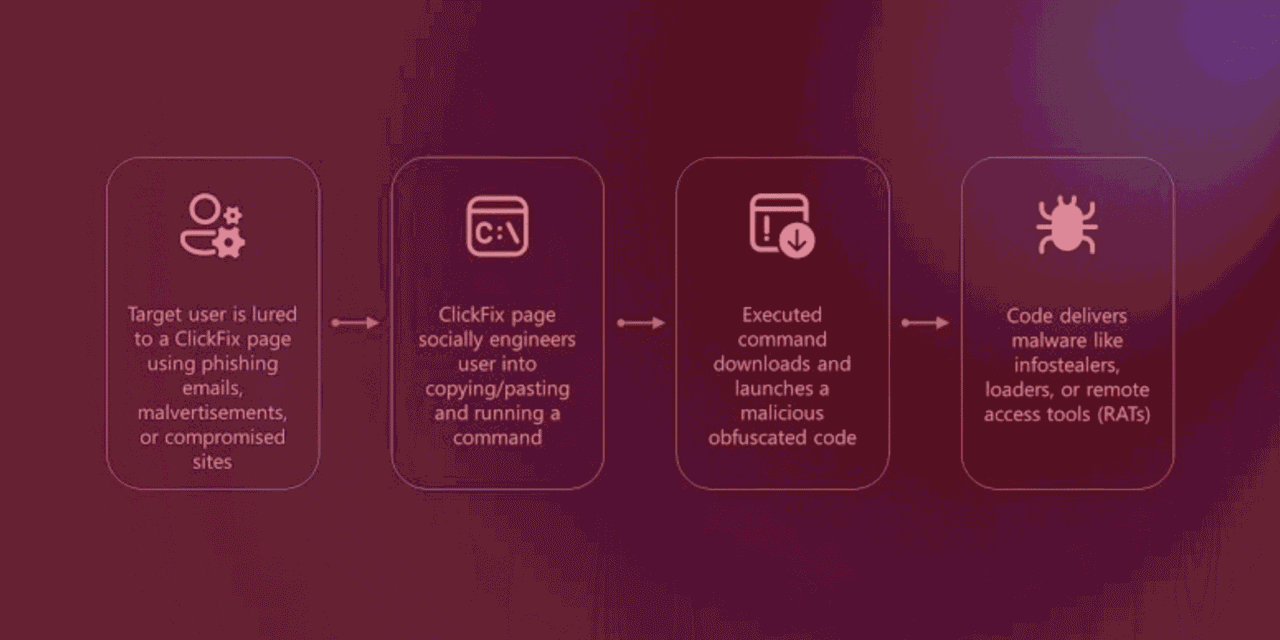
ClickFix tricks users into running malicious commands via Windows Terminal. See how to detect the execution chain using KQL in Defender XDR.
Learn how correlating Microsoft Teams chats with RMM activity detects social engineering attacks used to gain remote endpoint access.
See how behavioral scoring detects suspicious PowerShell commands, catching obfuscation and encoding that static indicators miss.