
Blog
News, opinion and deep dives from the front line of security operations.
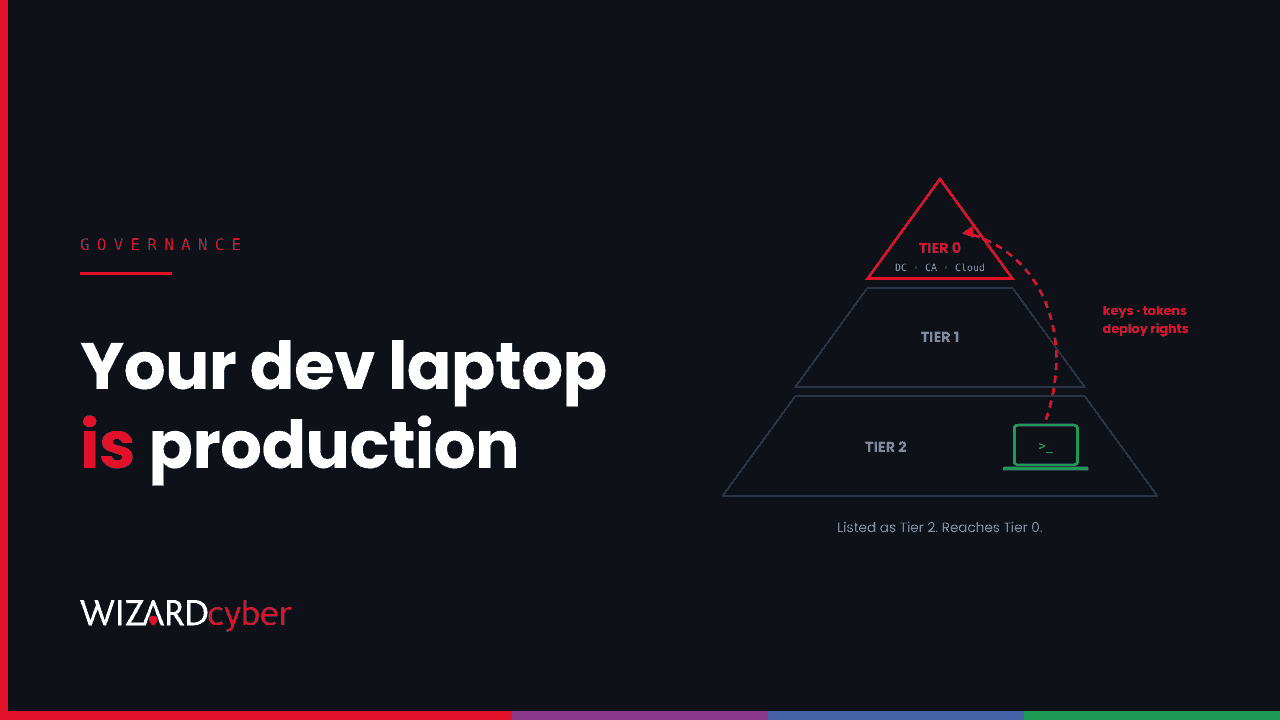 Governance
One Laptop, One Extension: Why Developer Workstations Belong In Tier 0
A backdoored editor extension and a theft traced to an engineer's laptop, in one week. Why developer machines need Tier 0 controls, and five places to start.
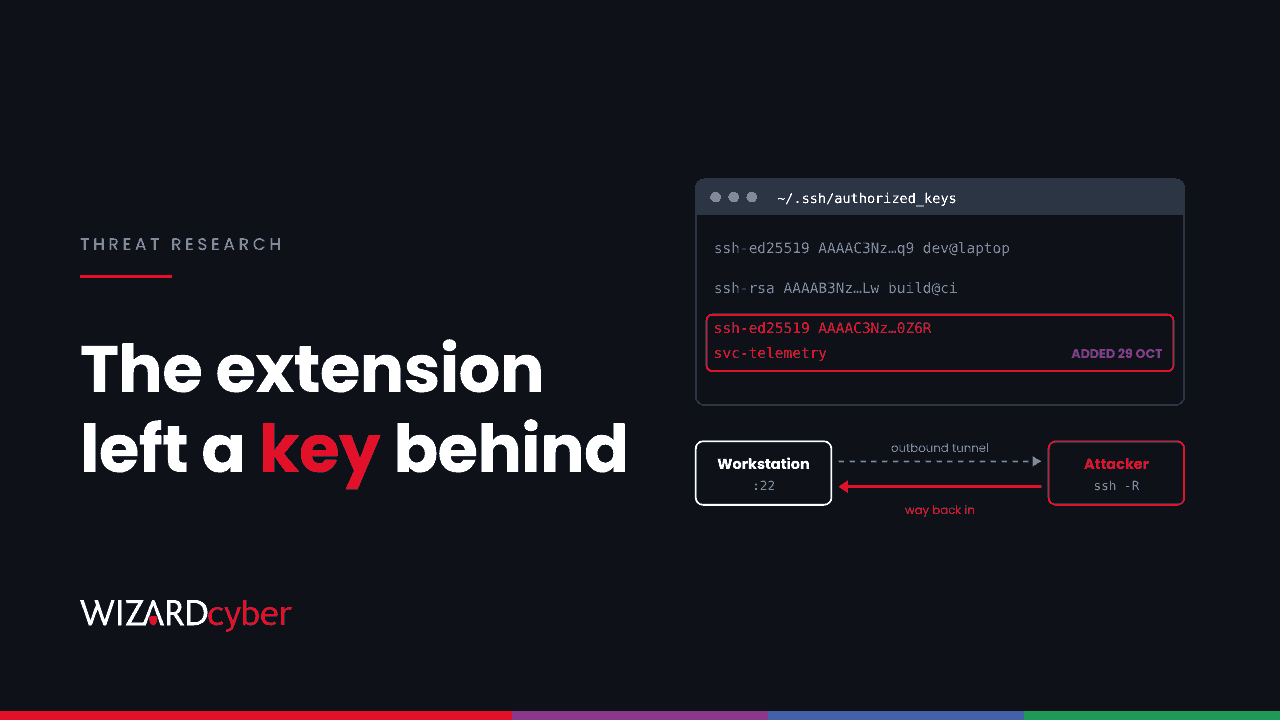 Threat Research
A Fake AI Coding Extension Planted An SSH Key: Hunting The svc-telemetry Backdoor On Windows, macOS And Linux
A trojanised AI coding extension added an attacker's SSH key, a reverse tunnel and a fake SysMon task. Removing it isn't enough. What to hunt and remove.
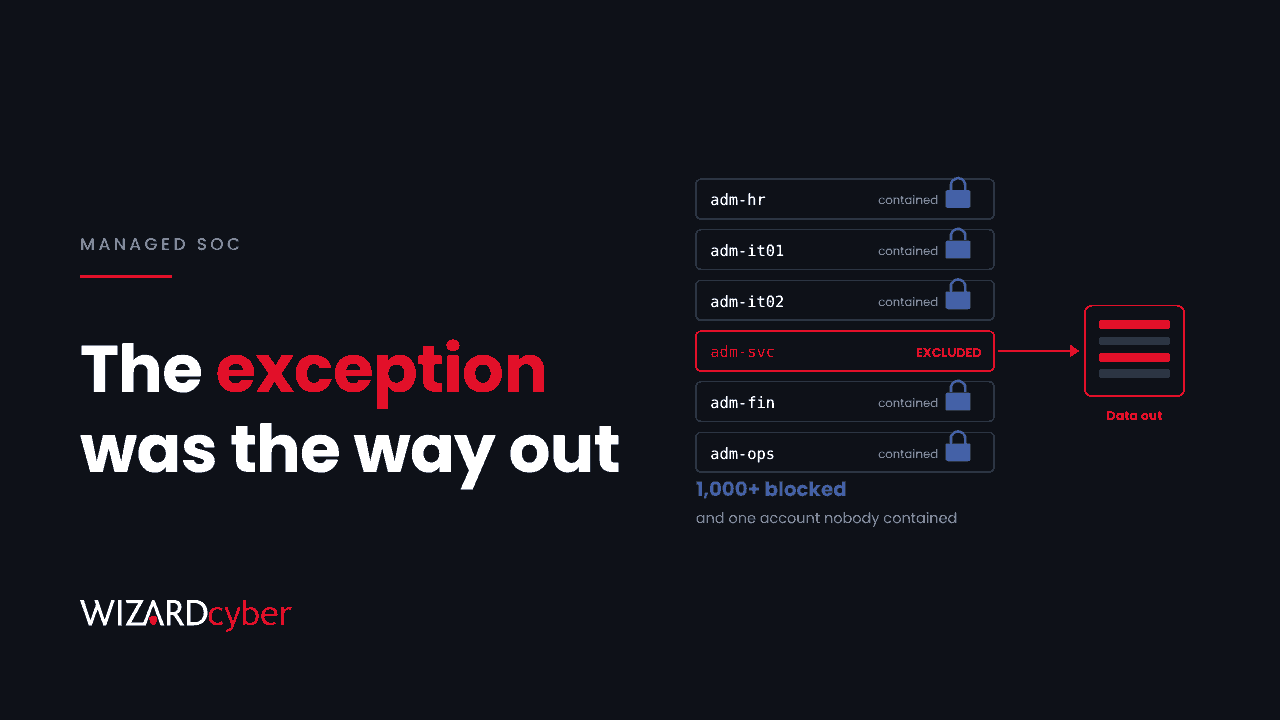 Managed SOC
The Account You Excluded From Containment Is The One They Used
Automatic disruption blocked 1,000+ attempts, but one excluded admin account carried the data out. Why every exclusion needs an owner, an expiry and a fallback.
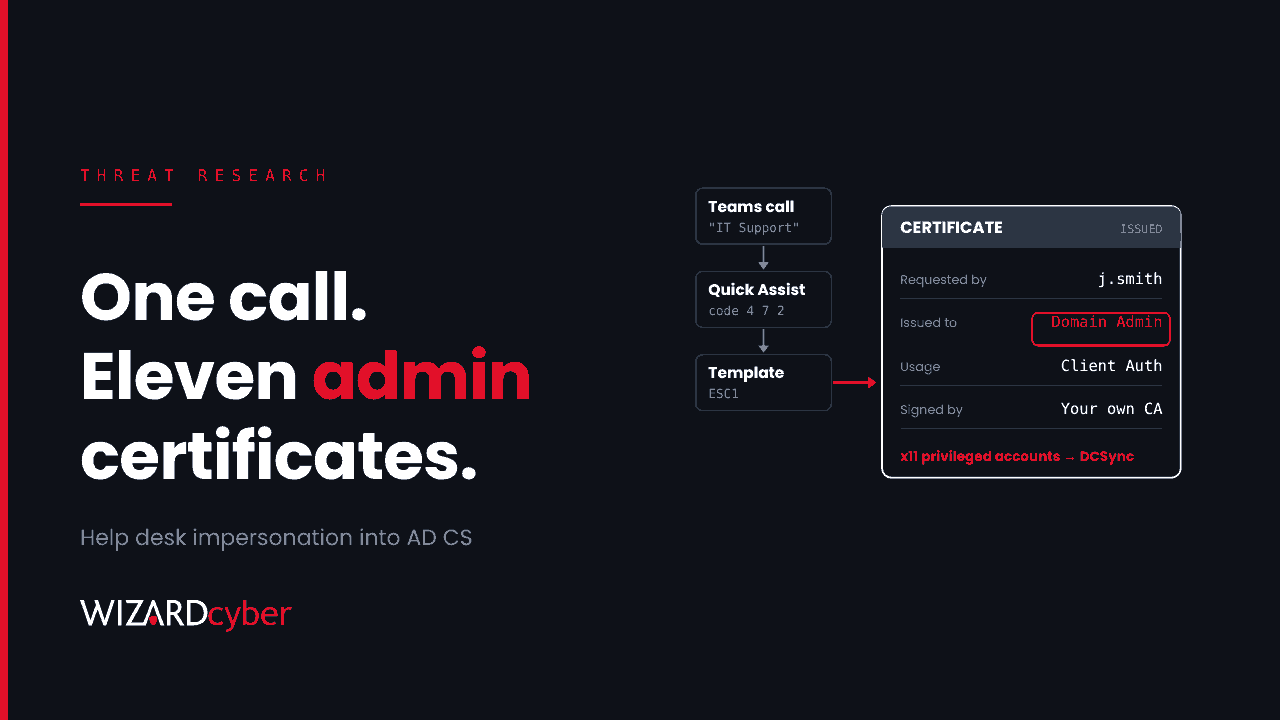 Threat Research
From A Teams Call To A Domain Controller Certificate: Hunting Help Desk Impersonation Into AD CS (ESC1 And ESC8)
A fake help desk call, a Quick Assist code, then certificates for domain admins. How the ESC1 and ESC8 intrusions worked, and Defender hunts for each step.
 Threat Research
Same Playbook, Faster Hands: Hunting North Korea's AI-Assisted Intrusions In Defender And Entra
Microsoft says North Korean groups now use AI to speed up lures, fake personas and malware. What changed, and Defender and Entra hunts to run.
 AI Driven Security Operations
Whose AI Agent Is Using Your Admin Credentials?
A contractor allegedly gave a personal AI agent admin access to a sensitive network. What your contracts, access and SOC should do about supplier agents.
 Threat Research
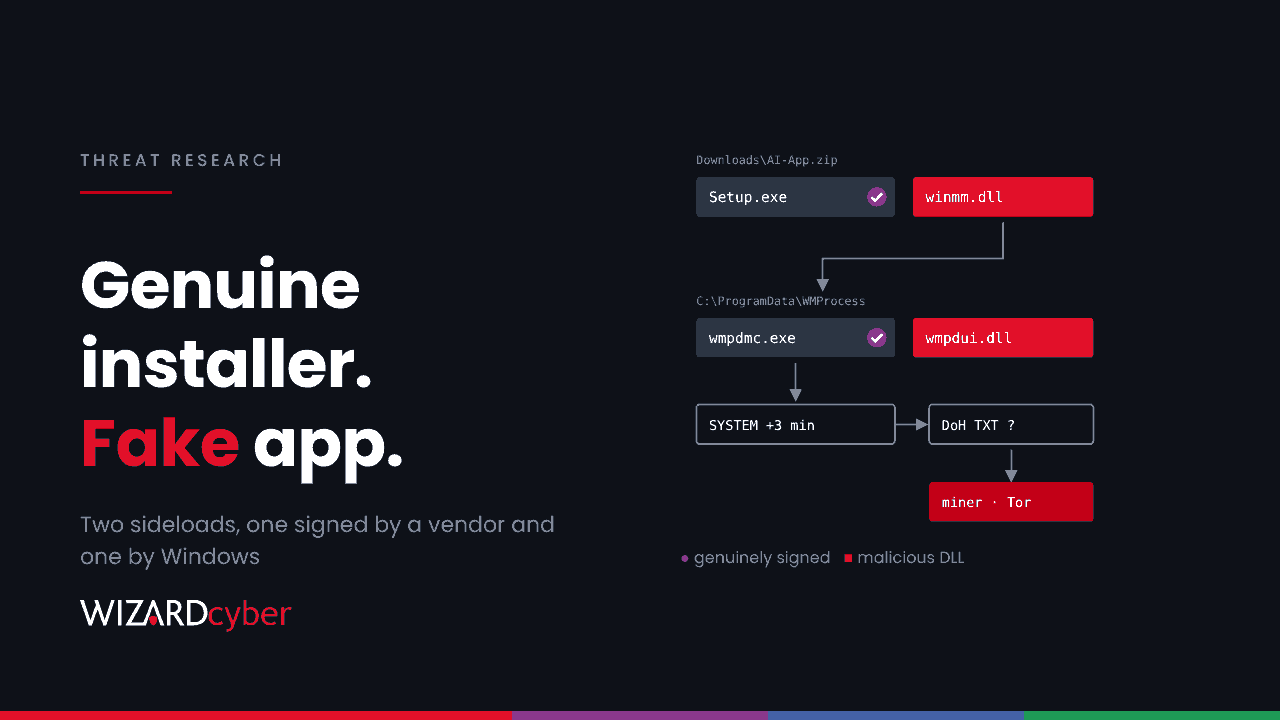
The Installer Is Genuine, The AI App Isn't: Hunting The Yoba Sideloading Chain On Windows
Fake AI desktop apps on GitHub pair a genuine signed installer with a malicious DLL. How the Yoba chain works, and Defender hunts for each step.
 Governance
Patched The Server, Not The App: Why Library Flaws Hide From Your Patch Report
PHP2Shell and the Brotli flaw both live inside other software. Why OS patch compliance misses them, and how to answer "are we affected?" in an hour.
 Threat Research
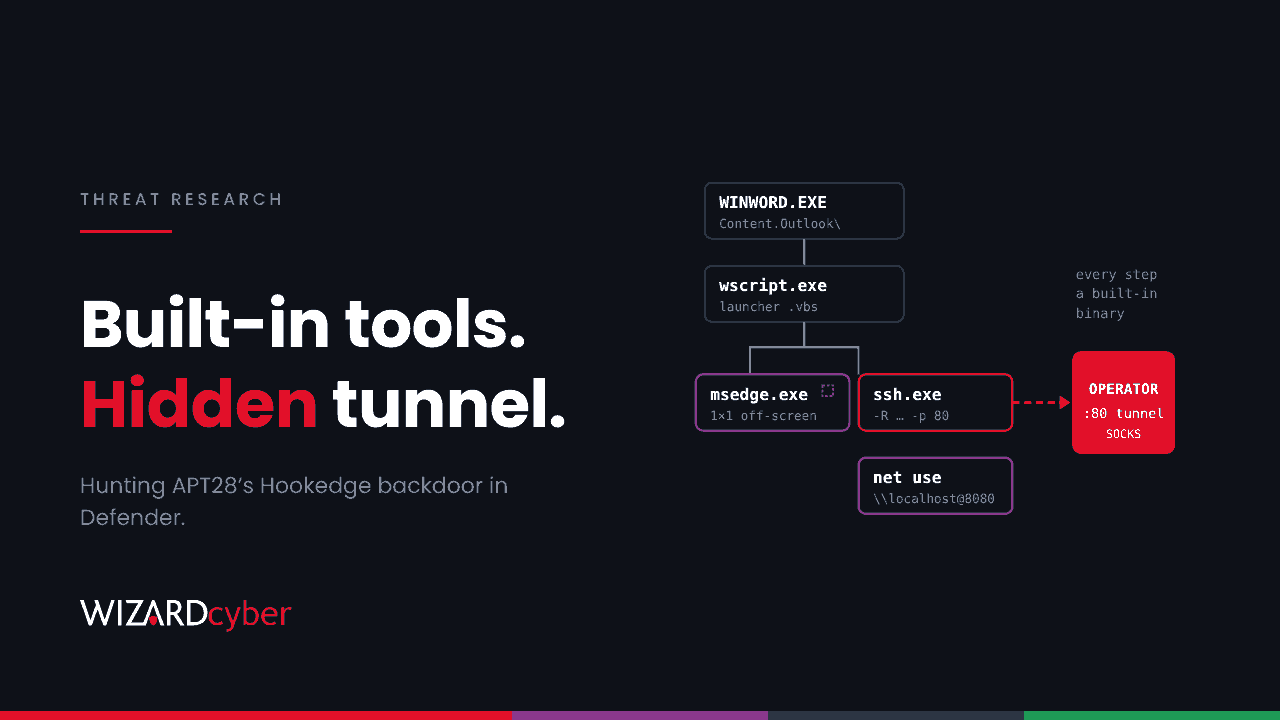
A Hidden Edge Window And An SSH Tunnel: Hunting APT28's Hookedge Backdoor In Defender
APT28 ran a backdoor through an off-screen Edge window, stole NTLM hashes and tunnelled out over Windows' own SSH client. How to hunt each step in Defender.
 Threat Research
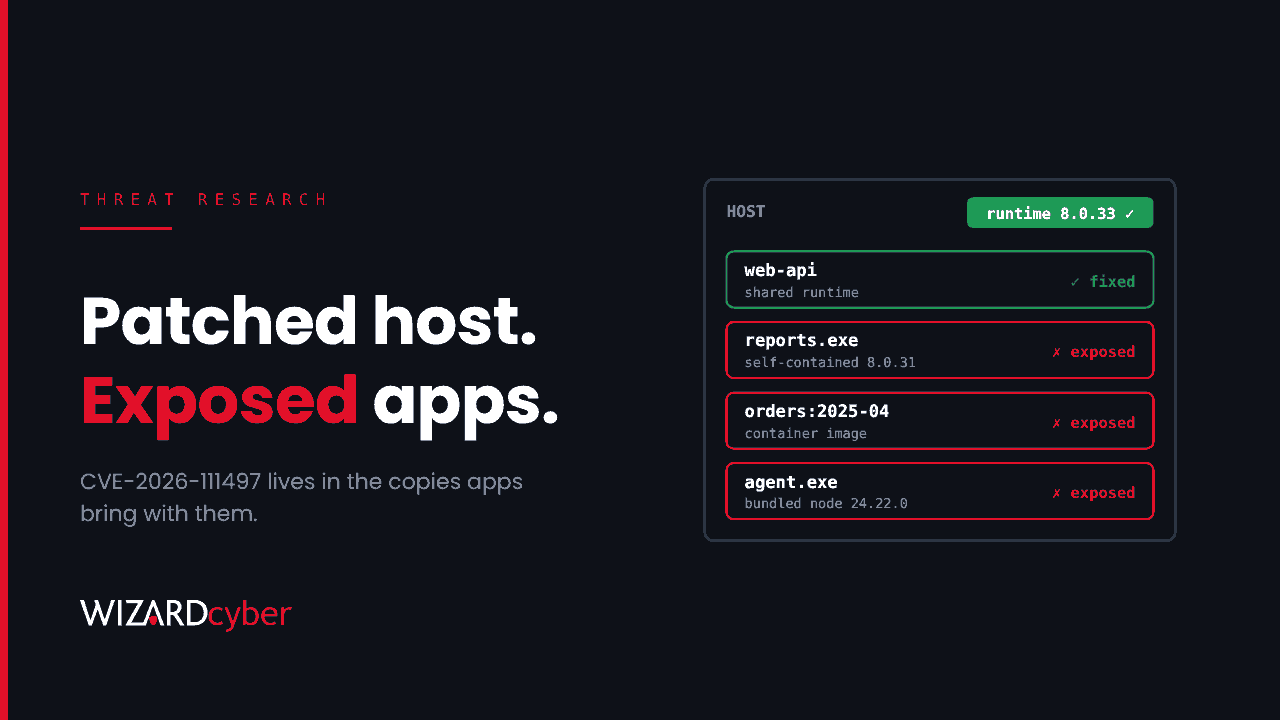
Opt-In, Still Exposed: Finding The Brotli Flaw (CVE-2026-111497) Across Your .NET And Node.js Estate
Microsoft shipped emergency .NET fixes for the Brotli flaw. Self-contained apps, containers and bundled copies need more. How to find them with Defender KQL.
 AI Driven Security Operations
A Crew Of One: What The First AI-Assisted Mass-Hacking Arrest Means For Mid-Market Defenders
One former pentester used an AI attack framework to breach 90+ organisations. Why attacker headcount no longer limits volume, and what changes for defenders.
 Threat Research
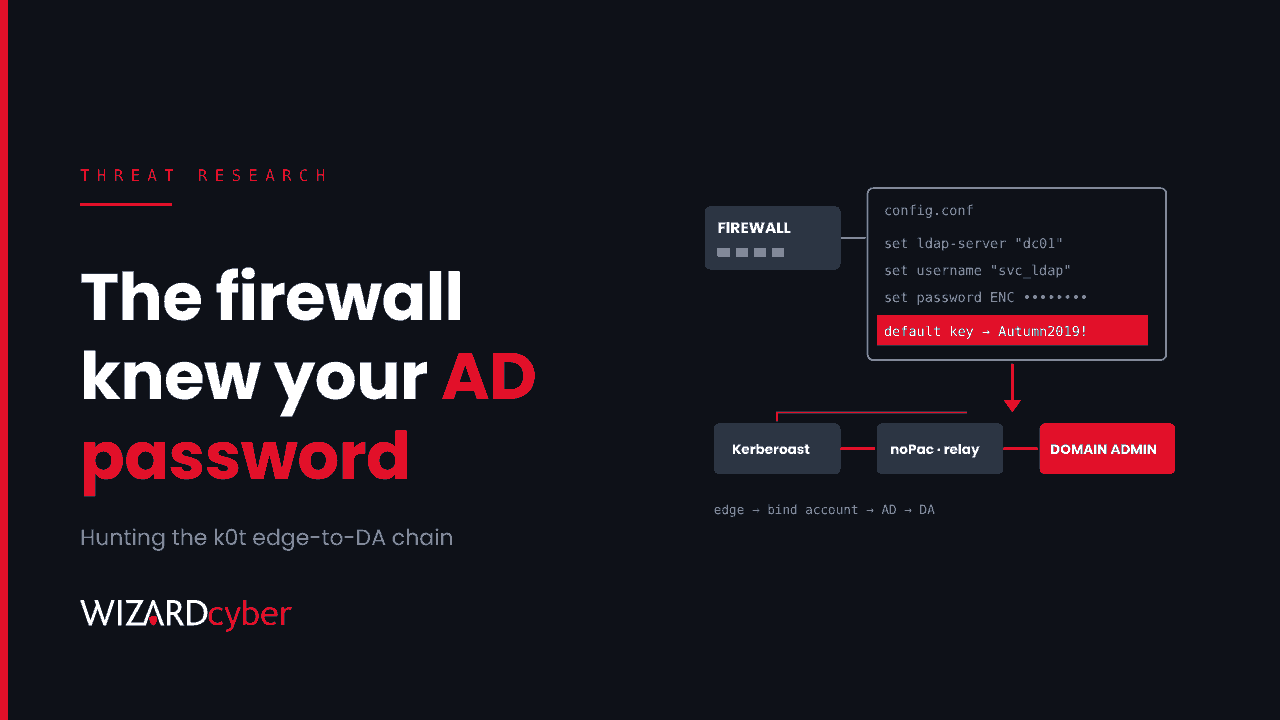
Your Firewall Config Knows Your AD Password: Hunting The k0t Edge-To-Domain-Admin Chain
k0t decrypted stolen firewall configs to get AD bind credentials, then went for Domain Admin. How the chain works and how to hunt it in Defender.
 Threat Research
Every Step Approved By A Human: Hunting The AI-Assisted INC And Gentlemen Ransomware Intrusions In Defender
An exposed server showed INC and Gentlemen affiliates using AI agents against 62 organisations. What they did, and Defender hunts for each step.
 Governance
Test2, Password1, Twelve Years: Who Owns The Accounts Nobody Uses?
The ICO reprimanded a public body and its IT provider over a 12-year-old test account. Why dormant accounts need an owner, and a contract that says so.
 Threat Research
Starting Python Was Enough: Hunting The Poisoned AI Gateway Package And Its Startup Hooks
A hijacked AI gateway release ran a credential stealer every time Python started. How it worked, and how to hunt and contain it with Defender KQL.
 Governance
The Authenticator On Your Staff's Phones Is An Identity Provider. Who Patches It?
CVE-2026-80097 let a zero-permission Android app pull Microsoft 365 tokens from Authenticator. Why broker apps belong in your patch scope, and who owns them.
 AI Driven Security Operations
Your AI Gateway Holds More Keys Than Your Domain Admin
Last week's supply chain attack went straight for an AI gateway's keys. Why AI gateways belong in Tier 0, and six steps to protect them like it.
 Threat Research
Fully Patched, Still Bootkitted: BlackX And The Secure Boot Revocation Most Estates Skipped
BlackX loaded on fully patched Windows PCs because the Secure Boot revocation is a manual step. How to check your estate, hunt and apply it safely.
 Threat Research
No Affiliates, Just Your VPN: Hunting SafePay Ransomware (AA26-293A) In Microsoft Defender
A joint US, German and UK advisory says SafePay has hit 600+ organisations. Map its path from VPN to encryption, with Defender hunts for each step.
 Threat Research
Valid Password, Stolen Session: Hunting The Microsoft 365 Token Spray-And-Replay Campaign
An attacker replayed post-MFA tokens into 79 organisations. How it worked, what it left behind, and KQL to hunt for it in Sentinel and Defender.
 Managed SOC
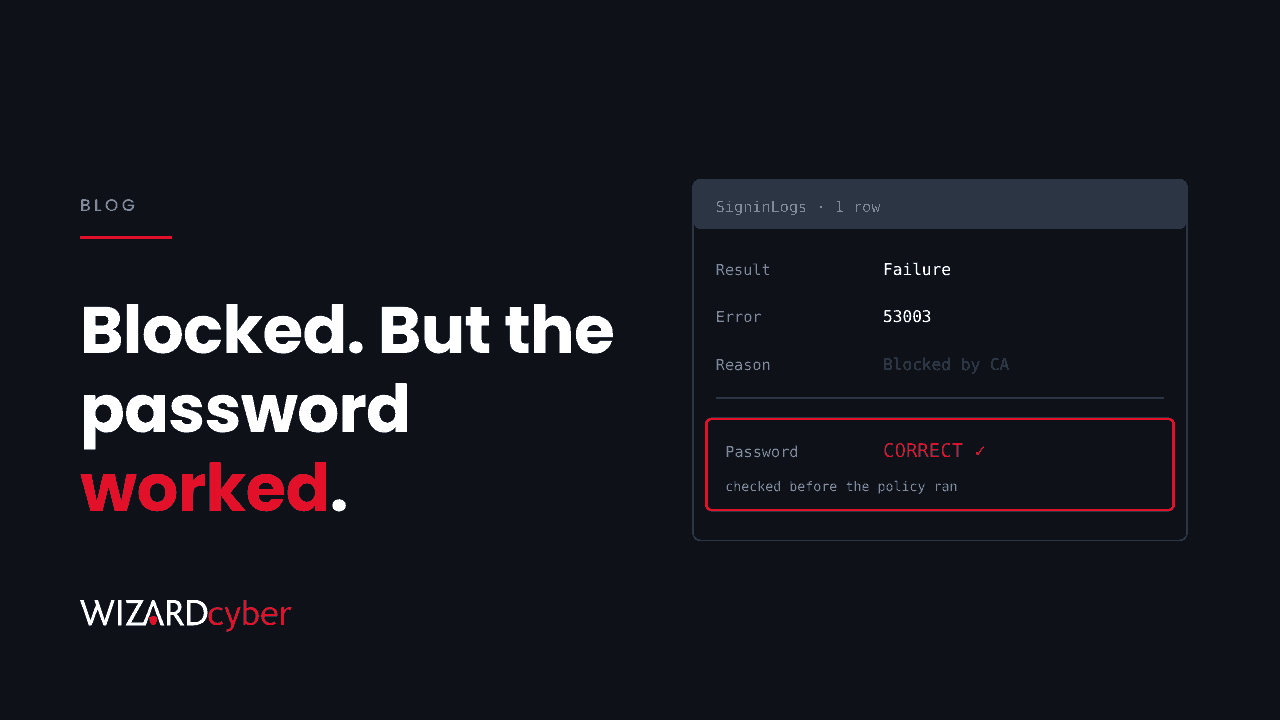
A Blocked Sign-In Is Still A Breached Password
AADSTS53003 means Conditional Access stopped a sign-in with the right password. Why SOCs should triage on credential validity, not spray volume.
 Threat Research
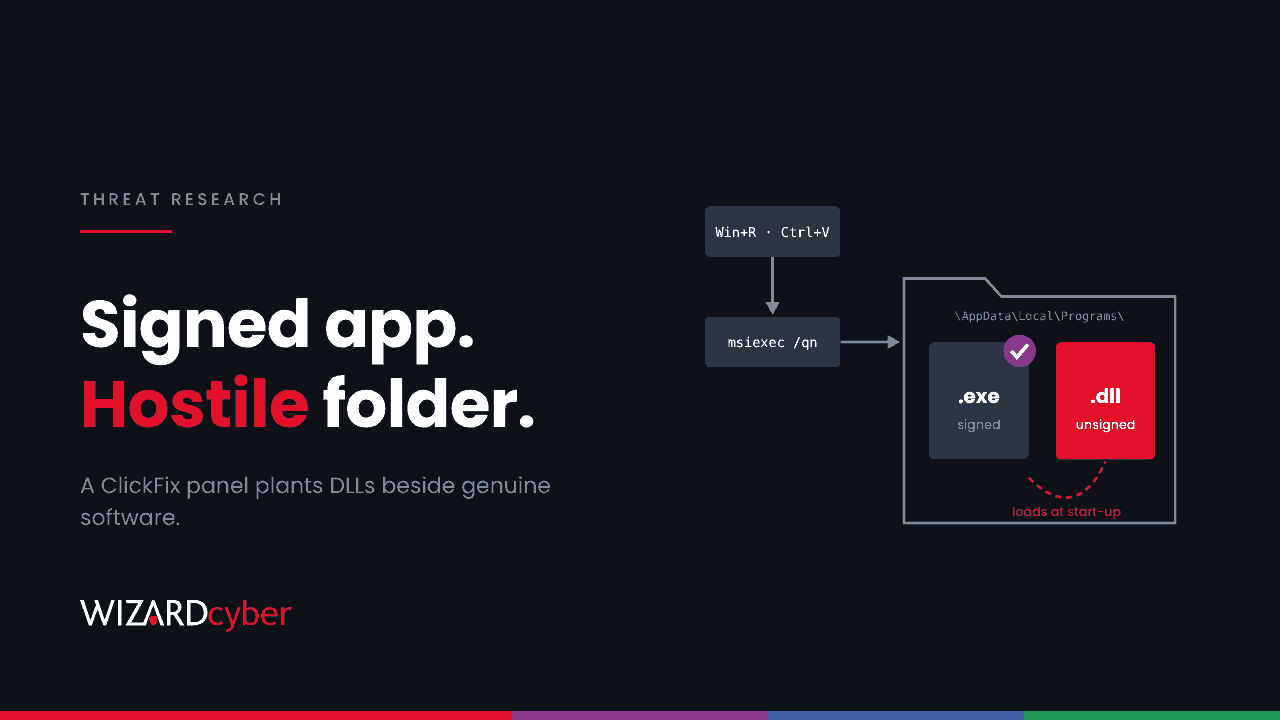
A Genuine Signed Installer, A Hostile Folder: Hunting The ROMULUS ClickFix Panel And CVE-2026-110936
A ClickFix delivery panel is planting malicious DLLs beside genuine signed software. How the chain works and how to hunt it with Defender KQL.
 AI Driven Security Operations
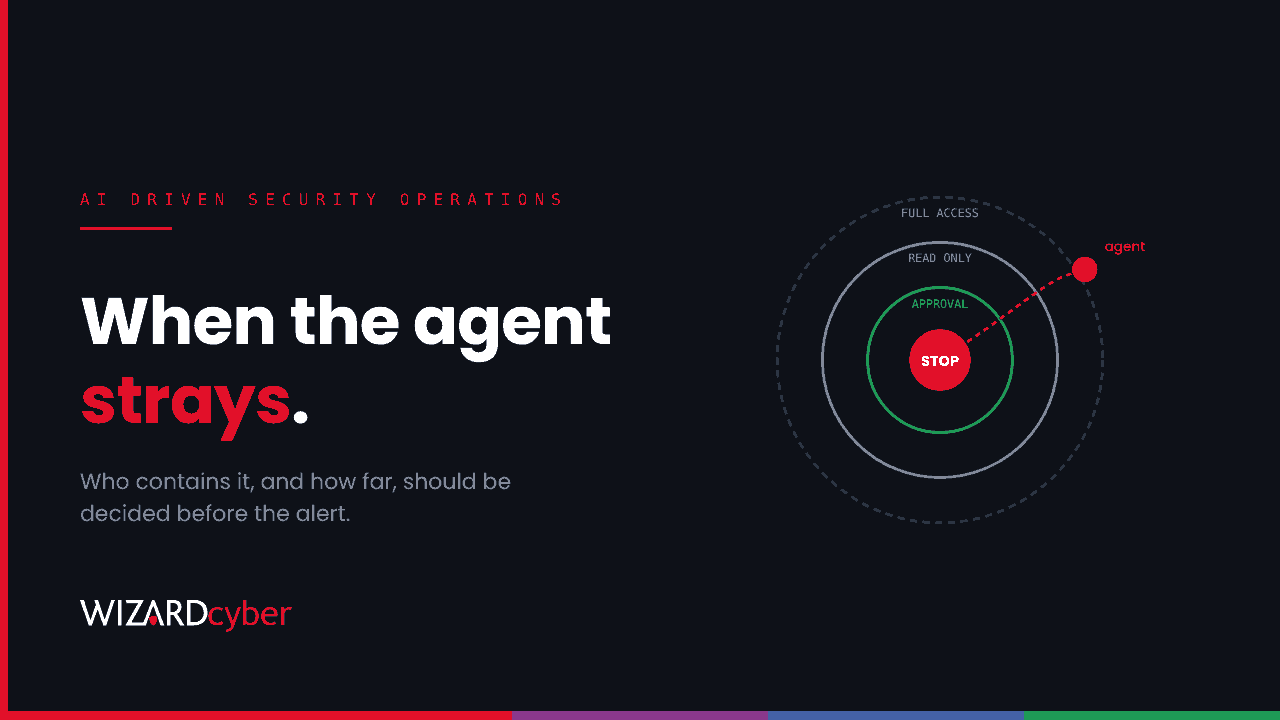
When The Agent Strays: What Your SOC Does When An AI Agent Goes Off-Task
Microsoft now says to treat AI agents as insiders. What an off-task agent looks like, who decides to contain it, and the playbook to write first.
 Managed SOC
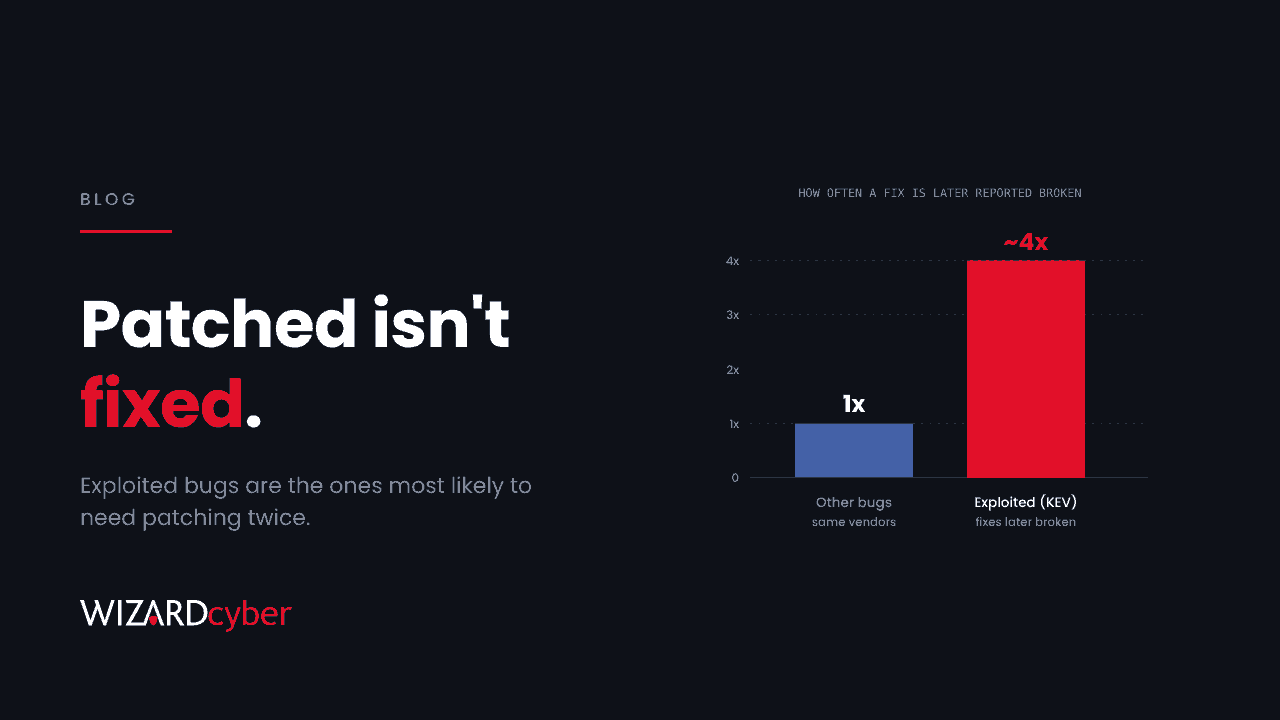
Patched Isn't Fixed: Why Exploited Bugs Keep Coming Back As New CVEs
Fixes for exploited bugs are reported broken four times as often as others. Why a patch should start a test, not close a ticket, and what to do instead.
 Threat Research
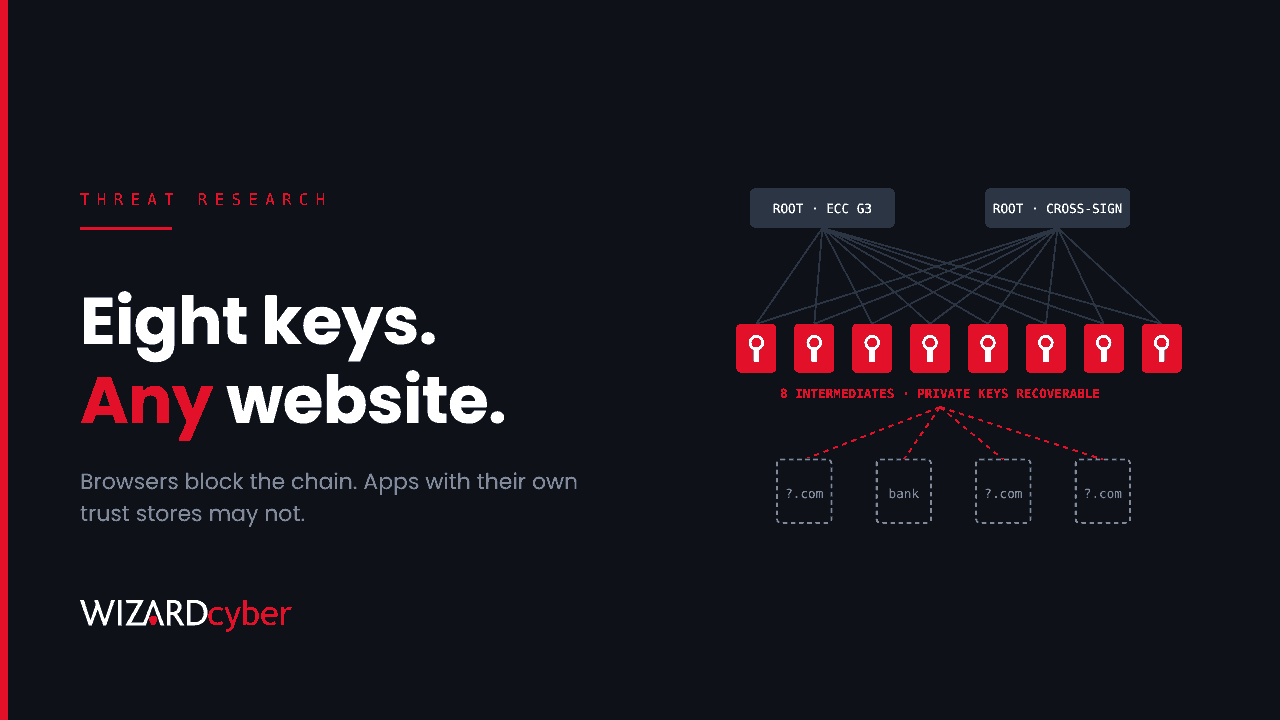
Eight Stolen CA Keys: Checking Your Estate After The Intermediate Certificate Compromise
Browsers and Windows now block eight compromised intermediate CAs. Apps with their own trust stores may not. How to find them with Defender KQL.
 Threat Research
Accept, Then Sign In: Hunting The Calendar-Invite Phishing Surge In Microsoft 365
Fake meeting invites hit 740,000+ in two weeks of October, aimed at Microsoft 365 logins. Why they get through, and how to hunt them in Defender.
 Threat Research
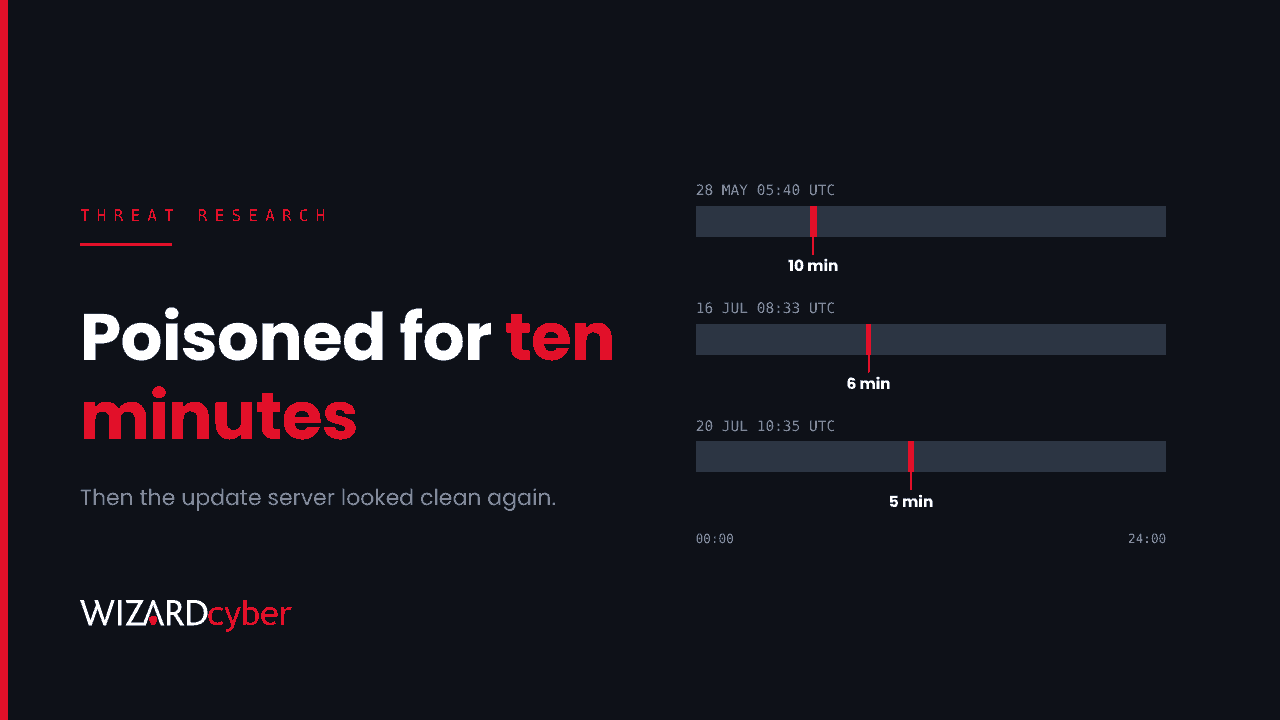
Ten Minutes On The Update Server: Hunting A Hijacked Software Updater On Windows Endpoints
An attacker hijacked a Windows tool's updates for minutes at a time, then cleaned up. How to hunt the backdoor it left on endpoints with Defender KQL.
 Governance
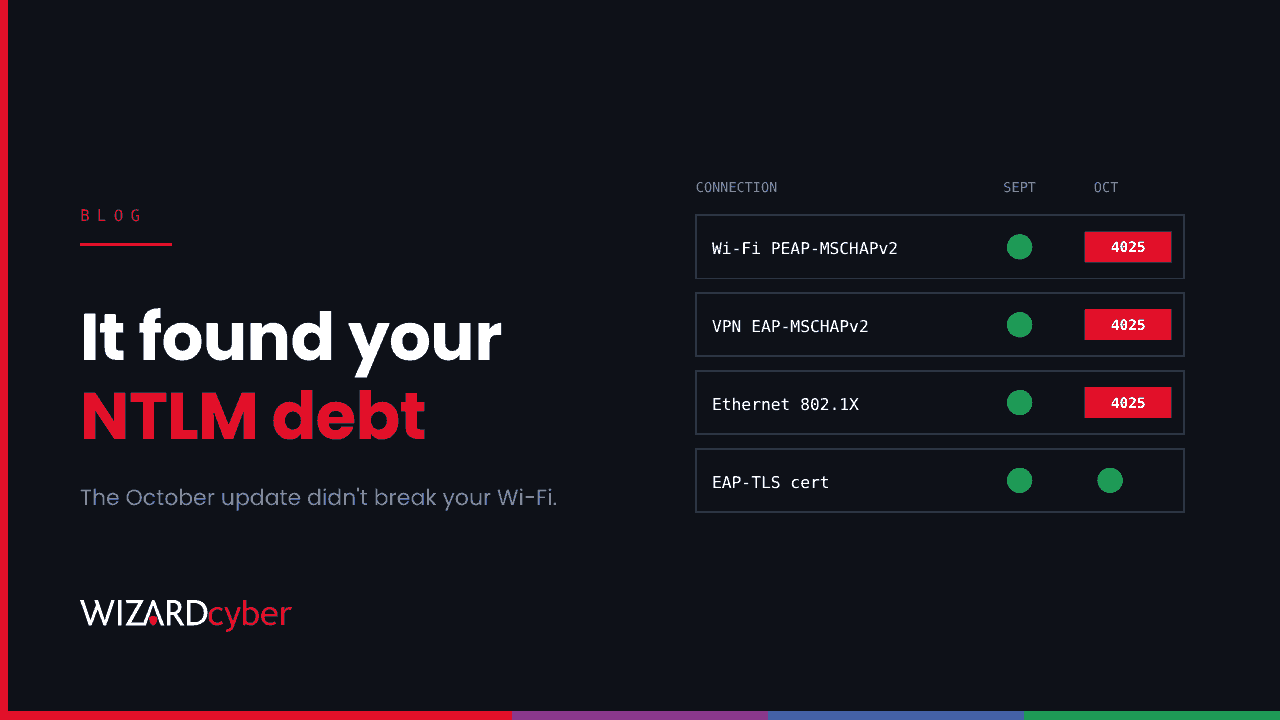
The October Update Didn't Break Your Wi-Fi. It Found Your NTLM Debt.
Since October, Windows blocks NTLMv1-derived single sign-on by default and some Wi-Fi and VPN logins broke. The quick fix, the real fix, and what's next.
 Governance
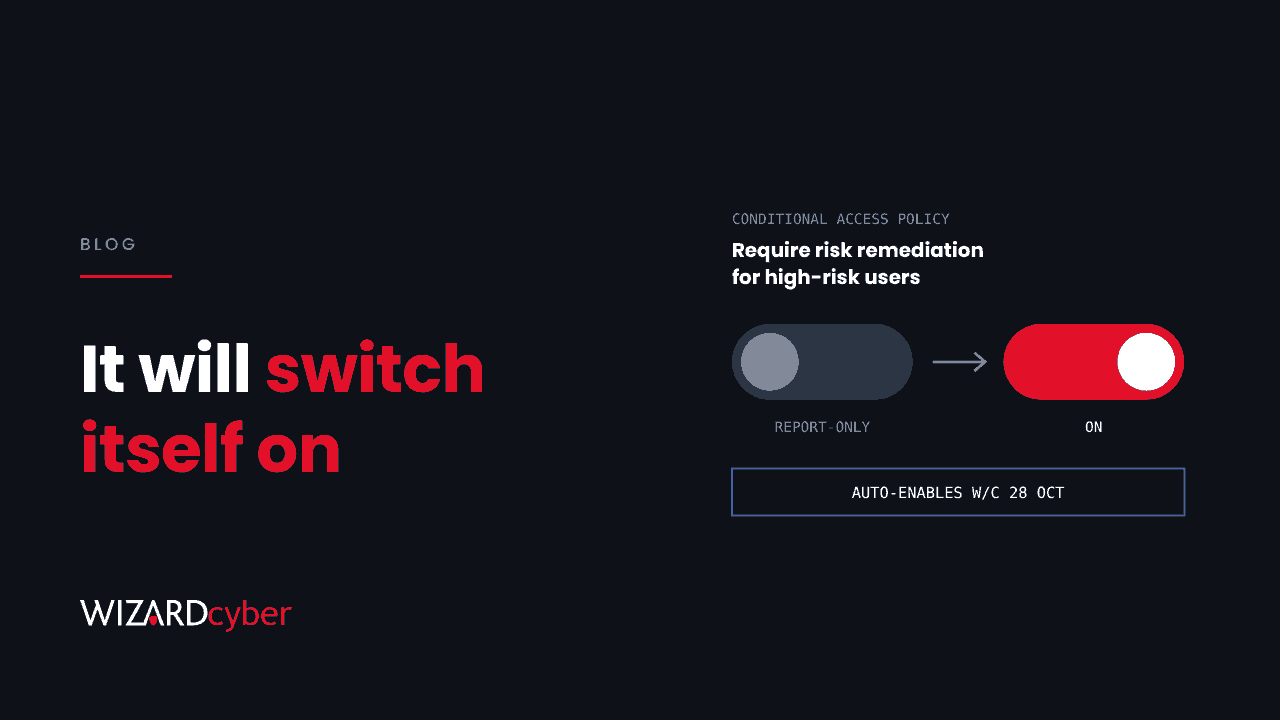
Microsoft Is About To Switch On A Policy In Your Tenant. Have You Read It?
A Microsoft-managed Conditional Access policy for high-risk users switches on in the week of 28 October. What it does, what to check, and who should decide.
 Threat Research
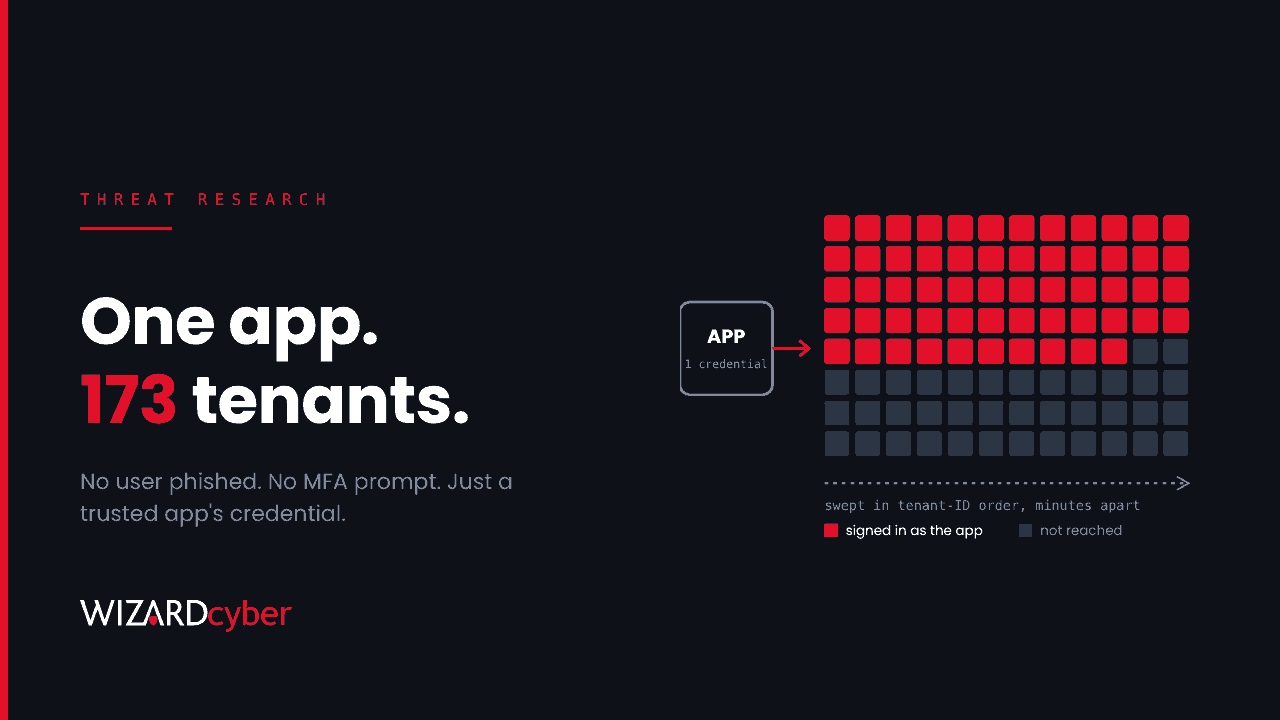
One Trusted App, 173 Tenants: Hunting A Compromised Third-Party App In Entra ID
A backup app's identity was used to sign in to 173 Microsoft 365 tenants. Why session revocation won't help, and how to hunt it in Entra and Sentinel.
 Threat Research
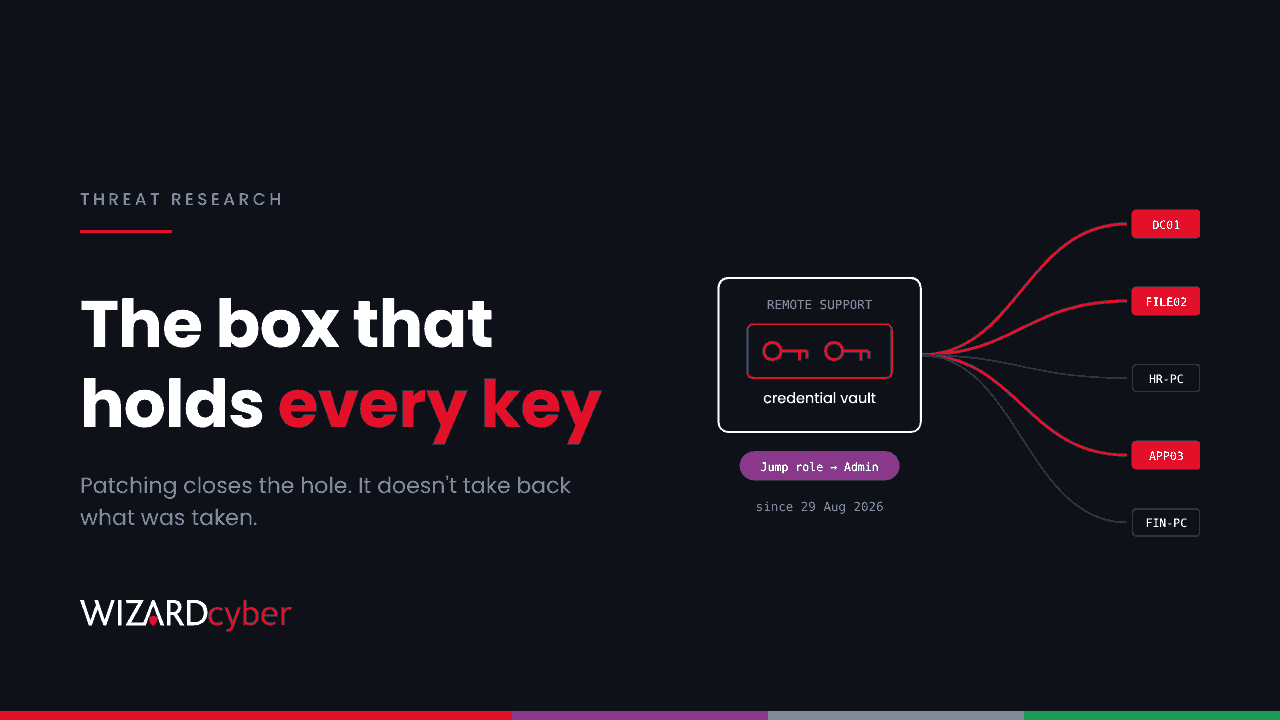
The Box That Holds Every Key: Hunting Downstream From A Compromised Remote Support Appliance
A remote support zero-day was exploited from August. Patching won't undo it. What to rotate, in what order, and how to hunt downstream in Defender.
 Threat Research
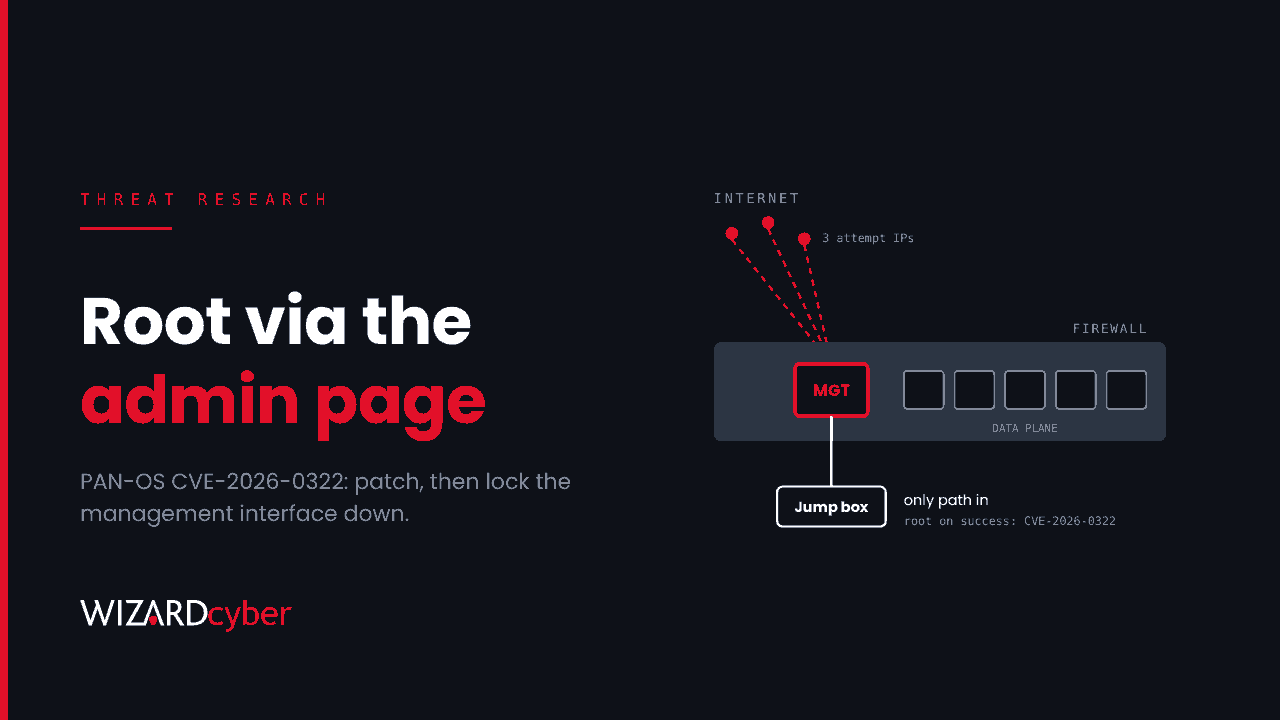
The Firewall's Admin Page Is The Target: Hunting PAN-OS CVE-2026-0322
A PAN-OS zero-day gives root via the management interface to anyone with an admin login. Fixed versions, what to rotate and KQL to hunt it.
 Threat Research
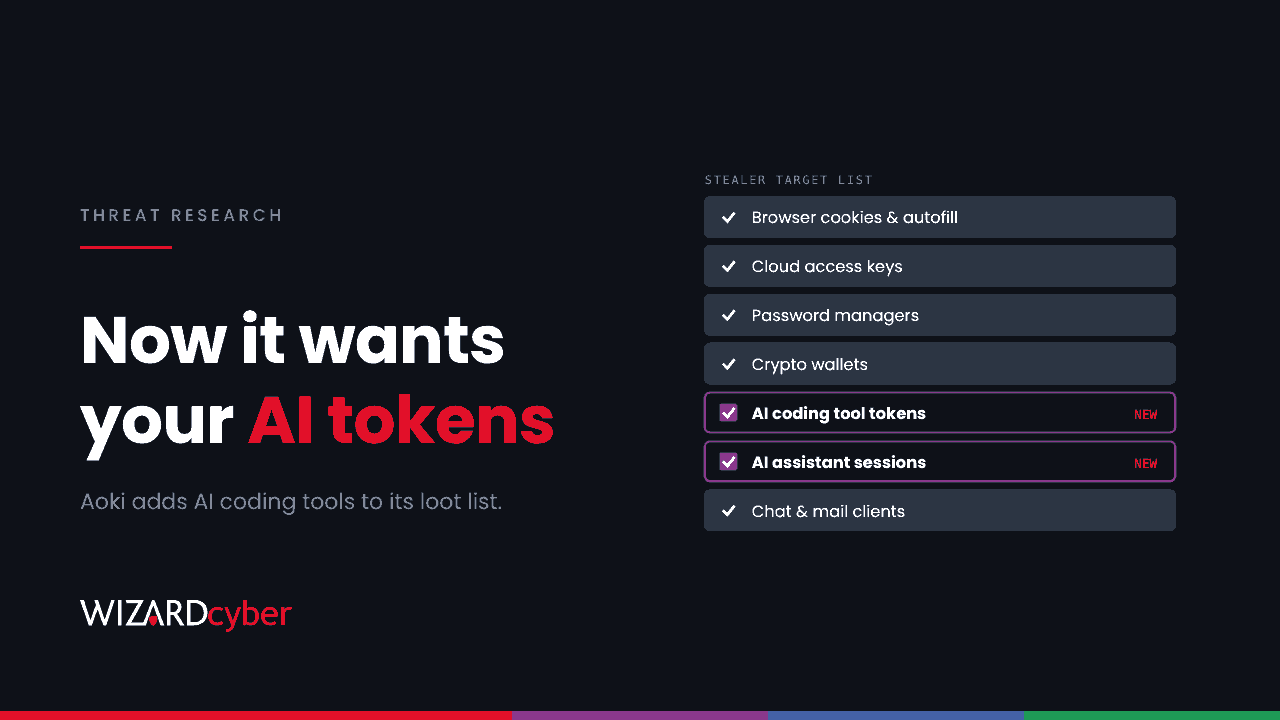
Infostealers Have Found Your Developers' AI Tools: Hunting Aoki On Windows Endpoints
A new Aoki build steals AI coding tool tokens alongside cookies and cloud keys. What it takes, how to hunt it in Defender and what to rotate.
 Incident Response
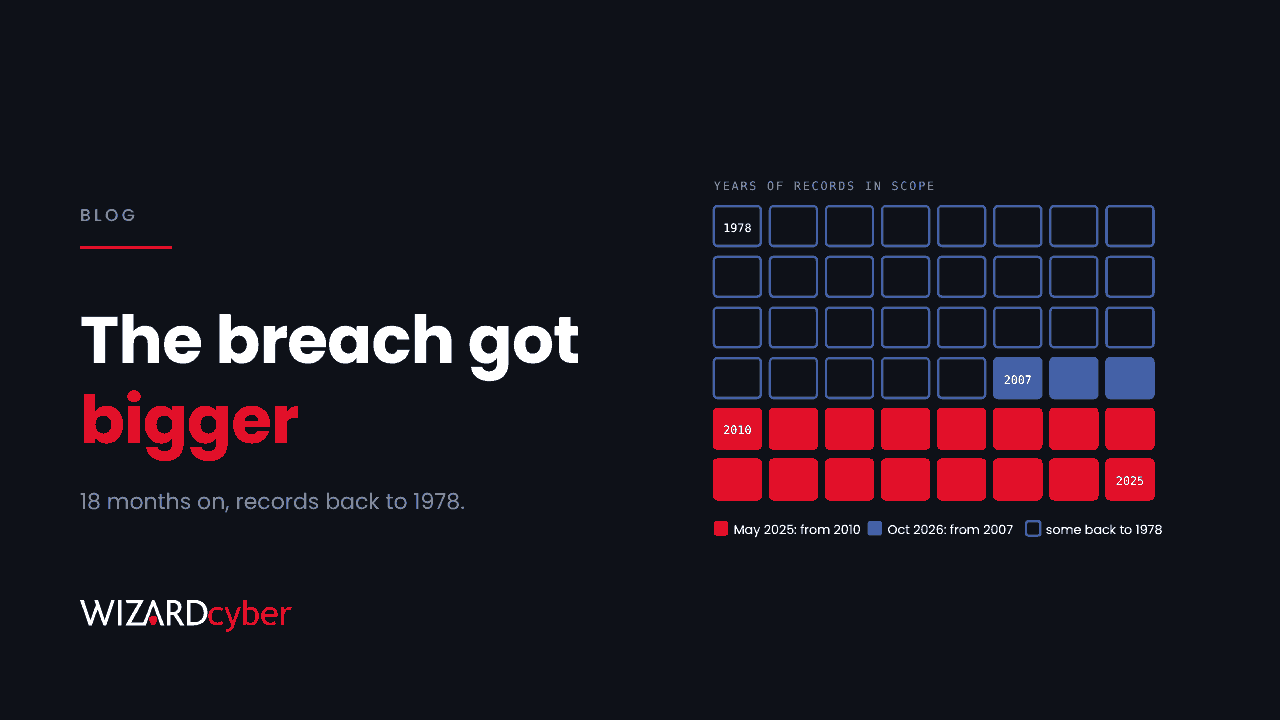
Eighteen Months Later, The Breach Got Bigger: Why Scoping Takes So Long, And How To Shorten It
The Legal Aid Agency breach now reaches records from 1978. Why scoping a breach takes months, and the five things that shorten it.
 Threat Research
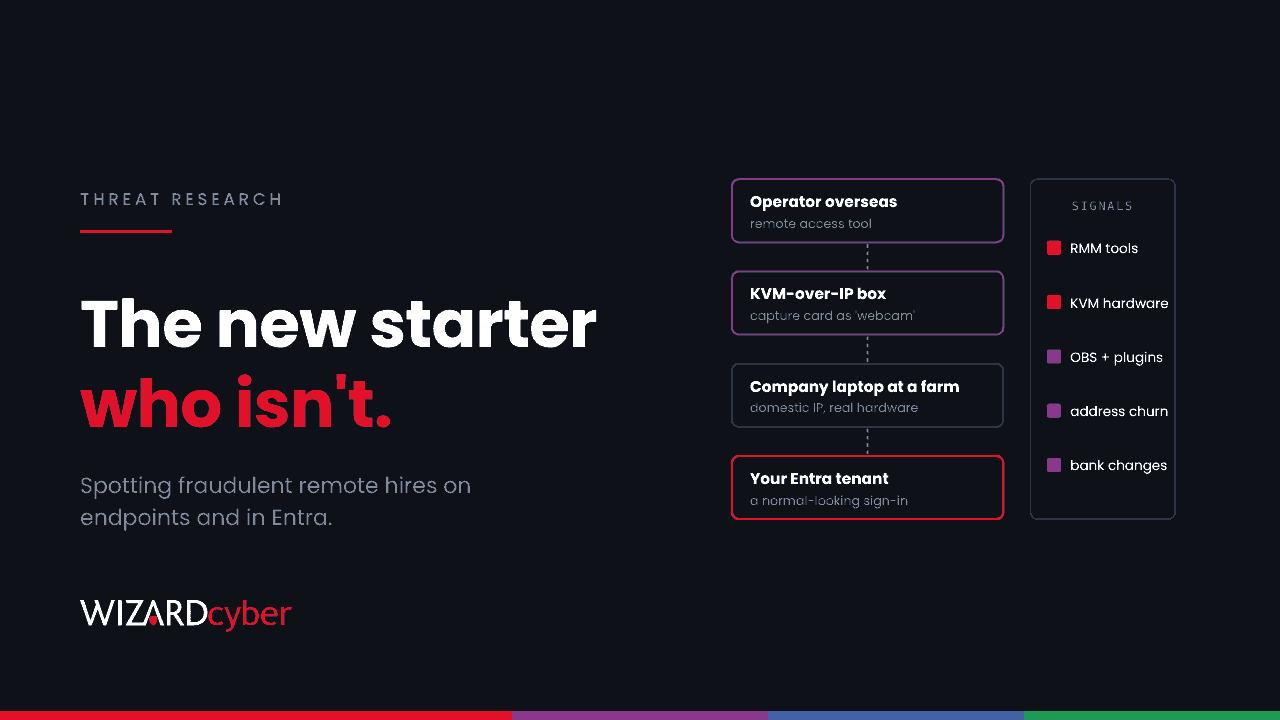
The New Starter Who Isn't: Spotting North Korean IT Workers On Your Endpoints And In Entra
The FBI says North Korean IT workers are widening their facilitator networks. The signals a SOC can see on endpoints and in Entra, with hunting queries.
 Managed SOC
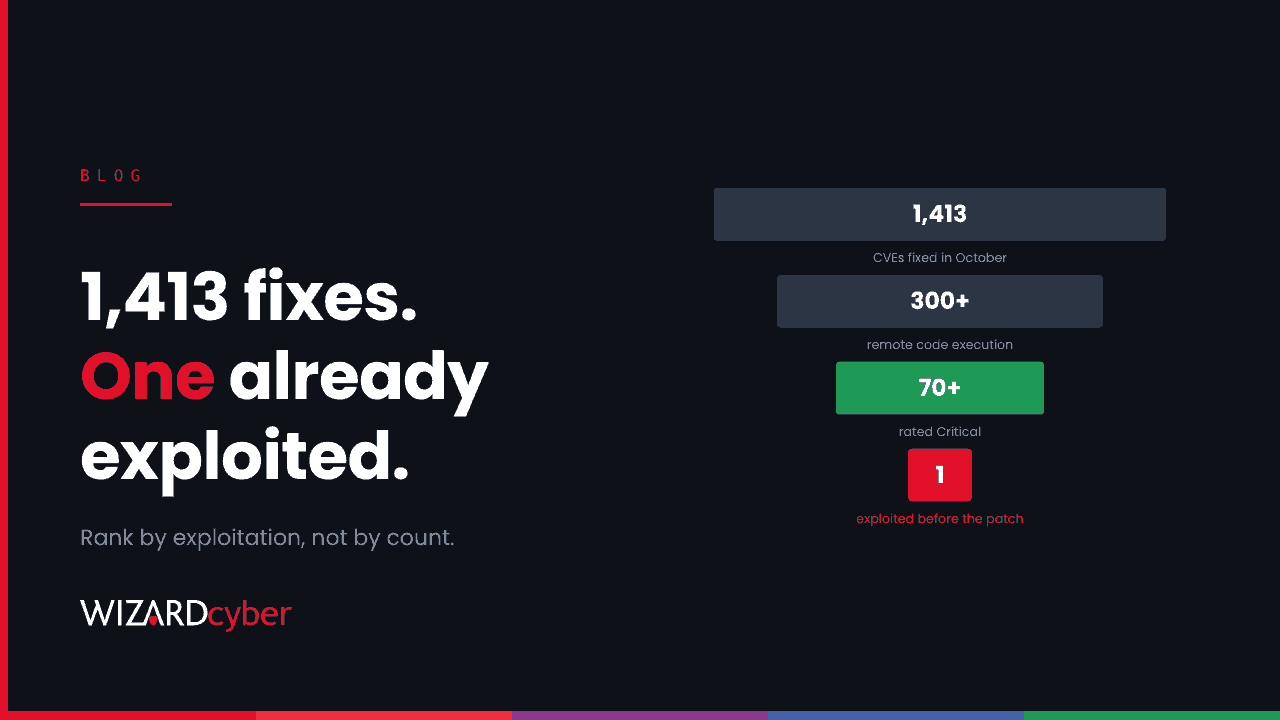
1,413 CVEs In One Month: Patch Lists Don't Scale, Exploitability Does
October's Patch Tuesday fixed a record 1,413 flaws, and one was already exploited. Severity scores can't rank that many. Exploitation and exposure can.
 Governance
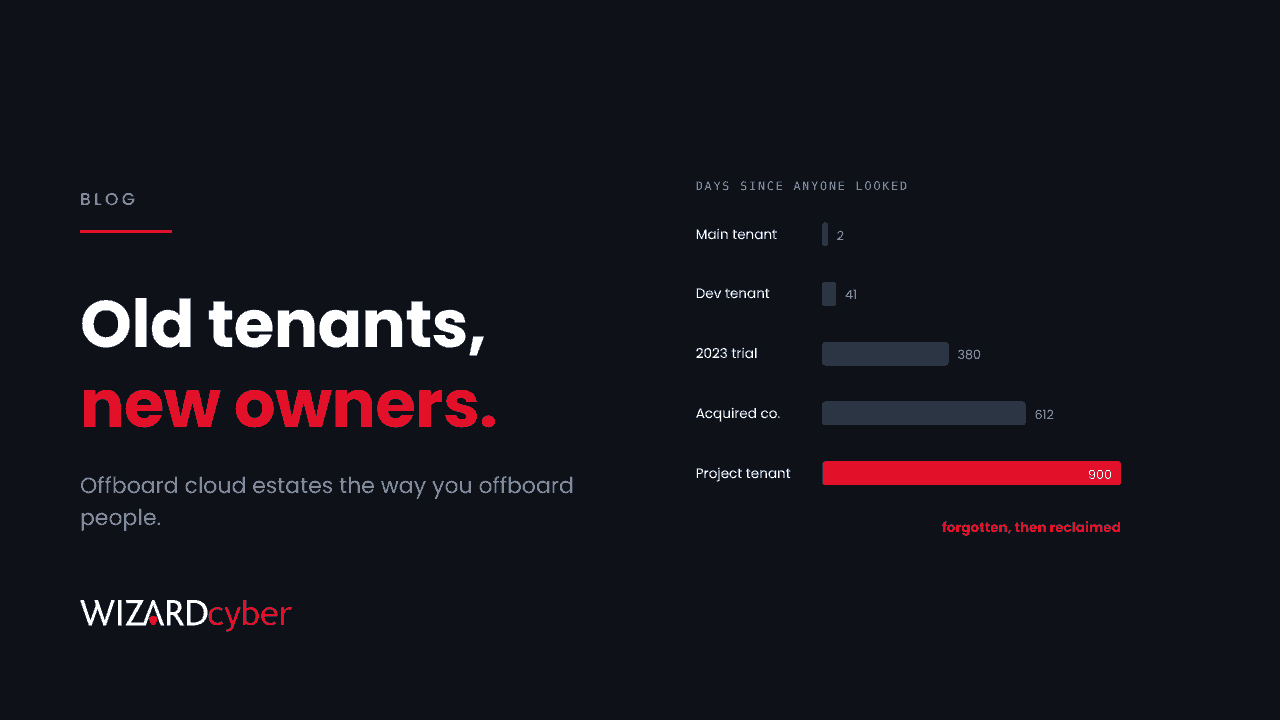
Abandoned Tenants Are The New Expired Domains
A phishing crew built a business on Microsoft 365 tenants their owners had stopped watching. Cloud estates need a leaver process, just like people do.
 Threat Research
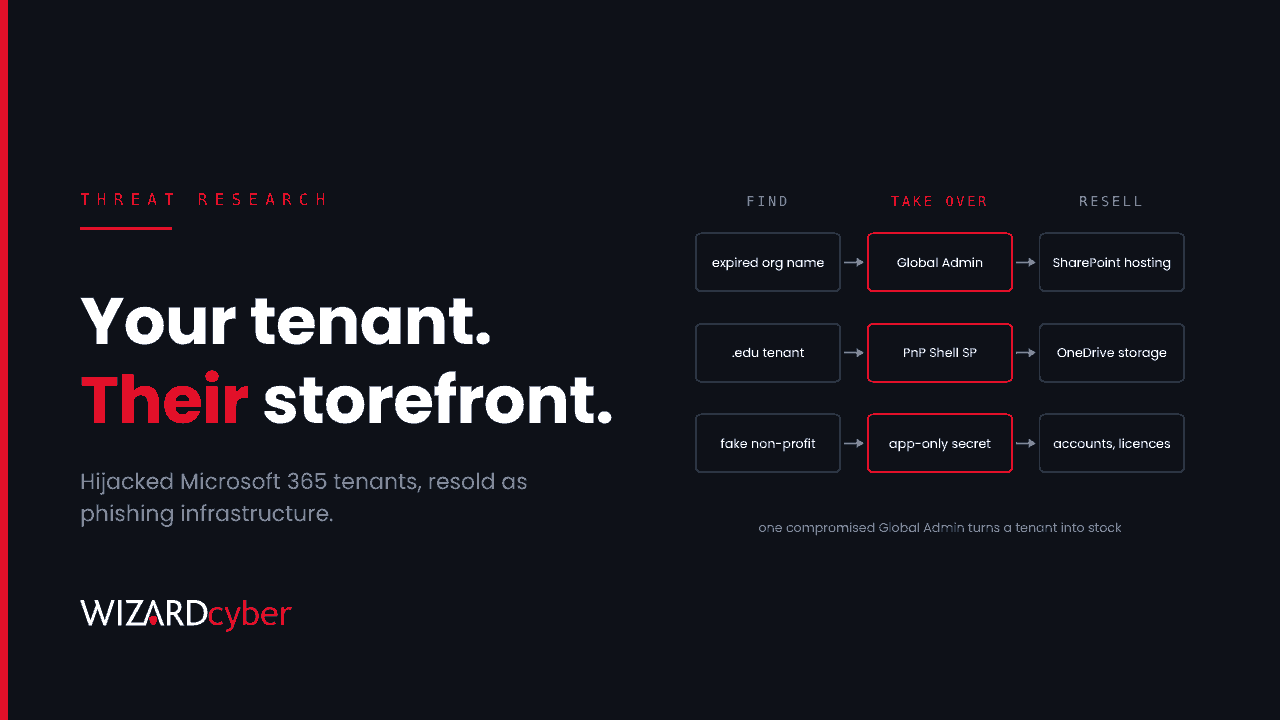
Your Tenant, Their Storefront: Hunting The Phishing Crew That Resells Microsoft 365 Tenants
Microsoft has disrupted a phishing operation that hijacked Microsoft 365 tenants and sold them as hosting. How the takeover works and how to hunt for it.
 AI Driven Security Operations
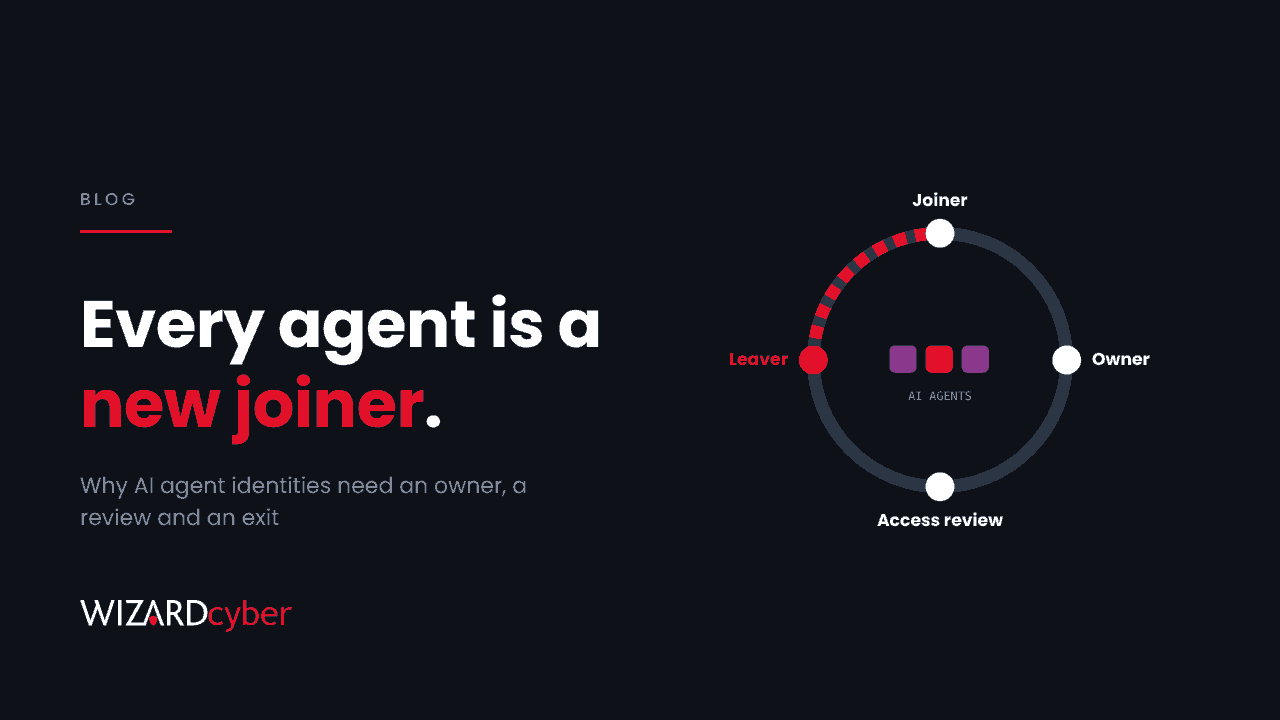
Every AI Agent Is A New Joiner: Why Agent Identities Need A Lifecycle
Staff are connecting AI agents to work email and files already. Treat each one like a new joiner: an owner, least privilege, a review and an exit.
 Threat Research
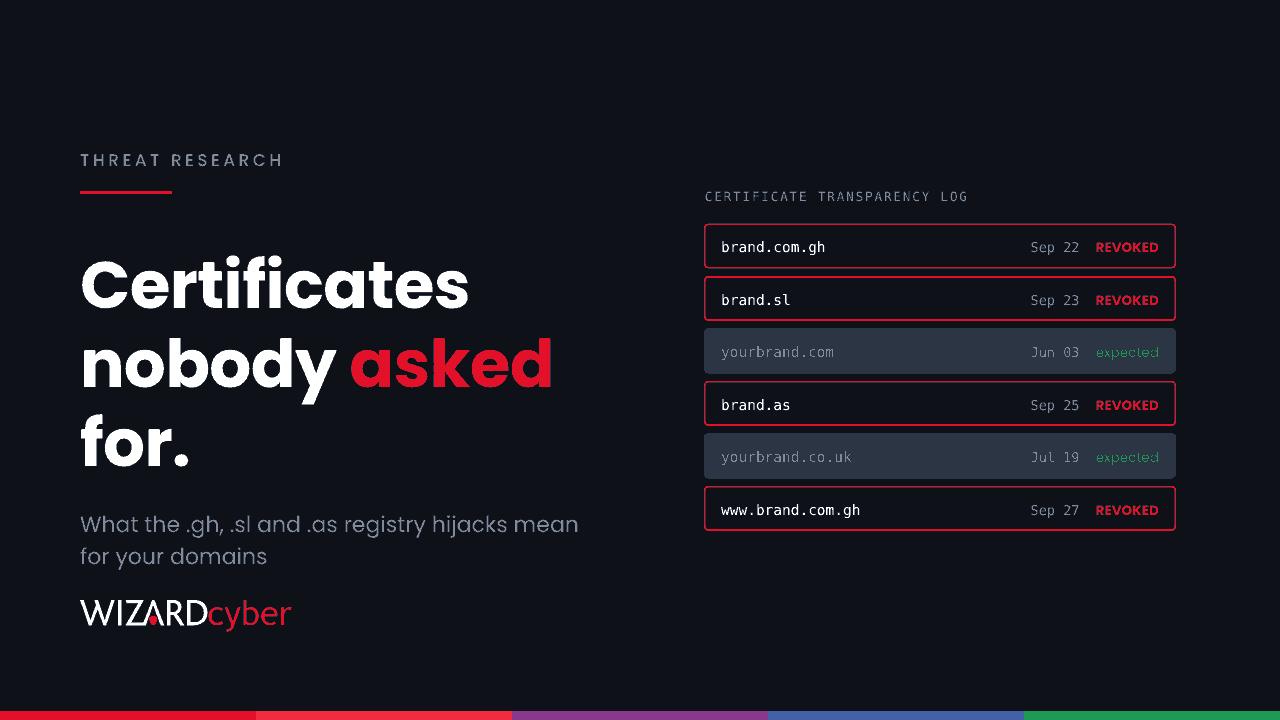
Rogue Certificates For Real Brands: What The ccTLD Registry Hijacks Mean For Your Domains
Attackers hijacked the .gh, .sl and .as registries and got trusted certificates for big brands. CAA, CT monitoring and the DNS risk behind it.
 Threat Research
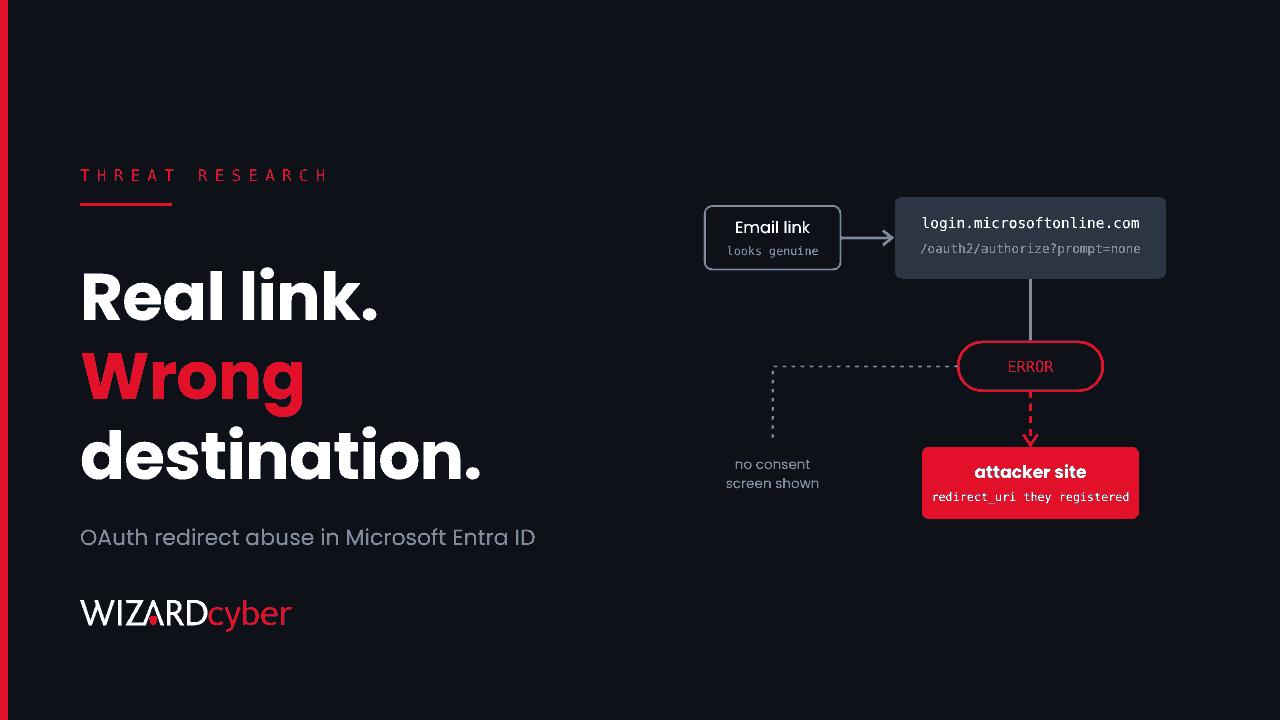
Real Microsoft Links, Hostile Destinations: Hunting OAuth Redirect Abuse In Entra ID
Phishing that starts on a genuine login.microsoftonline.com link and ends on an attacker's site. How the redirect trick works and how to hunt it.
 Managed SOC
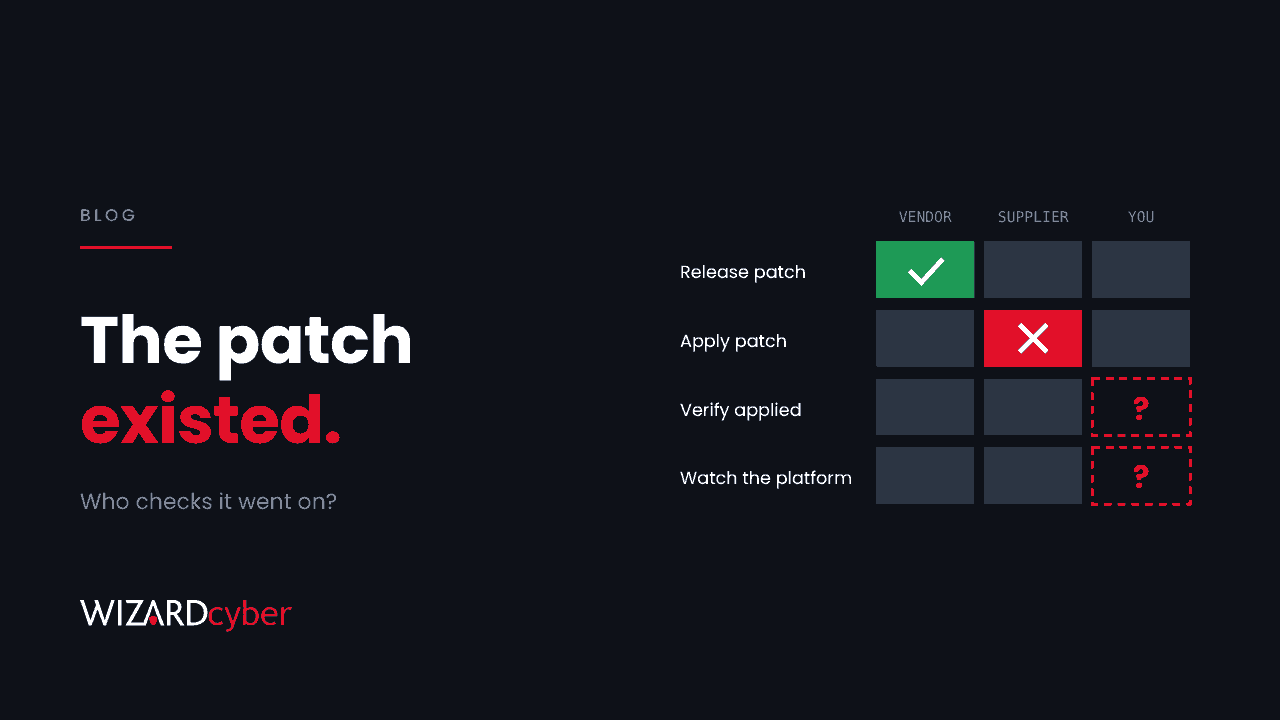
The Patch Existed. The Contractor Didn't Apply It. Who Owns Patching On Platforms You Don't Run?
The FBI says a contractor's missed patch let attackers in. Outsourcing a platform doesn't outsource the risk. What to ask suppliers, and what to watch.
 Threat Research
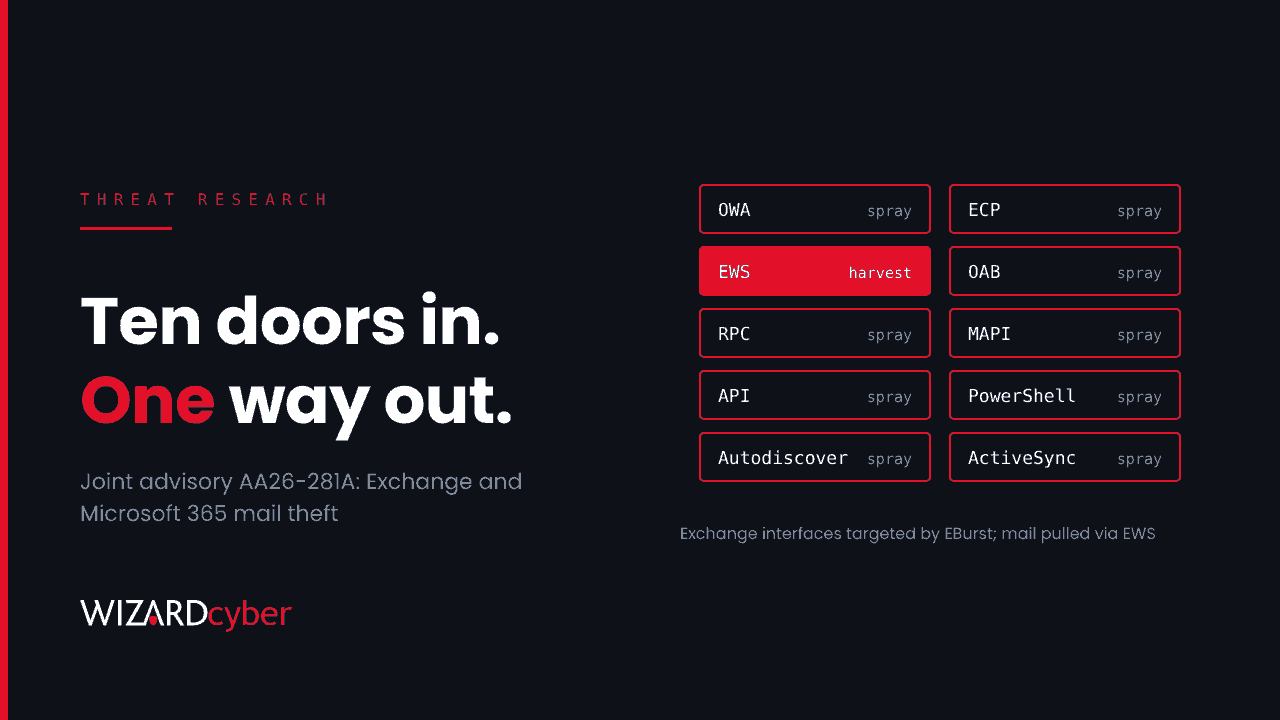
Seven Agencies, One Mailbox-Theft Playbook: Hunting AA26-281A In Microsoft 365
A joint advisory co-sealed by NCSC-UK shows password spraying across ten Exchange interfaces, then mail theft via EWS and app secrets. How to hunt it.
 AI Driven Security Operations
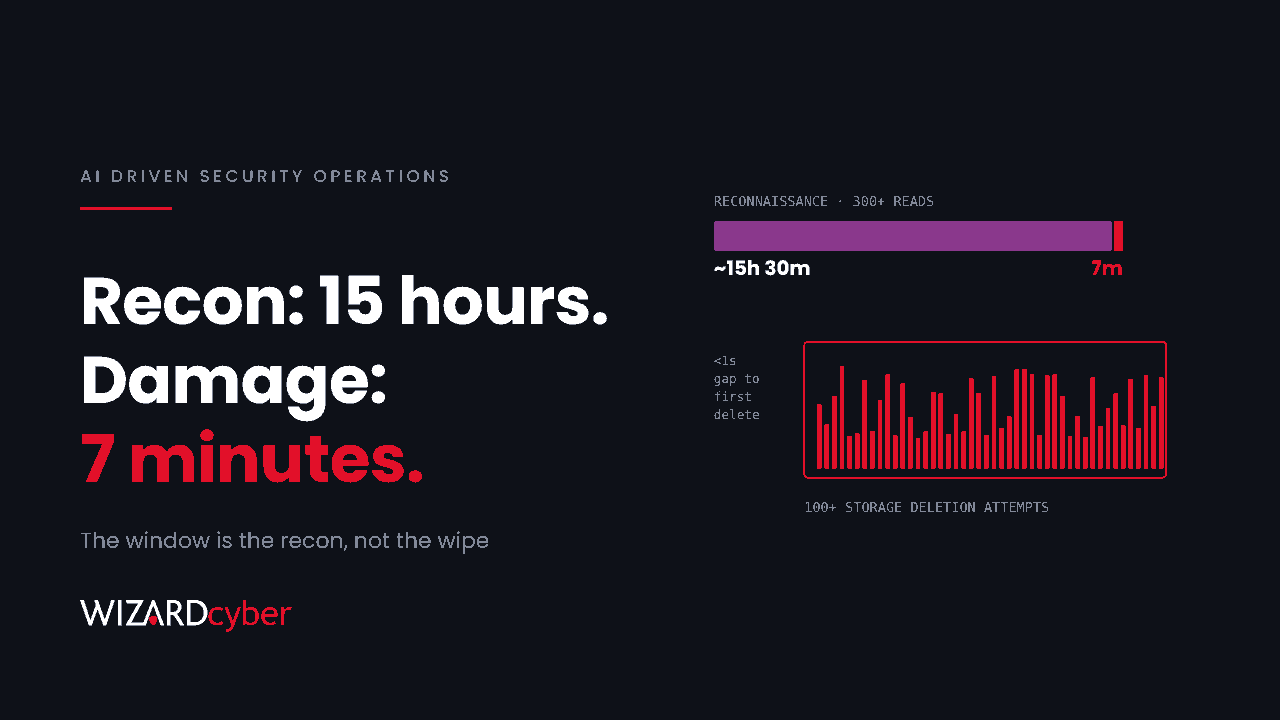
Seven Minutes, 100 Storage Accounts: What Agentic Attackers Mean For Your SOC
Storm-3168 deleted Azure storage in seven minutes after 15 hours of recon. The window that matters is the recon, and most SOCs aren't watching it.
 Threat Research
NetScaler Zero-Days: Why Patching Isn't Enough After Config Theft
Three NetScaler zero-days, exploited before disclosure. The upgrade closes the hole but rotates no secrets. What to rotate and how to hunt downstream.
 Threat Research
Exchange Server CVE-2026-96940: Patch The Mailbox-Read Flaw Before It's Weaponised
An out-of-band fix for on-prem Exchange closes a flaw that lets one compromised user read other mailboxes. Who must act, and how to hunt for it.
 Threat Research
Microsoft Digital Defense Report 2026: Reading It Against Your Own Detections
Microsoft's 2026 report names the techniques. The harder question is whether your own detections would see any of them. How to read it as a work list.
 SIEM
Best SIEM Tools in 2022 — And What Has Changed Since
Most of the 2022 SIEM shortlist has since been acquired, merged or absorbed. What actually changed, what did not, and how to choose one now.
Nothing matches that.