
Fully autonomous
Agents triage, investigate and act inside the limits you set, without waiting for anyone. Every action is still recorded and reviewable in the Control Centre.
CYBERSHIELD AI is our own agentic security platform — built and run in-house by our 24/7 SOC. Fourteen specialised agents triage, investigate, hunt and respond at machine speed, while senior analysts stay accountable for every decision.

We are a security company that automated itself, not an AI company that discovered security.
Our analysts have run Microsoft Sentinel since 2019. CYBERSHIELD AI executes the triage and escalation procedures they wrote, across 14 agent roles — with senior analysts still signing off every customer-facing decision.
“Barely two weeks into our onboarding, they detected and stopped an SQL injection attack against a development server that had a vulnerability in its code… probably the best shining example of why we’ll always be a Wizard Cyber customer.”
The same fourteen agents, delivered two different ways. Pick the one that matches where you are today.
The platform, in your own single-tenant instance. Your analysts stay on the work that needs judgement while the agents carry triage and investigation. You set the guardrails, per agent.
The service, run by us. Our 24/7 manned SOC and named senior analysts own the outcome, so you stop staffing a night shift and start getting verdicts instead of alerts.
Most Microsoft estates are running a fraction of what they are licensed for. We run a funded workshop that shows you exactly what you already own, what is switched off, and where the gaps are — paid for by Microsoft, not by you.
You don’t need an all-Microsoft estate — or to be a Microsoft security customer beyond Sentinel. CYBERSHIELD AI works across your identity, endpoint, email, cloud and network tools.
It gathers evidence, tests hypotheses and reasons to a conclusion — then hands your team a decision, not a longer alert.
A structured outcome on every incident — malicious or benign, scope, root cause, impact, confidence and a recommended action.
Investigations run against a Threat Attack Profile built for your sector, geography, stack and known adversaries — never a generic playbook.
A senior human analyst reviews and approves every customer-facing decision. Responsibility never sits with the model.
Autonomy is a dial, not a property. Set it per agent and per tenant, and move it as your confidence grows. Guardrails and confidence scoring sit under all three settings.
Agents triage, investigate and act inside the limits you set, without waiting for anyone. Every action is still recorded and reviewable in the Control Centre.
Nominate the points where a person must approve before anything proceeds. Set it per agent, so containment can wait for a human while enrichment does not.
You set the bar. Above it the agent proceeds; below it the work routes to an analyst. This is where most customers settle once they have watched it run.
On the managed service, senior analyst sign-off is the default — not a limitation.
This is a SOC org chart, not a feature list — each agent owns one function, colour-coded by squad, the way a real SOC is staffed.
The conductor. Tasks the right agent at the right moment, enforces the completeness gate, holds high-impact actions for human approval, and hands your SOC a case ready to close.
Everything from the queue to the verdict — triage, investigation, response, reporting and stakeholder comms.
Thinking like the attacker — global intelligence and proactive hunting for what never alerted.
Making the next incident easier to catch — detections, exposure across systems and people, and platform health.
Evidence, entity graph, timeline, triage plan and a signed-off report — the whole case, assembled for you and ready to review.
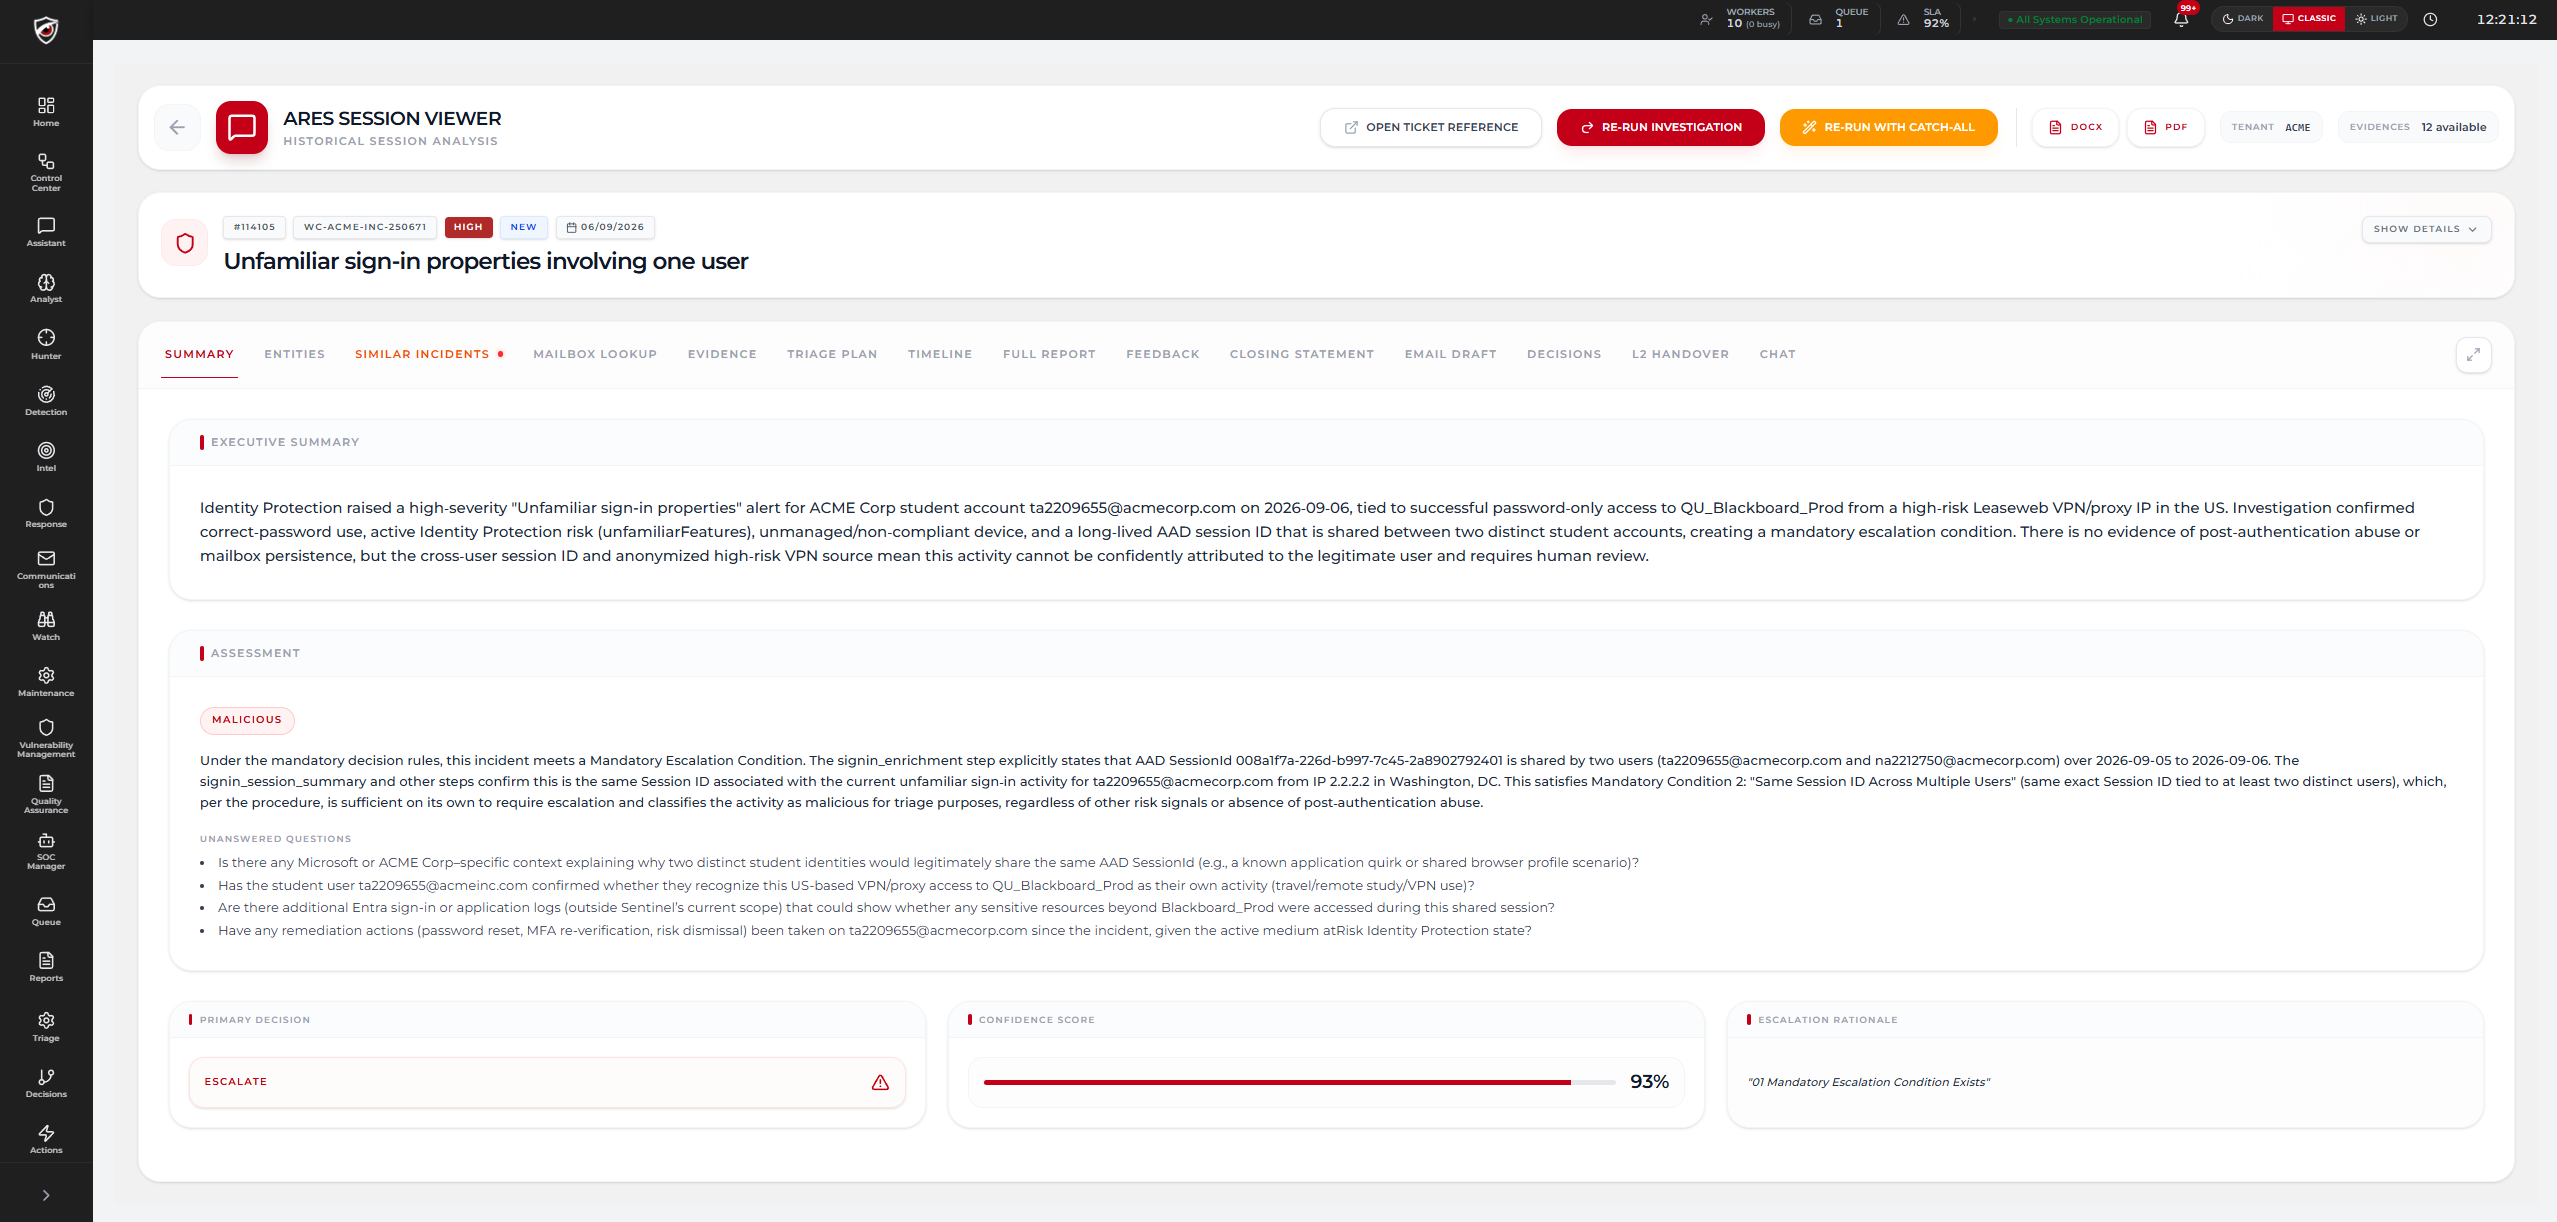
High-impact actions wait for a senior analyst to sign off.
Evidence, timeline, entity graph and report — compiled automatically.
A real AiTM (adversary-in-the-middle) case, replayed — investigated, scoped and contained end to end, holding for human approval before anything executes.
Two clocks we can defend, rather than one tidy round number. Every investigation ends in a verdict with the evidence attached.
Measured across our own SOC. Both clocks start at the same point: the moment a signal reaches CYBERSHIELD AI.
Boutique providers just bolt AI onto someone else’s tools. Global MSSPs treat you like a ticket number. We’re the rare middle: our own CYBERSHIELD AI platform, run by a SOC that actually knows your environment.
CYBERSHIELD AI runs day-to-day detection and response. Around it, our specialists cover the rest — from Microsoft consultancy to offensive testing, vulnerability management and risk.
Design, deploy and optimise Sentinel, Defender and the wider Microsoft security estate.
See what AI your people are actually using, stop sensitive data reaching it, and govern the agents acting on your behalf.
Web, mobile, network, cloud, wireless, IoT and OT — all tested in house.
Red and blue working together — adversary emulation that hardens your detections live.
Visibility and defence for industrial and operational technology environments.
Continuous scanning across everything you own, with the patching that closes the finding.
Senior security leadership on a retainer — strategy, board reporting and a roadmap that moves.
Continuous monitoring of your supply chain and vendor ecosystem.
Microsoft 365 E7 sits above E5 and bundles Copilot, Agent 365 and the Entra Suite. What the step up actually contains, who it is for, and the question to ask before buying it.
XDRWhat Microsoft XDR is, and how Defender and Sentinel work together to deliver unified detection and response across identities, endpoints, email and cloud.
AI Driven Security OperationsContext memory lets AI security tools retain knowledge across sessions and incidents. See why it matters and how Microsoft implements it.
Book a demo and watch the platform work a real scenario — with our senior analysts walking you through every decision.