
Incident response, around the clock
How Wizard Cyber handles a live cyber incident: picked up by analysts already on shift, worked through the NIST SP 800-61 phases, and closed with a written report and remediation advice.
Transcript
0:00Already underway
Incident response starts once an attack is already underway. What happens next decides how much it costs you.
0:08Already on shift
Our SOCs are staffed around the clock, so an incident raised at three in the morning is picked up by people already on shift, not an on-call rota being woken.
0:18A known model
We work to NIST SP 800-61, the model most response teams and regulators use: preparation, detection and analysis, containment and recovery, then the review.
0:32Understood first
Investigation establishes the cause, not just the symptom, because an incident nobody understands cannot be contained safely.
0:41Attacker out first
Whether the attack came from outside or inside, the attacker is out before anything is restored. Recovering a system they can still reach just restarts the incident.
0:52The route closed
Every incident ends with a written report and remediation advice, so the route the attacker used is not open twice.
1:01Your estate
You do not need a particular platform, or to be a customer already. The service is shaped around the security you already run.
1:10Book a Demo
If an incident is underway, report it now. Otherwise, plan the response before you need it. Book a demo.
Consultancy
 1:09
Consultancy
vCISO
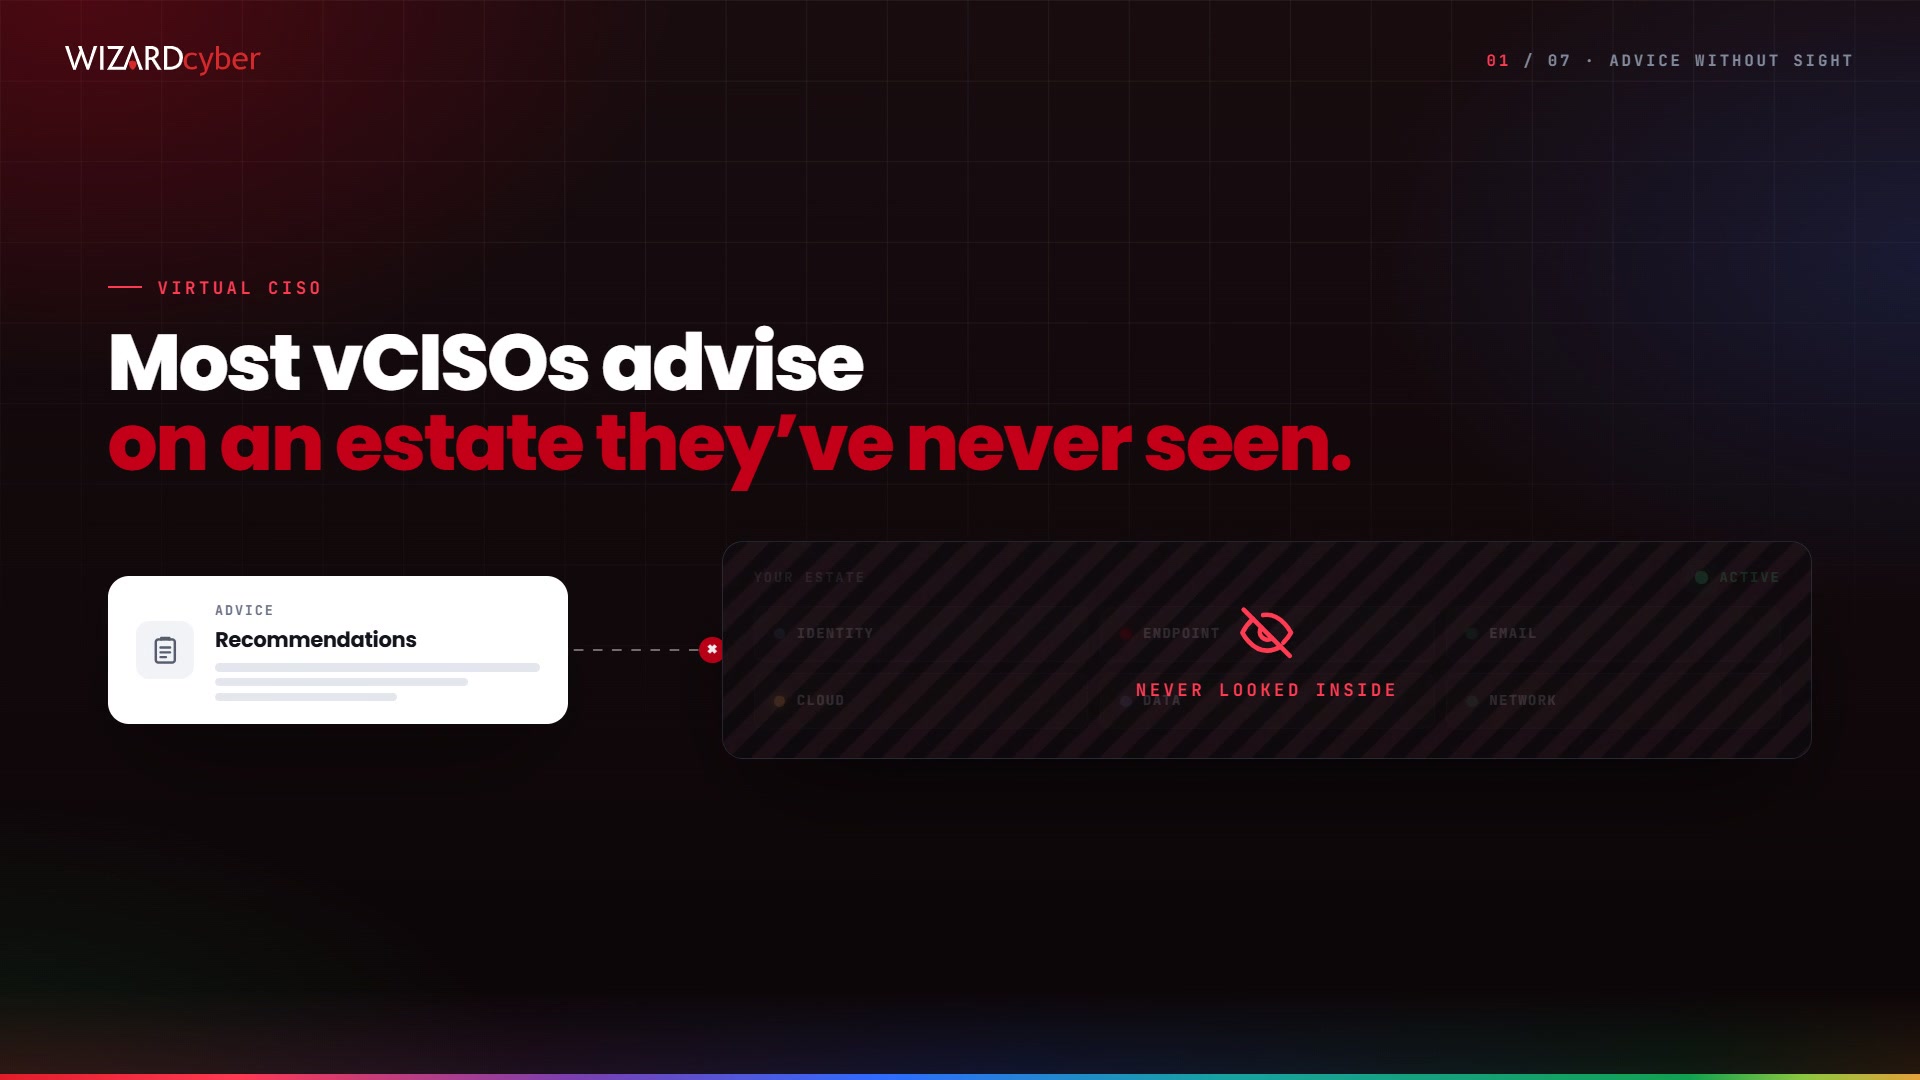
How Wizard Cyber’s virtual CISO builds your risk register from what a 24/7 SOC sees in your estate, not from a questionnaire, with three ways in: Baseline, vCISO and Assurance.
 1:28
Consultancy
AI Governance
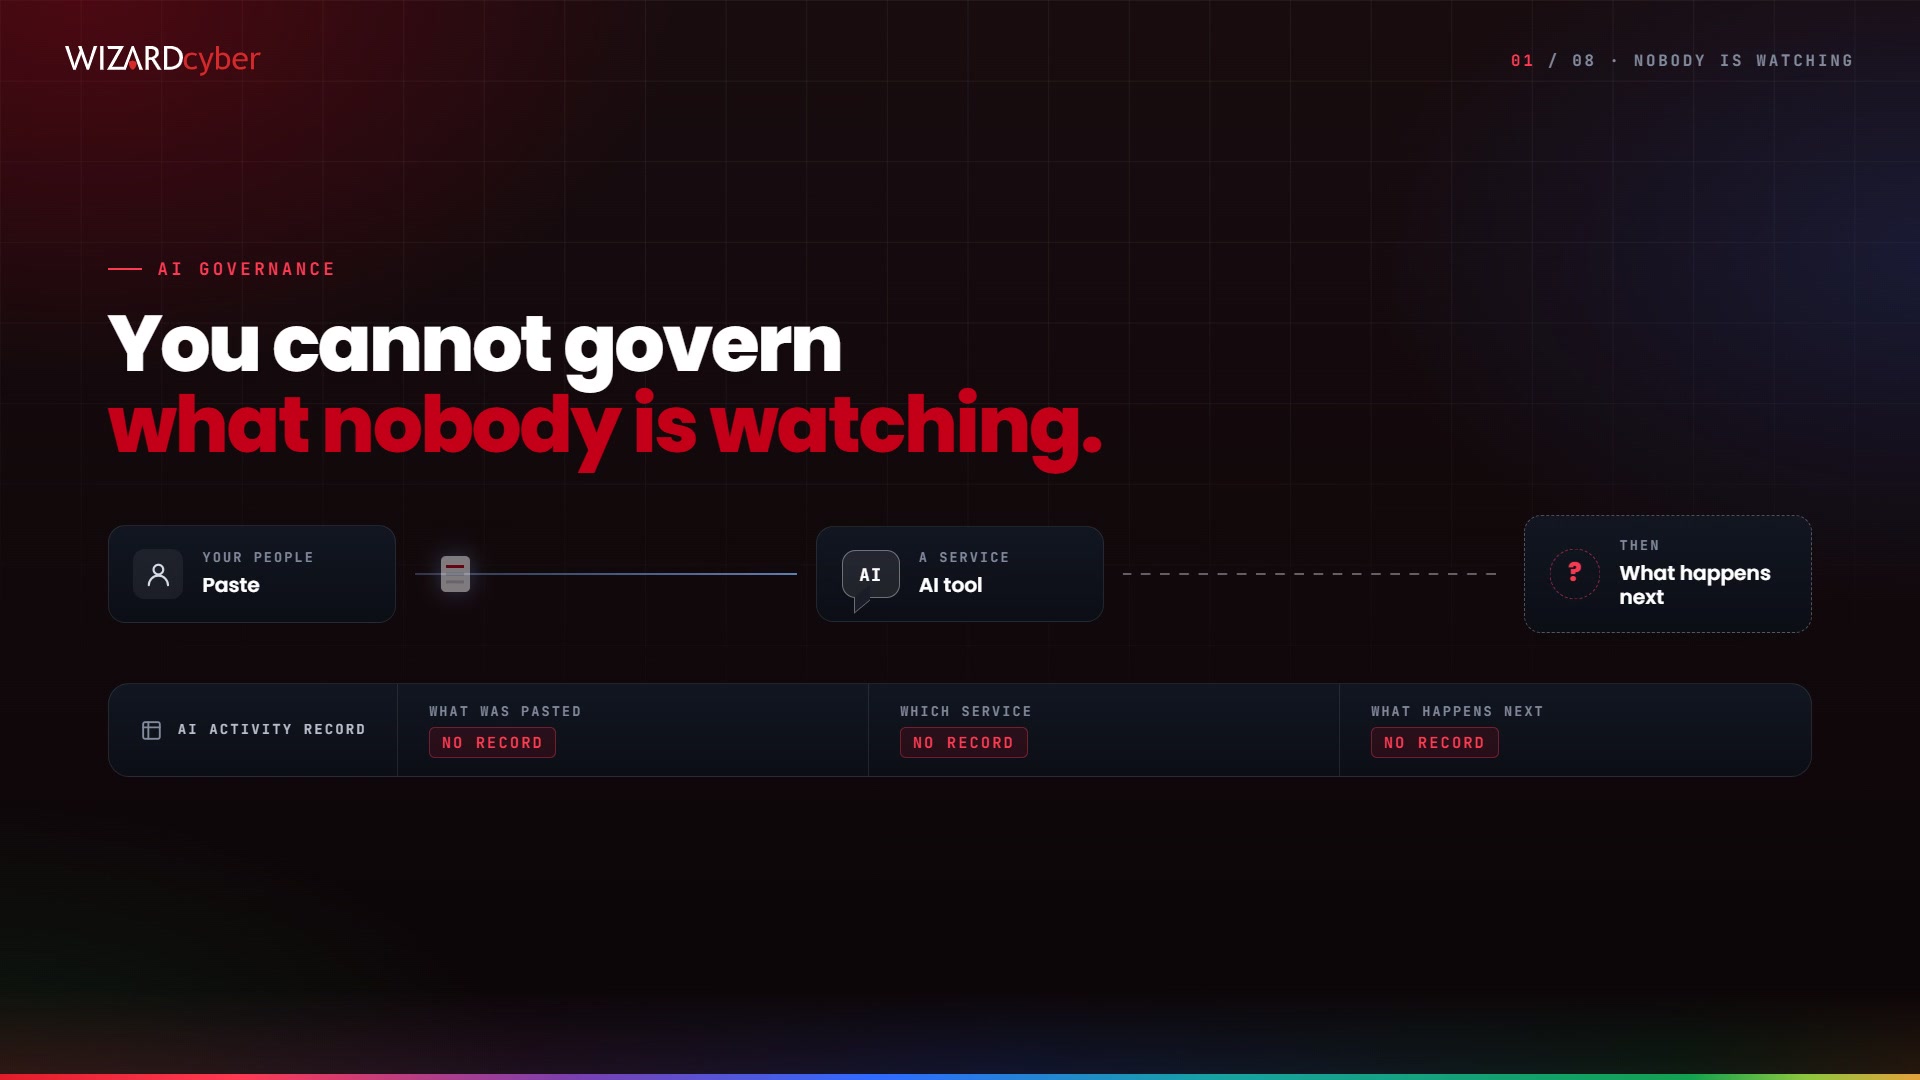
How Wizard Cyber governs how your people use AI: controls on the Microsoft security you already own that notice sensitive data leaving, keep approved AI usable, and put AI activity in front of the SOC.
Watch it run
on your own alert types.
An hour with a SOC analyst: a live investigation from signal to signed verdict, and the autonomy dial set where you would set it. Your scenarios, not a canned demo.