
ISO 27001, kept alive after the certificate
How Wizard Cyber gets you ready for ISO 27001, from gap analysis to both audit stages, and keeps the management system running and evidenced after an accredited body issues the certificate.
Transcript
0:00The easy part
Getting to ISO 27001 is a project with a known shape. Keeping the management system alive afterwards is what catches organisations out.
0:11A management system
ISO 27001 certifies a management system: how you find risk, decide what to do about it, and prove that it works.
0:21Who certifies
We do not certify you. The certificate comes from an accredited certification body, and that separation is deliberate. We do the readiness, the build and the evidence.
0:33Gap to audit
We start with a gap analysis, then scope the risk, build the controls and the Statement of Applicability, and run the system so there is something to audit.
0:43Both audit stages
Then we sit with you through both audit stages. The first reviews the system on paper. The second tests whether it actually operates.
0:53Certified once
The common failure is not the first audit. It is a system that stops running once the consultant leaves, and a year with no evidence when the surveillance audit comes round.
1:04Evidence as you go
Where we run your SOC, much of that evidence builds up on its own: monitoring, incidents, response actions and supplier assessments, all with dates.
1:15Book a Demo
Start with a gap analysis, before anybody quotes you a programme. Book a demo.
Risk & Compliance
 1:06
Risk & Compliance
SOC 2 Compliance
How Wizard Cyber gets you ready for a SOC 2 Type I or Type II audit, holds the dated evidence through the observation window, and sits with you while a licensed CPA firm issues the report.
 1:28
Risk & Compliance
GRC
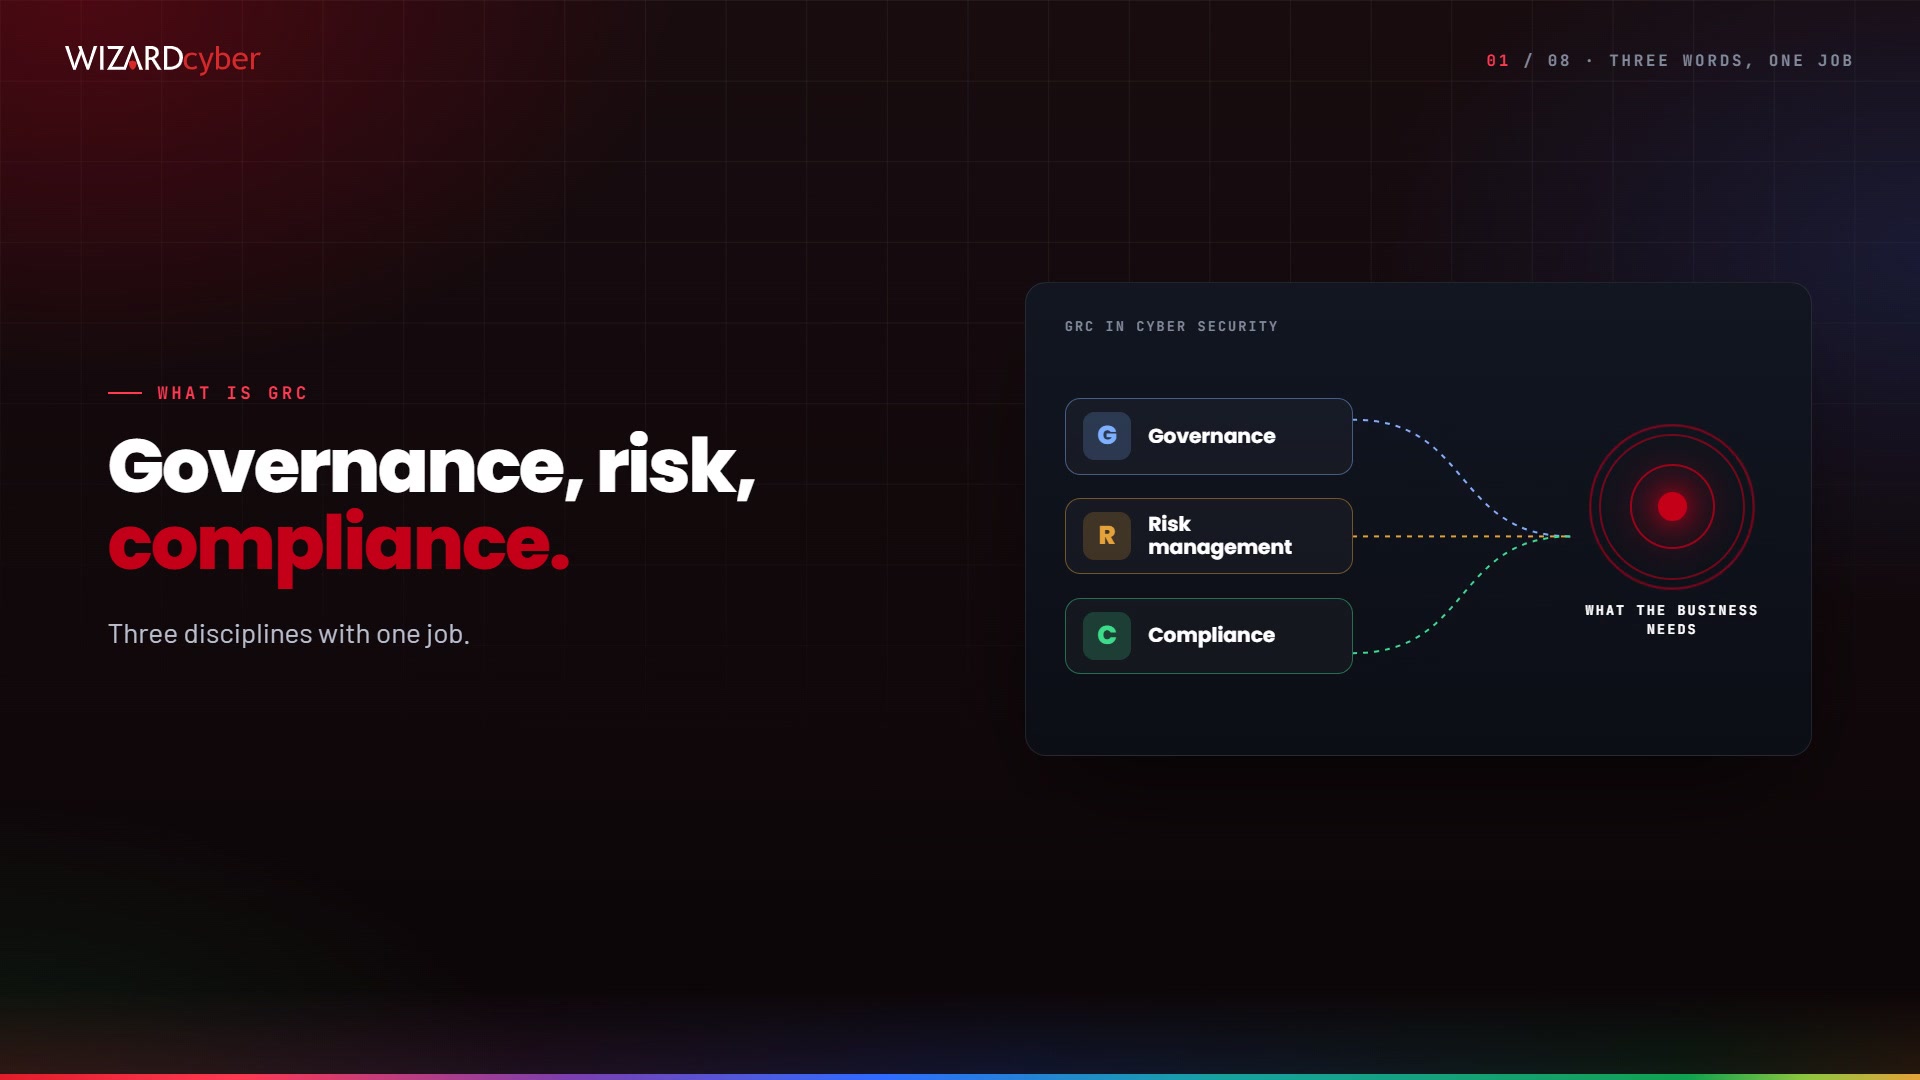
GRC in cyber security explained: governance, risk management and compliance, what each one does, why they work best as one programme, and how to put that programme in place.
Watch it run
on your own alert types.
An hour with a SOC analyst: a live investigation from signal to signed verdict, and the autonomy dial set where you would set it. Your scenarios, not a canned demo.