
What is GRC in cyber security?
GRC in cyber security explained: governance, risk management and compliance, what each one does, why they work best as one programme, and how to put that programme in place.
Transcript
0:00Three words, one job
GRC stands for governance, risk management and compliance. Three disciplines with one job: keeping security pointed at what the business actually needs.
0:11Governance
Governance is how security is directed and controlled: the policies, the procedures, and a clear owner for every decision about your information.
0:22Risk
Risk management finds, assesses and ranks the threats to your information, so effort goes to what could hurt the business most, not to whatever is loudest.
0:32Compliance
Compliance means meeting the laws, regulations and standards that apply to you, and keeping up as they change. It is also how you prove it.
0:42Better together
Run apart, the three drift: policies nobody tests, risks nobody owns, audits passed on paper. GRC joins them into one programme.
0:53A cycle, not a project
Set clear objectives, write the policies that serve them, assess risk regularly and monitor continuously, so the programme improves instead of going stale.
1:04Everyone’s job
It needs commitment from senior leadership, clear roles from the board down, and people across the organisation who see it as their job too. Start with a department or two, then roll it out.
1:17Book a Demo
Wizard Cyber helps you build GRC that actually runs, not a framework on a shelf. Book a demo.
Risk & Compliance
 1:06
Risk & Compliance
SOC 2 Compliance
How Wizard Cyber gets you ready for a SOC 2 Type I or Type II audit, holds the dated evidence through the observation window, and sits with you while a licensed CPA firm issues the report.
 1:26
Risk & Compliance
ISO 27001
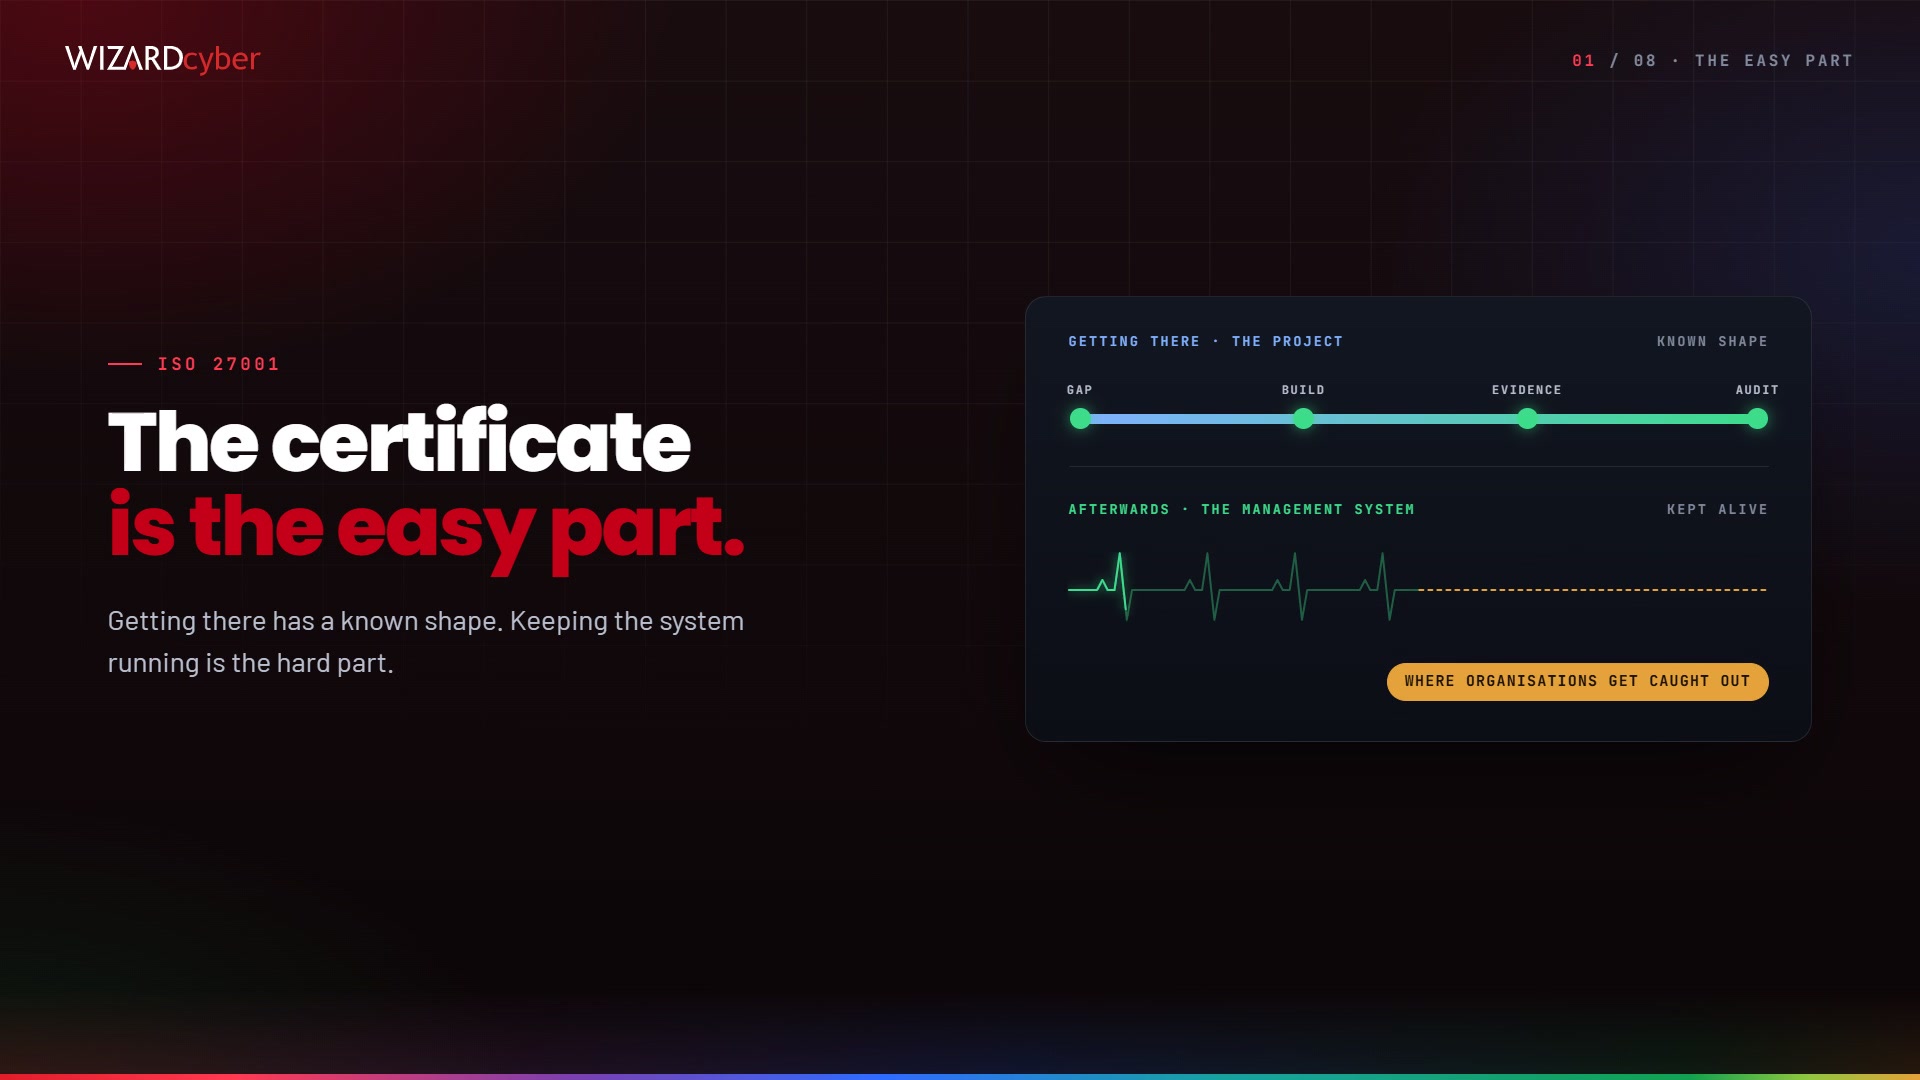
How Wizard Cyber gets you ready for ISO 27001, from gap analysis to both audit stages, and keeps the management system running and evidenced after an accredited body issues the certificate.
Watch it run
on your own alert types.
An hour with a SOC analyst: a live investigation from signal to signed verdict, and the autonomy dial set where you would set it. Your scenarios, not a canned demo.