
SOC 2 readiness, for the deal that needs it
How Wizard Cyber gets you ready for a SOC 2 Type I or Type II audit, holds the dated evidence through the observation window, and sits with you while a licensed CPA firm issues the report.
Transcript
0:00The deal waiting on it
Your customer will not sign without a SOC 2 report. There is usually a deadline attached, and a deal waiting on it.
0:08An attestation
SOC 2 is not a certification. It is an attestation report, issued by an independent licensed CPA firm.
0:17A period, not a snapshot
Type I looks at your controls at one point in time. Type II looks across an observation window, and you cannot retrofit a window.
0:28Ready for the audit
We get you ready for the audit. We scope it, find the gaps, and help you close them.
0:37Evidence as you go
Where we run your SOC, the dated evidence builds up while the window runs: incidents, monitoring and supplier oversight.
0:46Through the audit
Then we sit with you through the audit. The opinion is the auditor’s. The preparation is ours.
0:54Book a Demo
Tell us the deadline, and which customer set it. If the date is not achievable, we will say so. Book a demo.
Risk & Compliance
 1:26
Risk & Compliance
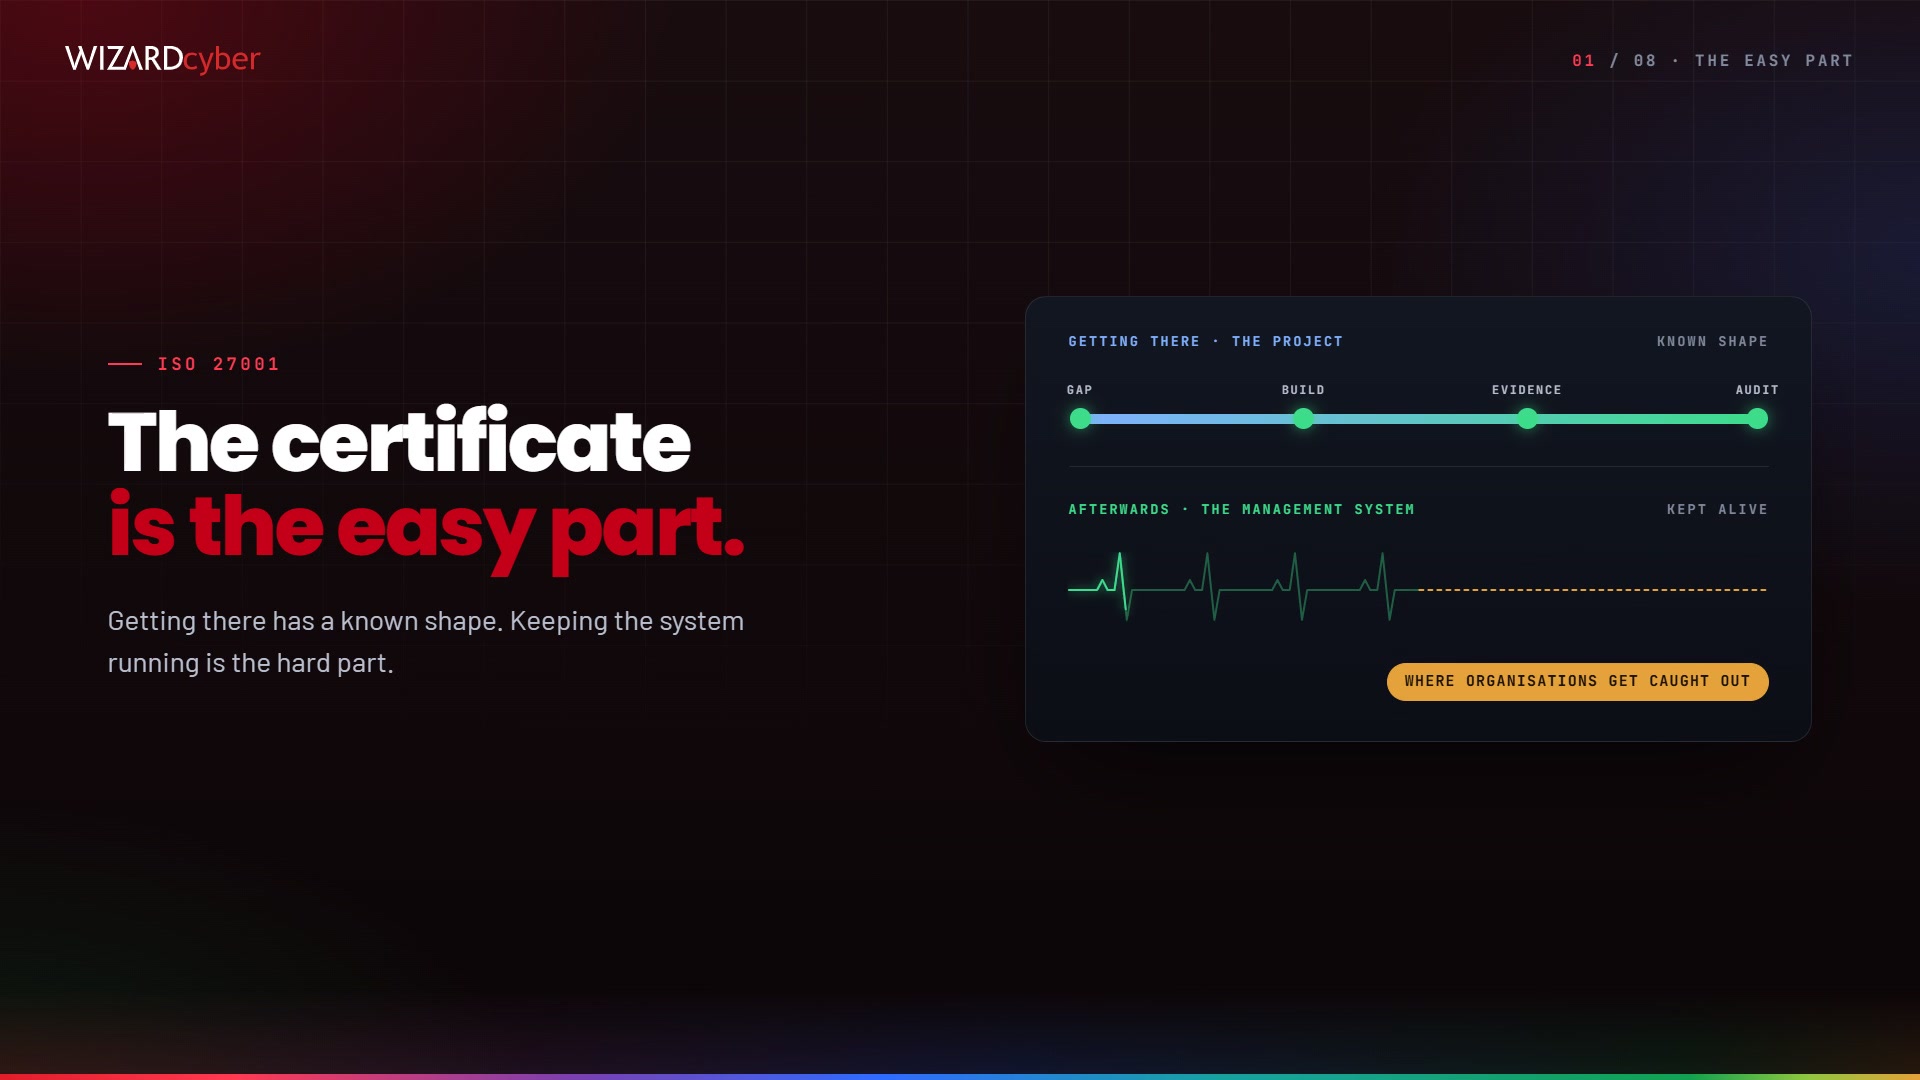
ISO 27001
How Wizard Cyber gets you ready for ISO 27001, from gap analysis to both audit stages, and keeps the management system running and evidenced after an accredited body issues the certificate.
 1:28
Risk & Compliance
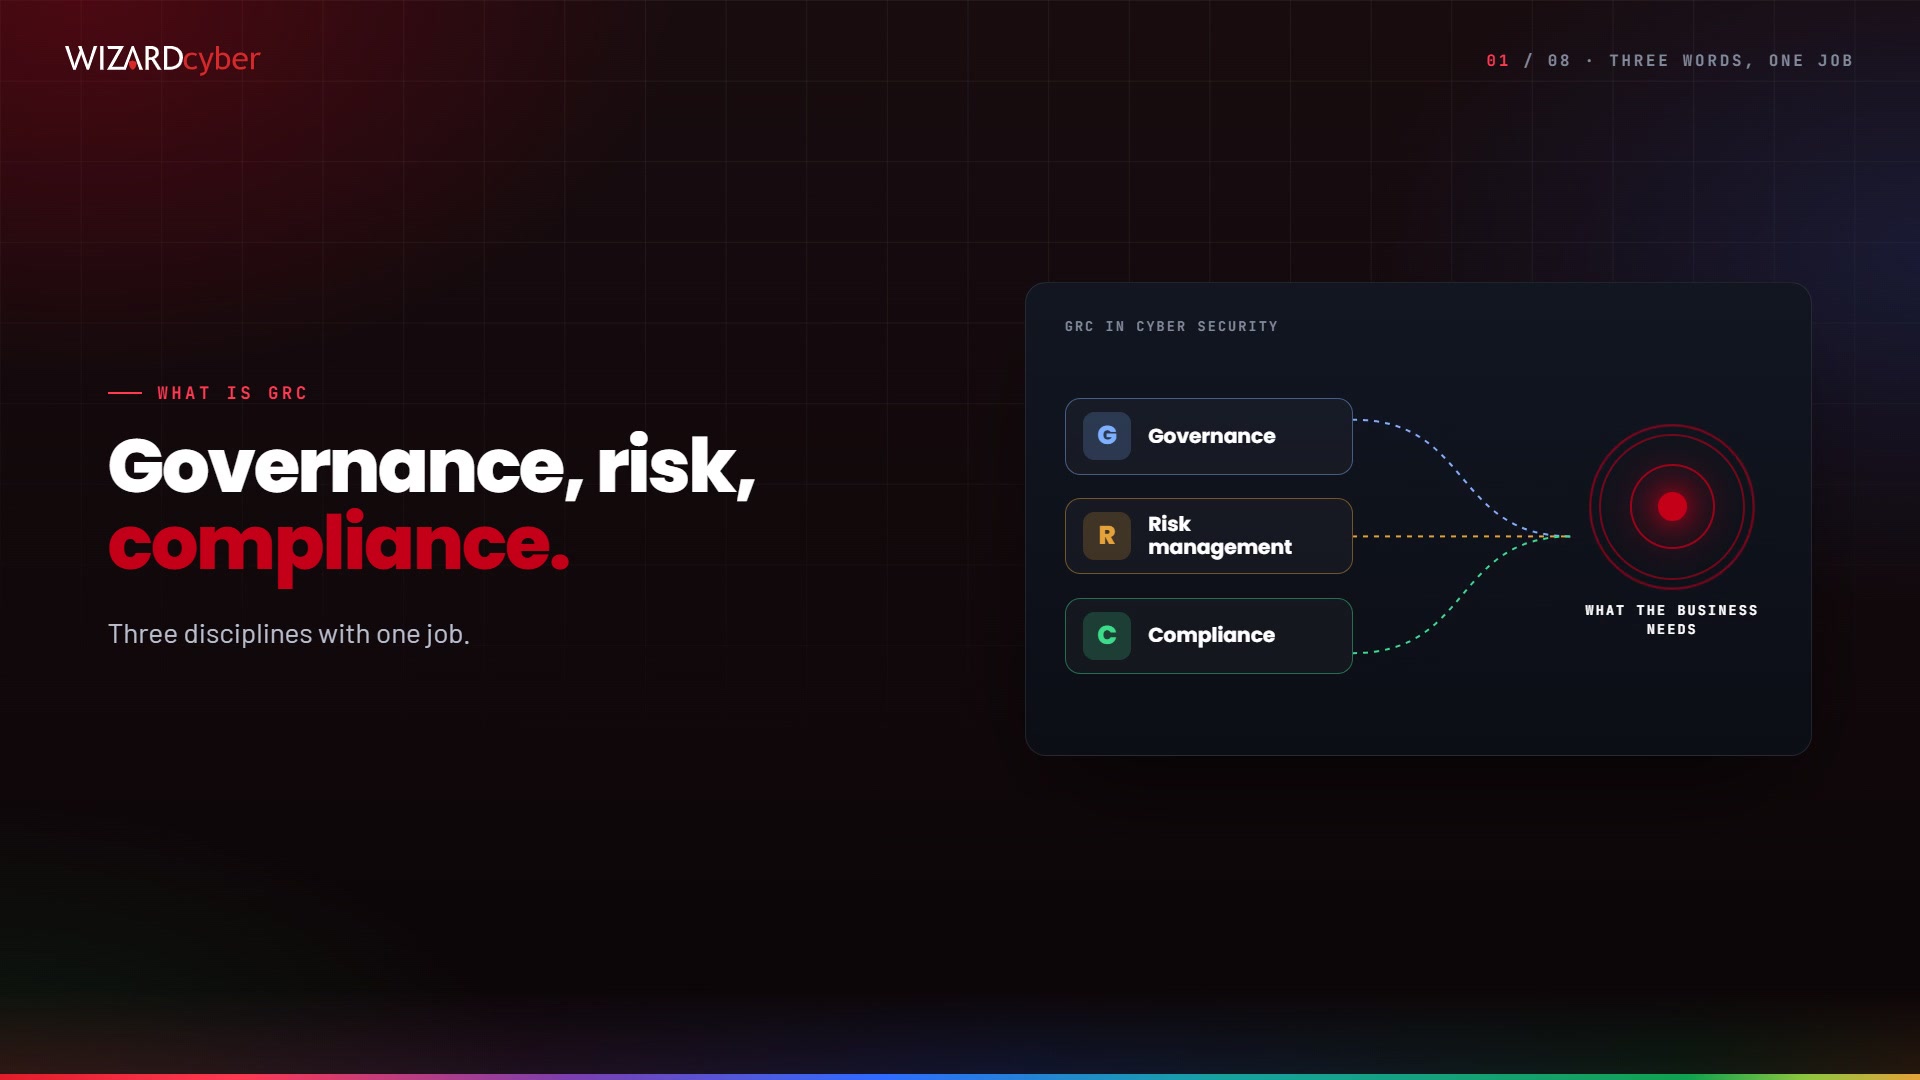
GRC
GRC in cyber security explained: governance, risk management and compliance, what each one does, why they work best as one programme, and how to put that programme in place.
Watch it run
on your own alert types.
An hour with a SOC analyst: a live investigation from signal to signed verdict, and the autonomy dial set where you would set it. Your scenarios, not a canned demo.