
Managed Microsoft Sentinel, run by an AI SOC
How Wizard Cyber runs Microsoft Sentinel as a service inside your own tenant: AI agents investigate every alert to a verdict, and a senior analyst signs it off.
Transcript
0:00Owned, not run
You already own Microsoft Sentinel. The hard part is running it: somebody has to look at every alert, at four in the morning as much as at noon.
0:09Your Sentinel
We run your Sentinel as a service, inside your own tenant. The workspace, the rules and the data stay yours, and you keep all of it if we ever part company.
0:20Run by an AI SOC
Sentinel is the platform. Our AI SOC is what runs it. Specialised AI agents triage every alert and investigate it to a verdict, drawing on 250+ named analyst skills.
0:35Time to verdict
The average time to a verdict is three minutes thirty, or seven minutes fifty where the Incident needs Advanced Investigation. And a senior analyst signs it off.
0:46Staffed around the clock
Behind the agents are multiple SOCs, each staffed 24/7. We build and tune your detections too, so the next incident is easier to catch.
0:57Two ways to run it
Run it fully managed, or co-managed alongside your own team, with the boundary agreed in writing.
1:04Sentinel first
Sentinel is the only requirement. Connectors for the rest of your estate are built during onboarding, and included in the service.
1:13Since 2019
We have run Microsoft Sentinel in production since 2019, as a Microsoft Solutions Partner.
1:21Book a Demo
Bring us your Sentinel, and we will show you what it is missing. Book a demo.
Detection & Response
 1:18
Detection & Response
Managed AI SOC
What Wizard Cyber’s Managed AI SOC gives you on every incident: a finished case from specialised AI agents on CYBERSHIELD AI, signed off by a senior analyst, in the Core, Complete or Command package.
 1:21
Detection & Response
Bypassing MFA
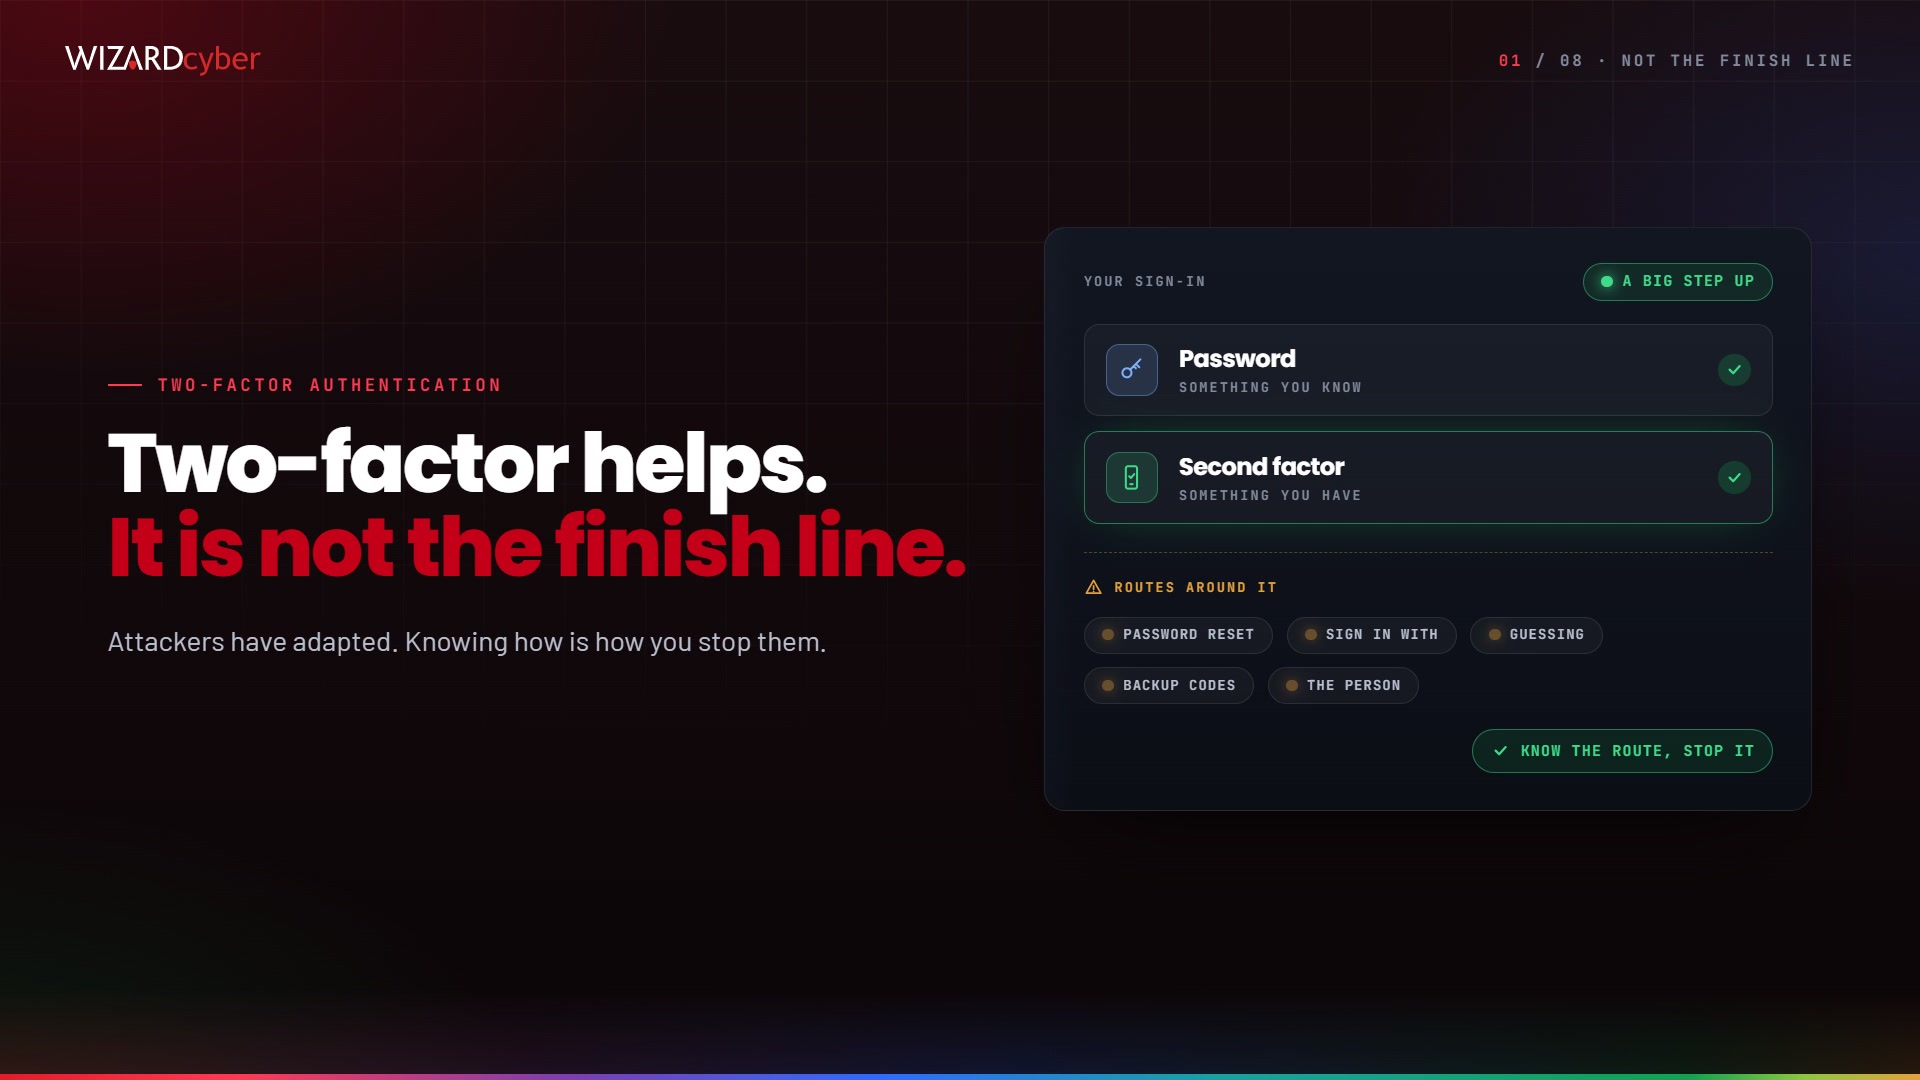
Two-factor authentication is a big step up from a password alone, but attackers have adapted. The routes they use around it, the warning signs to watch for, and the factors that cannot be relayed.
 1:34
Detection & Response
Microsoft XDR
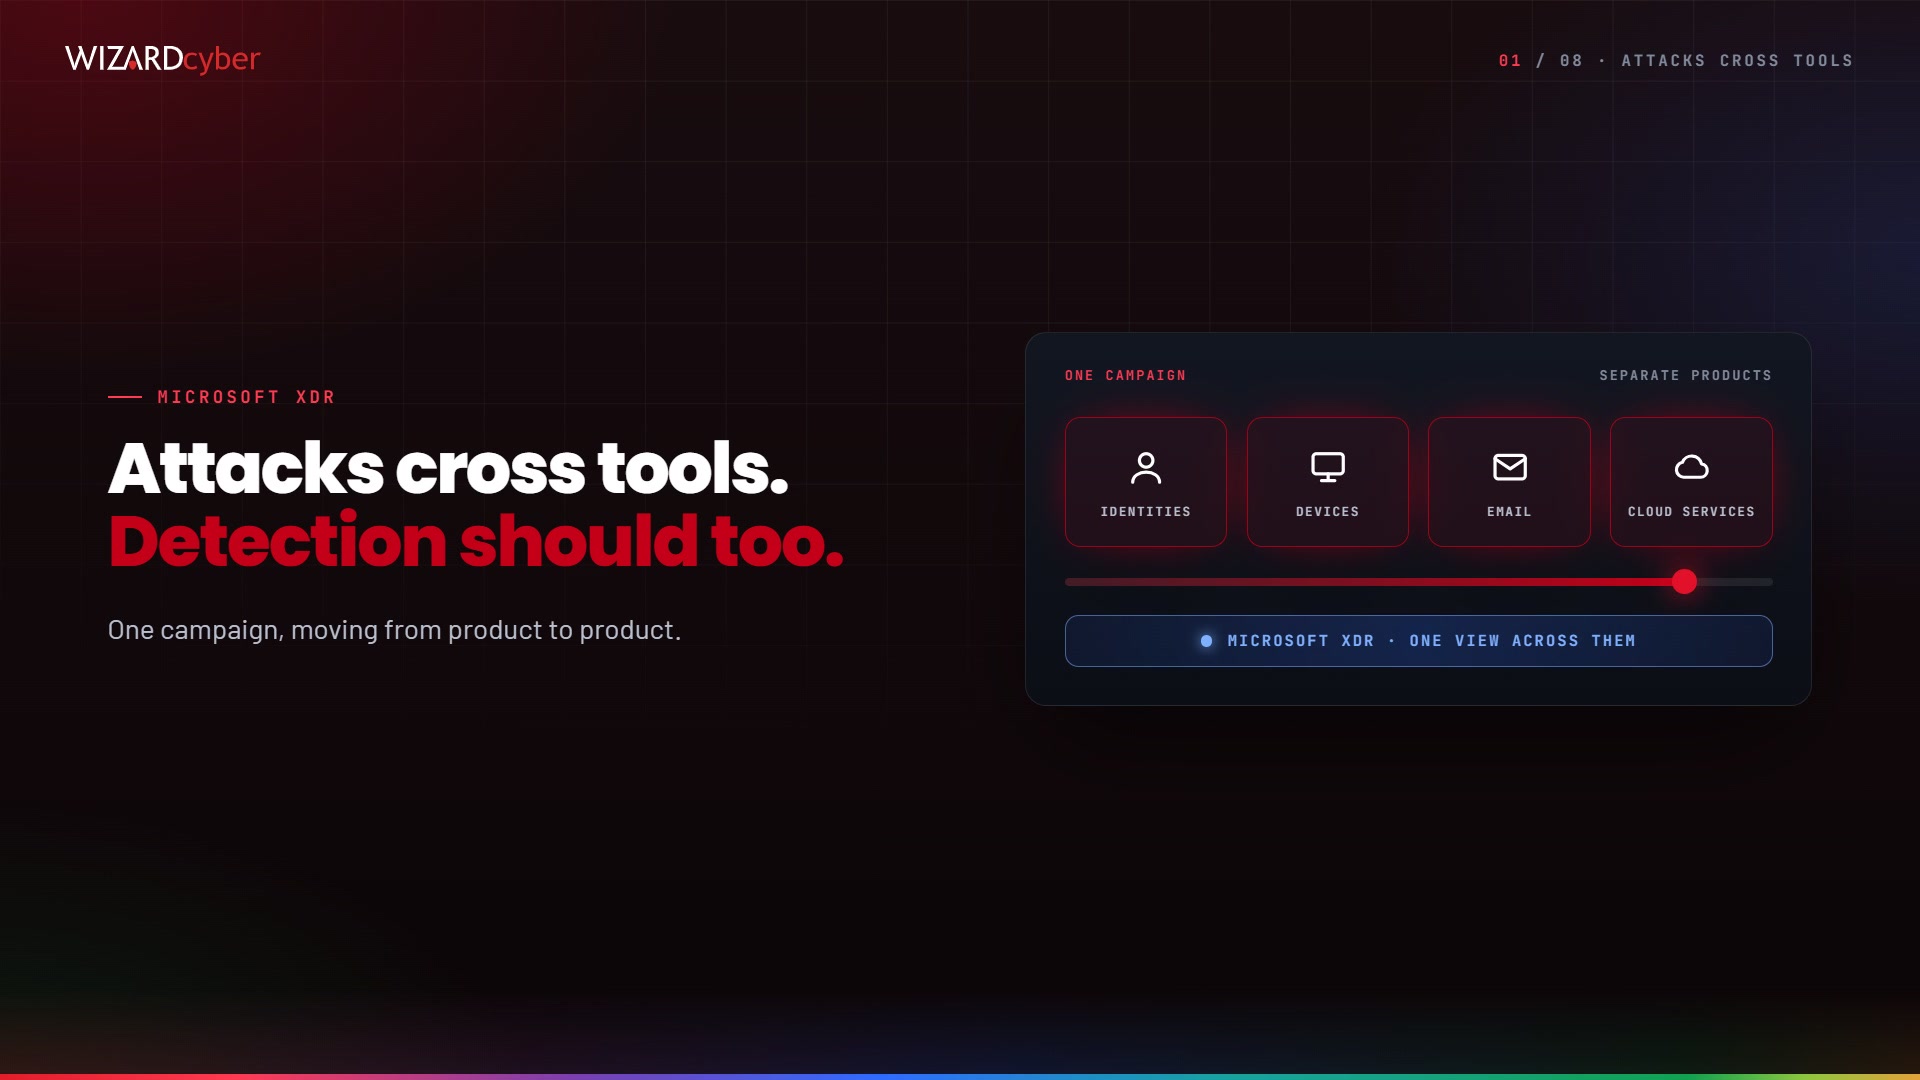
Microsoft XDR explained: how Microsoft Defender and Microsoft Sentinel connect signals across identities, endpoints, email and cloud, group them into single incidents, and contain threats from one place.
Watch it run
on your own alert types.
An hour with a SOC analyst: a live investigation from signal to signed verdict, and the autonomy dial set where you would set it. Your scenarios, not a canned demo.