
Microsoft Security
The Microsoft security stack as a working whole — Defender, Entra, Purview and Copilot — and how identity, endpoint and cloud signals reach a SOC.
 Microsoft Security
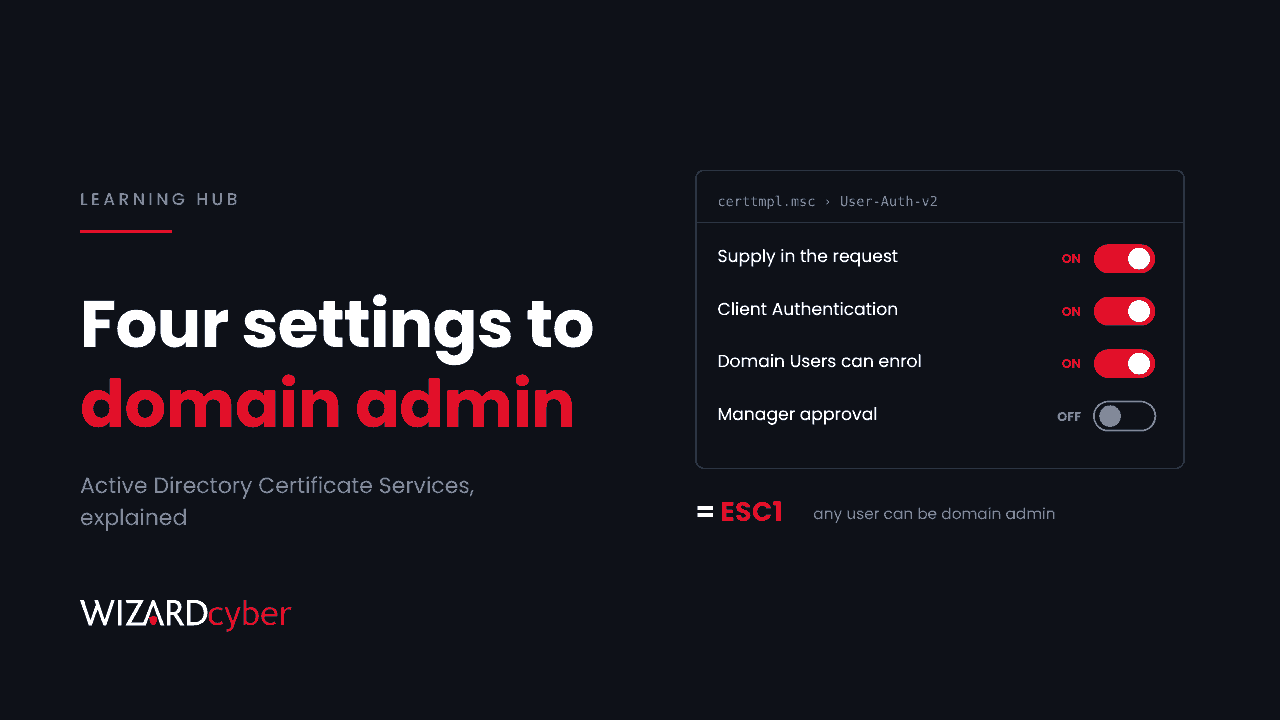
What Is AD CS? Active Directory Certificate Services, ESC1 And ESC8 Explained, And How To Harden Them
AD CS issues the certificates your Windows estate trusts. How it works, why ESC1 and ESC8 turn it into a route to domain admin, and how to audit and harden it.
 Microsoft Security
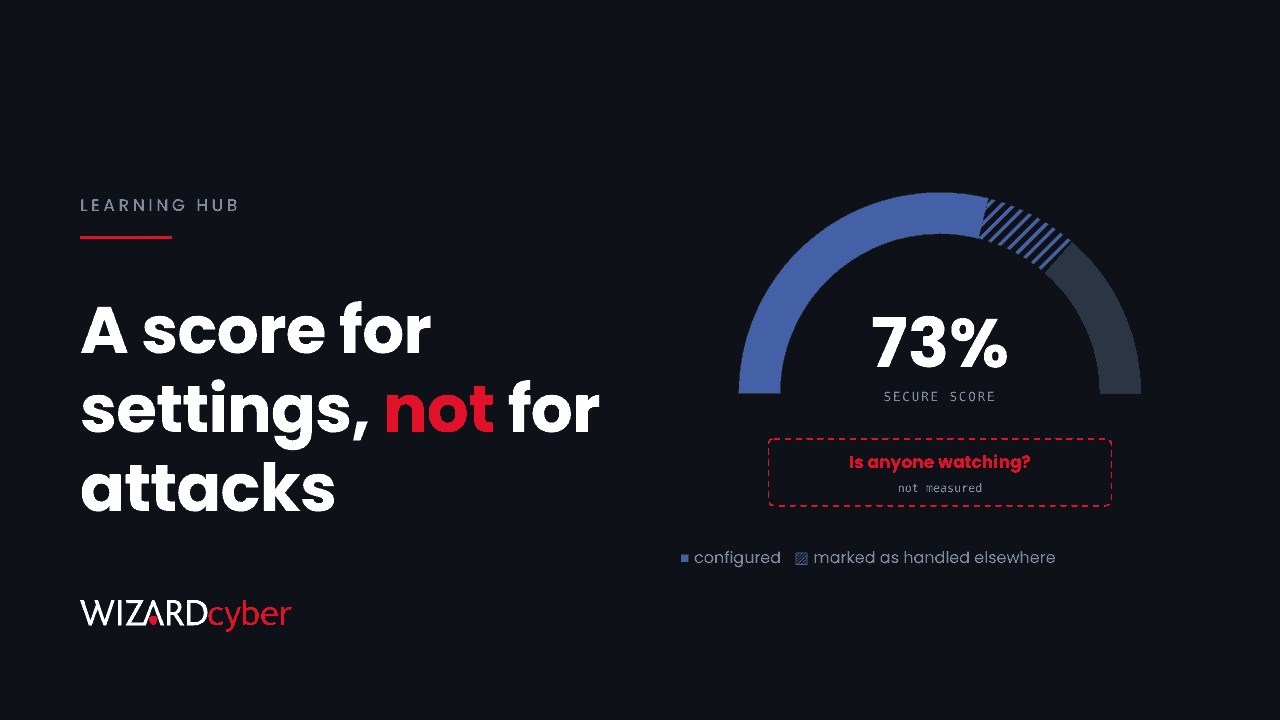
What Is Microsoft Secure Score? What It Measures, What It Misses, And How To Raise It Safely
Microsoft Secure Score measures your Microsoft 365 security configuration. How it is calculated, what it misses, and how to raise it safely.
 Microsoft Security
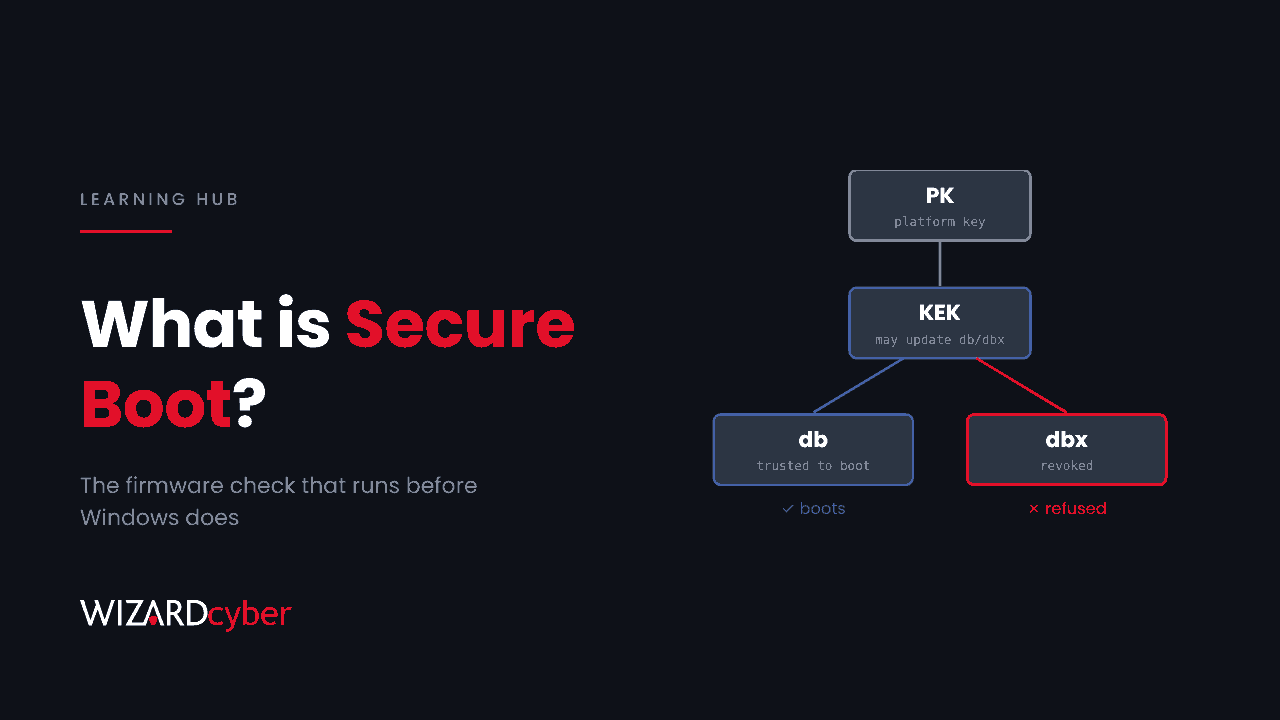
What Is Secure Boot? How It Works, Why It Matters, And How Bootkits Still Get Past It
Secure Boot only lets signed, trusted software start before Windows. How it works, what it misses, the 2026 certificate changes and how to check it.
 Microsoft Security
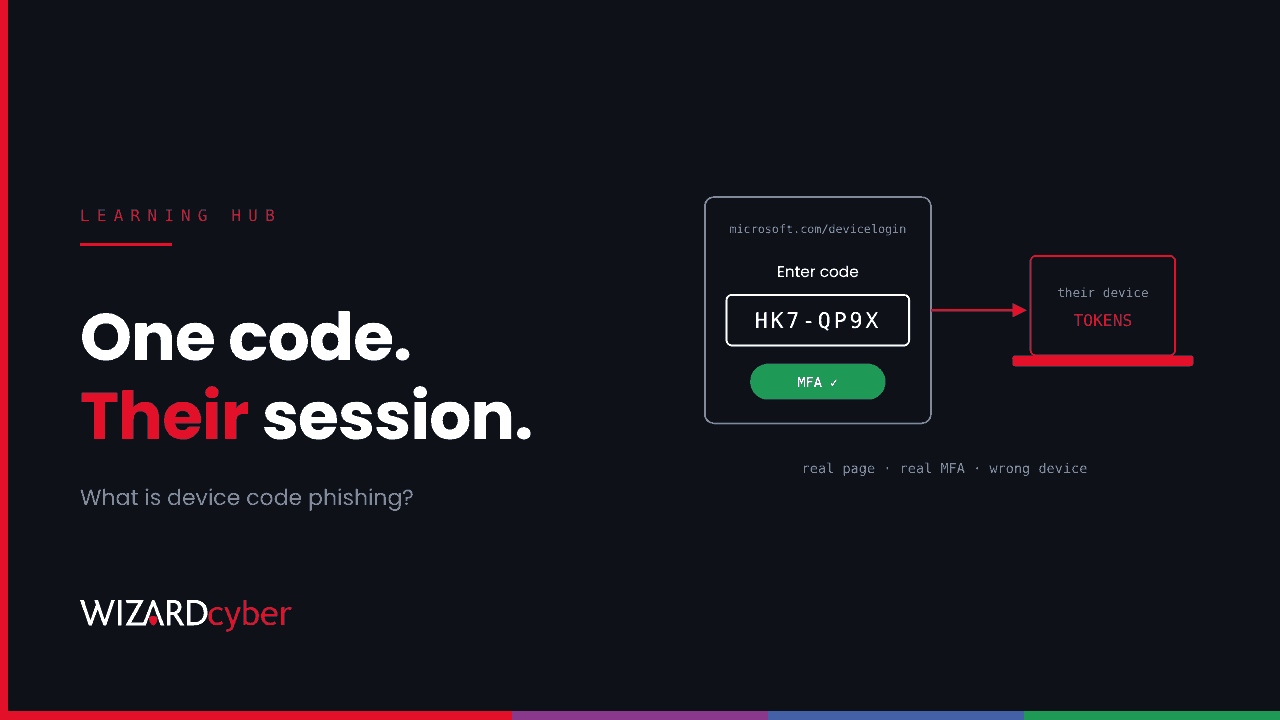
What Is Device Code Phishing? How It Works In Microsoft 365, And How To Block It
Device code phishing tricks users into signing in on Microsoft's real page for an attacker's device. How it works, how to detect it and how to block it.
 Microsoft Security
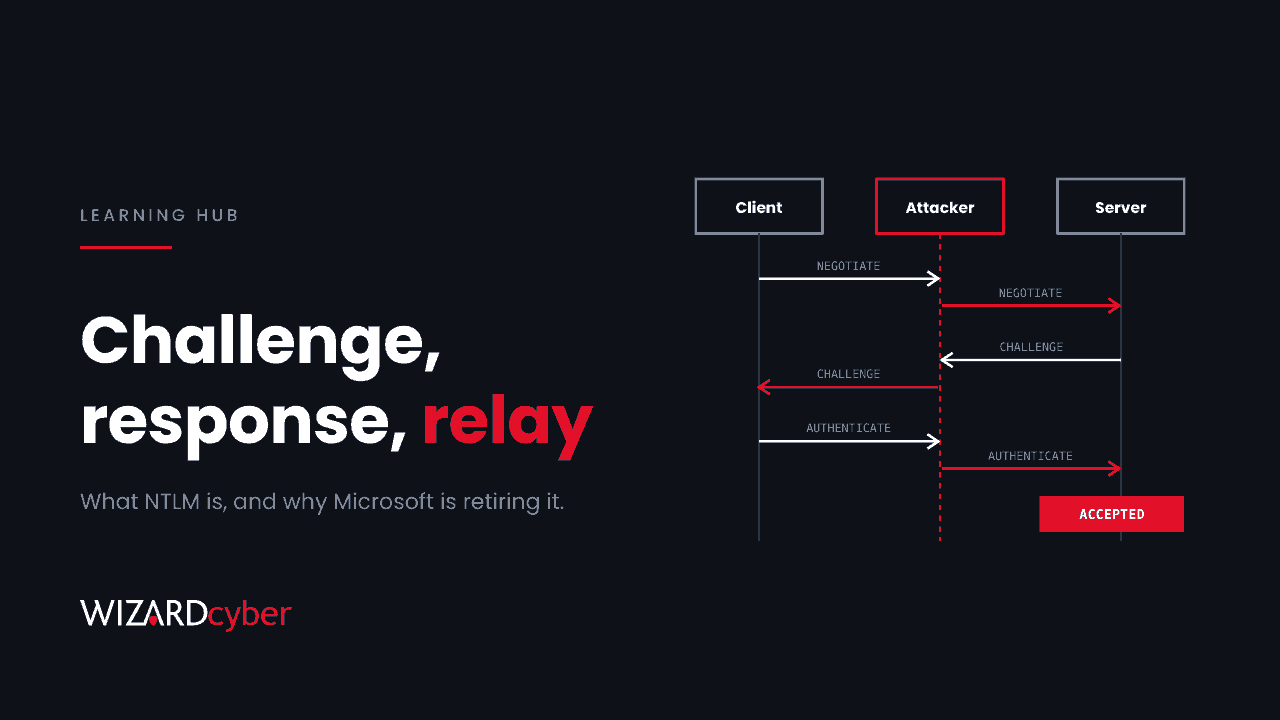
What Is NTLM? How It Works, Why Microsoft Is Retiring It, And How Attackers Abuse It
NTLM is Windows' older challenge-response authentication. How it works, how it differs from Kerberos, how attackers abuse it, and how to find and reduce it.
 Microsoft Security
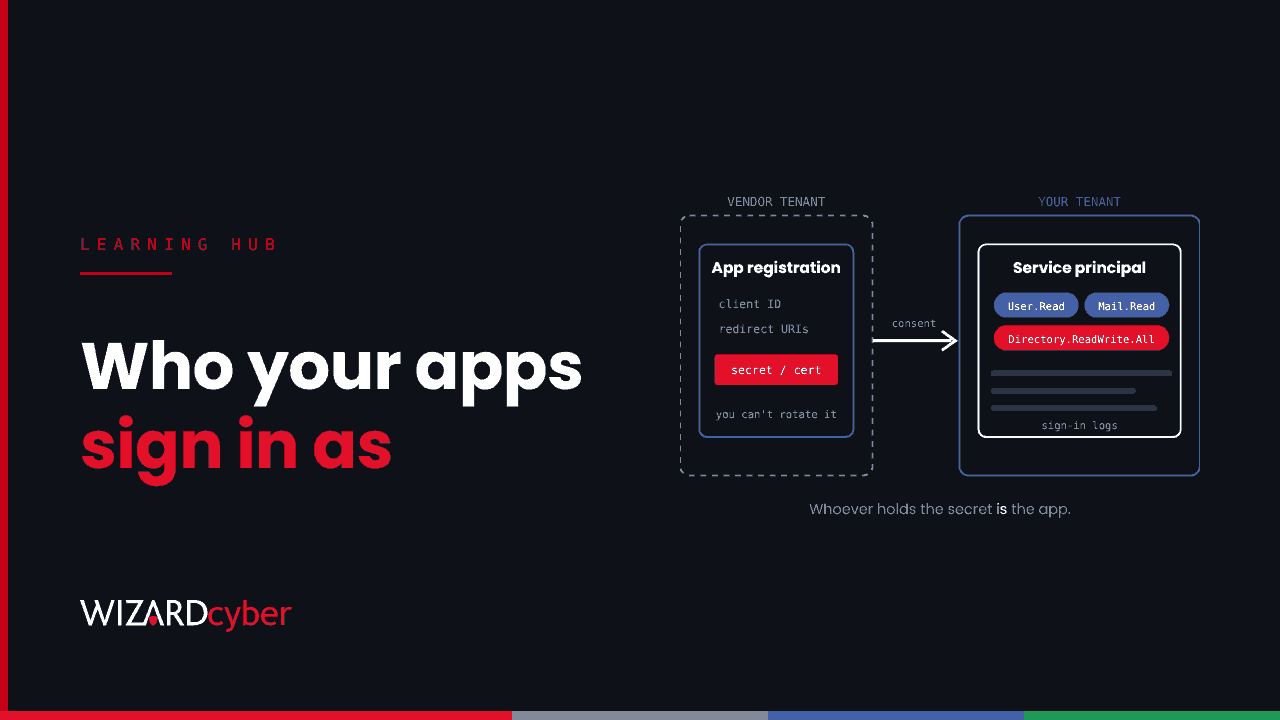
What Is A Service Principal? App Registrations, Enterprise Apps And How To Secure Them In Entra
A service principal is an app's identity in your Entra tenant. How it relates to app registrations, where secrets live, and how to secure and monitor them.
 Microsoft Security
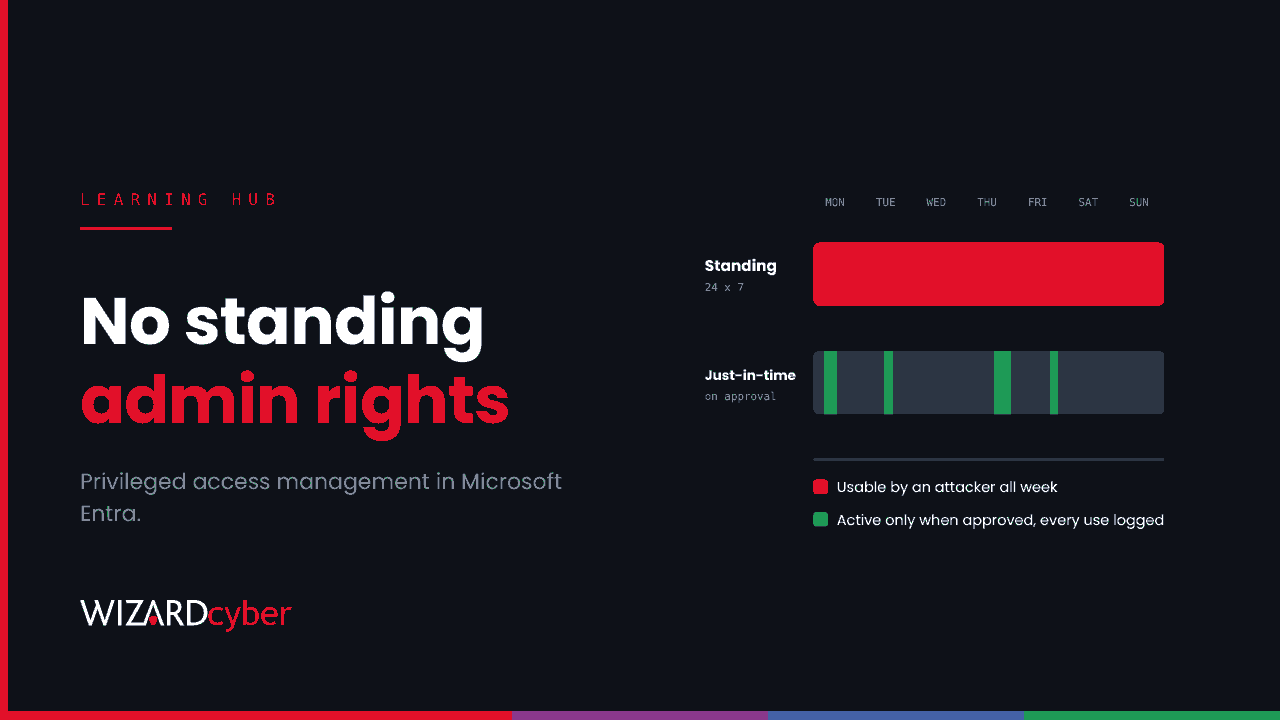
What Is Privileged Access Management (PAM)? How It Works In Microsoft Entra, And Where It Fails
Privileged access management controls who holds admin rights, when and how. How PAM works in Microsoft Entra with PIM, and where it usually fails.
 Microsoft Security
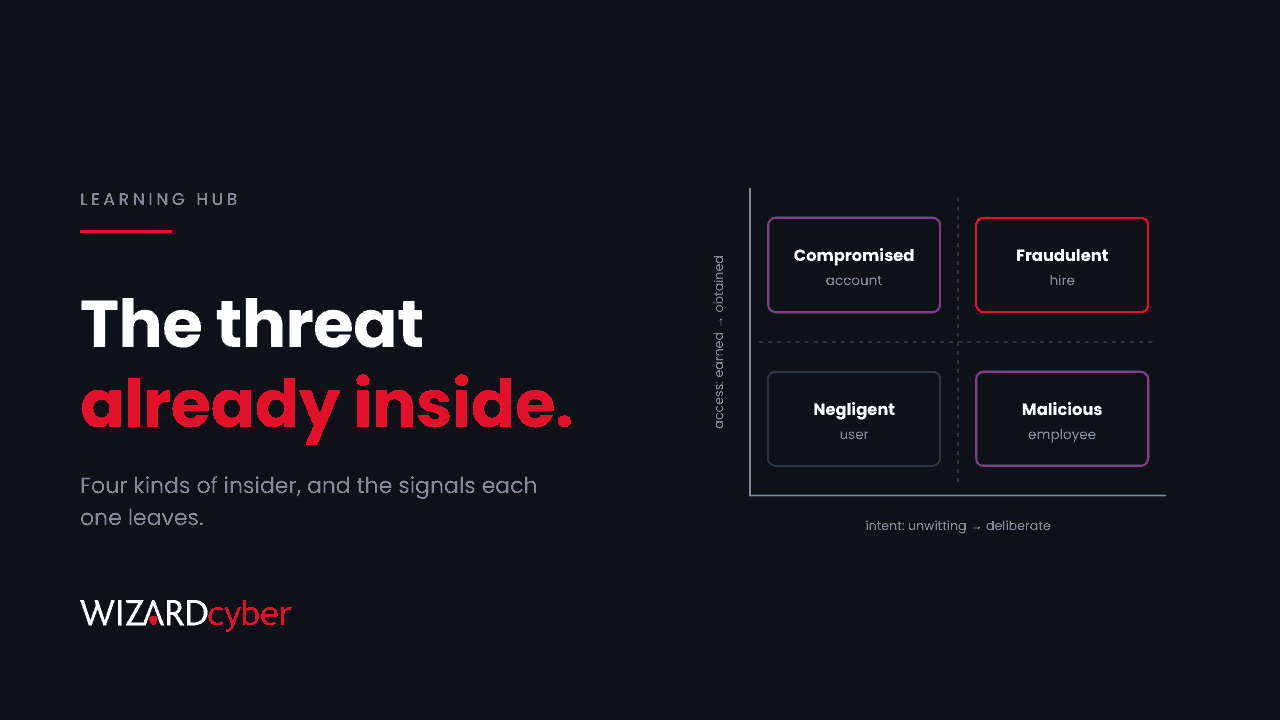
What Is An Insider Threat? Types, Warning Signs And How To Detect Them In Microsoft 365
An insider threat is harm caused through legitimate access. The four types, the warning signs, and how to detect insider risk in Microsoft 365.
 Microsoft Security
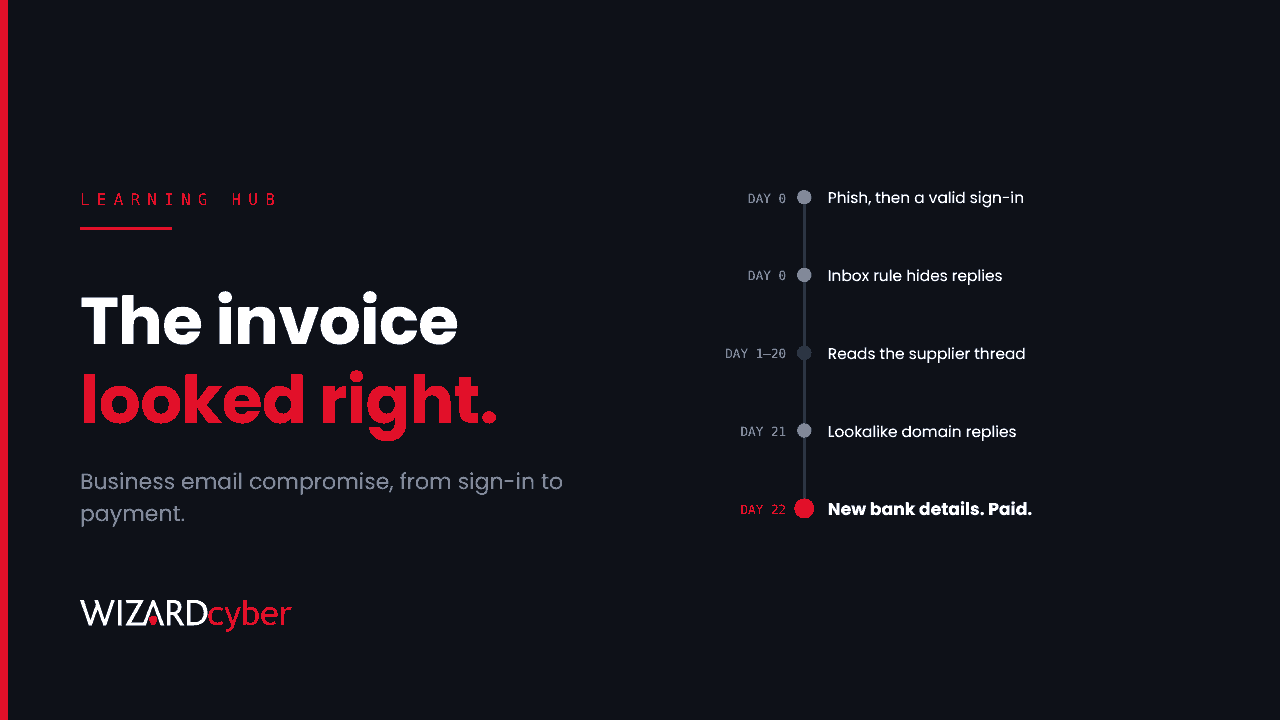
What Is Business Email Compromise (BEC)? How It Works And How To Stop It In Microsoft 365
Business email compromise uses a hijacked or spoofed mailbox to divert payments. How BEC works, the signs in Microsoft 365, and how to stop it.
 Microsoft Security
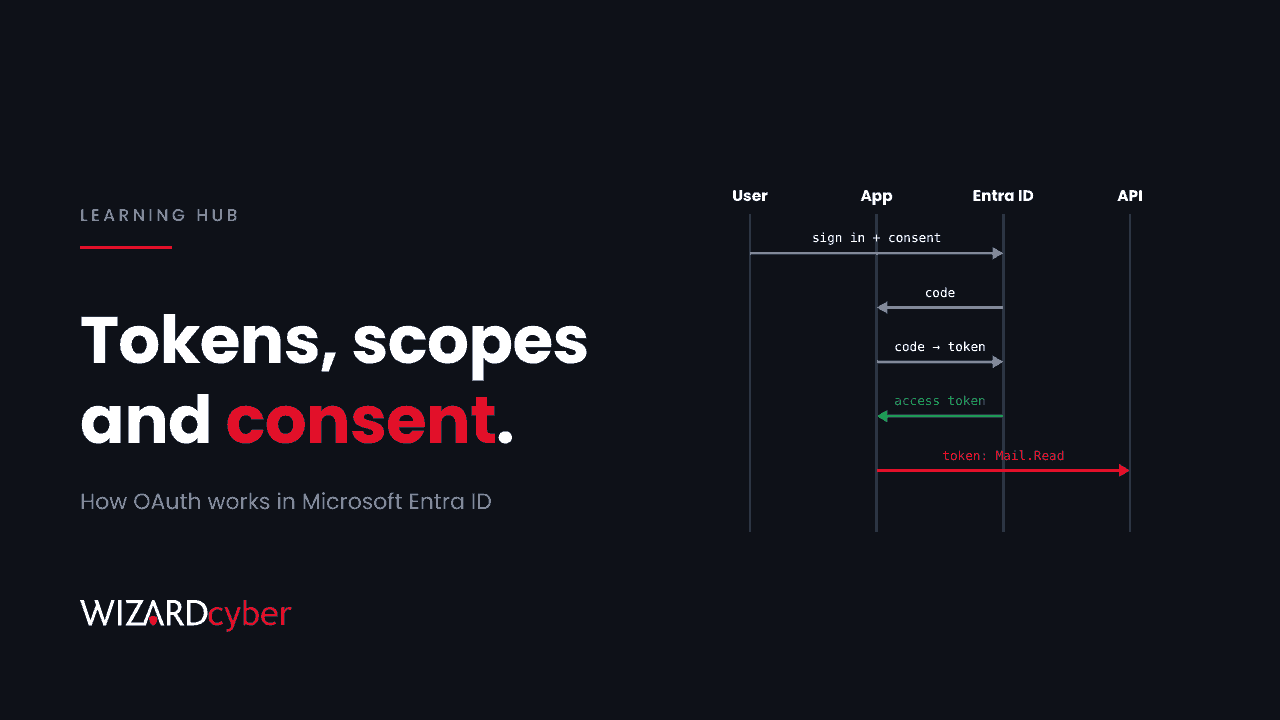
What Is OAuth? How It Works In Microsoft Entra ID, And How Attackers Abuse It
OAuth lets apps access data on your behalf without your password. How tokens, scopes and consent work in Entra ID, and how attackers abuse them.
 Microsoft Security
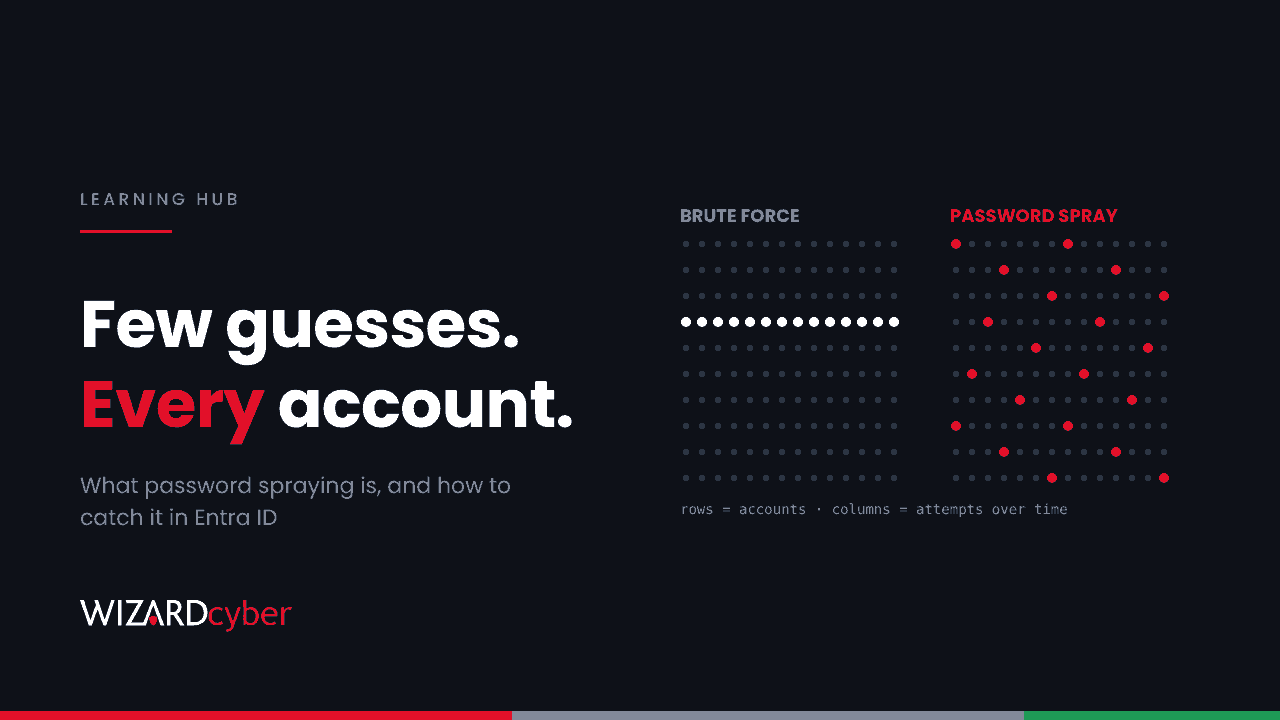
What Is Password Spraying? How It Works And How To Detect It In Microsoft Entra ID
Password spraying tries a few common passwords across many accounts to dodge lockouts. How it works, why MFA gaps matter and how to spot it in Entra ID.
Microsoft SecurityMicrosoft 365 E5 vs E7: What the New Tier Actually Adds
Microsoft 365 E7 sits above E5 and bundles Copilot, Agent 365 and the Entra Suite. What the step up actually contains, who it is for, and the question to ask before buying it.
 Microsoft Security
Microsoft Defender XDR Explained
Understand Microsoft Defender XDR and how it correlates identity, endpoint, email, and cloud signals into incidents for SOC response.
 Microsoft Security
How Microsoft Security Powers Modern Security Operations
Discover how Microsoft Security powers modern SOC operations with incident-based detection, automation, and unified response.
 Microsoft Security
Using Microsoft Security To Improve Cyber Resilience
Learn how Microsoft Security improves cyber resilience through early detection, rapid response, and coordinated recovery.
 Microsoft Security
 Vs Third-Party Tools: Do You Need Both?
Explore whether Microsoft Security alone is enough or when third-party tools add value, and how to build a balanced security stack.
 Microsoft Security
Managed Microsoft Security: What Organizations Need To Know
Understand what managed Microsoft Security means, how it works, and when organizations choose it for 24/7 protection and faster response.
 Microsoft Security
Why Organizations Choose Managed Microsoft Security Services
Learn why organizations choose managed Microsoft Security services for 24/7 coverage, faster response, and predictable outcomes.
 Microsoft Security
Conditional Access, MFA, And Identity Protection Explained
Learn how Conditional Access, MFA, and Identity Protection secure access in Microsoft Entra with risk-based policy.
 Microsoft Security
Identity Is The New Perimeter: Why Microsoft Puts Identity First
Why identity is the new perimeter and how Microsoft Security protects access, detects abuse, and enables Zero Trust.
 Microsoft Security
How Attackers Abuse Identity — And How Microsoft Security Detects It
Learn how attackers abuse identity and how Microsoft Security detects credential theft, token abuse, and privilege misuse early.
 Microsoft Security
Identity Threat Detection And Response (ITDR) With Microsoft Security
Learn how Microsoft Security delivers ITDR by correlating identity signals with endpoint, email, and cloud detection.
 Microsoft Security
Understanding The Microsoft Security Stack: A Unified Approach
Learn how the Microsoft Security stack unifies identity, endpoint, cloud, and SOC operations for coordinated detection and response.
 Microsoft Security
Microsoft Entra ID Security: Protecting Identities In A Cloud-First World
Discover how Microsoft Entra ID secures identities with MFA, Conditional Access, and real-time threat detection.
 Microsoft Security
What Is Microsoft Security? An Overview Of Microsoft’s Security Platform
An overview of Microsoft Security, its unified platform approach, and how it protects identities, endpoints, cloud, and data.
 Microsoft Security
How Microsoft Security Supports A Zero Trust Architecture
How Microsoft Security applies Zero Trust principles across identity, access, devices, detection, and SOC operations.
 Microsoft Security
 Explained: From Identity To Cloud To SOC
How Microsoft Security connects identity, endpoint, cloud, and SOC capabilities to detect threats across the full attack path.
Nothing matches that.