
Threat Research
Detections our analysts wrote and threats they pulled apart — published as we find them, not to a content calendar.
 Threat Research
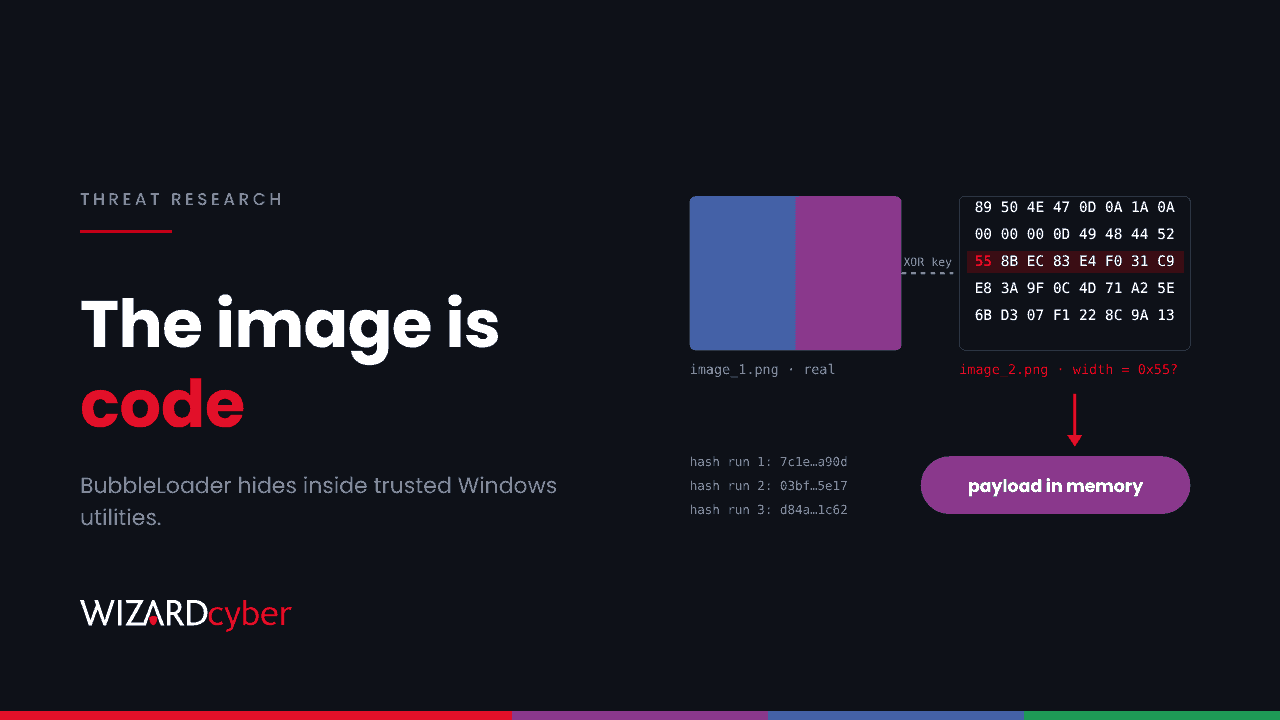
The Utility Is Real, The Image Isn't: Hunting BubbleLoader's Fake-PNG Loader In Trojanised Windows Tools
BubbleLoader patches familiar Windows tools and hides its code in a fake PNG, so hashes won't catch it. How it works, and how to hunt for it in Defender.
 Threat Research
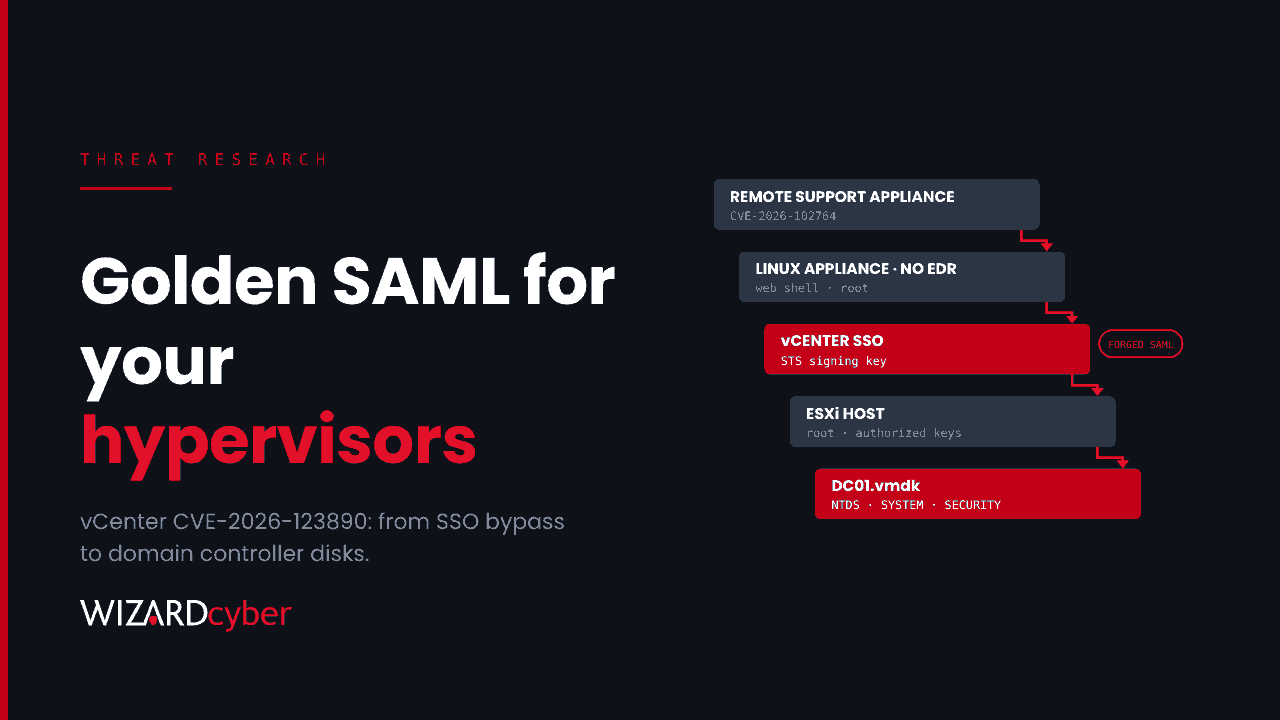
Golden SAML For Your Hypervisors: Hunting Armory Castle's vCenter Zero-Day (CVE-2026-123890) From Sentinel
A vCenter zero-day let Armory Castle forge SAML, backdoor ESXi and copy domain controller disks. What to hunt in Sentinel, and how to recover.
 Threat Research
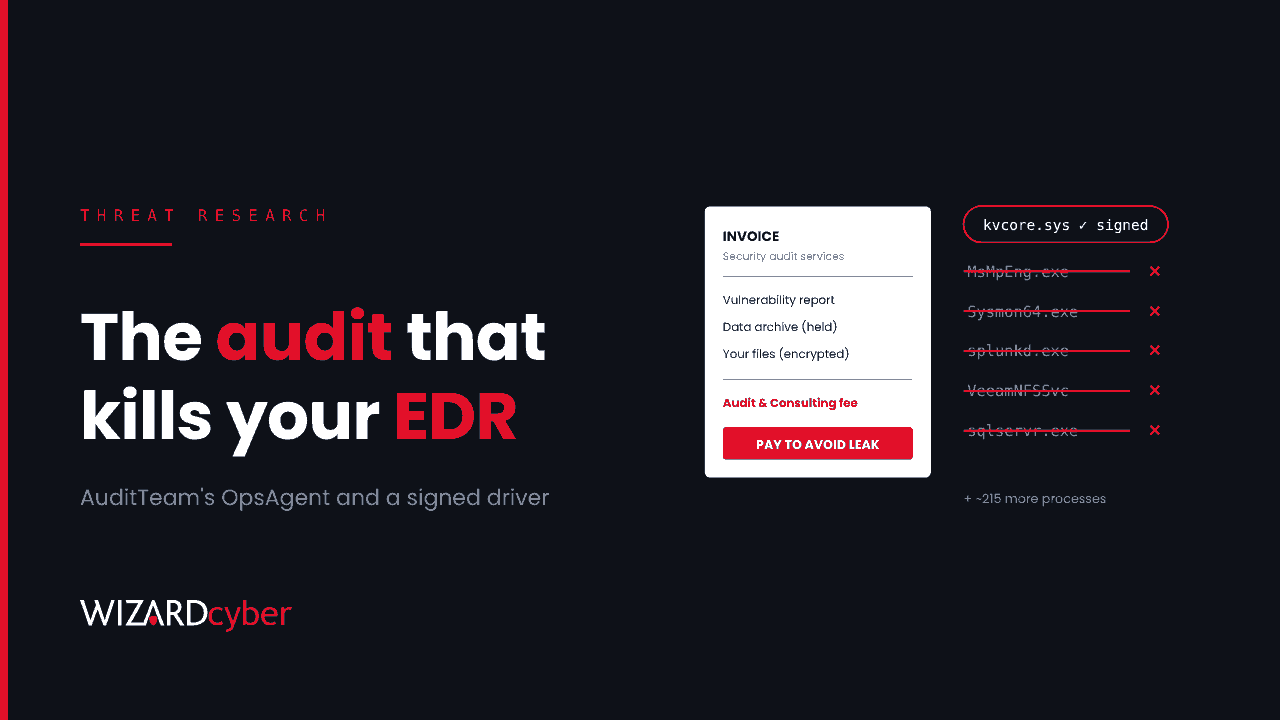
It Kills Defender First: Hunting AuditTeam's OpsAgent EDR Killer And 'Security Audit' Ransomware In Defender
AuditTeam bills its ransom as an audit fee, after a signed driver kills Defender and 220 other processes. What it does, and Defender hunts to catch it.
 Threat Research
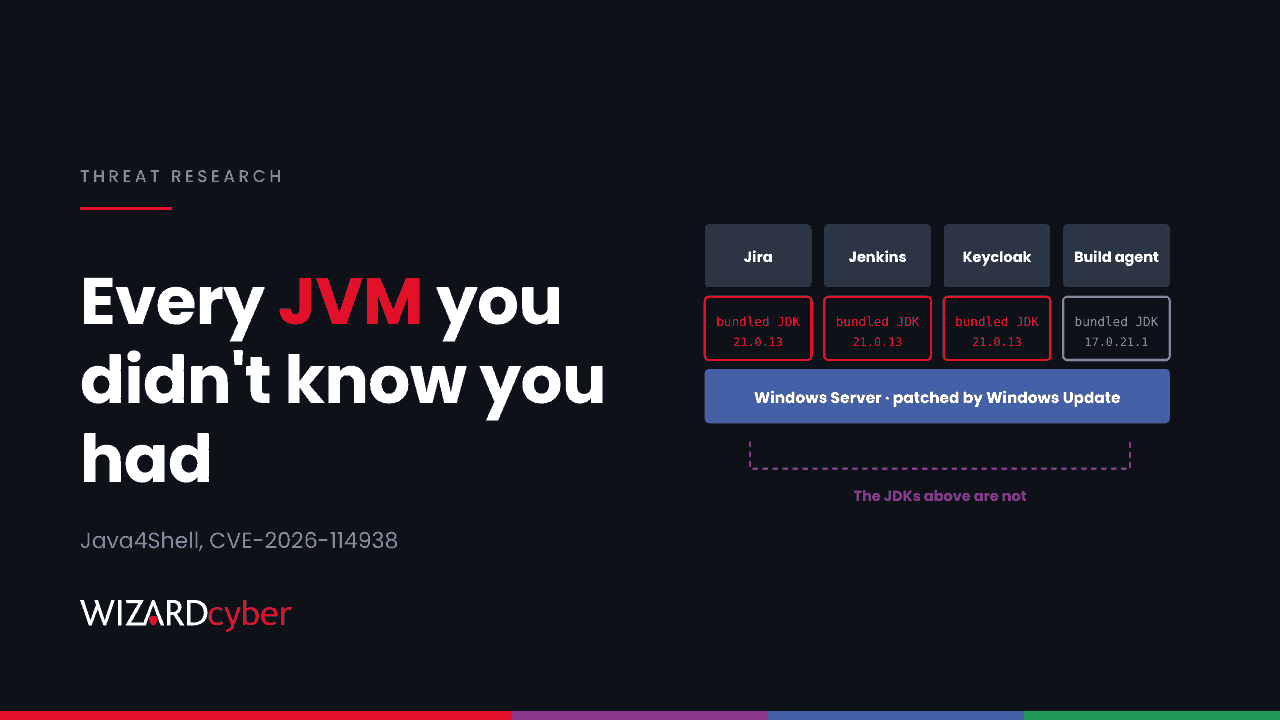
Every JVM You Didn't Know You Had: Finding Java4Shell (CVE-2026-114938) Exposure Before The Exploit Code Lands
Java4Shell gives pre-auth RCE in Jira, Jenkins and Keycloak, and bundled JDKs dodge Windows Update. How to find them with Defender and what to do first.
 Threat Research
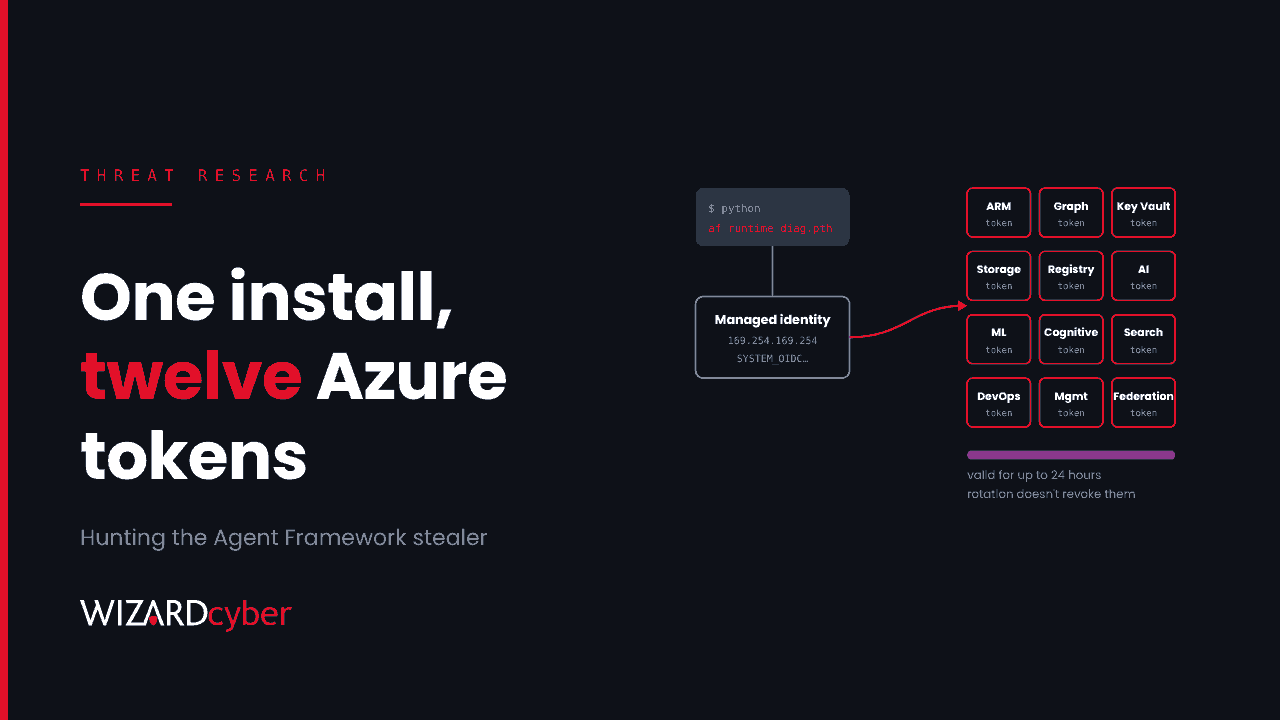
Thirty-Three Minutes On PyPI: Hunting The Agent Framework Stealer's Azure Token Theft In Entra ID And Azure DevOps
Two hijacked agent-framework releases minted Azure managed identity and pipeline tokens. How to find exposure and hunt token use in Entra and Azure.
 Threat Research
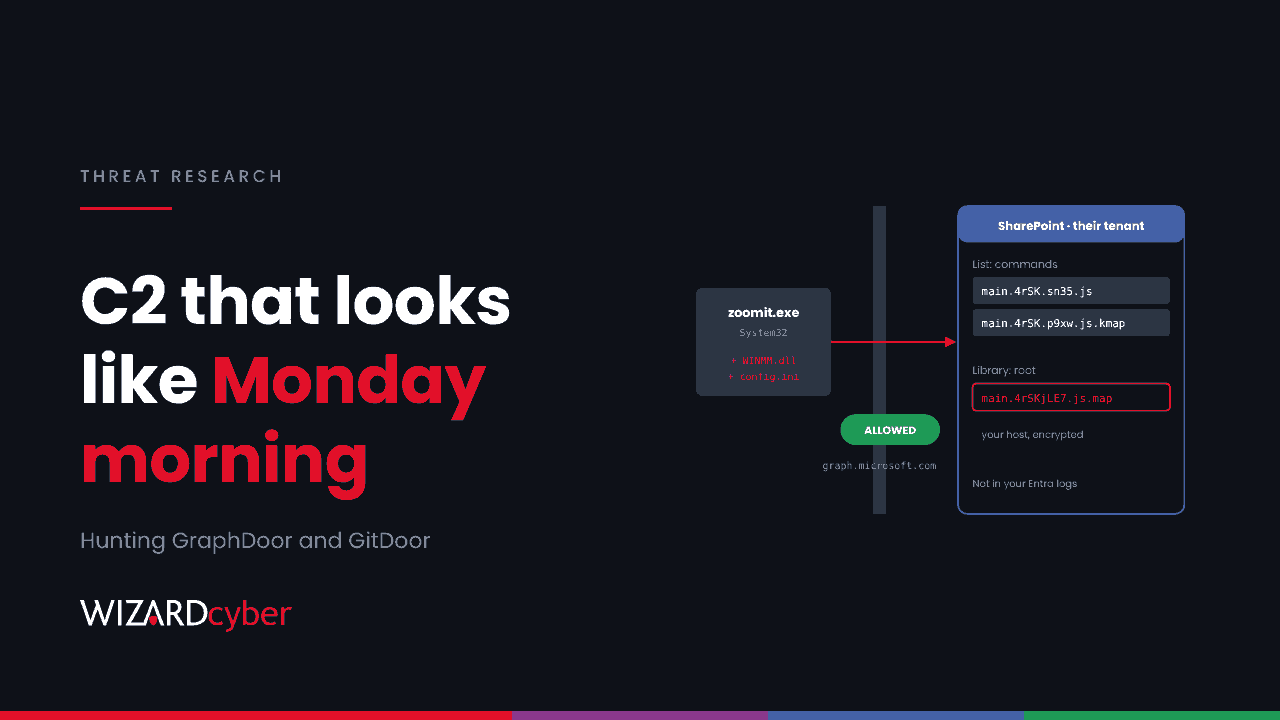
Command And Control Through SharePoint And GitHub: Hunting GraphDoor And GitDoor In Microsoft Defender
GraphDoor and GitDoor take orders through SharePoint and GitHub, so the traffic looks normal. Why Entra logs miss it, and where to hunt in Defender.
 Threat Research
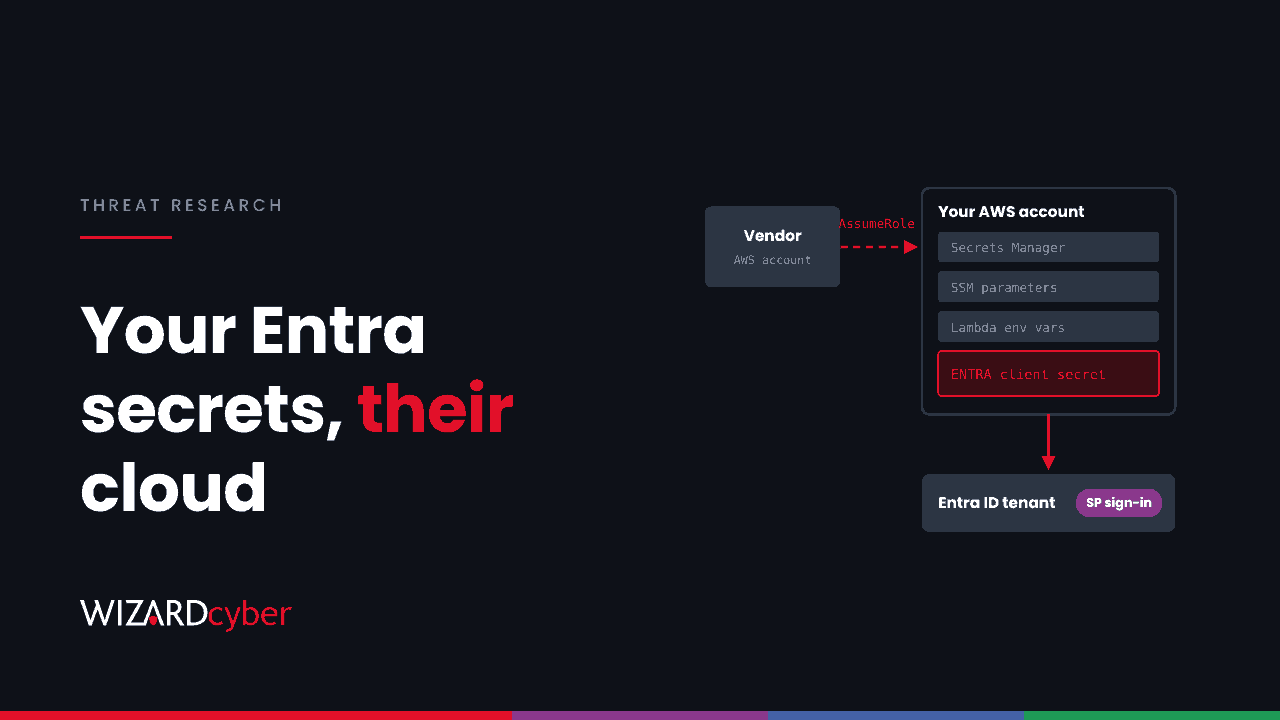
Your Entra Secrets Were Stored In Someone Else's Cloud: Hunting Downstream Of The Qubole Cross-Account Campaign In Entra ID
Attackers abused a vendor's AWS trust to harvest secrets, then signed in as Entra ID apps with them. How to hunt for it and what rotation doesn't fix.
 Threat Research
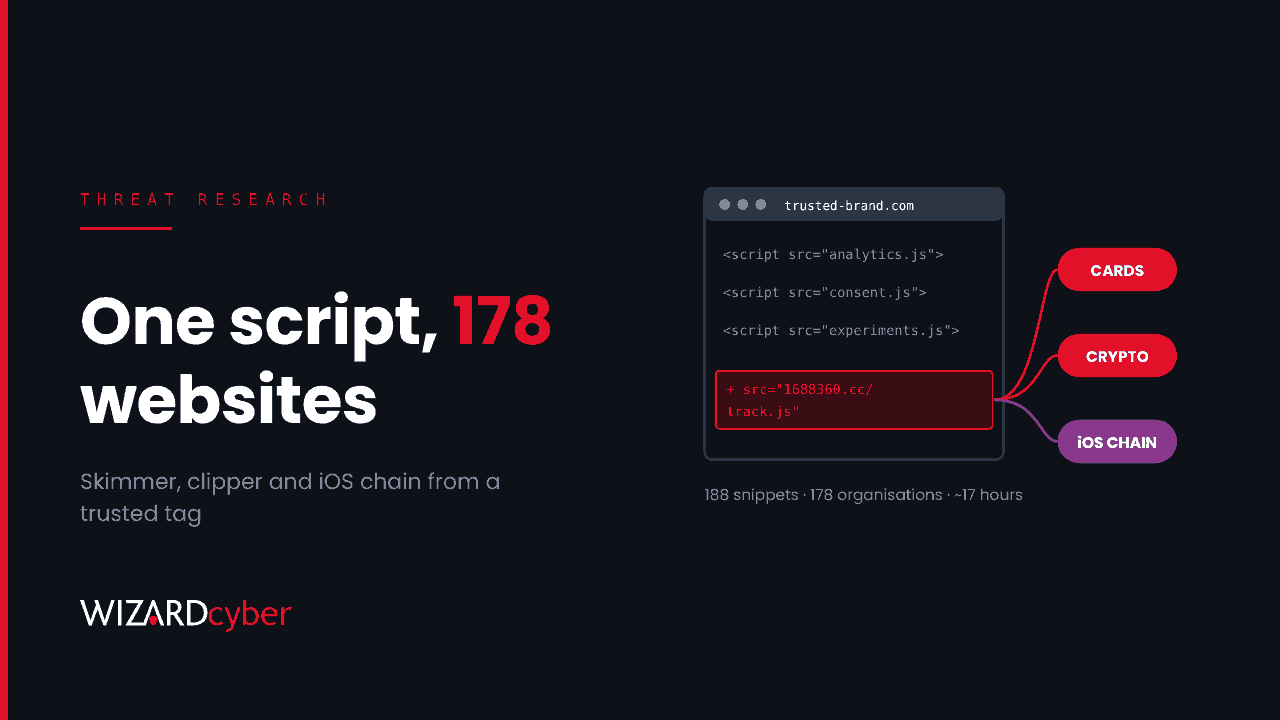
One Edited Script Field, 178 Websites: Hunting The Optimizely Skimmer And iOS Exploit Chain From Defender And Intune
Malicious JavaScript served through a trusted experimentation tool hit 178 organisations' sites. How to find exposed staff and devices from Defender and Intune.
 Threat Research
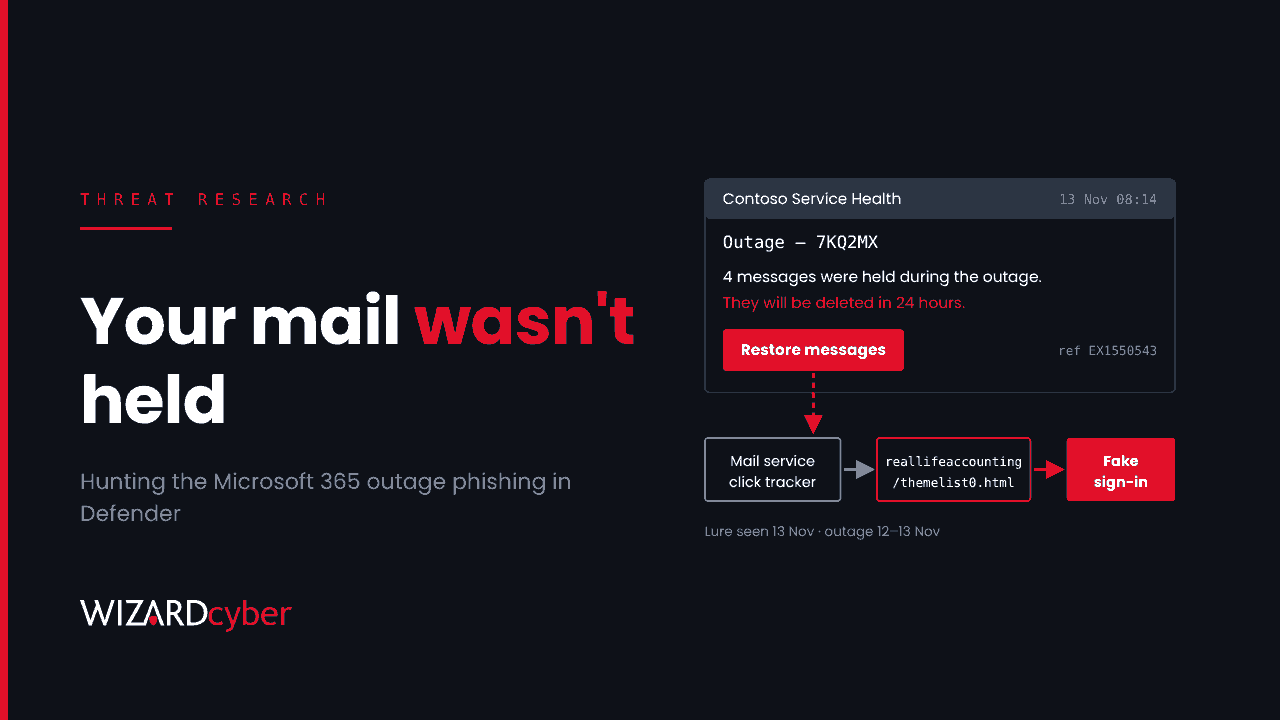
Your Mail Was "Held" During The Outage: Hunting The Microsoft 365 Outage Phishing In Defender For Office 365
Phishers used the 12–13 November Exchange Online outage as a lure within a day. The indicators, KQL to find who clicked, and what to do next.
 Threat Research
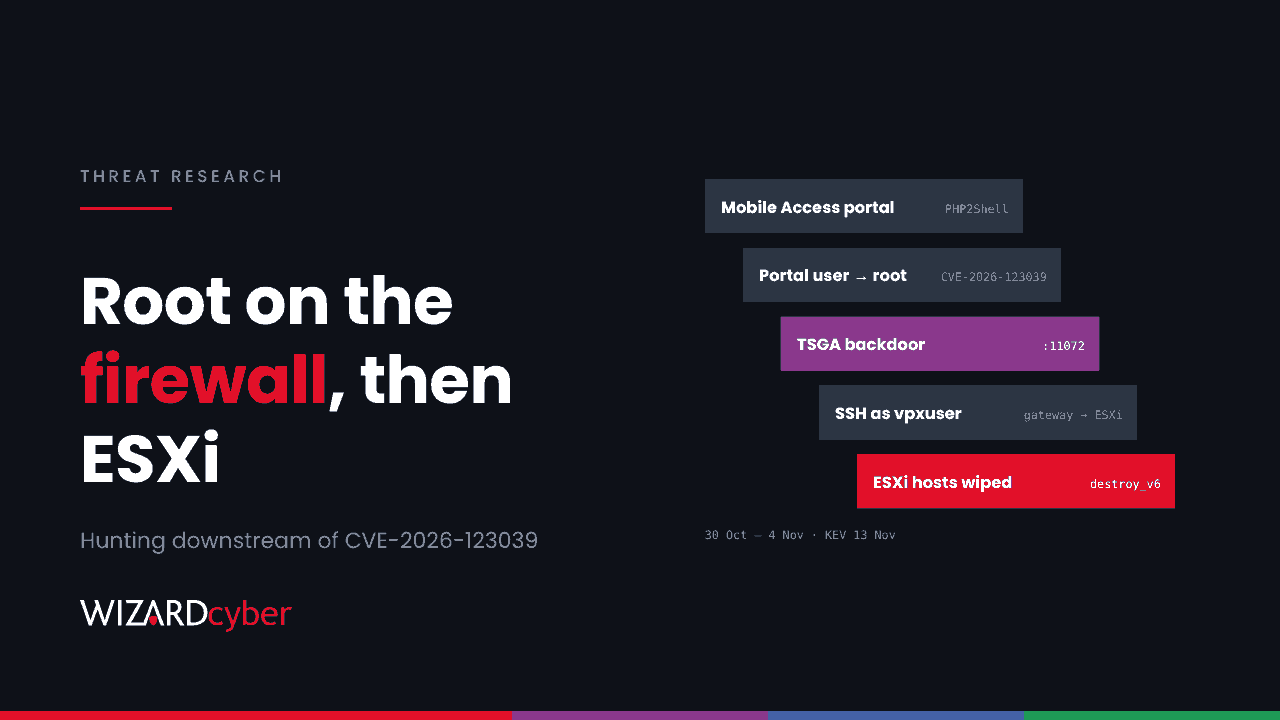
Root On The Firewall, Then The Hypervisors: Hunting Downstream Of Check Point CVE-2026-123039 And The TSGA Backdoor
PHP2Shell plus a Gaia root flaw put a backdoor on Check Point gateways and wiped some ESXi hosts. What happened, and what to hunt beyond the firewall.
 Threat Research
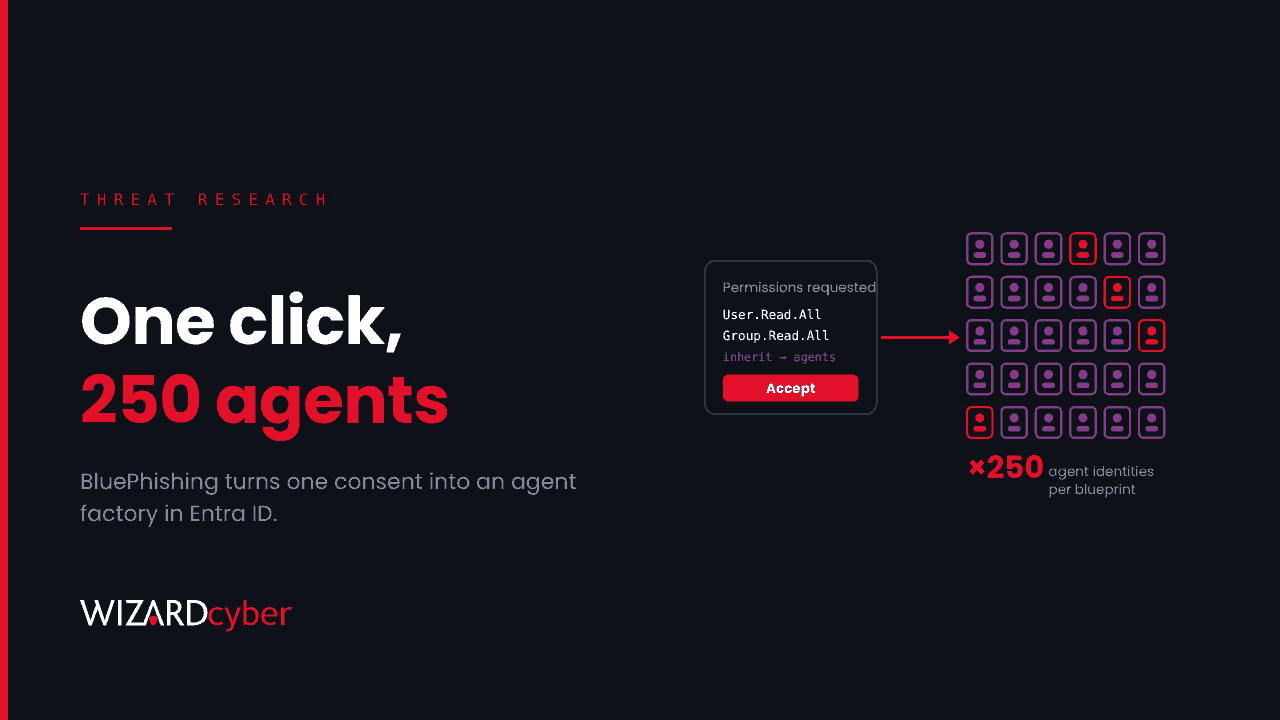
One Consent Click, Up To 250 Agents: Hunting BluePhishing Agent Blueprint Abuse In Microsoft Entra ID
BluePhishing turns one consent into up to 250 AI agent identities in your Entra tenant. How it works, KQL to hunt for it, and how to lock consent down.
 Threat Research
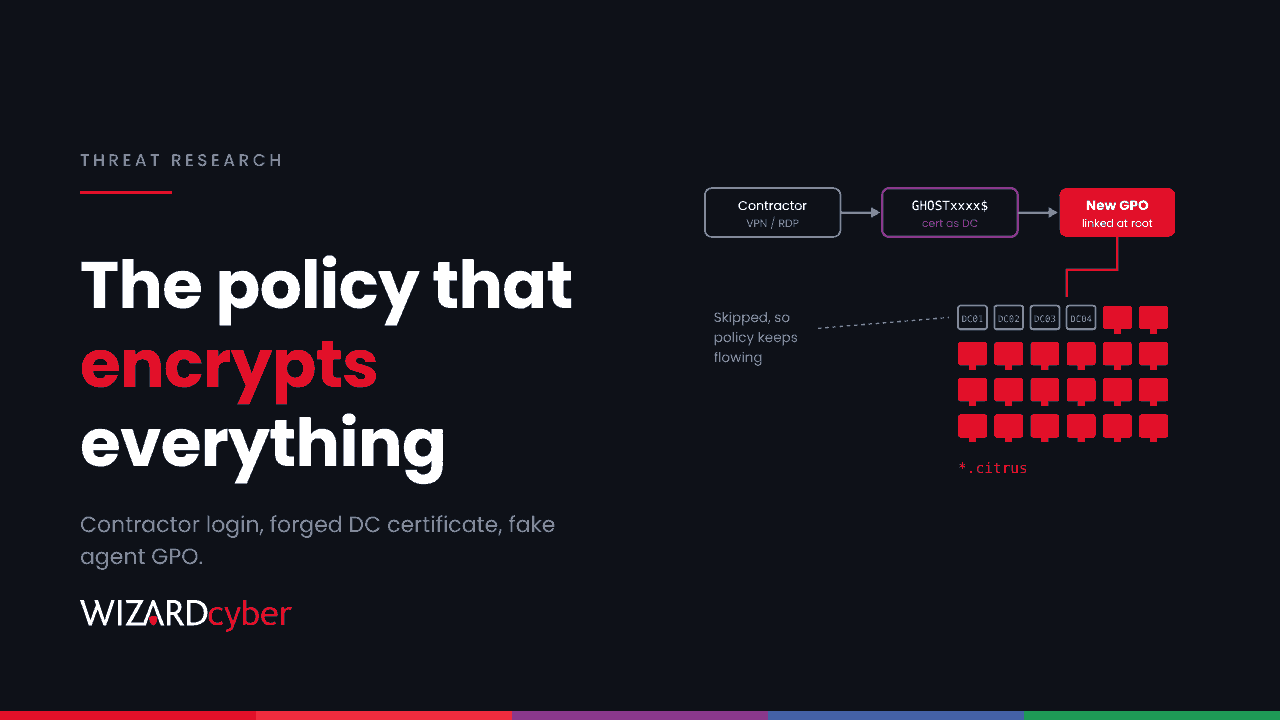
A Contractor's Login, A Fake Security-Agent GPO: Hunting The Citrus Ransomware Playbook In Active Directory
Citrus ransomware gets in through contractors, forges a DC certificate and deploys by Group Policy. How to hunt each step in Defender and Sentinel.
 Threat Research
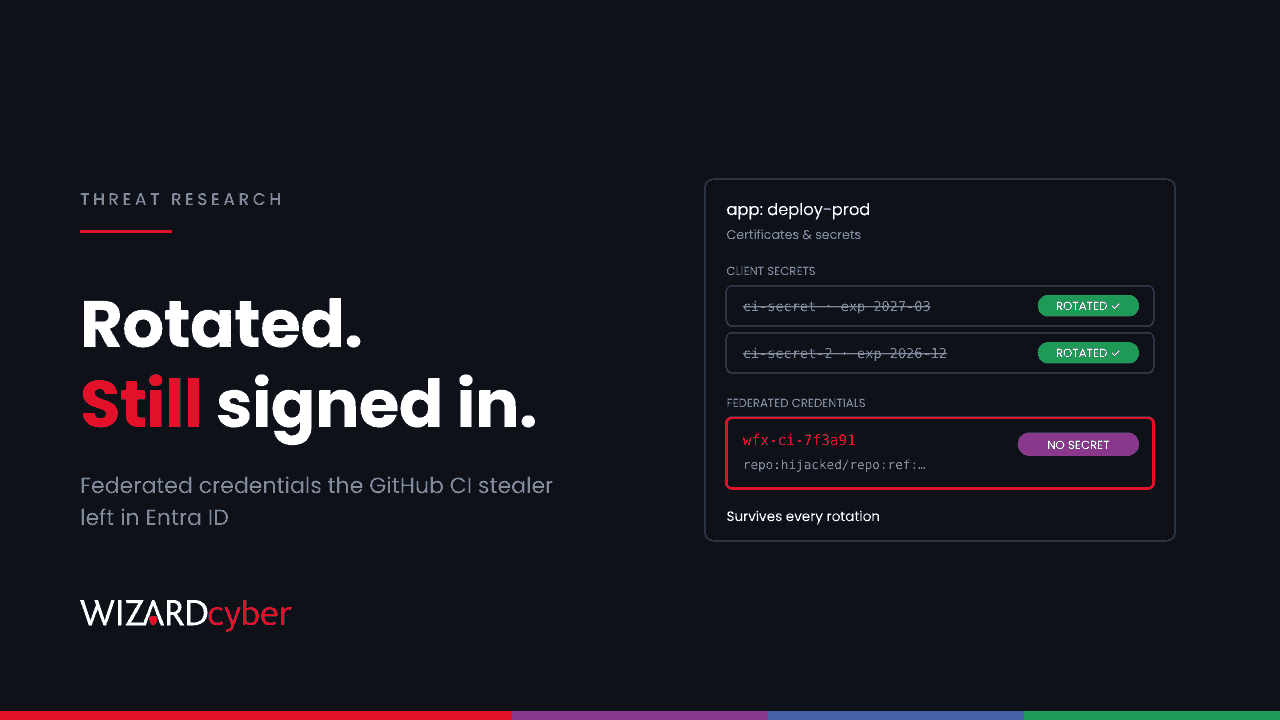
Rotated Every Secret, Still Signed In: Hunting The wfx-ci- Federated Credentials Left By The GitHub CI Stealer In Entra ID
A GitHub CI stealer added federated credentials to Entra ID apps that survive secret rotation. How to find them, and the order to clean up.
 Threat Research
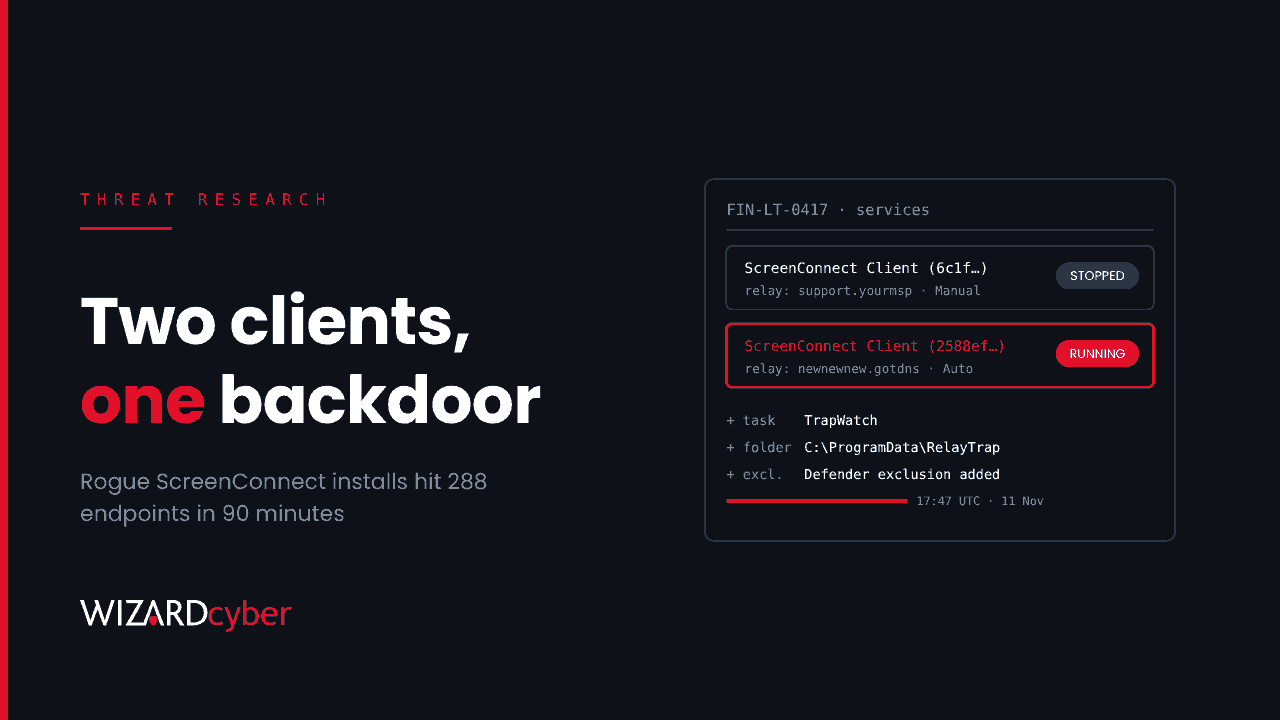
Your Support Tool, Their Backdoor: Hunting Rogue ScreenConnect Clients And The SCKit Worm In Defender
Attackers pushed rogue ScreenConnect clients to 288 endpoints in 90 minutes. What happened, and the Defender and Sentinel hunts to find it.
 Threat Research
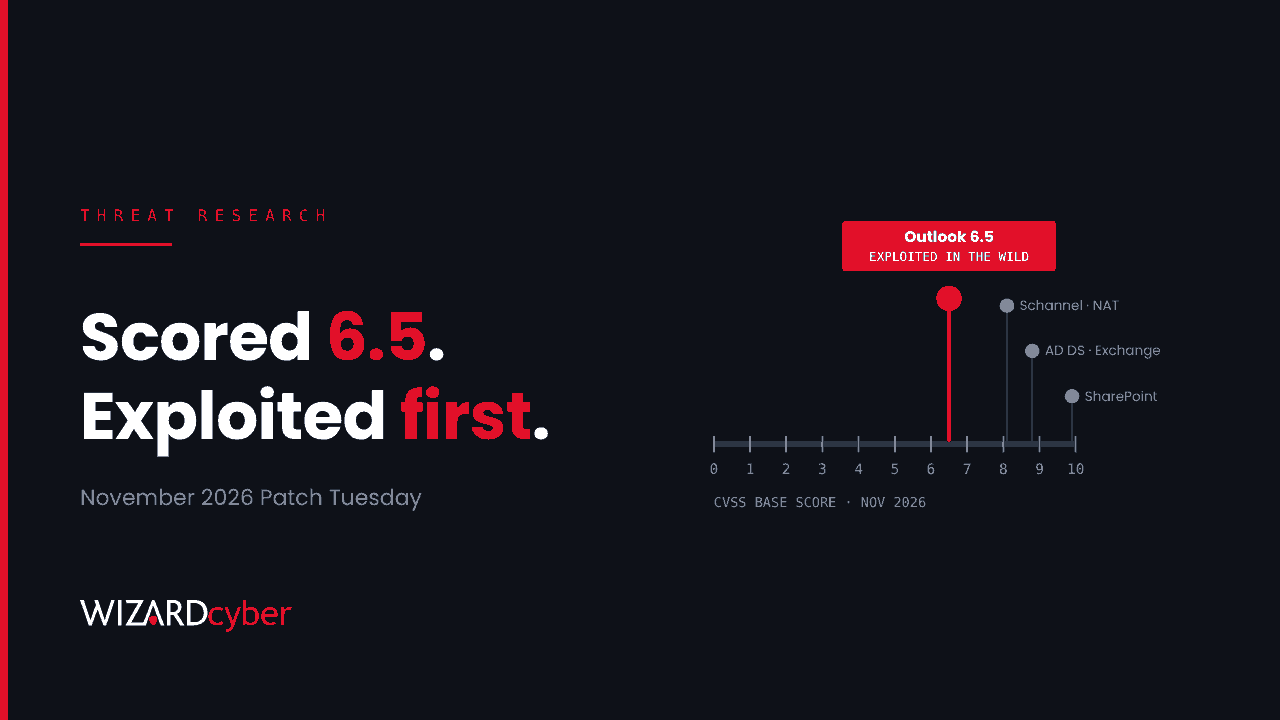
Rated Moderate, Exploited Anyway: November 2026 Patch Tuesday, The Outlook NTLM Zero-Day (CVE-2026-124194) And What To Patch First
The only exploited bug in November's 1,093-CVE release is a 6.5 Outlook flaw that leaks NTLM hashes. What to patch first, and how to hunt for it.
 Threat Research
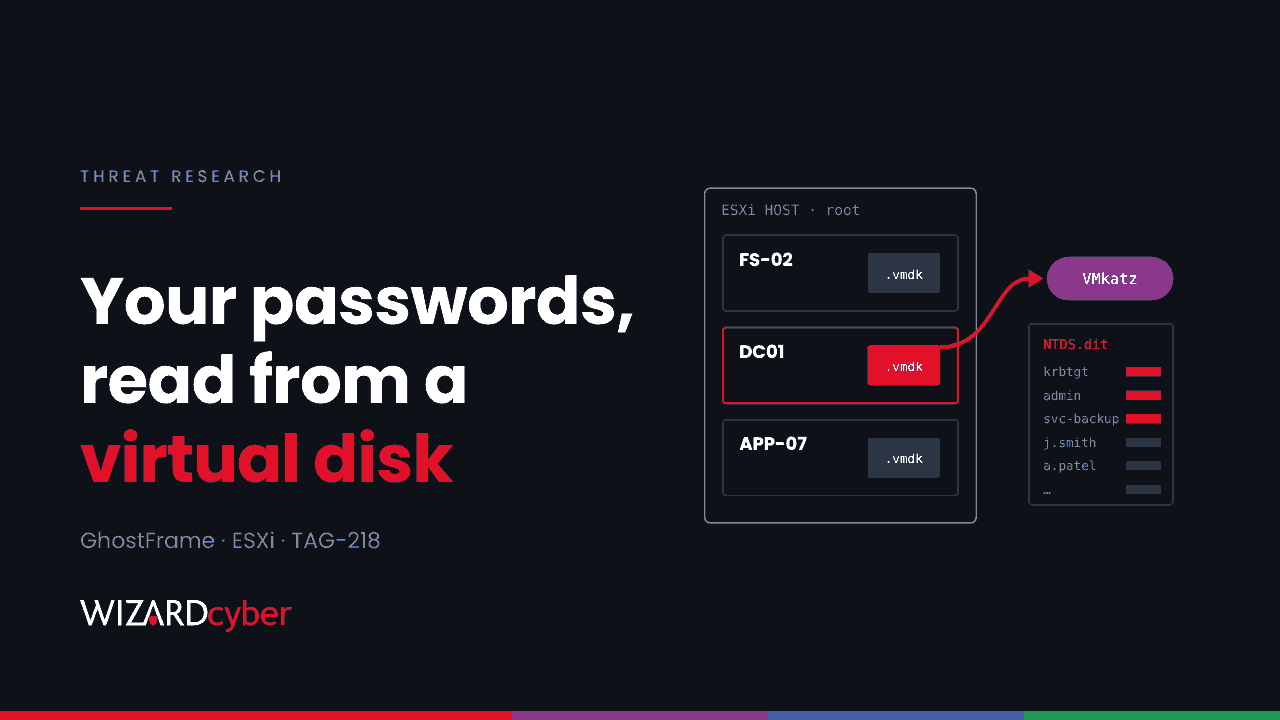
Your Domain Passwords, Read From A Virtual Disk: Hunting GhostFrame And TAG-218 From The Active Directory Side
GhostFrame reads NTDS.dit and other secrets straight from ESXi VM disks. How to hunt it before and after the hypervisor in Sentinel and Defender.
 Threat Research
Your MSP's Console Went Dark Overnight: What To Hunt Downstream Of The N-central Able2Shell Disclosure
N-able took N-central offline after 33 alleged zero-days went public. What to check in Defender and Entra for activity pushed through your RMM.
 Threat Research
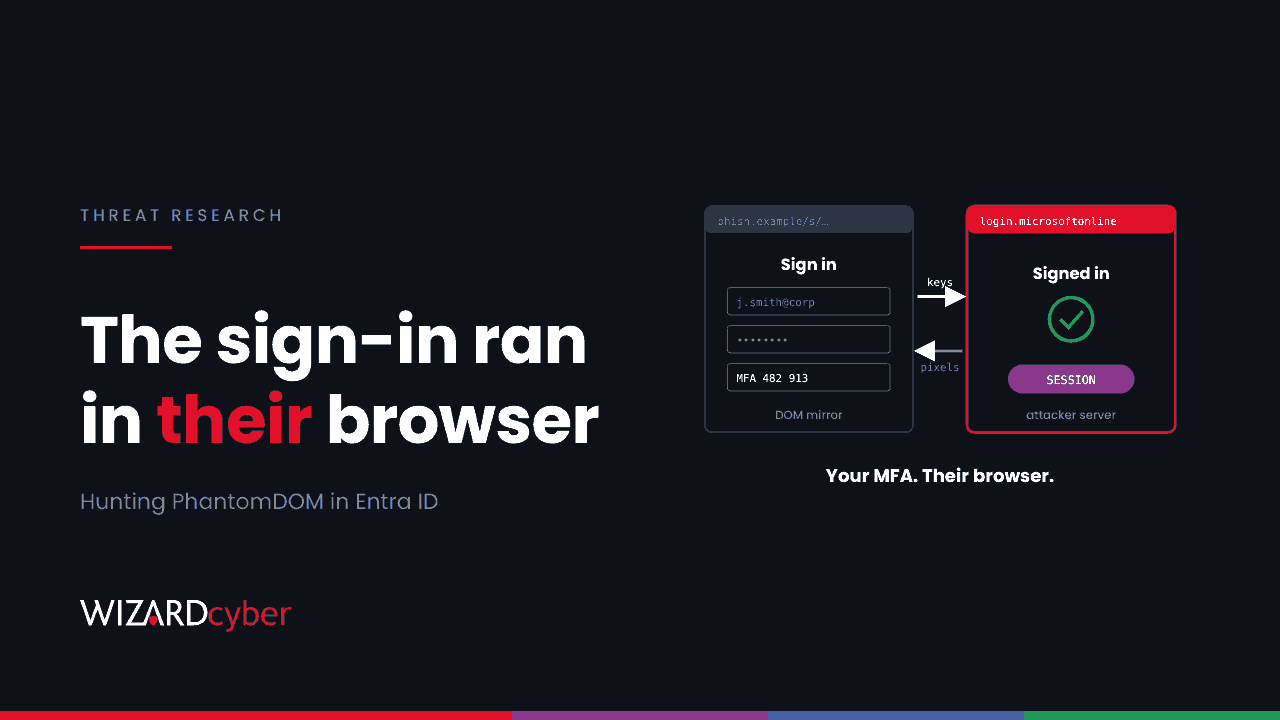
The Sign-In Happened In Their Browser: Hunting PhantomDOM Browser-In-The-Middle Phishing In Entra ID
PhantomDOM signs in to Microsoft 365 inside the attacker's browser, so MFA passes there. How to hunt it by Entra session, passkey requests and mail access.
 Threat Research
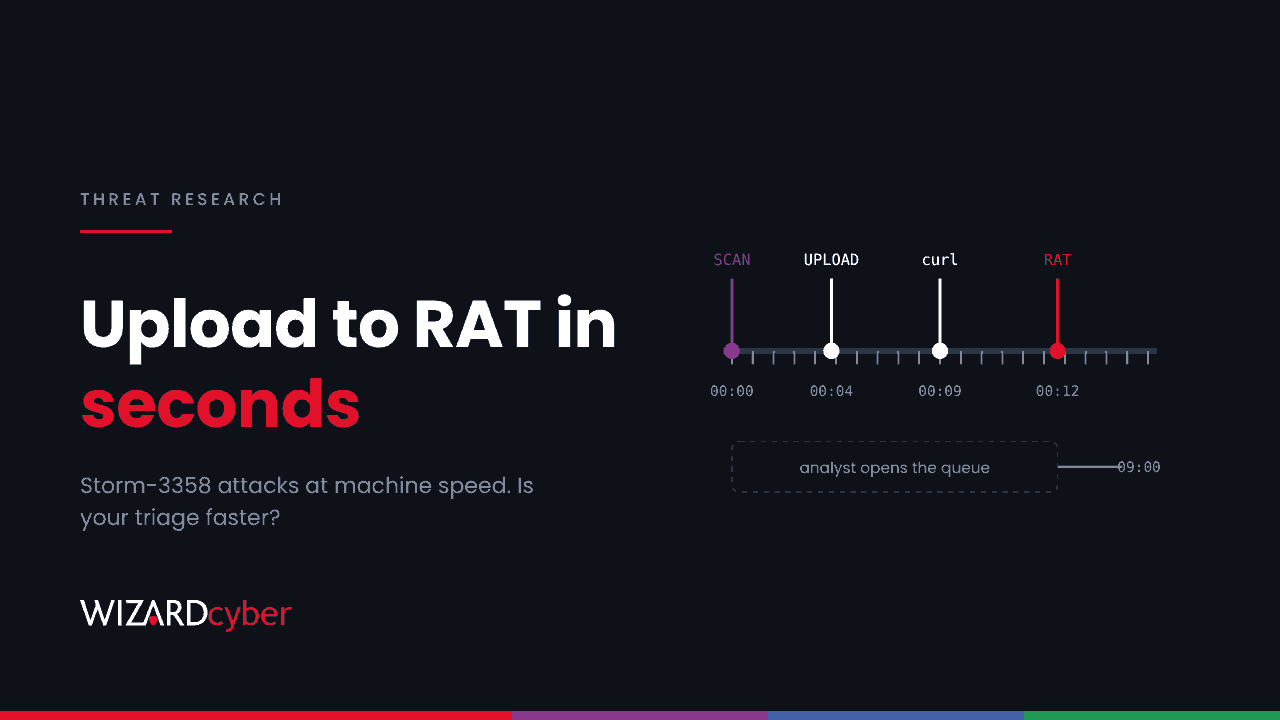
An Upload Field, Then A RAT In Seconds: Hunting Storm-3358's Machine-Speed Intrusions Against Financial Services
Storm-3358 uses AI agents to exploit upload and SSRF flaws, then pulls RATs with curl. Hunts for Sentinel and Defender, plus Microsoft's IOCs.
 Threat Research
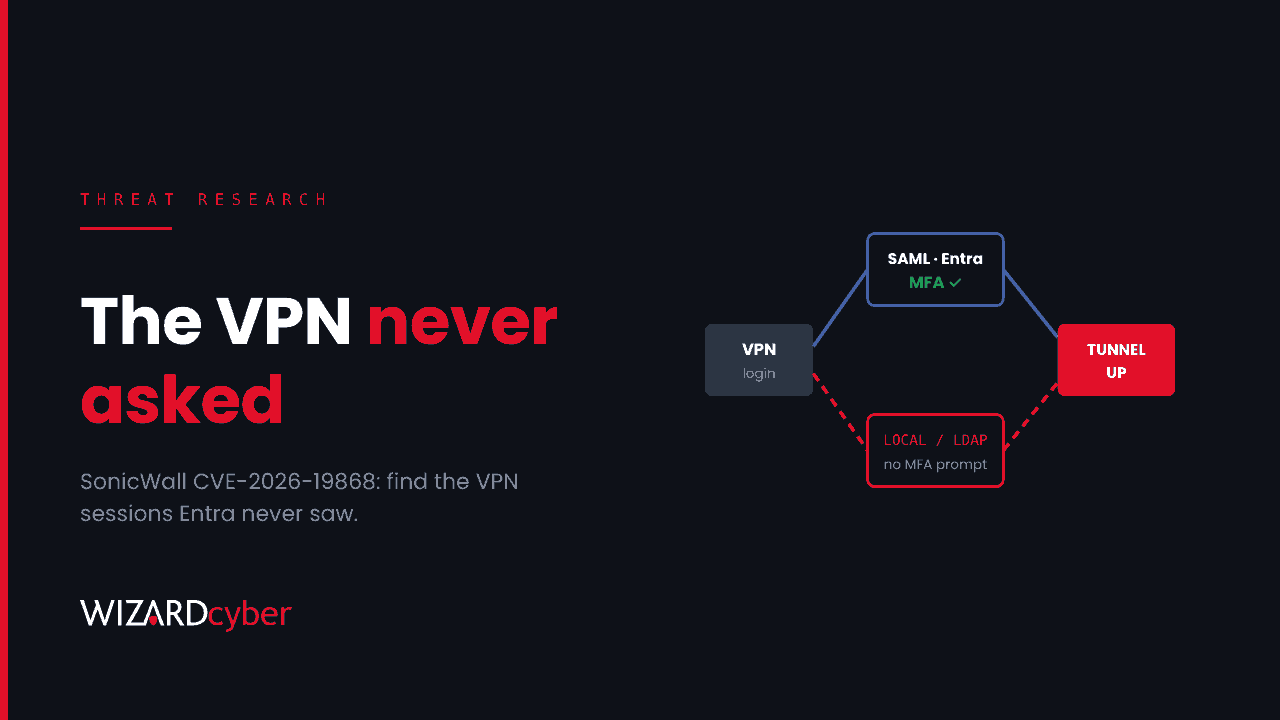
MFA Said Yes, The VPN Never Asked: Hunting Downstream Of The SonicWall SAML Bypass (CVE-2026-19868) In Entra And Active Directory
SonicWall's SSL VPN flaw let valid alternate credentials skip SAML and MFA. Find VPN sessions Entra never saw, then trace them into AD.
 Threat Research
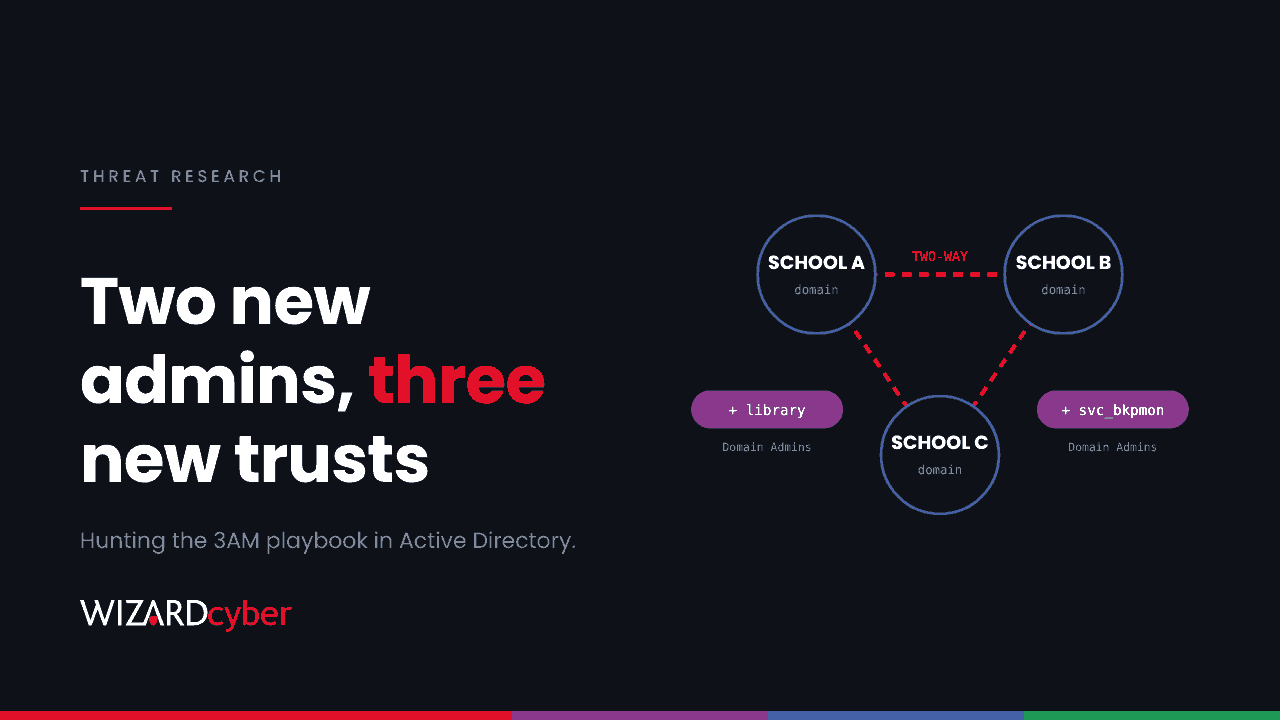
Two New Domain Admins And Three New Trusts: Hunting The 3AM Ransomware Playbook In Active Directory
3AM ransomware hit a UK school estate after nine nights of backup credential theft, new domain admins and new trusts. How to hunt each step in Defender.
 Threat Research
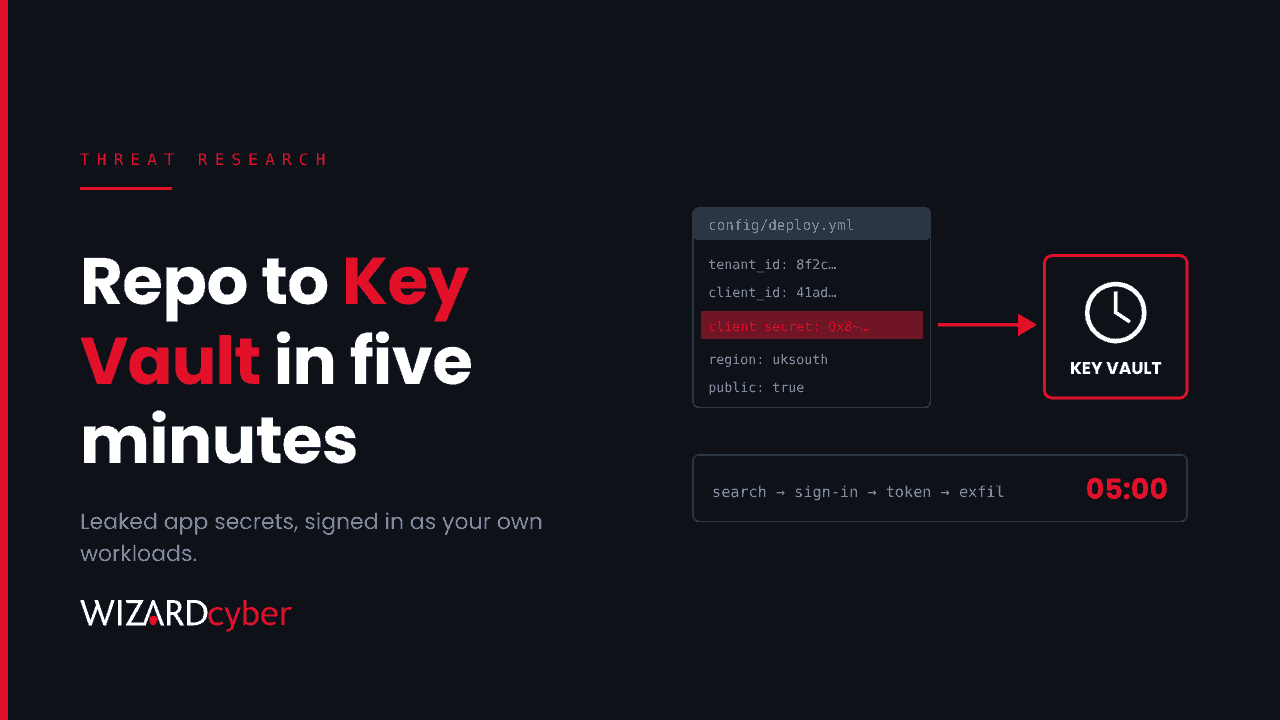
From A Public Repo To Key Vault In Five Minutes: Hunting The Agentic Secret-Harvesting Campaign In Entra ID And Azure
An AI-driven operator used leaked app secrets to sign in as victims' own workloads and raid Key Vault. What happened, and Defender and Sentinel hunts.
 Threat Research
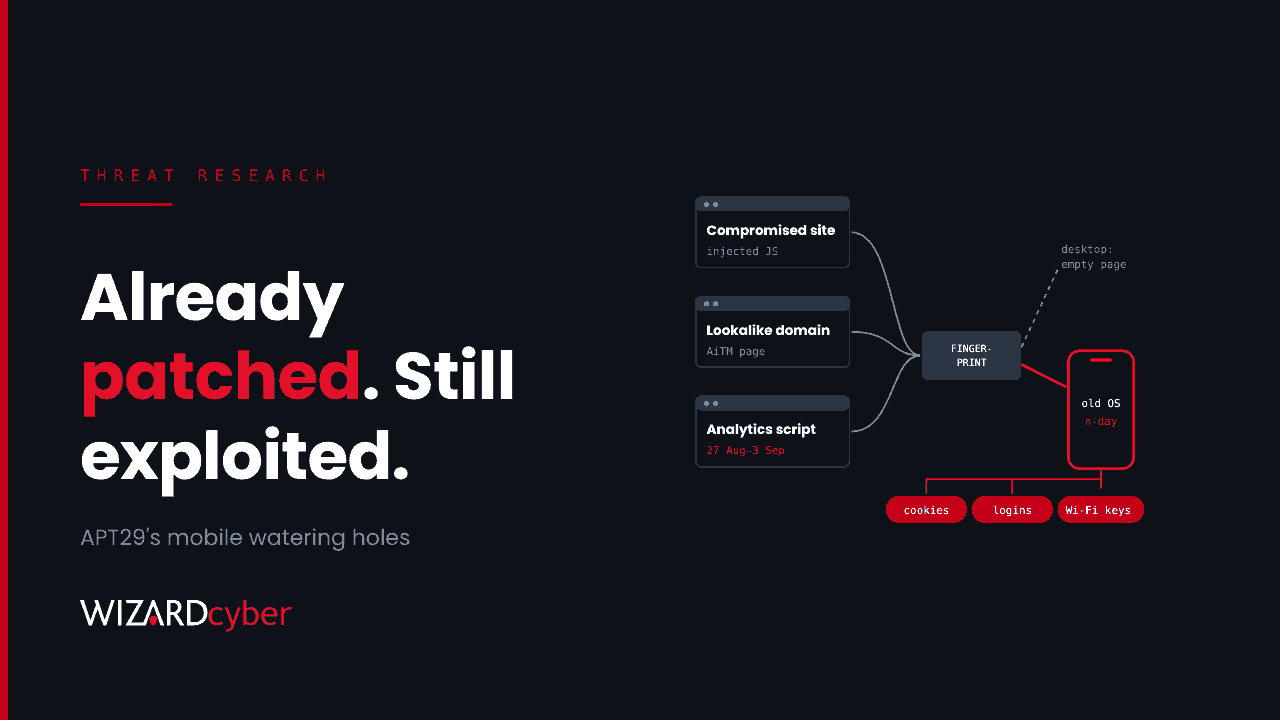
Patched Exploits, Poisoned Sites: Hunting APT29's Mobile Watering Holes From Defender And Intune
APT29 used poisoned websites and already-patched exploits to steal cookies from phones. How it worked, hunting queries, and the Intune fixes.
 Threat Research
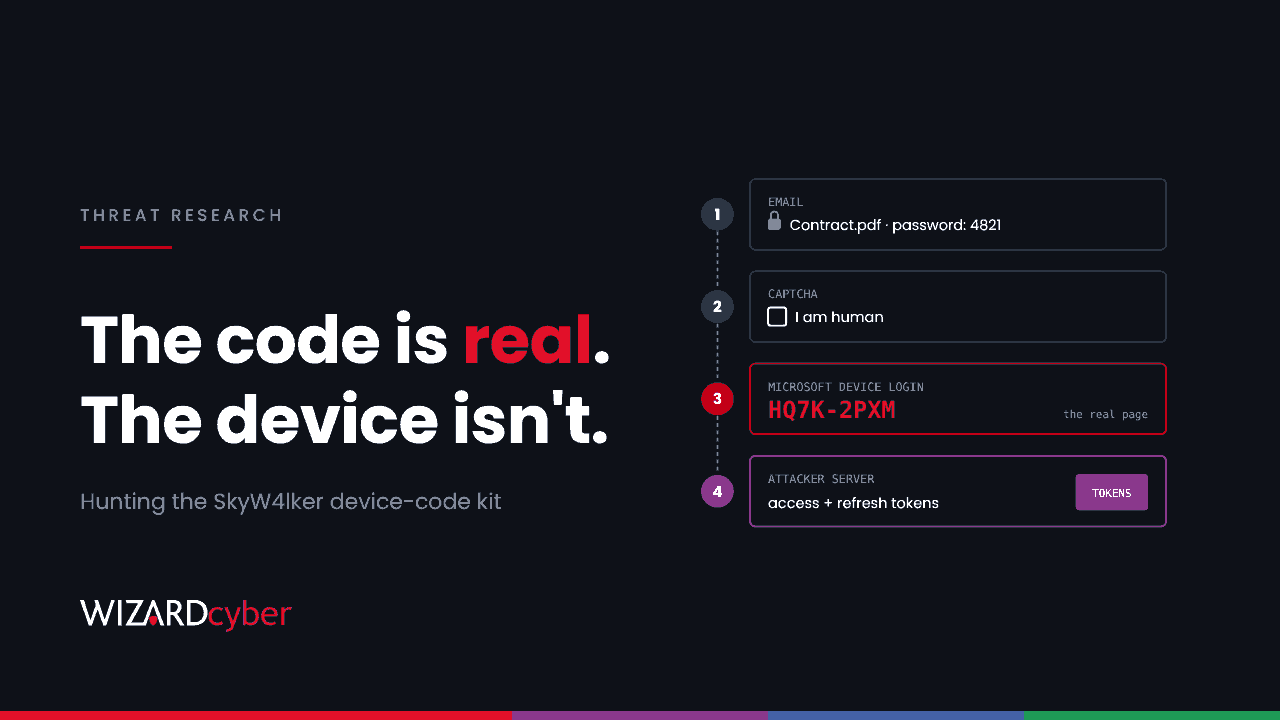
Password In The Email, Code On Microsoft's Page: Hunting The SkyW4lker Device-Code Kit In Microsoft 365
SkyW4lker gets users to enter an attacker's code on Microsoft's real login page. How the kit works, Defender and Sentinel hunts, and how to block it.
 Threat Research
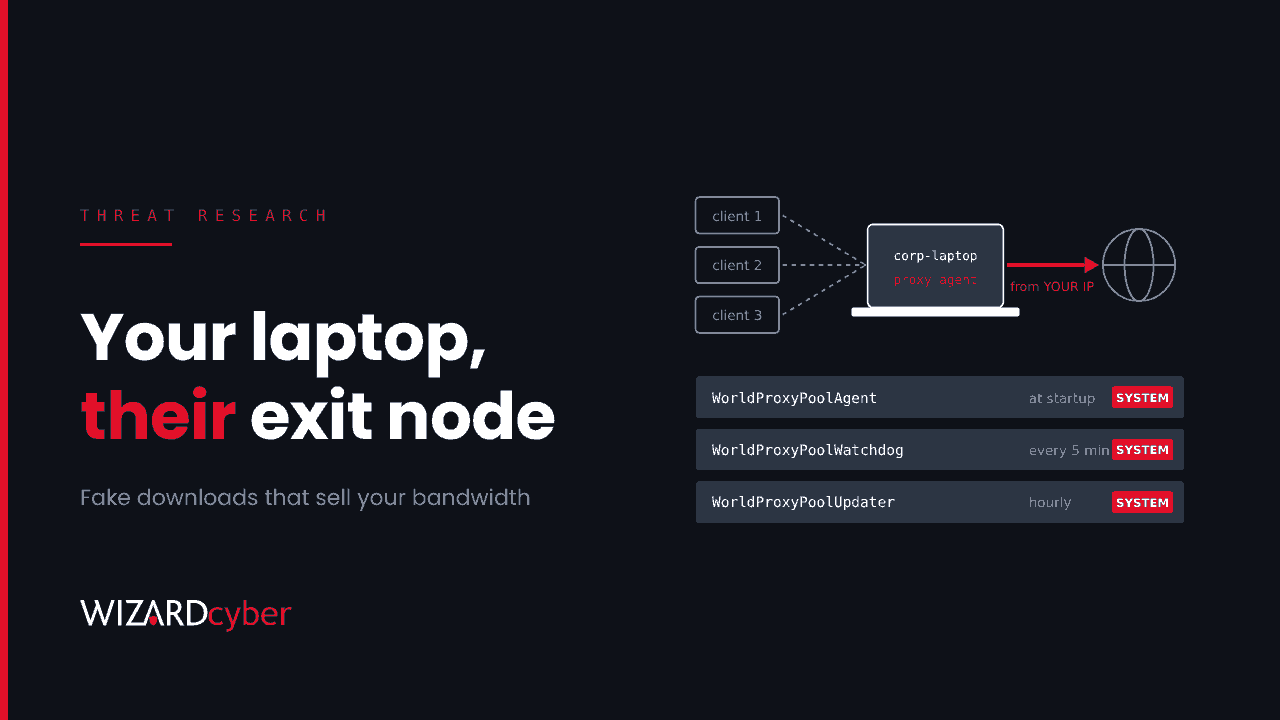
Your Laptop, Someone Else's Exit Node: Hunting Trojanised Inno Setup Installers And Proxyware In Defender
Fake downloads install proxyware and compute agents with SYSTEM scheduled tasks. How the chain works, and Defender hunts for every stage.
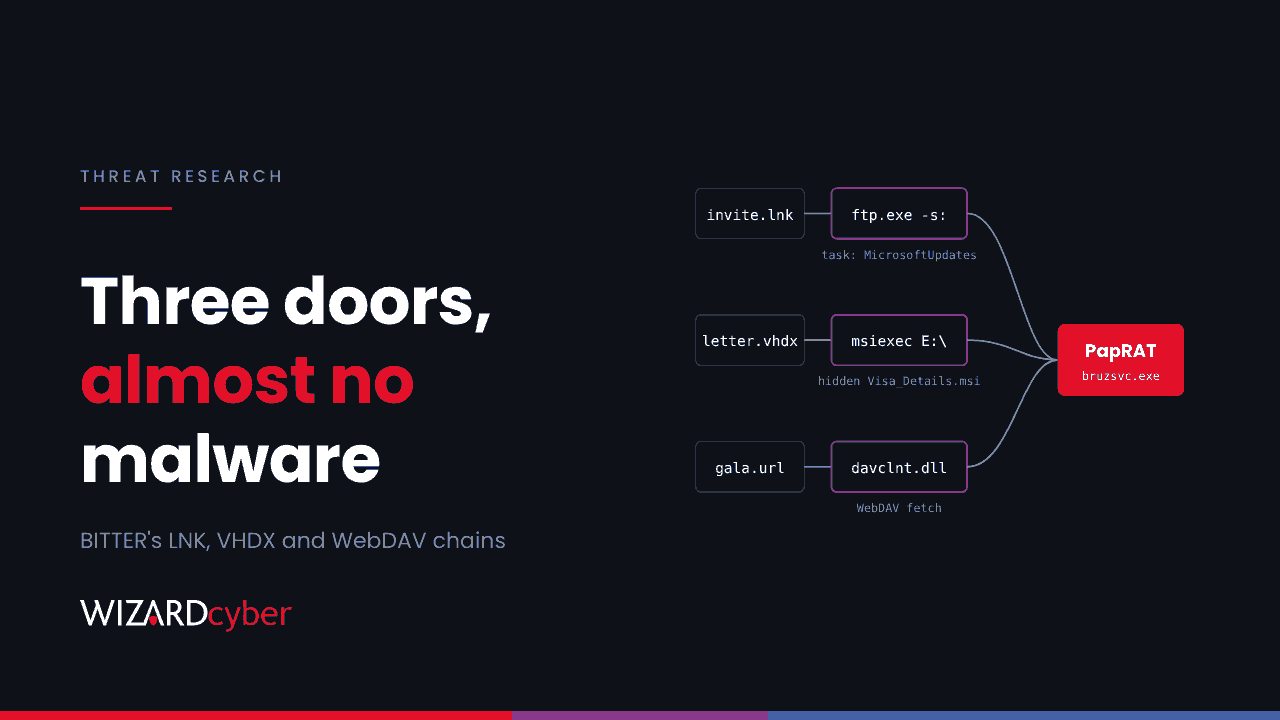 Threat Research
A Shortcut That Runs ftp.exe: Hunting BITTER's PapRAT Chains (LNK, VHDX And WebDAV) In Defender
BITTER delivers PapRAT through ftp.exe shortcuts, VHDX disk images and WebDAV links. How each chain works, and Defender hunts for every step.
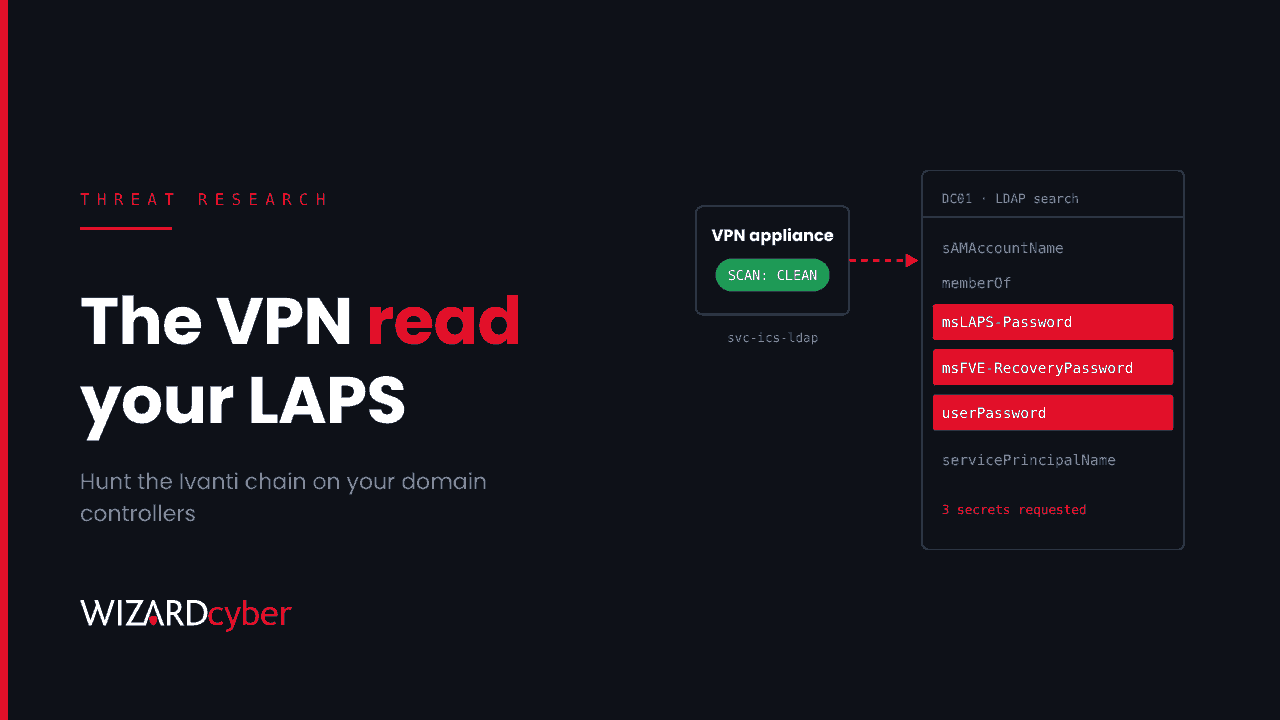 Threat Research
Your VPN Read Your LAPS Passwords: Hunting The Ivanti Connect Secure Chain From Active Directory
The Ivanti zero-day chain left no implant, so a clean appliance scan proves little. Hunt the LAPS, BitLocker and Kerberos activity on your DCs instead.
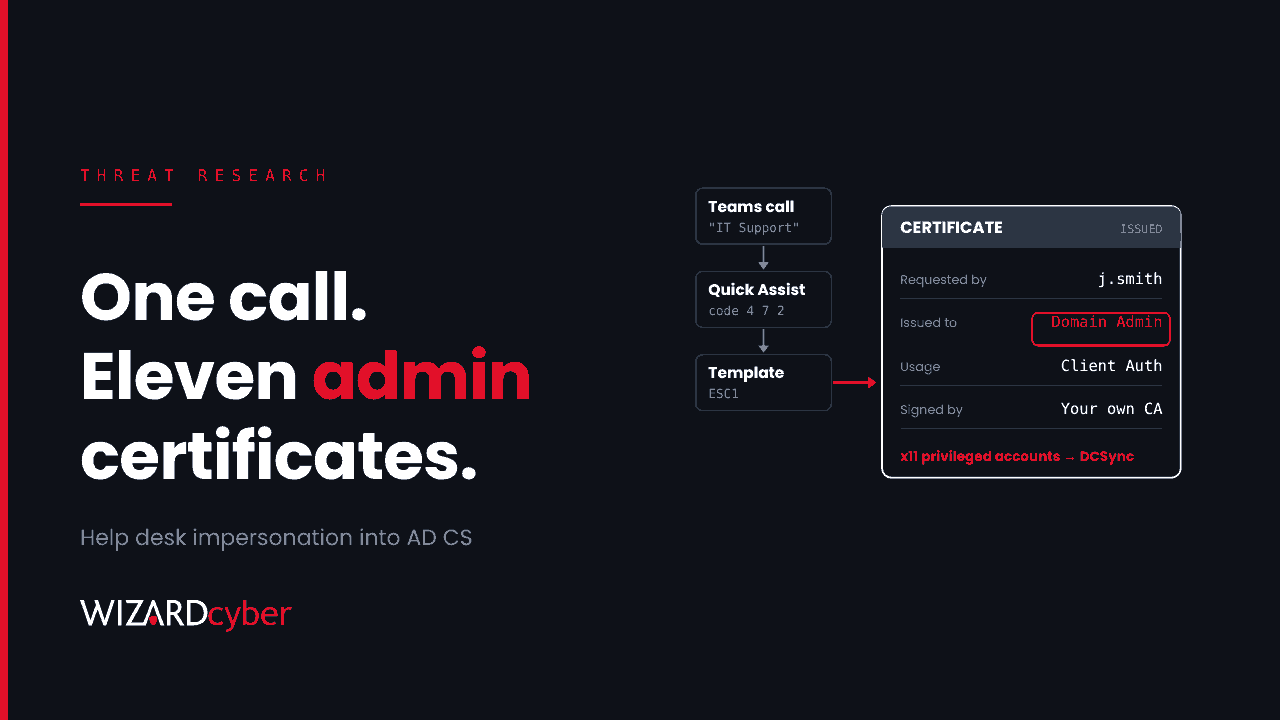 Threat Research
From A Teams Call To A Domain Controller Certificate: Hunting Help Desk Impersonation Into AD CS (ESC1 And ESC8)
A fake help desk call, a Quick Assist code, then certificates for domain admins. How the ESC1 and ESC8 intrusions worked, and Defender hunts for each step.
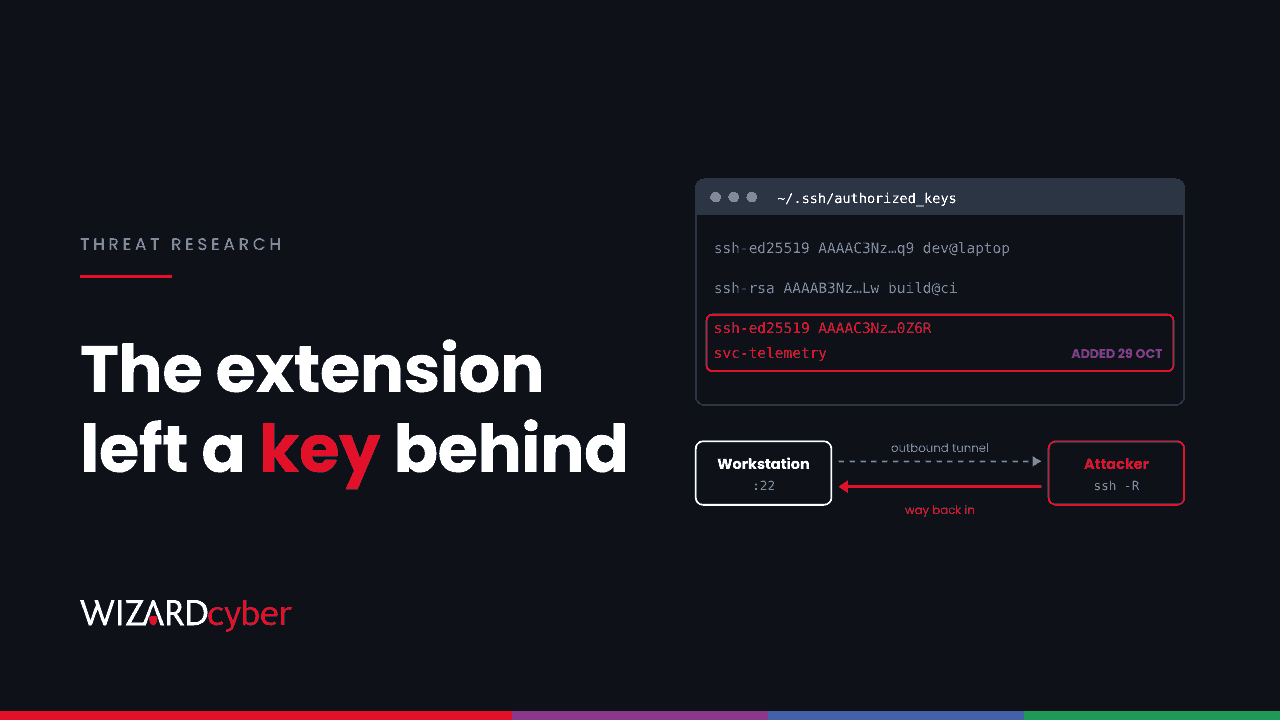 Threat Research
A Fake AI Coding Extension Planted An SSH Key: Hunting The svc-telemetry Backdoor On Windows, macOS And Linux
A trojanised AI coding extension added an attacker's SSH key, a reverse tunnel and a fake SysMon task. Removing it isn't enough. What to hunt and remove.
 Threat Research
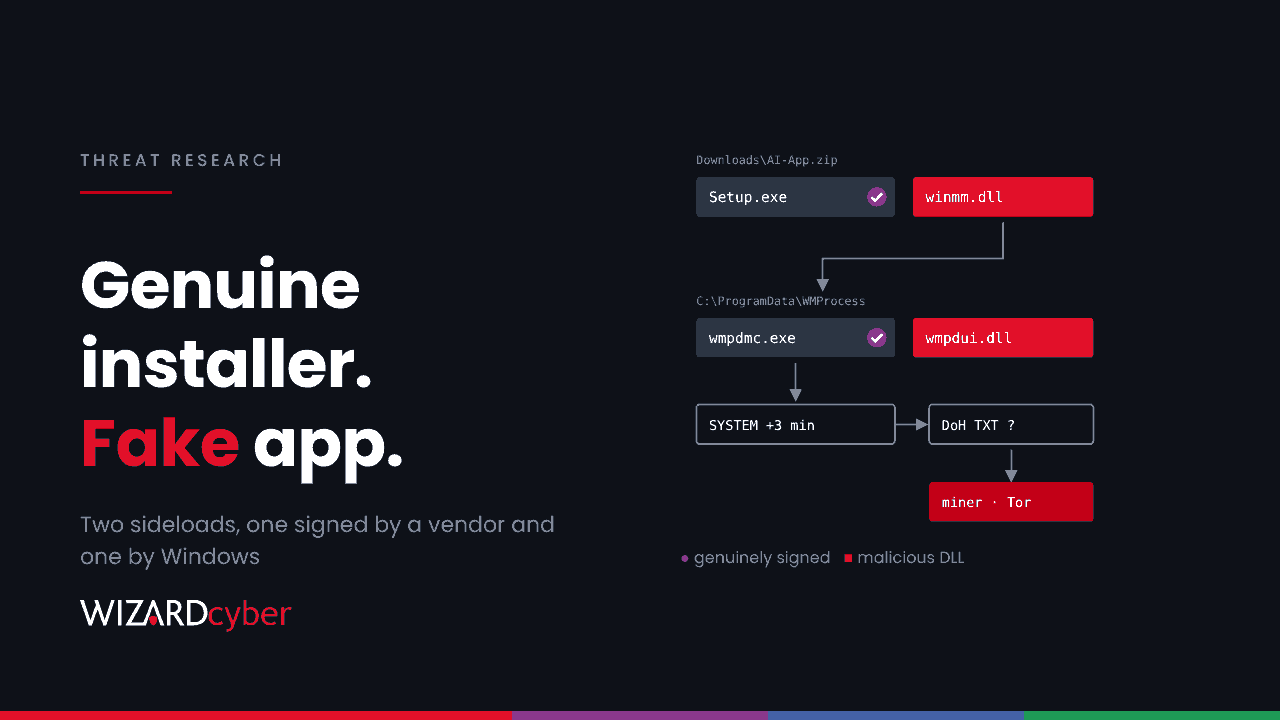
The Installer Is Genuine, The AI App Isn't: Hunting The Yoba Sideloading Chain On Windows
Fake AI desktop apps on GitHub pair a genuine signed installer with a malicious DLL. How the Yoba chain works, and Defender hunts for each step.
 Threat Research
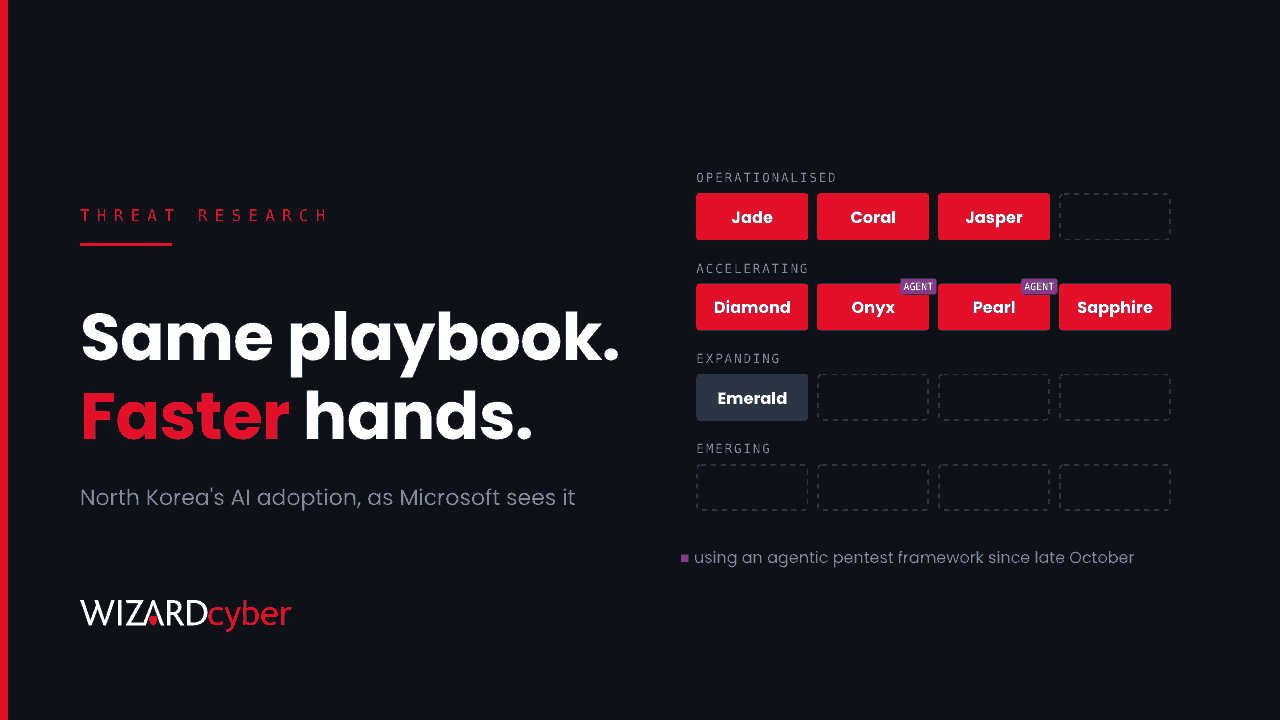
Same Playbook, Faster Hands: Hunting North Korea's AI-Assisted Intrusions In Defender And Entra
Microsoft says North Korean groups now use AI to speed up lures, fake personas and malware. What changed, and Defender and Entra hunts to run.
 Threat Research
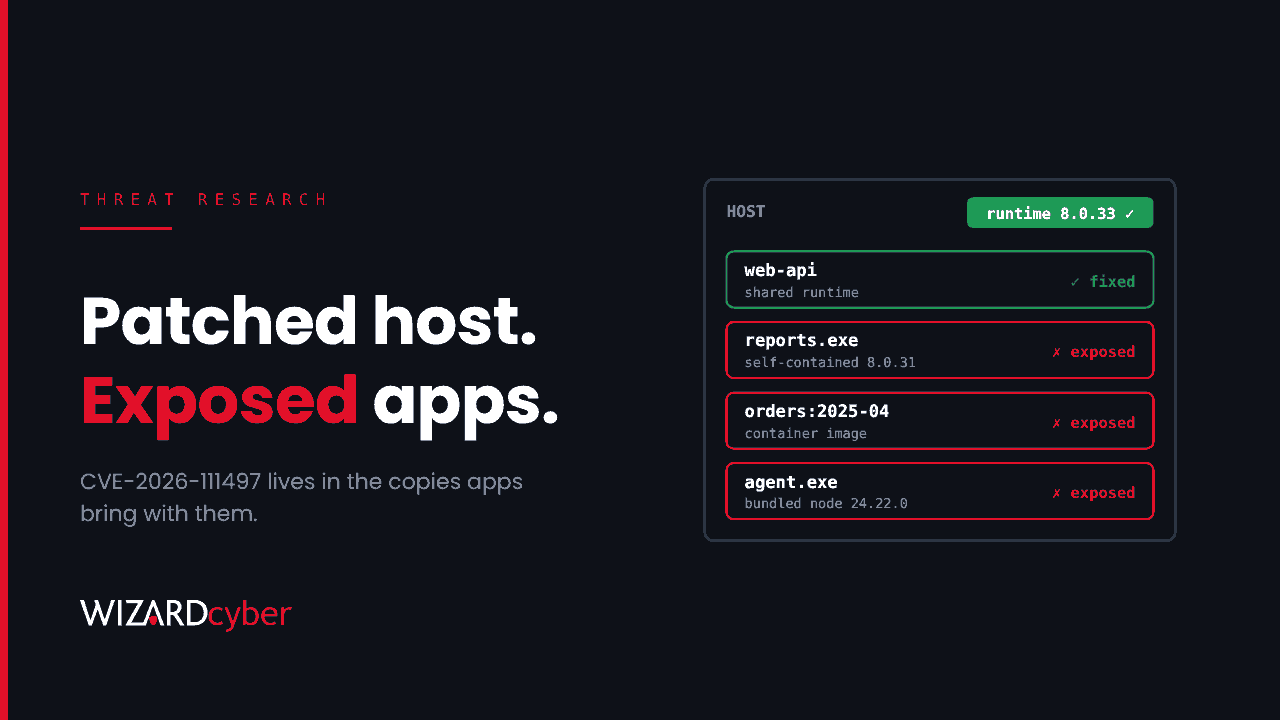
Opt-In, Still Exposed: Finding The Brotli Flaw (CVE-2026-111497) Across Your .NET And Node.js Estate
Microsoft shipped emergency .NET fixes for the Brotli flaw. Self-contained apps, containers and bundled copies need more. How to find them with Defender KQL.
 Threat Research
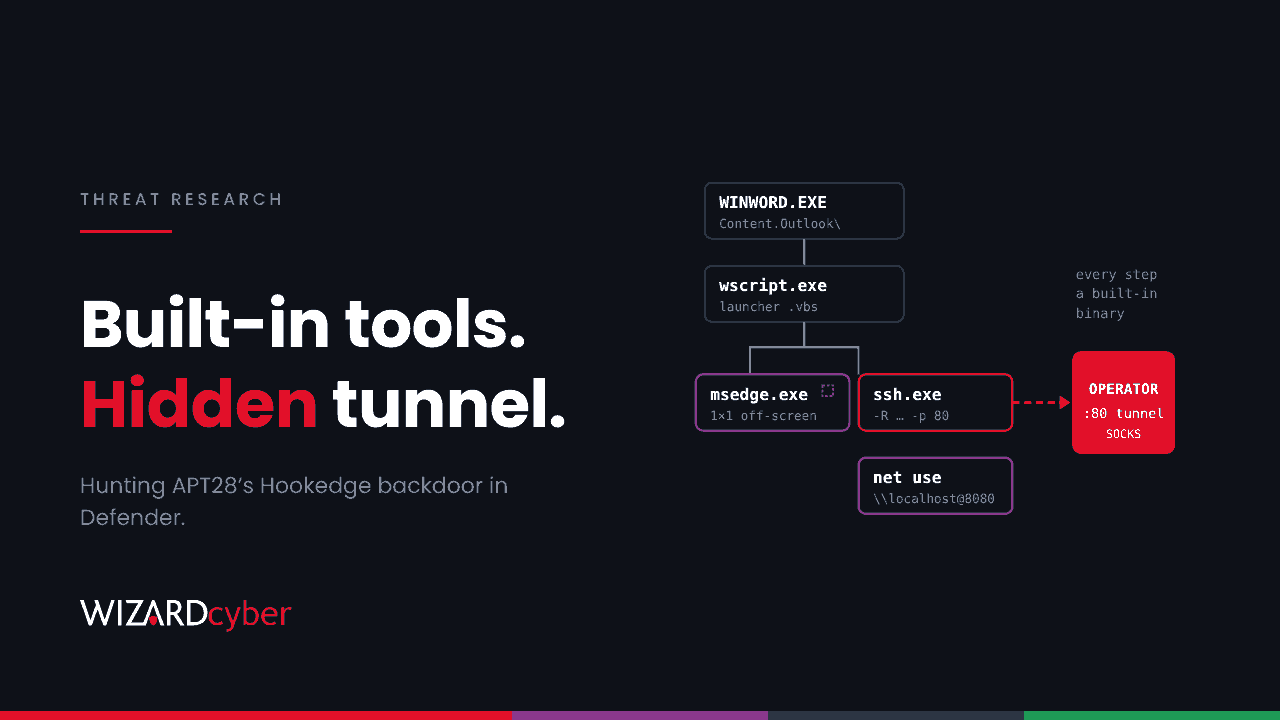
A Hidden Edge Window And An SSH Tunnel: Hunting APT28's Hookedge Backdoor In Defender
APT28 ran a backdoor through an off-screen Edge window, stole NTLM hashes and tunnelled out over Windows' own SSH client. How to hunt each step in Defender.
 Threat Research
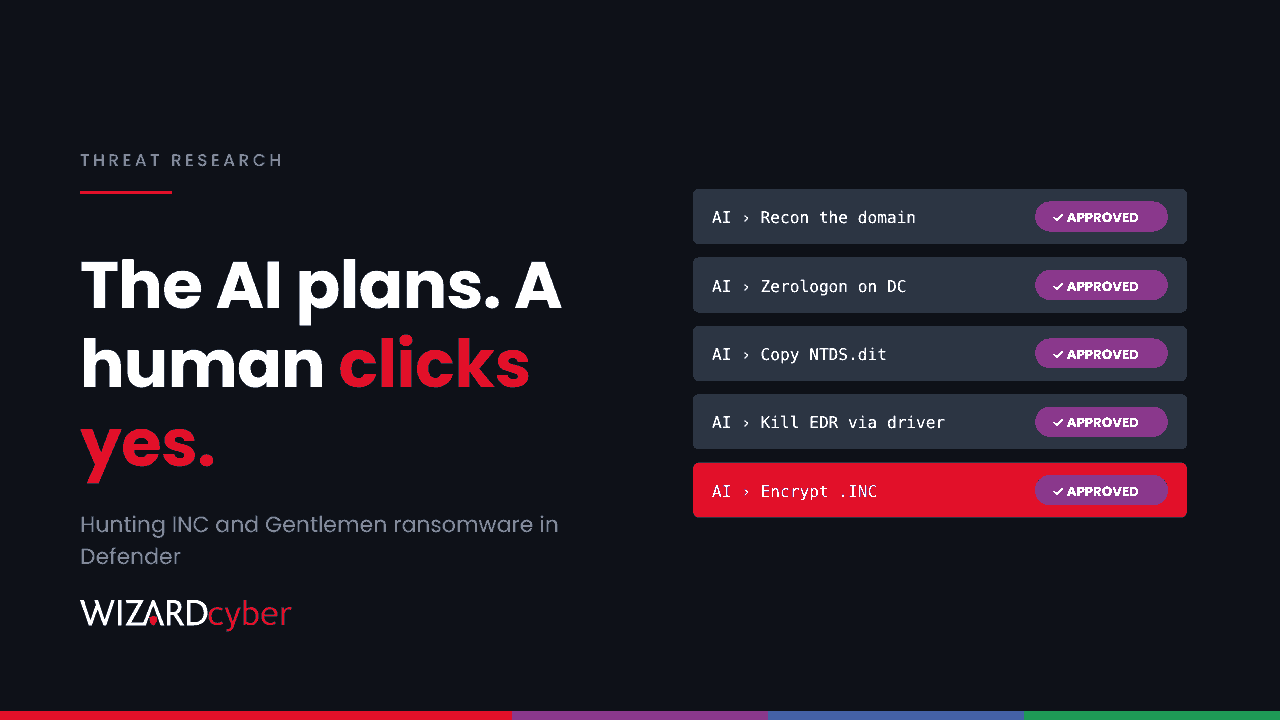
Every Step Approved By A Human: Hunting The AI-Assisted INC And Gentlemen Ransomware Intrusions In Defender
An exposed server showed INC and Gentlemen affiliates using AI agents against 62 organisations. What they did, and Defender hunts for each step.
 Threat Research
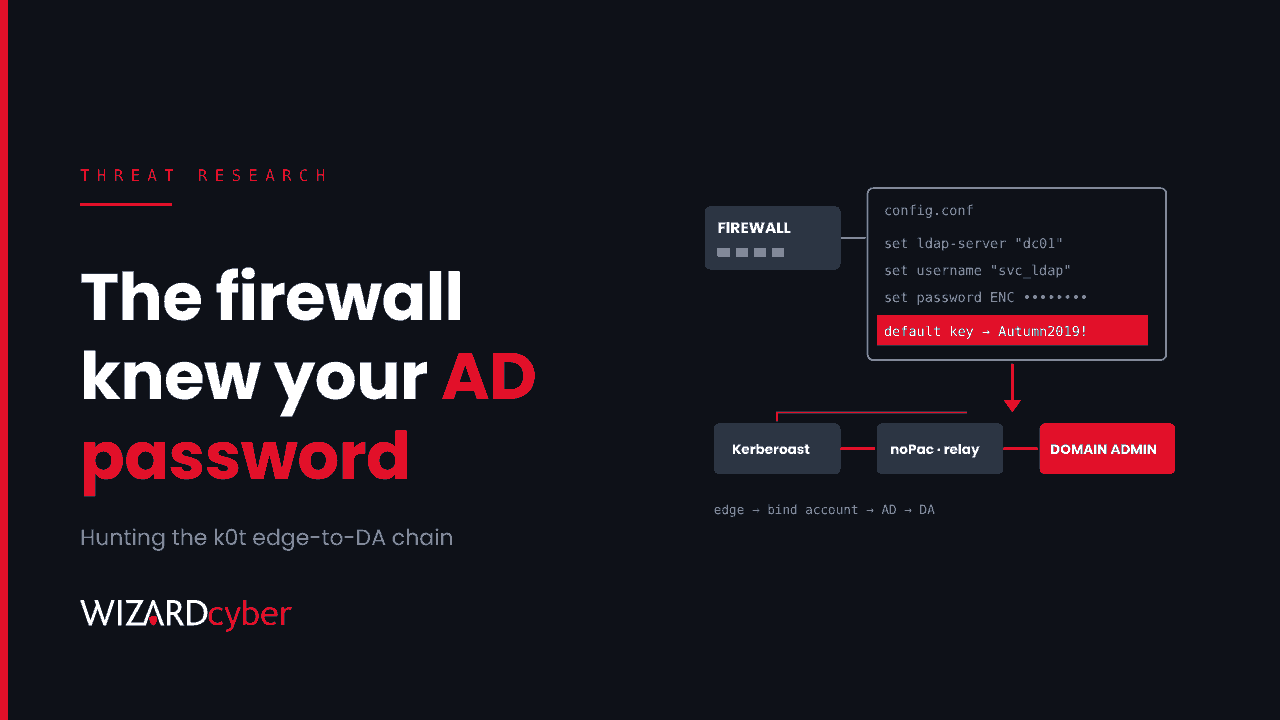
Your Firewall Config Knows Your AD Password: Hunting The k0t Edge-To-Domain-Admin Chain
k0t decrypted stolen firewall configs to get AD bind credentials, then went for Domain Admin. How the chain works and how to hunt it in Defender.
 Threat Research
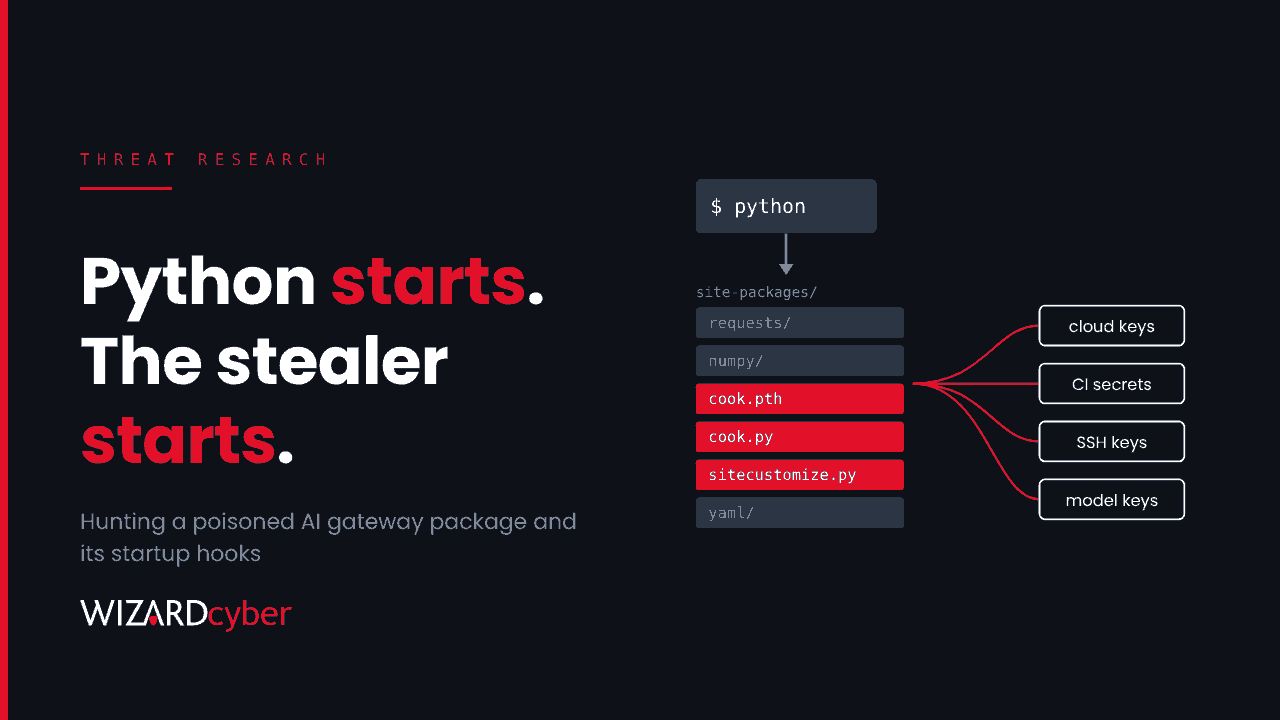
Starting Python Was Enough: Hunting The Poisoned AI Gateway Package And Its Startup Hooks
A hijacked AI gateway release ran a credential stealer every time Python started. How it worked, and how to hunt and contain it with Defender KQL.
 Threat Research
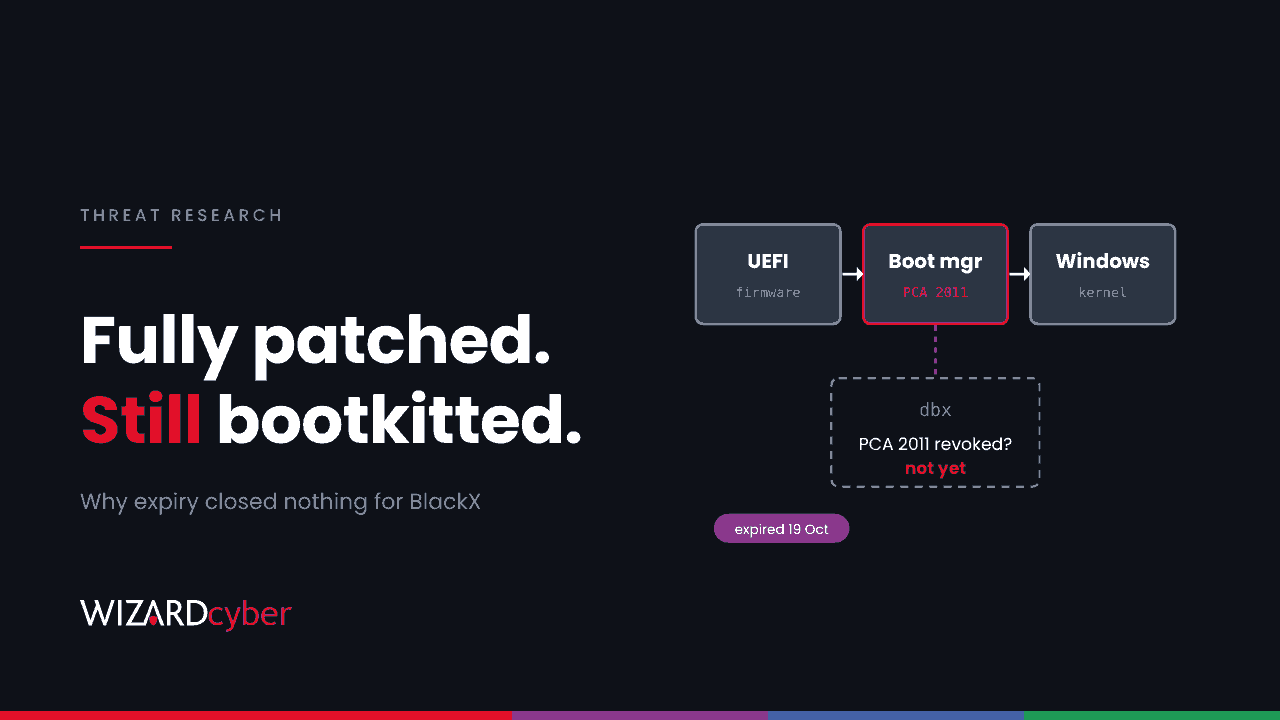
Fully Patched, Still Bootkitted: BlackX And The Secure Boot Revocation Most Estates Skipped
BlackX loaded on fully patched Windows PCs because the Secure Boot revocation is a manual step. How to check your estate, hunt and apply it safely.
 Threat Research
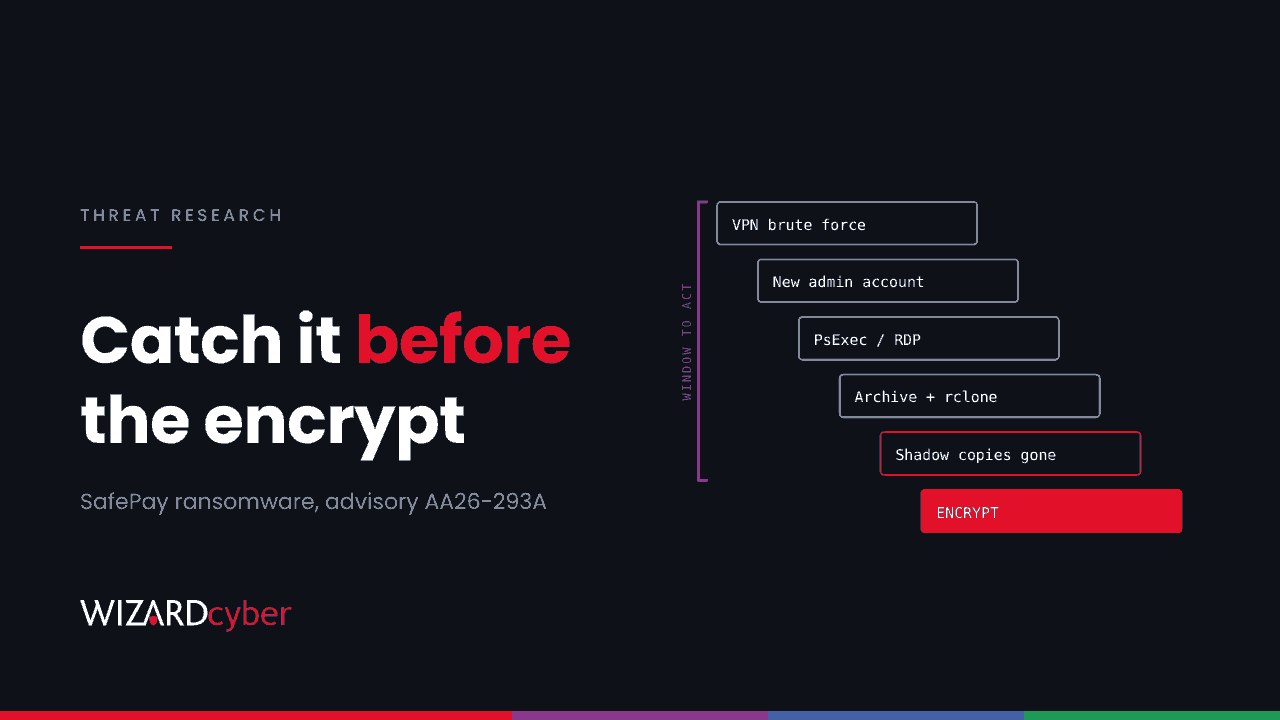
No Affiliates, Just Your VPN: Hunting SafePay Ransomware (AA26-293A) In Microsoft Defender
A joint US, German and UK advisory says SafePay has hit 600+ organisations. Map its path from VPN to encryption, with Defender hunts for each step.
 Threat Research
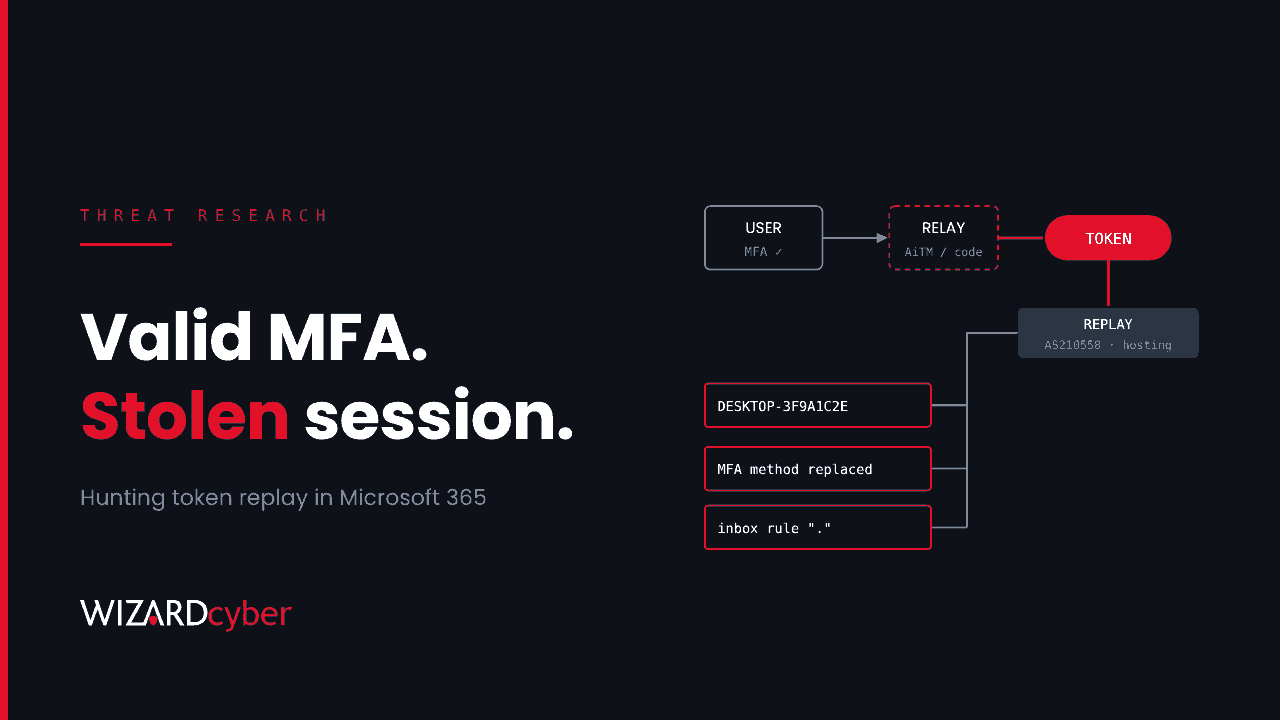
Valid Password, Stolen Session: Hunting The Microsoft 365 Token Spray-And-Replay Campaign
An attacker replayed post-MFA tokens into 79 organisations. How it worked, what it left behind, and KQL to hunt for it in Sentinel and Defender.
 Threat Research
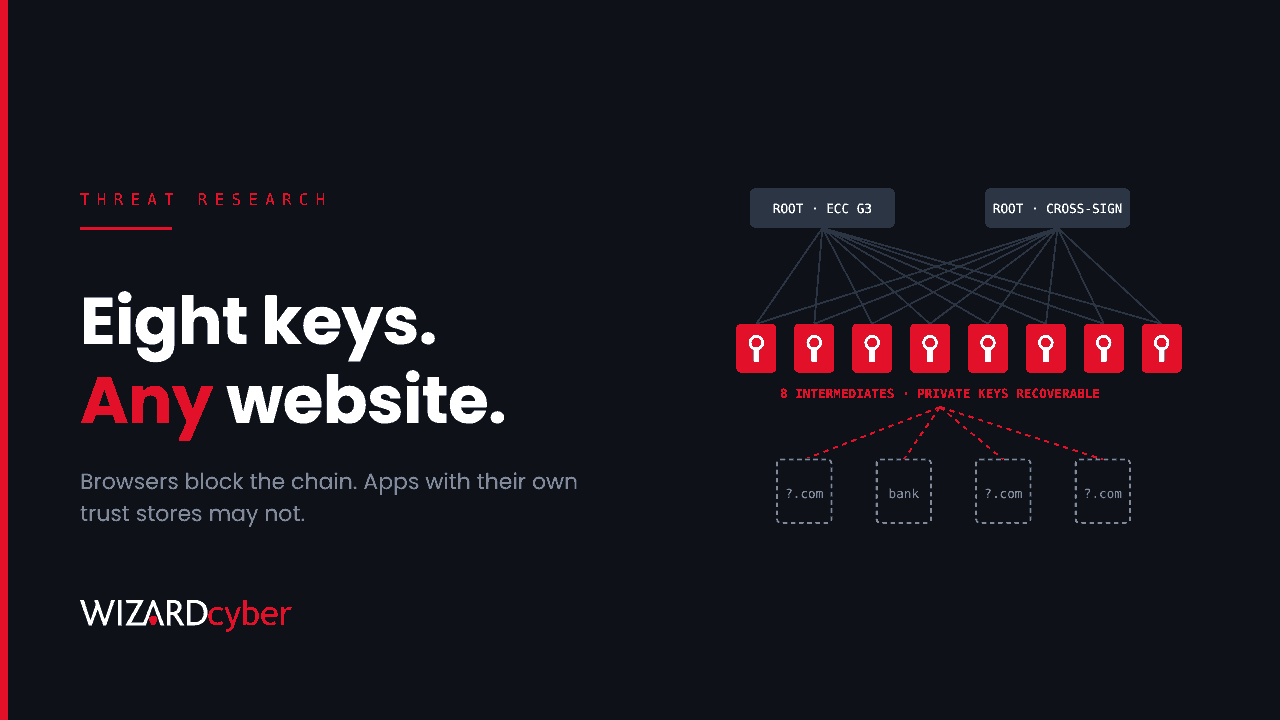
Eight Stolen CA Keys: Checking Your Estate After The Intermediate Certificate Compromise
Browsers and Windows now block eight compromised intermediate CAs. Apps with their own trust stores may not. How to find them with Defender KQL.
 Threat Research
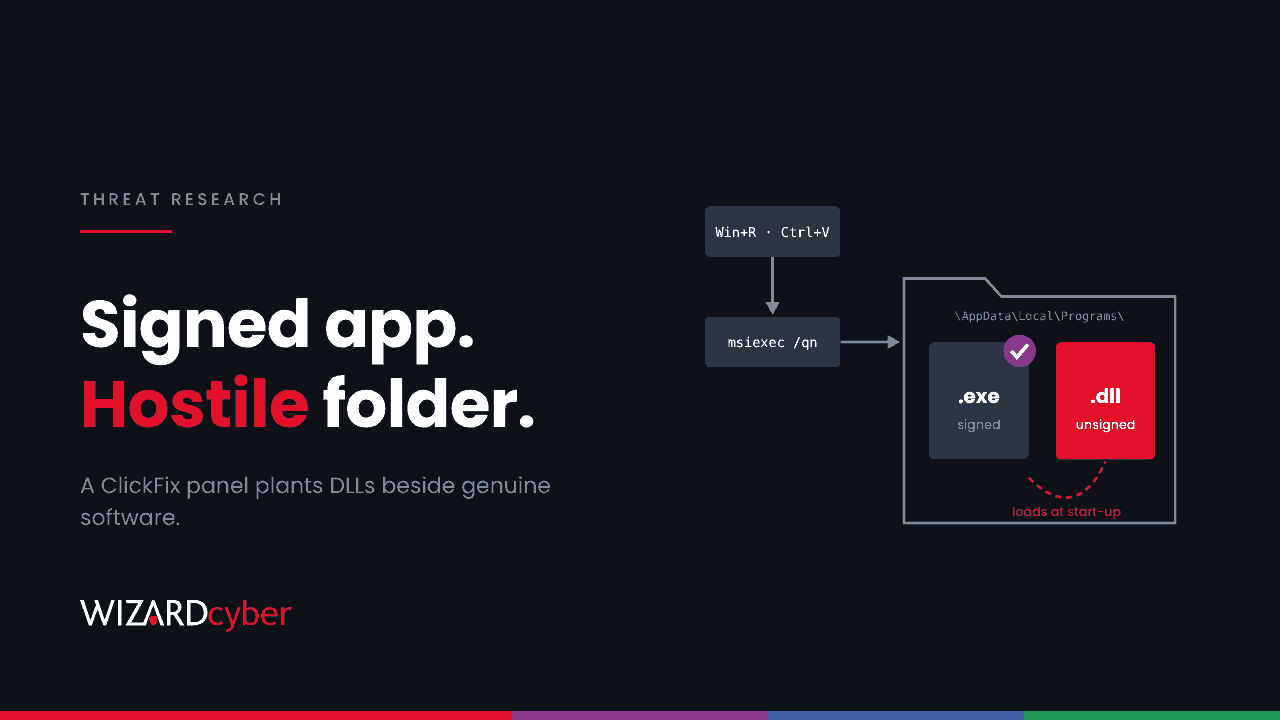
A Genuine Signed Installer, A Hostile Folder: Hunting The ROMULUS ClickFix Panel And CVE-2026-110936
A ClickFix delivery panel is planting malicious DLLs beside genuine signed software. How the chain works and how to hunt it with Defender KQL.
 Threat Research
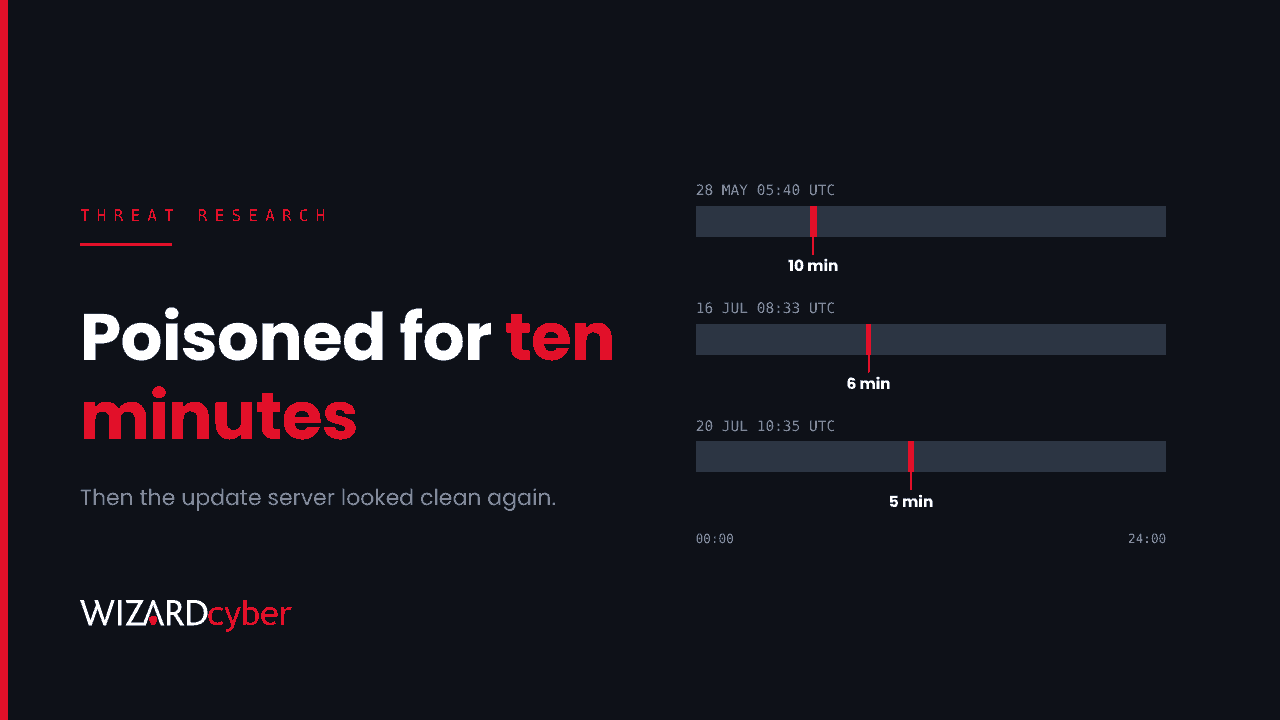
Ten Minutes On The Update Server: Hunting A Hijacked Software Updater On Windows Endpoints
An attacker hijacked a Windows tool's updates for minutes at a time, then cleaned up. How to hunt the backdoor it left on endpoints with Defender KQL.
 Threat Research
Accept, Then Sign In: Hunting The Calendar-Invite Phishing Surge In Microsoft 365
Fake meeting invites hit 740,000+ in two weeks of October, aimed at Microsoft 365 logins. Why they get through, and how to hunt them in Defender.
 Threat Research
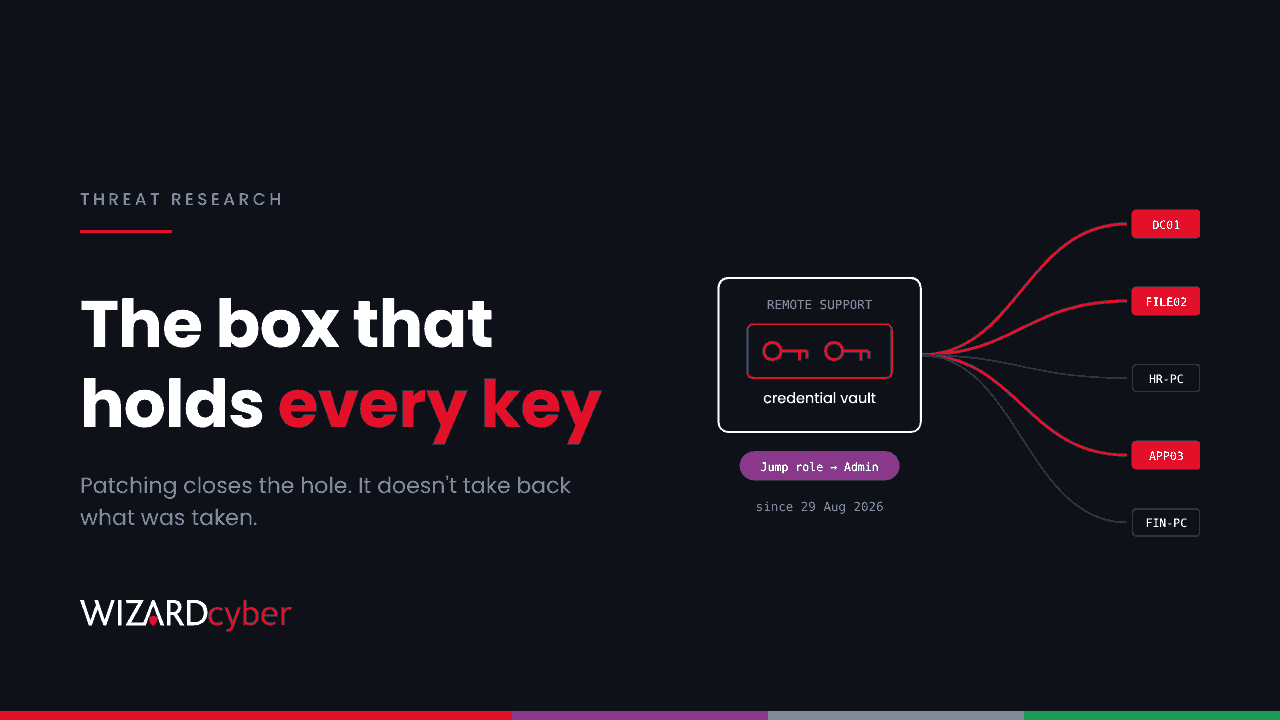
The Box That Holds Every Key: Hunting Downstream From A Compromised Remote Support Appliance
A remote support zero-day was exploited from August. Patching won't undo it. What to rotate, in what order, and how to hunt downstream in Defender.
 Threat Research
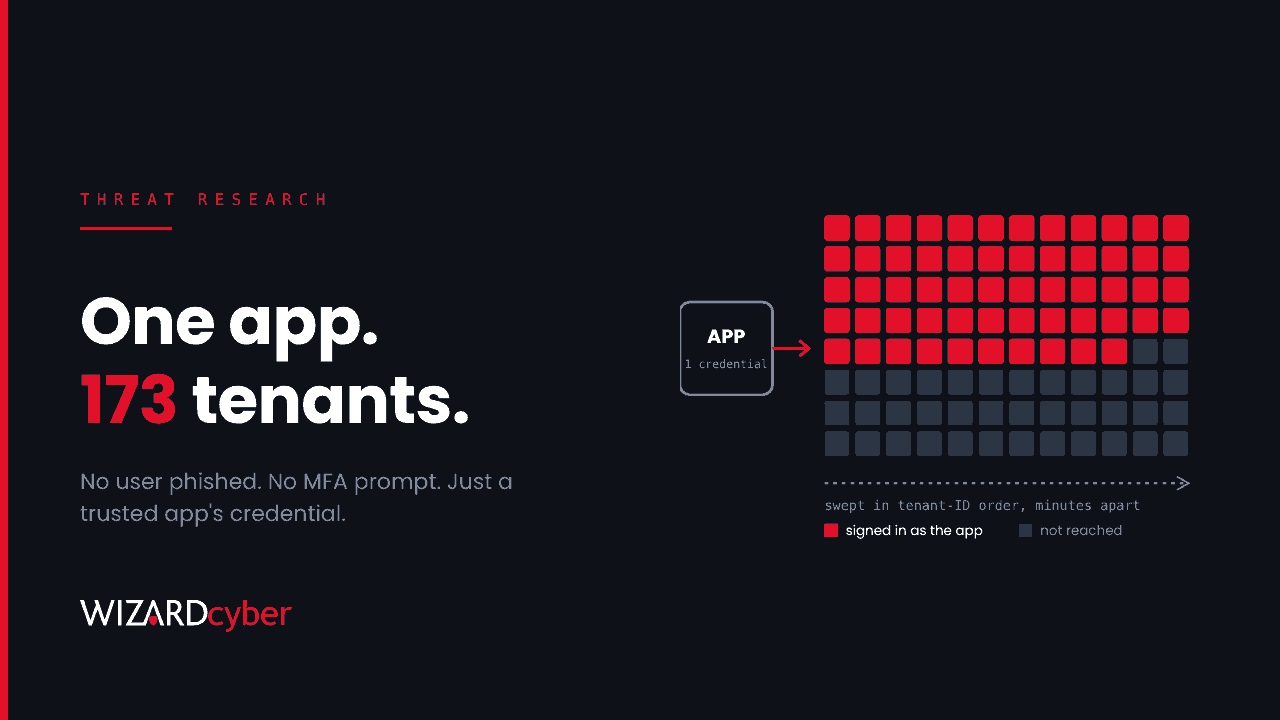
One Trusted App, 173 Tenants: Hunting A Compromised Third-Party App In Entra ID
A backup app's identity was used to sign in to 173 Microsoft 365 tenants. Why session revocation won't help, and how to hunt it in Entra and Sentinel.
 Threat Research
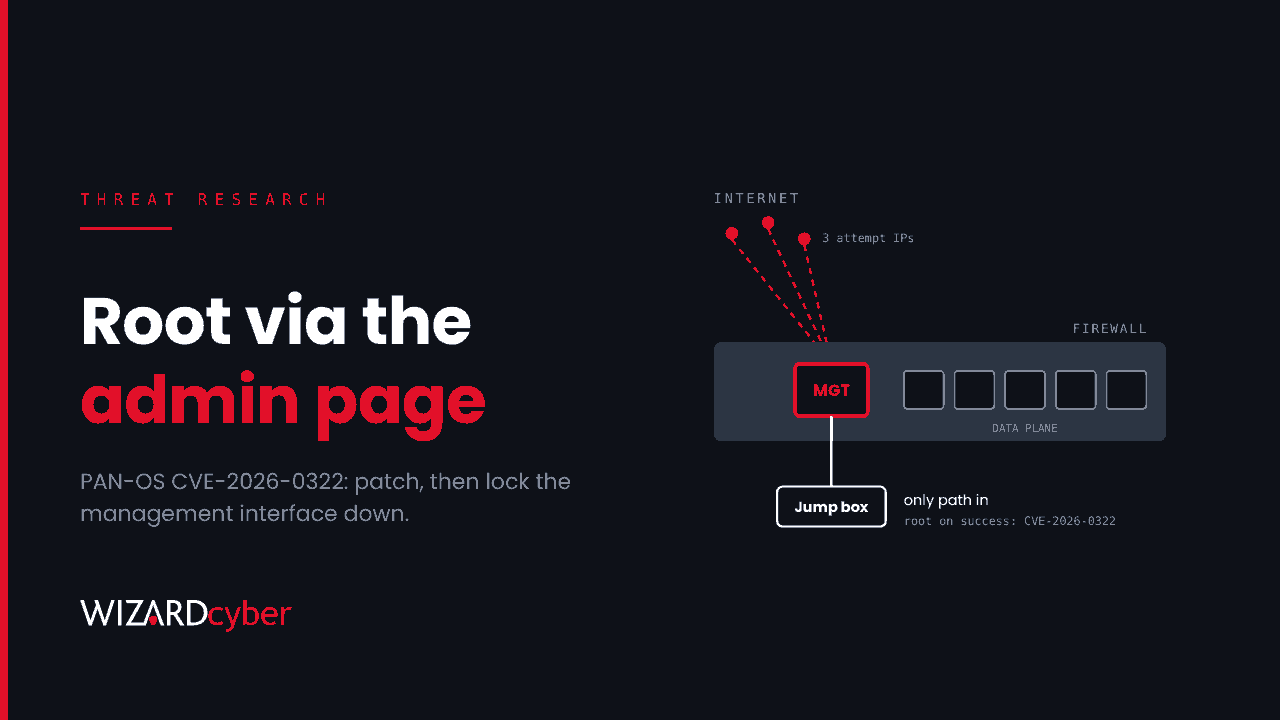
The Firewall's Admin Page Is The Target: Hunting PAN-OS CVE-2026-0322
A PAN-OS zero-day gives root via the management interface to anyone with an admin login. Fixed versions, what to rotate and KQL to hunt it.
 Threat Research
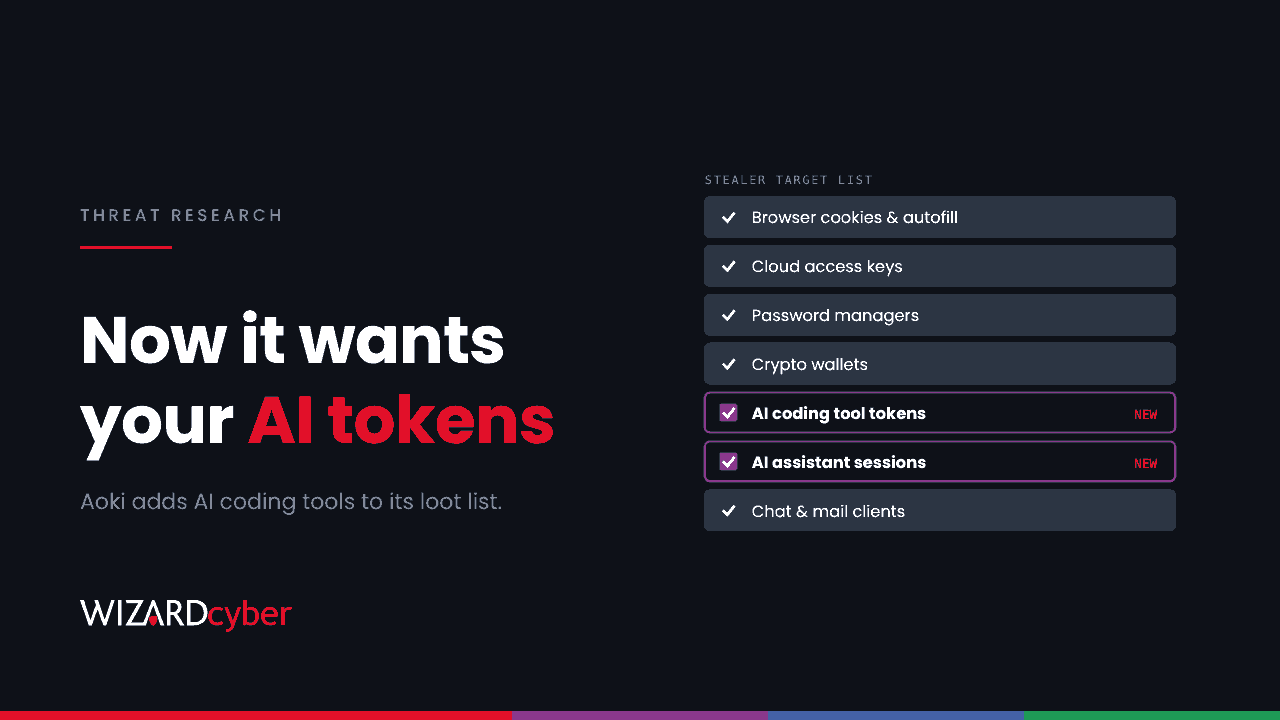
Infostealers Have Found Your Developers' AI Tools: Hunting Aoki On Windows Endpoints
A new Aoki build steals AI coding tool tokens alongside cookies and cloud keys. What it takes, how to hunt it in Defender and what to rotate.
 Threat Research
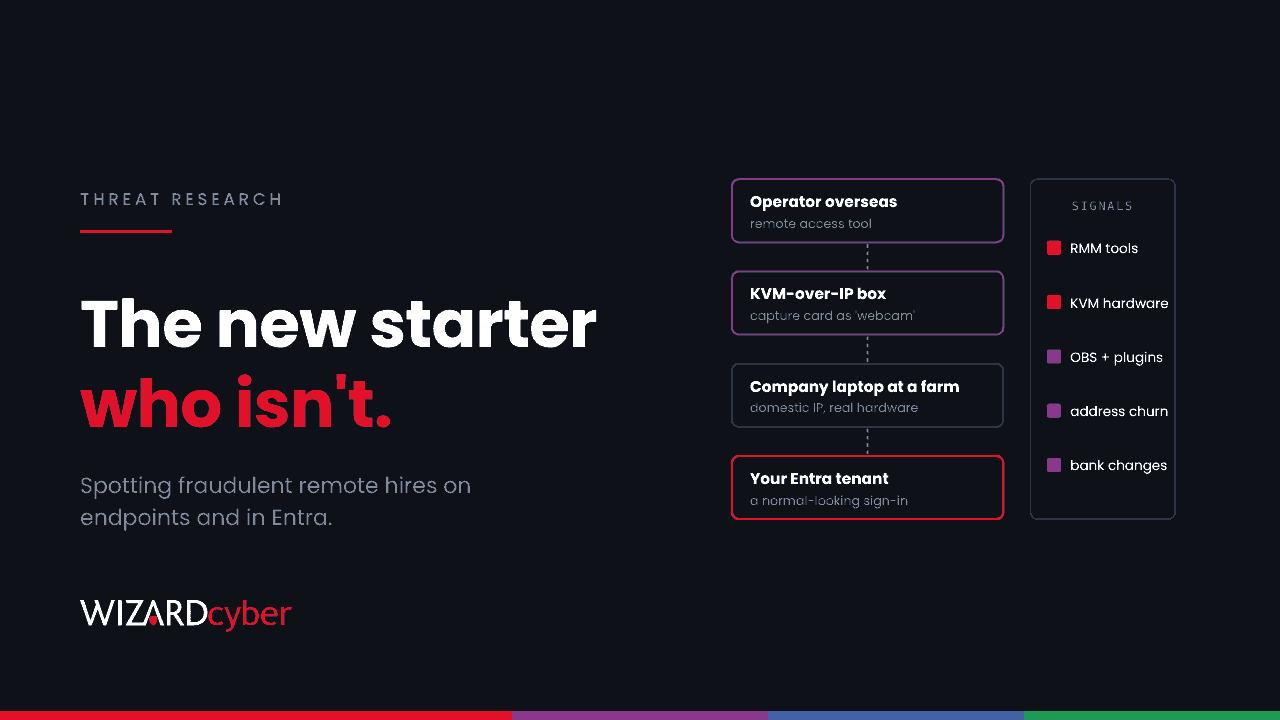
The New Starter Who Isn't: Spotting North Korean IT Workers On Your Endpoints And In Entra
The FBI says North Korean IT workers are widening their facilitator networks. The signals a SOC can see on endpoints and in Entra, with hunting queries.
Nothing matches that.