
Learning Hub
Clear, practical explainers on agentic AI, the modern SOC and the Microsoft security stack.
 Fundamentals
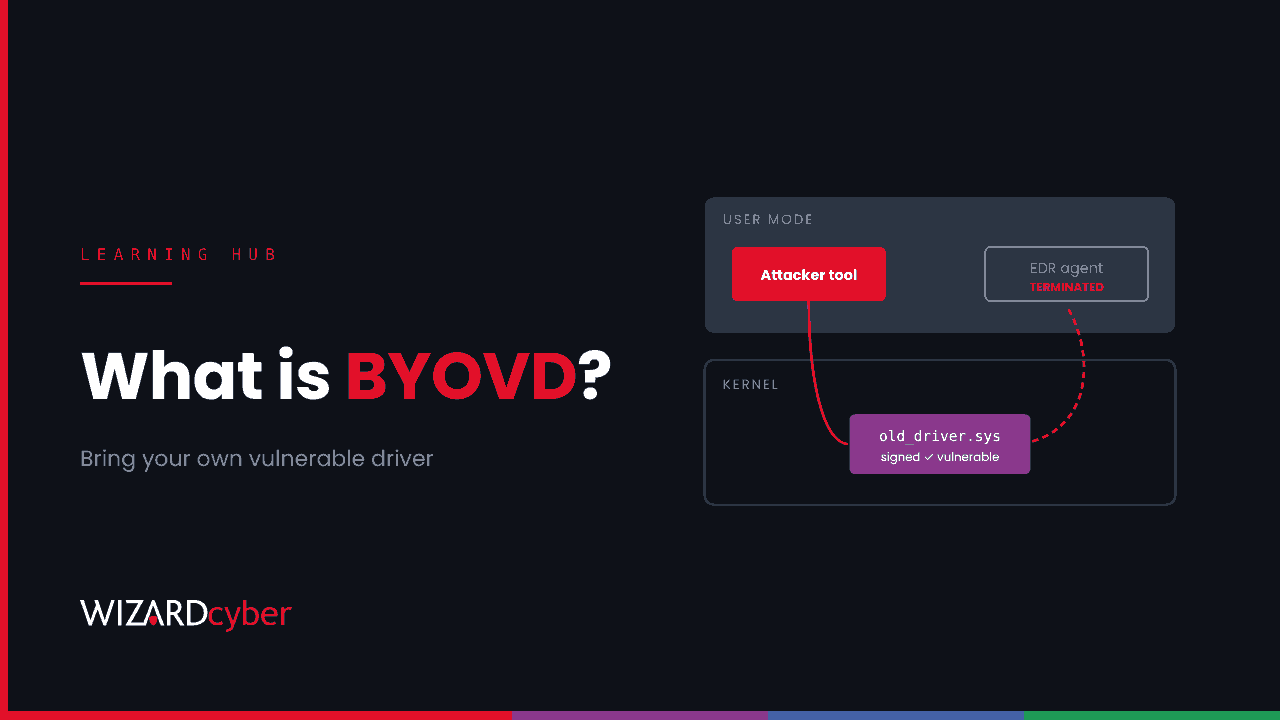
What Is BYOVD? Bring Your Own Vulnerable Driver Attacks Explained, And How To Block Them On Windows
BYOVD attacks load a signed but vulnerable driver to kill EDR before ransomware runs. How they work, and the Windows and Defender controls that stop them.
 Microsoft Security
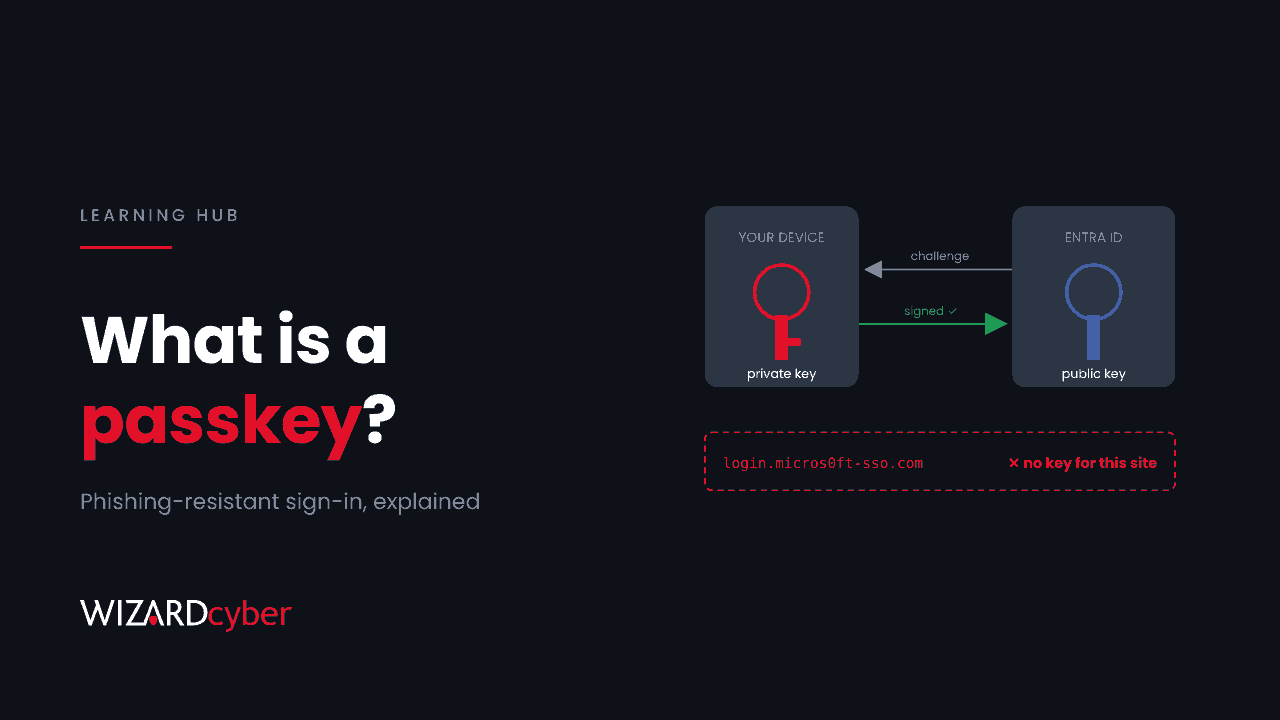
What Is A Passkey? How Passkeys Work, Why They Stop Phishing, And How To Manage Them In Microsoft Entra
A passkey signs you in with a key pair instead of a password, and can't be phished. How passkeys work, device-bound vs synced, and managing them in Entra.
 Fundamentals
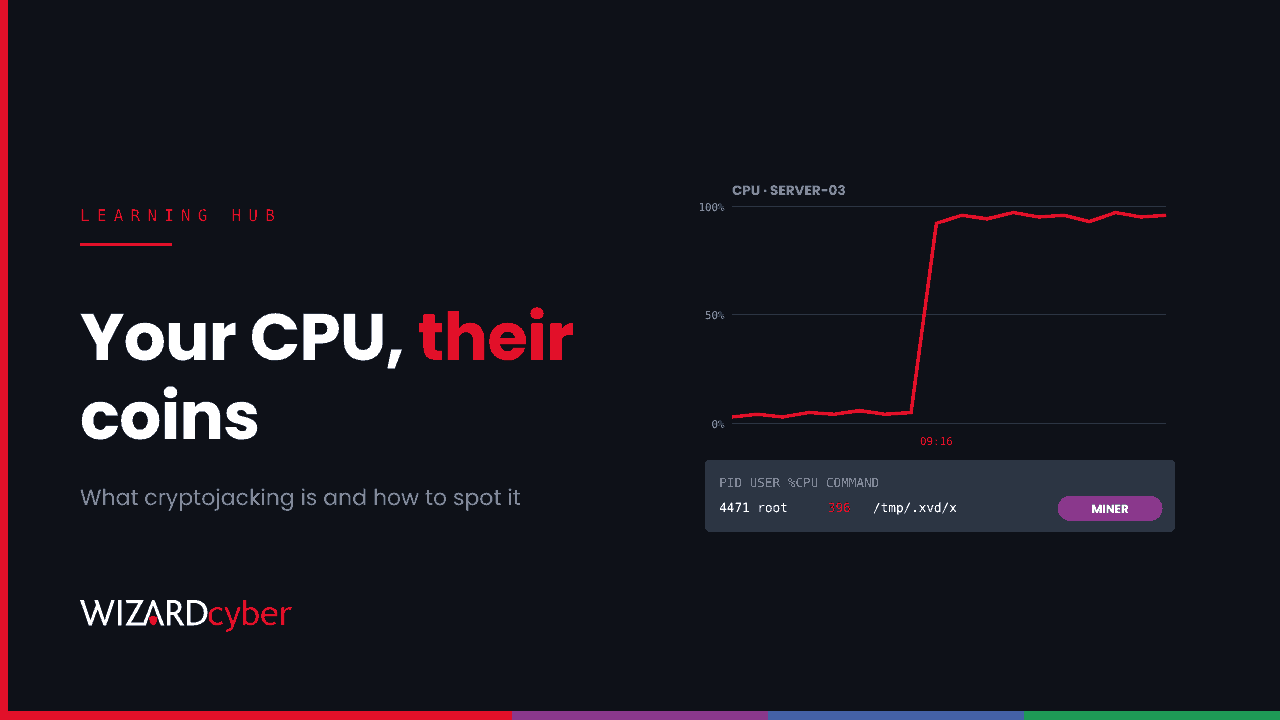
What Is Cryptojacking? How Hidden Miners Get In, From Servers To Browsers, And How To Spot Them
Cryptojacking is attackers mining cryptocurrency on your servers, cloud or browsers. How miners get in, the signs to look for, and why a miner is rarely alone.
 Fundamentals
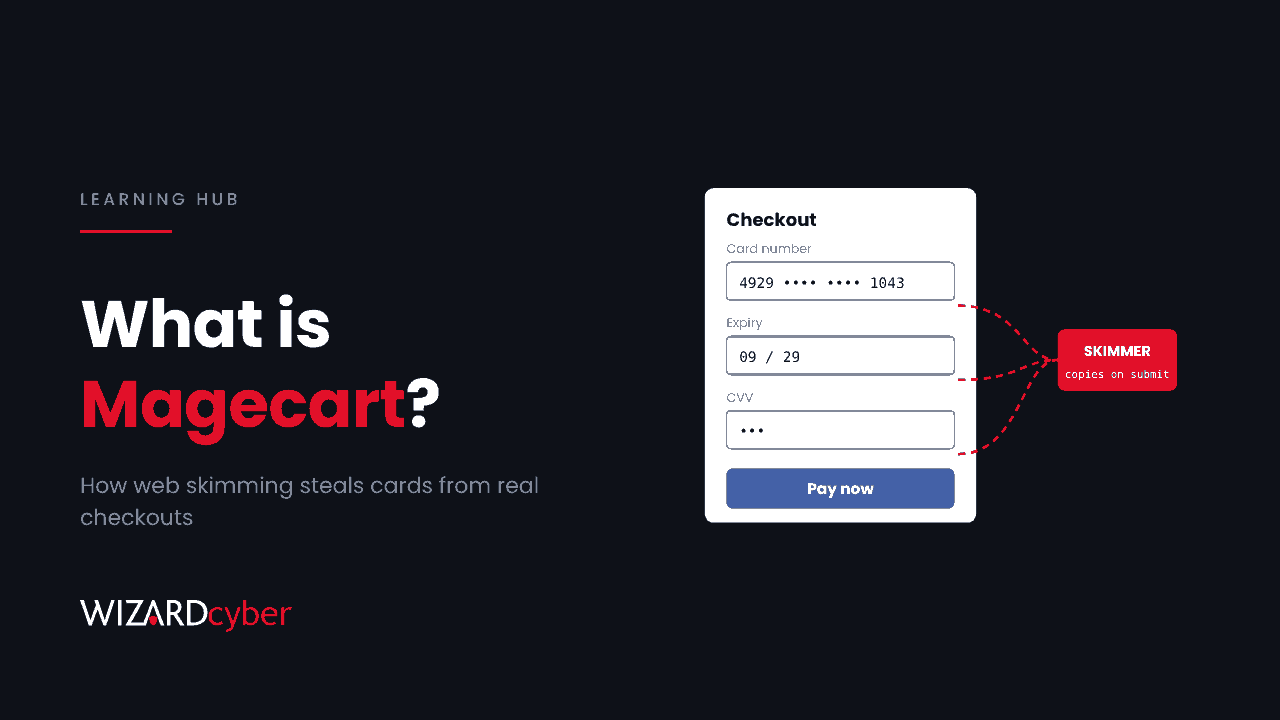
What Is A Magecart Attack? How Web Skimming Works, And How To Protect Your Site And Your Customers
Magecart attacks plant skimming code in websites to steal card details as customers type. How they work, how they get in, and how to protect your site.
 Fundamentals
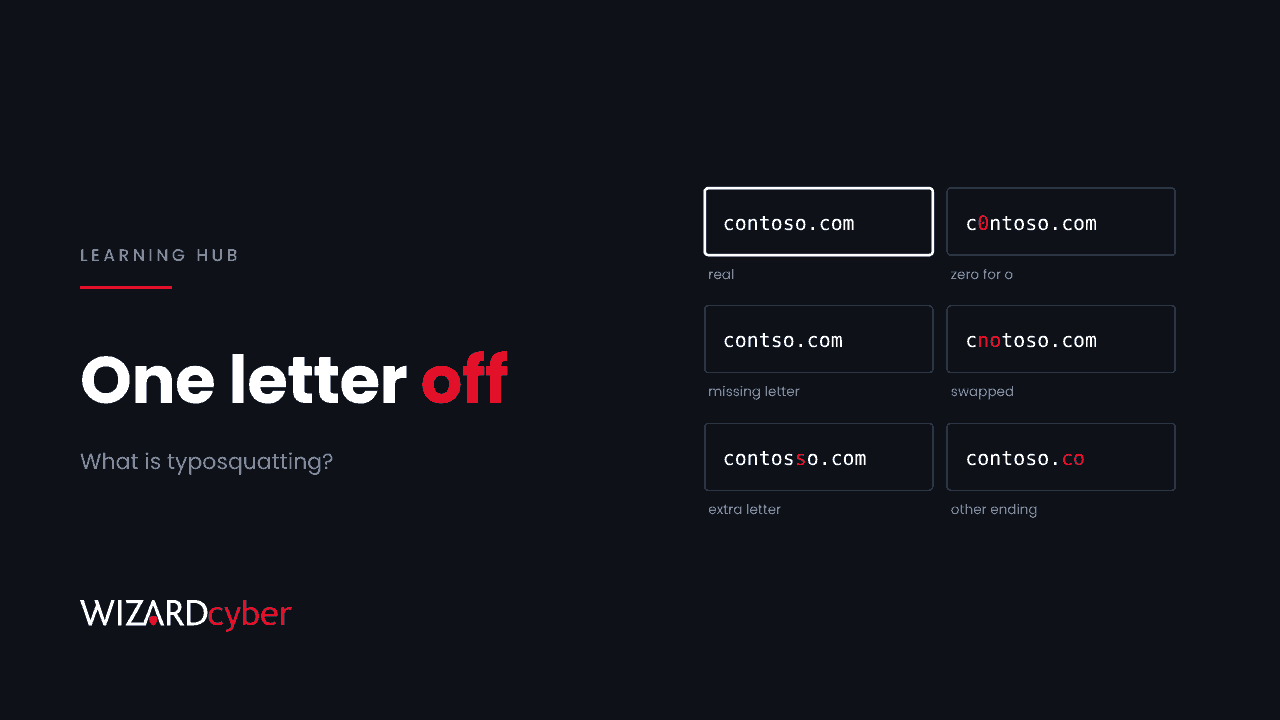
What Is Typosquatting? How Lookalike Domains Work, From Fake AI Sites To Phishing, And How To Protect Your Users
Typosquatting uses lookalike domains to catch typos and quick glances. How it works, what attackers use it for, and how to protect your users.
 Microsoft Security
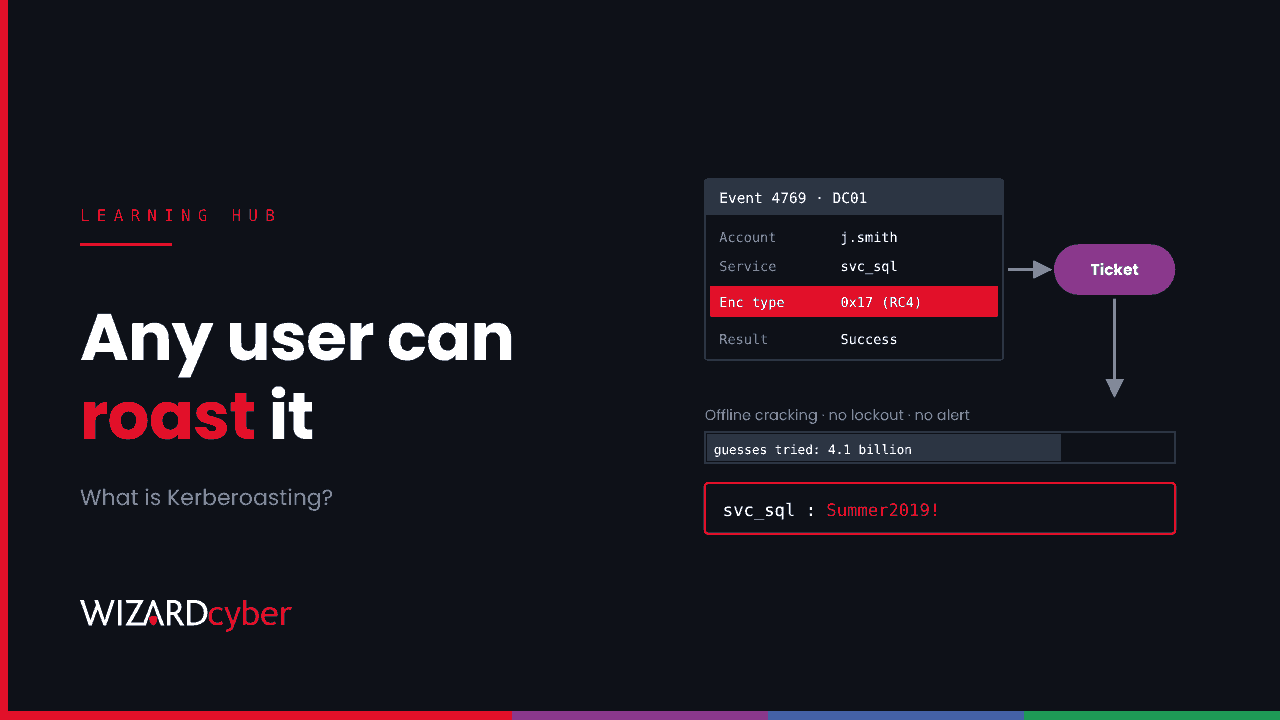
What Is Kerberoasting? How It Works, Why It Still Works, And How To Detect It In Active Directory
Kerberoasting lets any domain user crack service account passwords offline. How it works, why RC4 changes matter, and how to detect and stop it.
 Microsoft Security
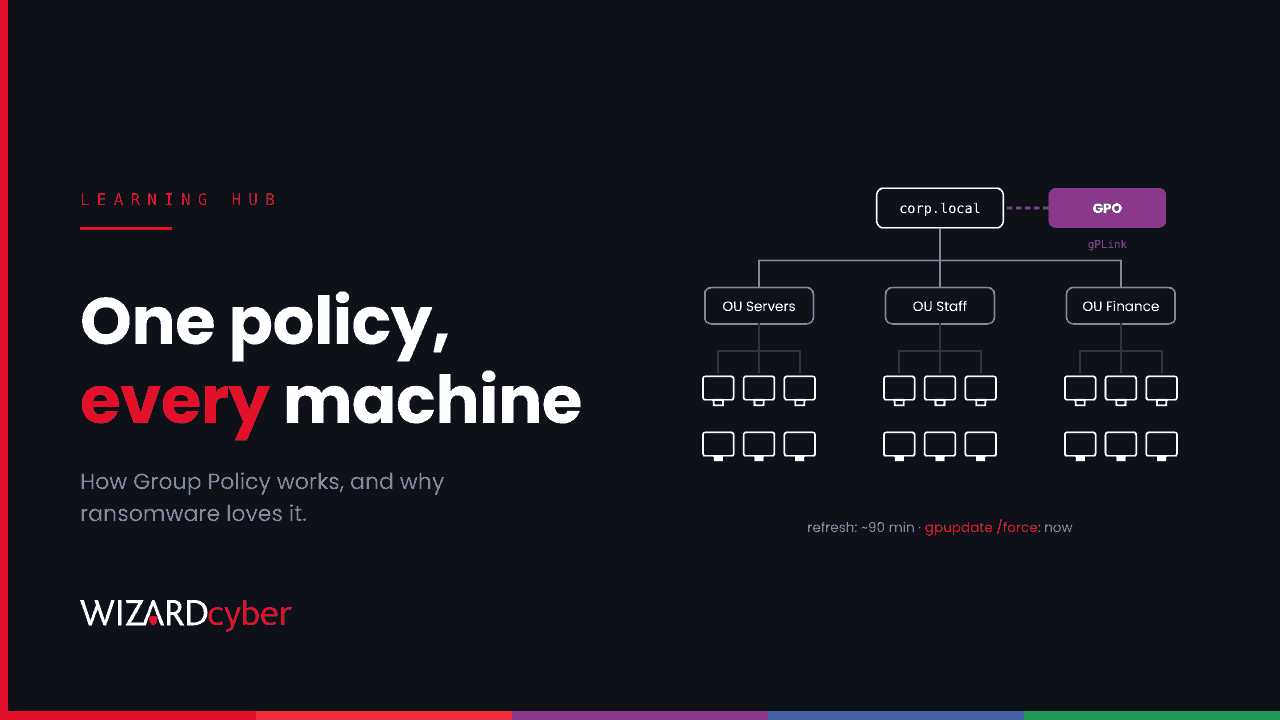
What Is Group Policy? How GPOs Work In Active Directory, And How Attackers Use Them To Deploy Ransomware
Group Policy applies settings to every machine in a domain. How GPOs work, how ransomware groups abuse them, and how to monitor and lock them down.
 Fundamentals
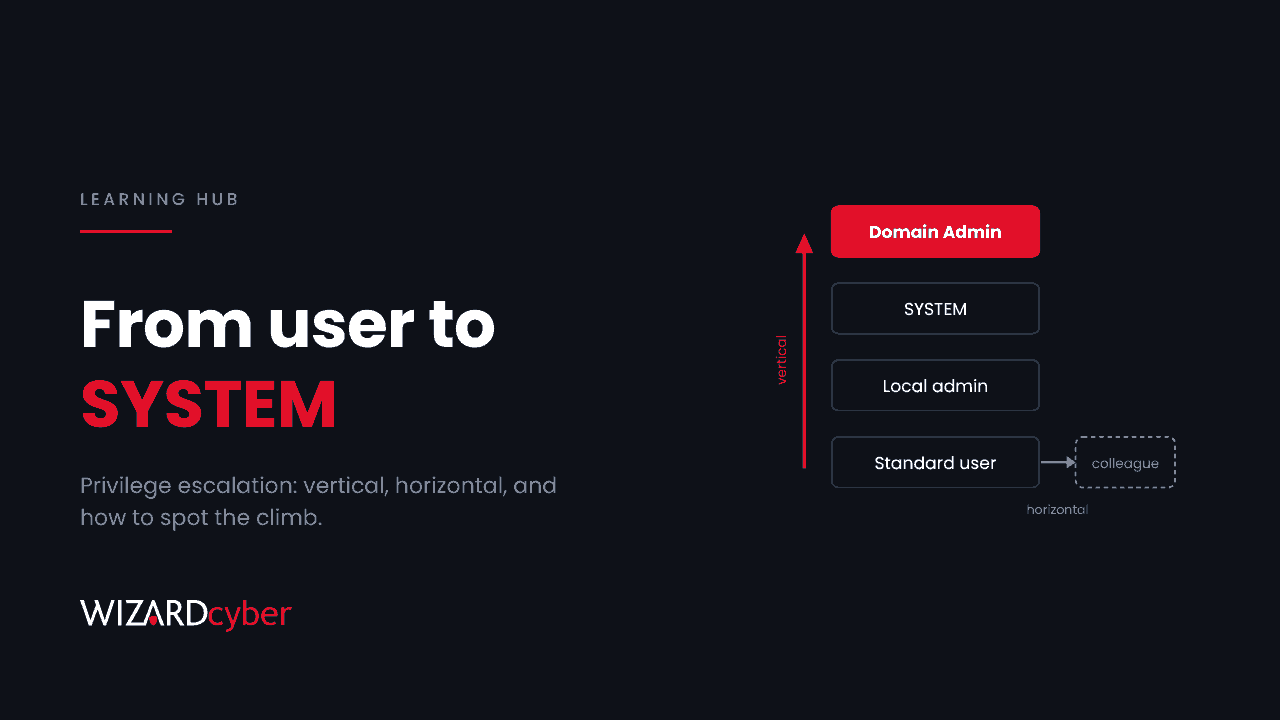
What Is Privilege Escalation? Vertical vs Horizontal, Real Windows Examples, And How To Detect It
Privilege escalation turns a weak foothold into admin or SYSTEM. Vertical vs horizontal, real Windows and AD examples, and how to detect it.
 Fundamentals
What Is A Remote Access Trojan (RAT)? How RATs Work, Why Attackers Now Use Legitimate Remote Tools, And How To Spot Them
A remote access trojan gives an attacker hidden control of a computer. How RATs work, why attackers now misuse real remote tools, and how to spot them.
 AI Driven Security Operations
What Is Data Poisoning? How Attackers Corrupt AI Models, And How To Check The Models You Deploy
Data poisoning corrupts what an AI model learns so it behaves as an attacker wants. The types, how it happens, and how to check models you deploy.
 Fundamentals
What Is Pass-The-Hash? How Attackers Reuse NTLM Hashes, And How To Detect It In Active Directory
Pass-the-hash lets attackers sign in with a stolen NTLM hash instead of a password. How it works, where hashes come from, and how to detect and stop it.
 Fundamentals
What Is CVSS? How Vulnerability Scores Work, And Why A 6.5 Can Matter More Than A 9.9
CVSS rates how severe a vulnerability is, not how likely it is to be exploited. How scores are built, what changed in v4.0, and how to use them.
 Fundamentals
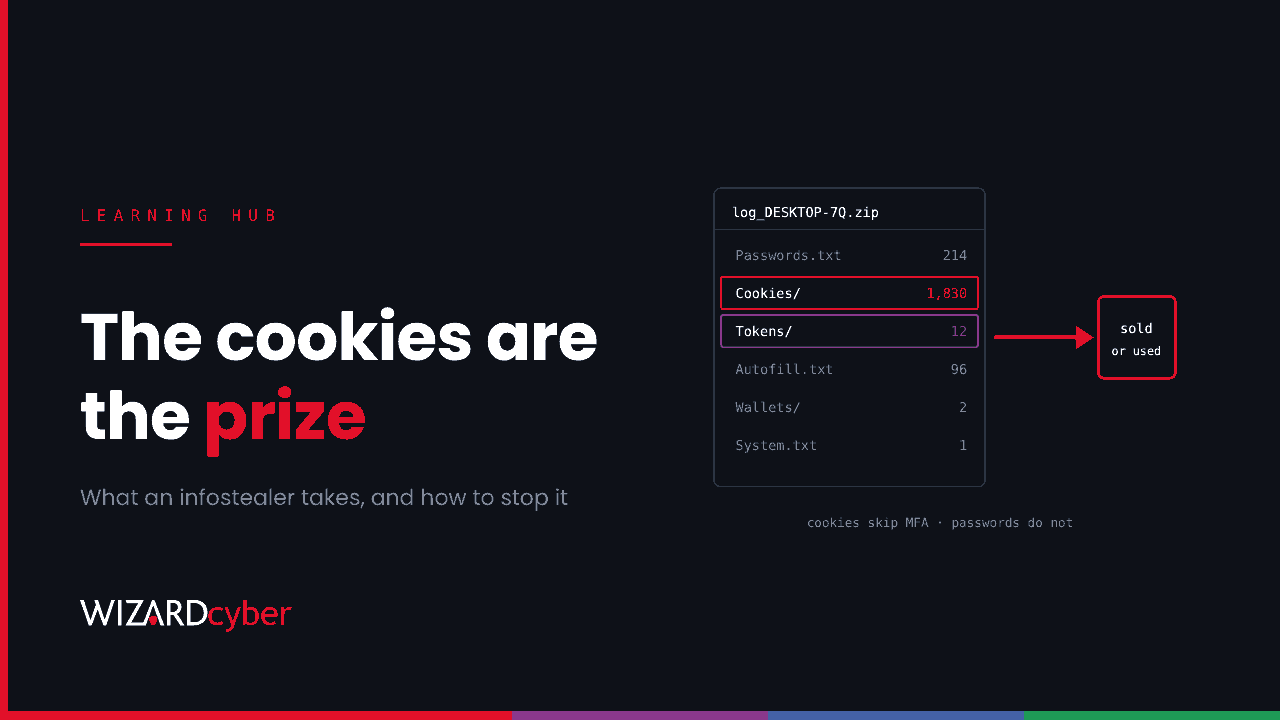
What Is An Infostealer? How Credential-Stealing Malware Works, And Why Your Browser Cookies Are The Prize
Infostealers grab saved passwords, cookies and tokens in seconds. How they get in, why stolen cookies skip MFA, and how to detect and respond.
 Fundamentals
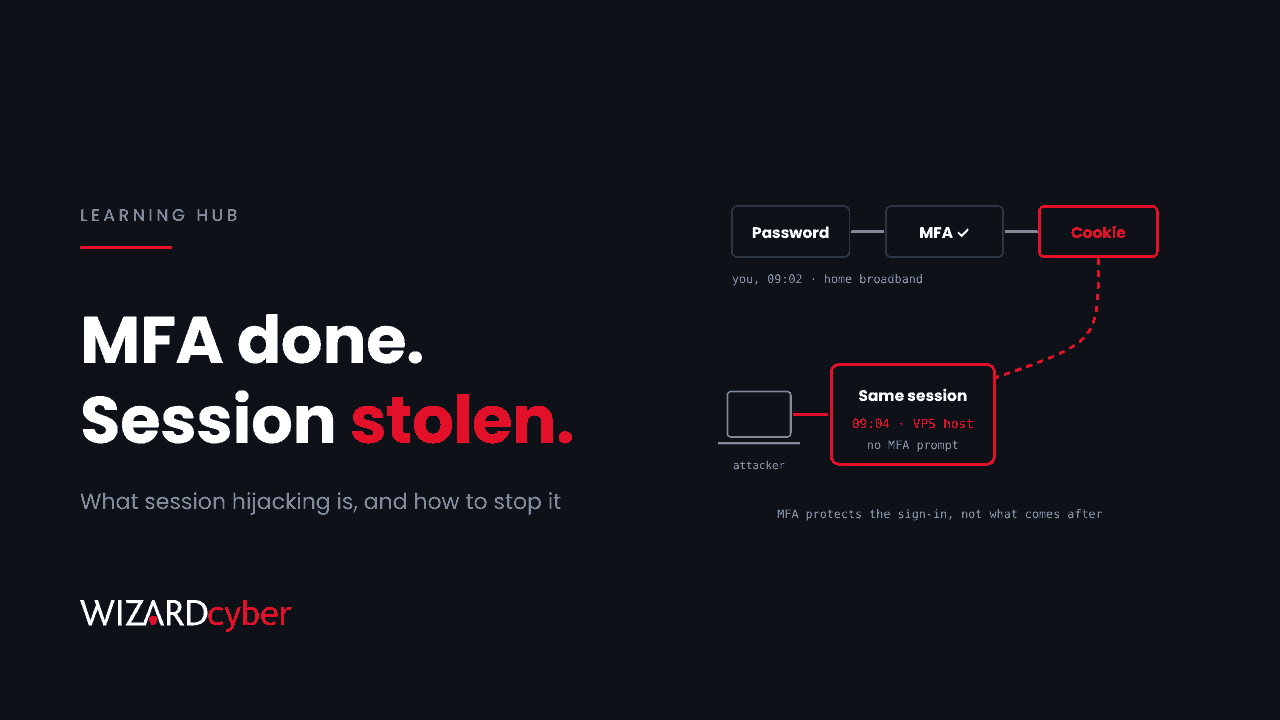
What Is Session Hijacking? How Stolen Sessions Bypass MFA In Microsoft 365, And How To Stop It
Session hijacking lets attackers reuse your signed-in session, so MFA never applies. How it works in Microsoft 365, and how to prevent and detect it.
 Microsoft Security
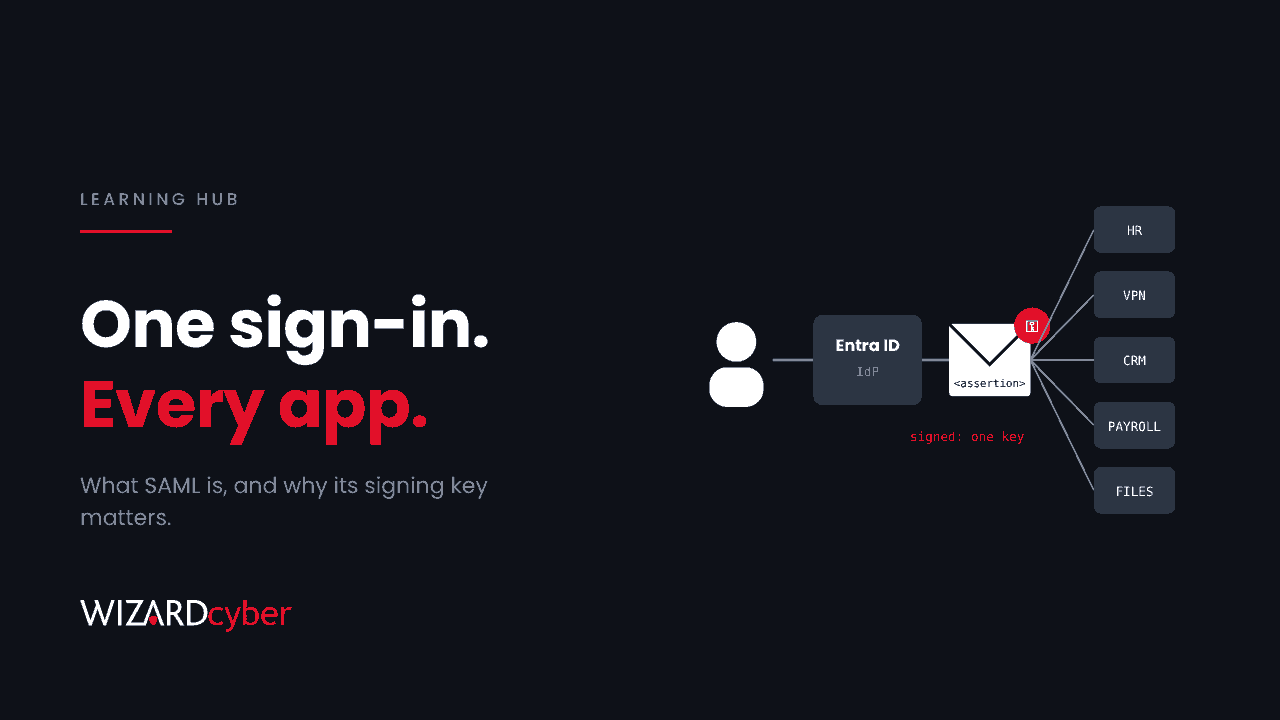
What Is SAML? How SAML Single Sign-On Works In Microsoft Entra ID, And How Attackers Abuse It
SAML lets Entra ID sign users in once for every app. How SAML SSO works, SAML vs OAuth, how attackers abuse it, and how to detect it.
 Fundamentals
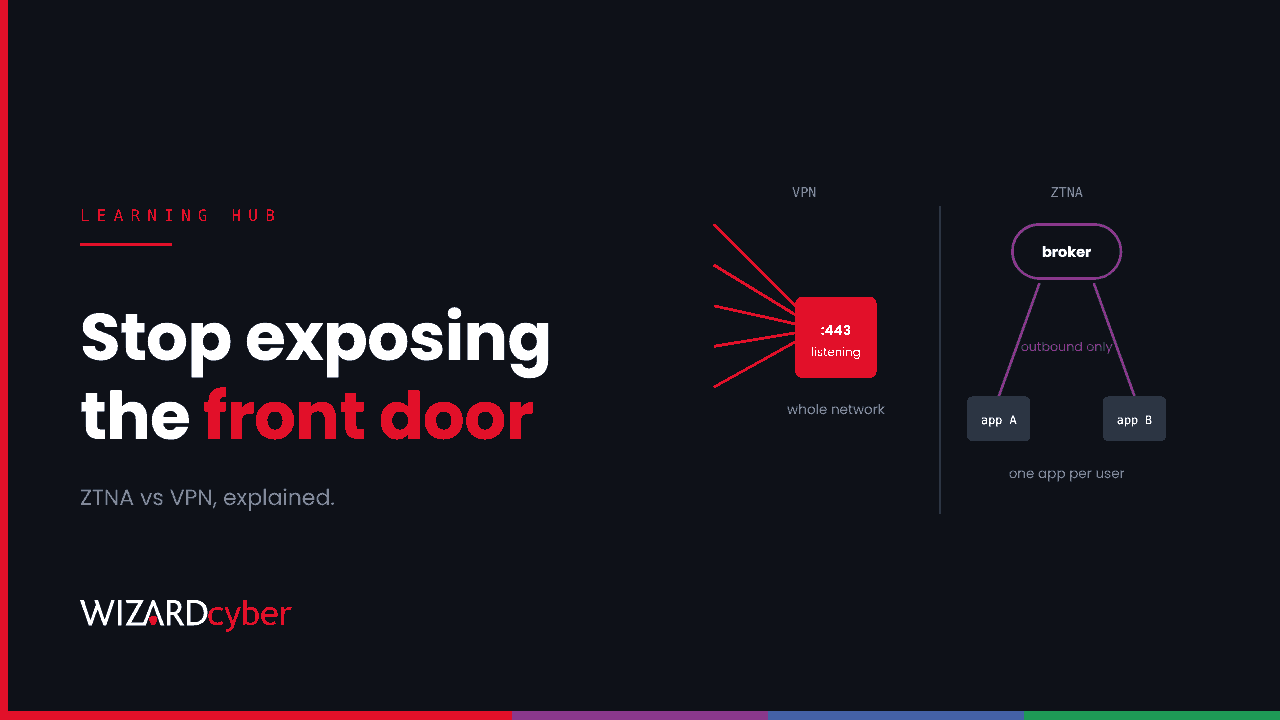
What Is ZTNA? Zero Trust Network Access vs VPN, And What Changes For Your SOC
ZTNA gives users access to single apps, not the network, with nothing listening on the internet. How it works, ZTNA vs VPN, and its limits.
 Microsoft Security
What Is Workload Identity Federation? Removing Stored Secrets From Your CI/CD Pipelines And Azure Apps
Workload identity federation lets pipelines and external workloads reach Entra ID resources without a stored secret. How it works and how to secure it.
 Fundamentals
What Is Mimikatz? How Attackers Steal Windows Credentials, And How To Detect And Stop It
Mimikatz pulls passwords, hashes and Kerberos tickets out of Windows. How it works, why it still succeeds, and how to detect and block it.
 Fundamentals
What Is A Watering Hole Attack? How Attackers Poison Trusted Websites, And How To Defend Against It
A watering hole attack poisons a website your people already trust. How it works, real examples, and how to defend against it in Microsoft environments.
 Fundamentals
What Is Phishing-As-A-Service (PhaaS)? How Phishing Kits Work, And Why They Get Past MFA
Phishing-as-a-service rents ready-made phishing kits to criminals. How the kits work, why many beat MFA, and the defences that work in Microsoft 365.
 Microsoft Security
What Is A Managed Identity? Replacing Client Secrets In Azure And Entra ID
A managed identity lets Azure workloads get tokens without storing a secret. System vs user-assigned, when to use federation, and how to find secrets.
 Microsoft Security
What Is GDAP? Granular Delegated Admin Privileges Explained, And How To Review Your Partners' Access
GDAP gives Microsoft partners time-limited, role-based admin access to your tenant. How it works, how it differs from DAP, and how to review it.
 Microsoft Security
What Is LDAP? How It Works In Active Directory, And How Attackers Use It For Reconnaissance
LDAP is how applications read and search Active Directory. How it works, LDAPS, signing and channel binding, and how attackers use it to map your domain.
 Fundamentals
What Is The Vulnerability Management Lifecycle? The Six Stages, And Where Most Programmes Stall
The vulnerability management lifecycle: discover, assess, prioritise, remediate, verify, report. What each stage involves, and where programmes stall.
 Microsoft Security
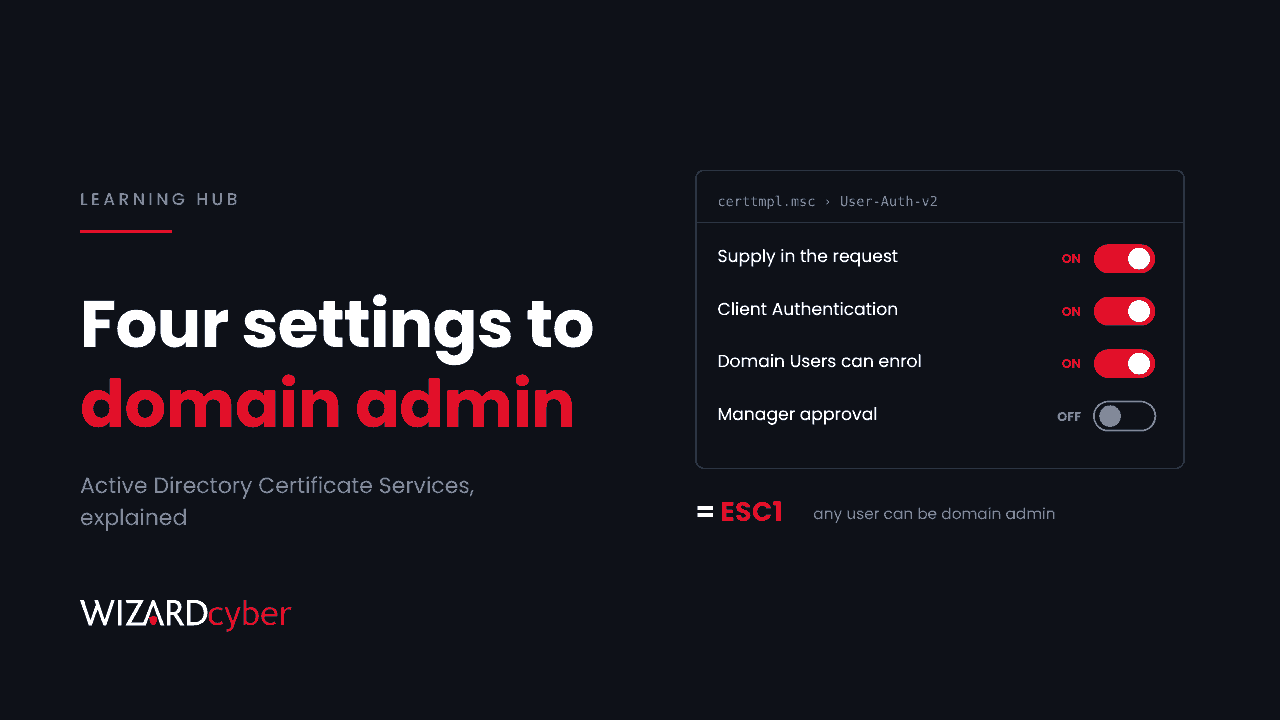
What Is AD CS? Active Directory Certificate Services, ESC1 And ESC8 Explained, And How To Harden Them
AD CS issues the certificates your Windows estate trusts. How it works, why ESC1 and ESC8 turn it into a route to domain admin, and how to audit and harden it.
 Fundamentals
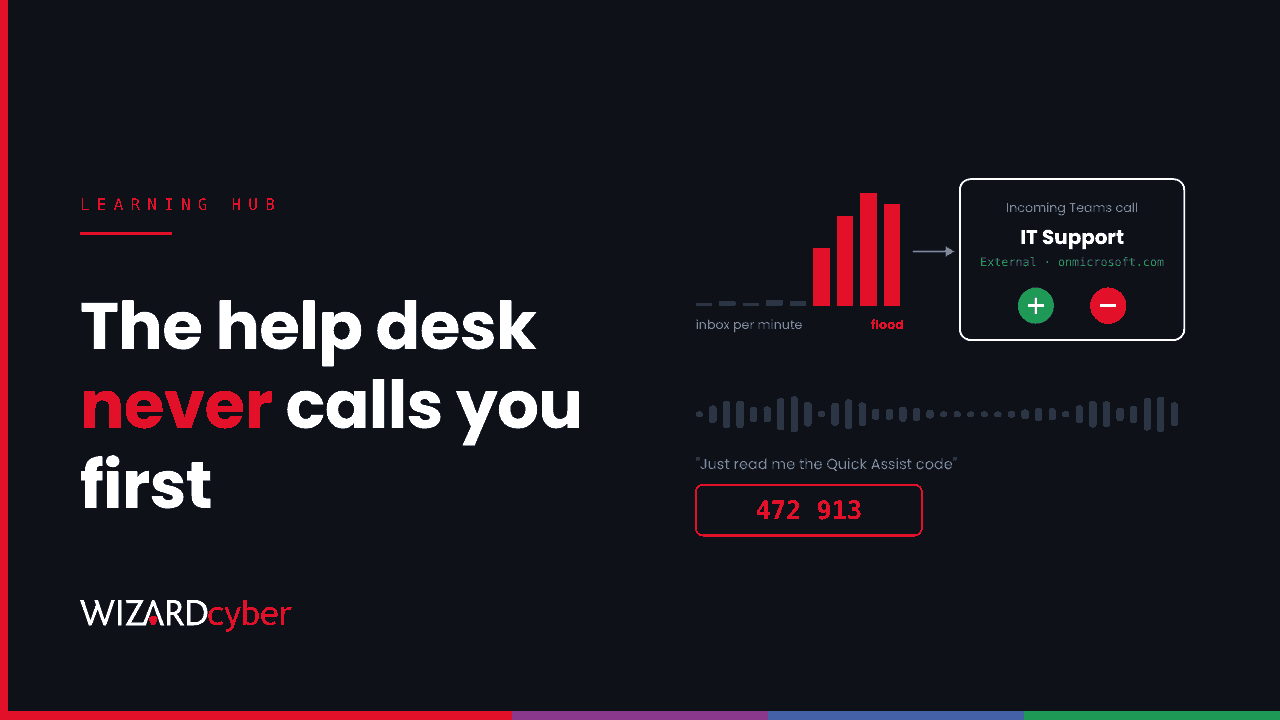
What Is Vishing? How Voice Phishing Works, From Fake Help Desk Calls To Teams, And How To Stop It
Vishing is phishing by phone or voice call. How it works, from fake help desk calls on Teams to cloned voices, and the checks and Microsoft 365 controls that stop it.
 Fundamentals
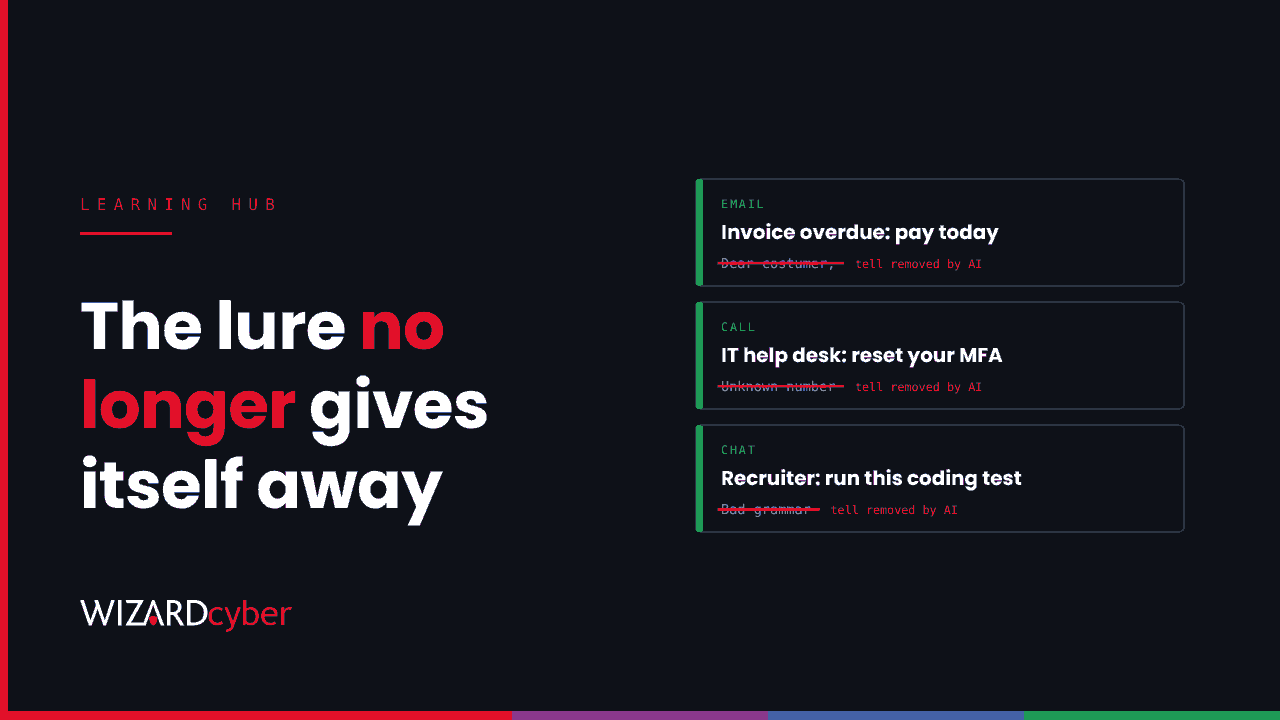
What Is Social Engineering? How Attackers Manipulate People, And What AI Has Changed
Social engineering manipulates people into handing over access, money or data. The main types, what AI has changed and the Microsoft 365 controls that help.
 Microsoft Security
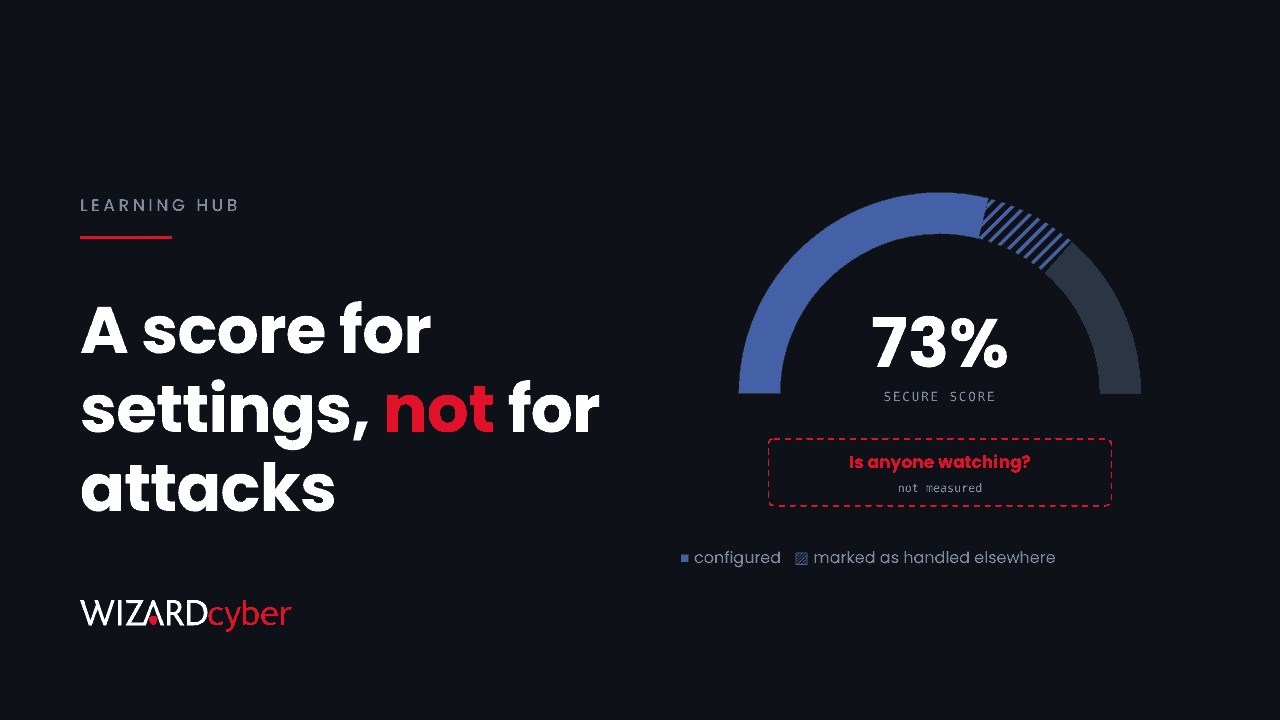
What Is Microsoft Secure Score? What It Measures, What It Misses, And How To Raise It Safely
Microsoft Secure Score measures your Microsoft 365 security configuration. How it is calculated, what it misses, and how to raise it safely.
 Fundamentals
What Is An SBOM? Software Bills Of Materials Explained, And How To Use One When The Next Library Flaw Lands
An SBOM lists the components inside a piece of software. What it contains, the main formats, how to get one from suppliers and how to use it in a crisis.
 Fundamentals
What Is An Advanced Persistent Threat (APT)? How Nation-State Groups Operate, And How To Spot One In Microsoft 365
An APT is a skilled, well-resourced attacker that stays hidden in a network for months. How they operate, how they're named and the signs to look for.
 Fundamentals
What Is An RMM Tool? Why Attackers Love Remote Monitoring And Management Software, And How To Spot Rogue Agents
RMM tools let IT manage devices remotely, and attackers love them for the same reason. How RMM gets abused and how to find unapproved agents in Defender.
 Fundamentals
What Is Credential Stuffing? How It Works, How It Differs From Password Spraying, And How To Stop It In Microsoft Entra
Credential stuffing replays leaked username and password pairs at scale. How it works, how it differs from spraying and how to spot and stop it in Entra.
 Microsoft Security
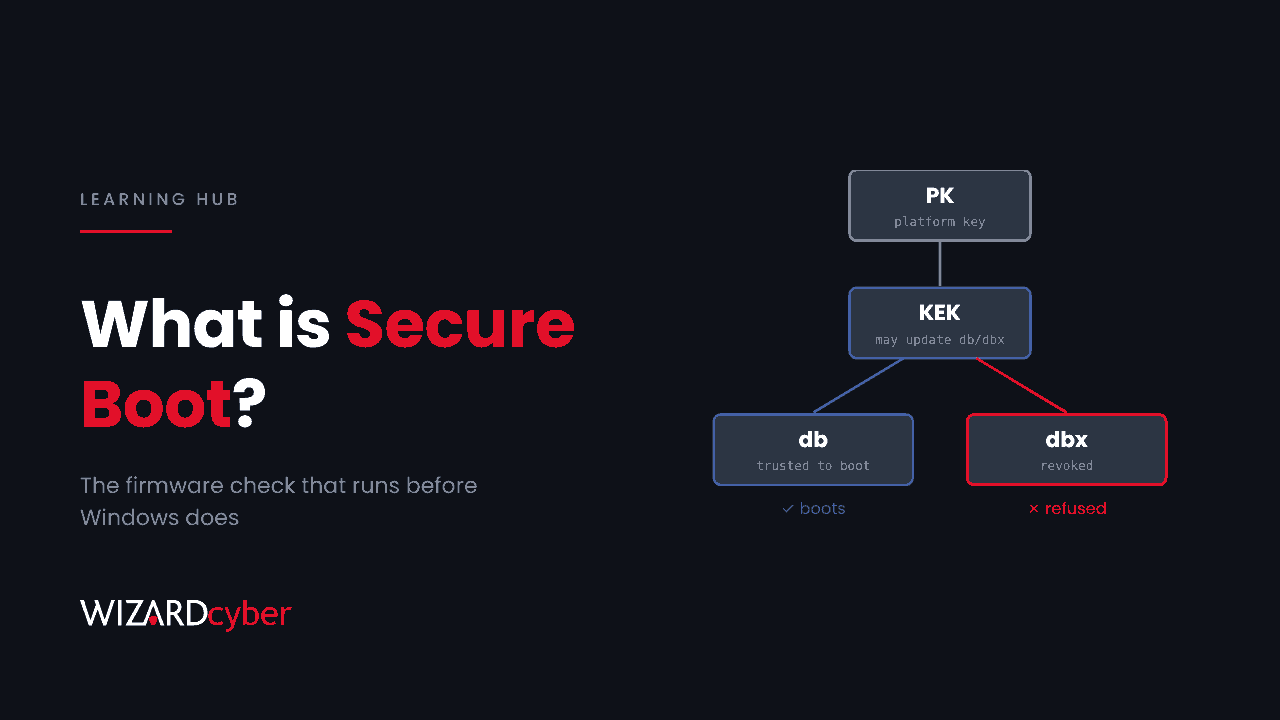
What Is Secure Boot? How It Works, Why It Matters, And How Bootkits Still Get Past It
Secure Boot only lets signed, trusted software start before Windows. How it works, what it misses, the 2026 certificate changes and how to check it.
 Fundamentals
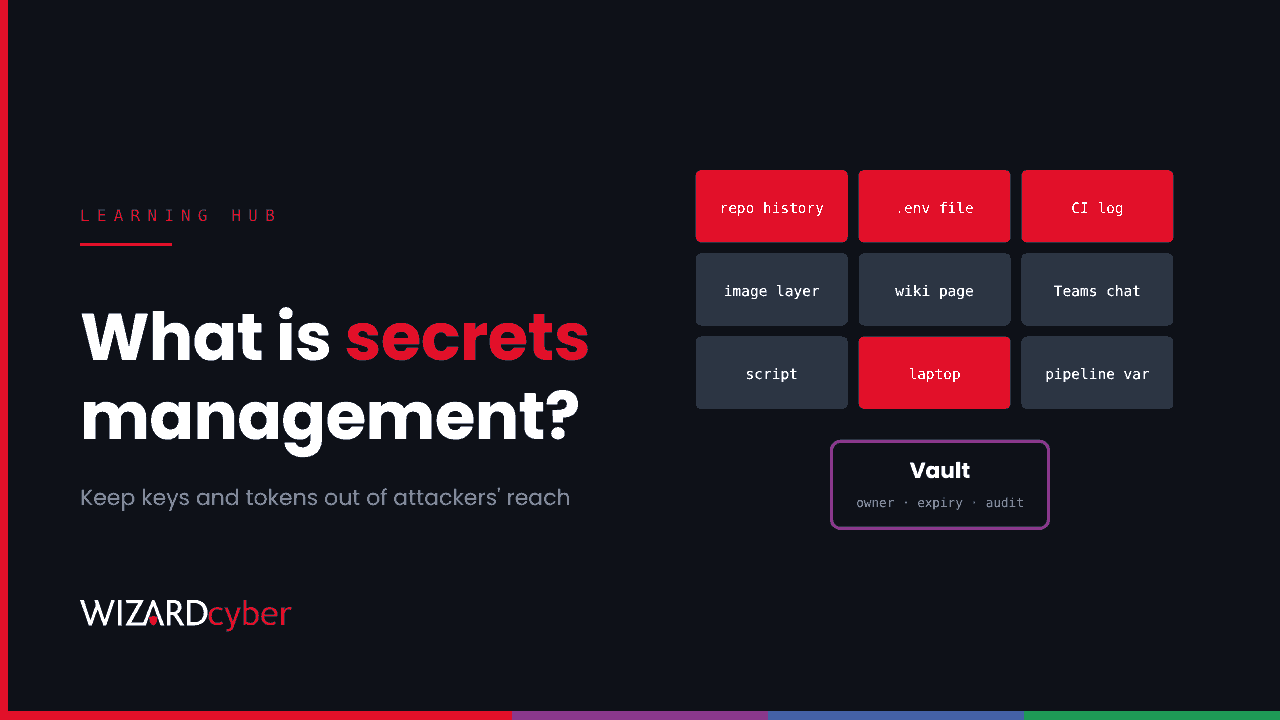
What Is Secrets Management? Keeping API Keys, Tokens And Passwords Out Of Attackers' Reach
Secrets management keeps API keys, tokens and passwords out of code and files. Where secrets leak, how vaults and managed identities work, and what to do.
 Fundamentals
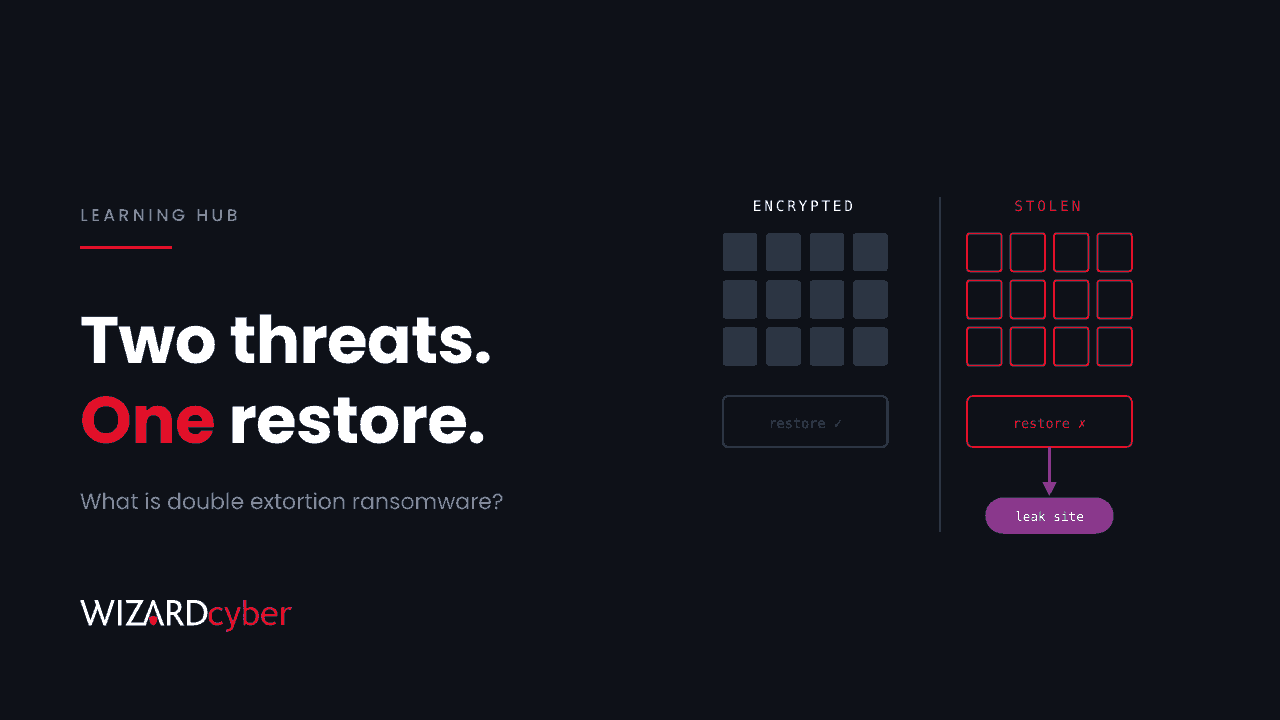
What Is Double Extortion Ransomware? How It Works, And Why Backups Alone Won't Save You
Double extortion ransomware steals data before encrypting it, so restoring from backup is only half the answer. How it works and how to reduce the damage.
 Microsoft Security
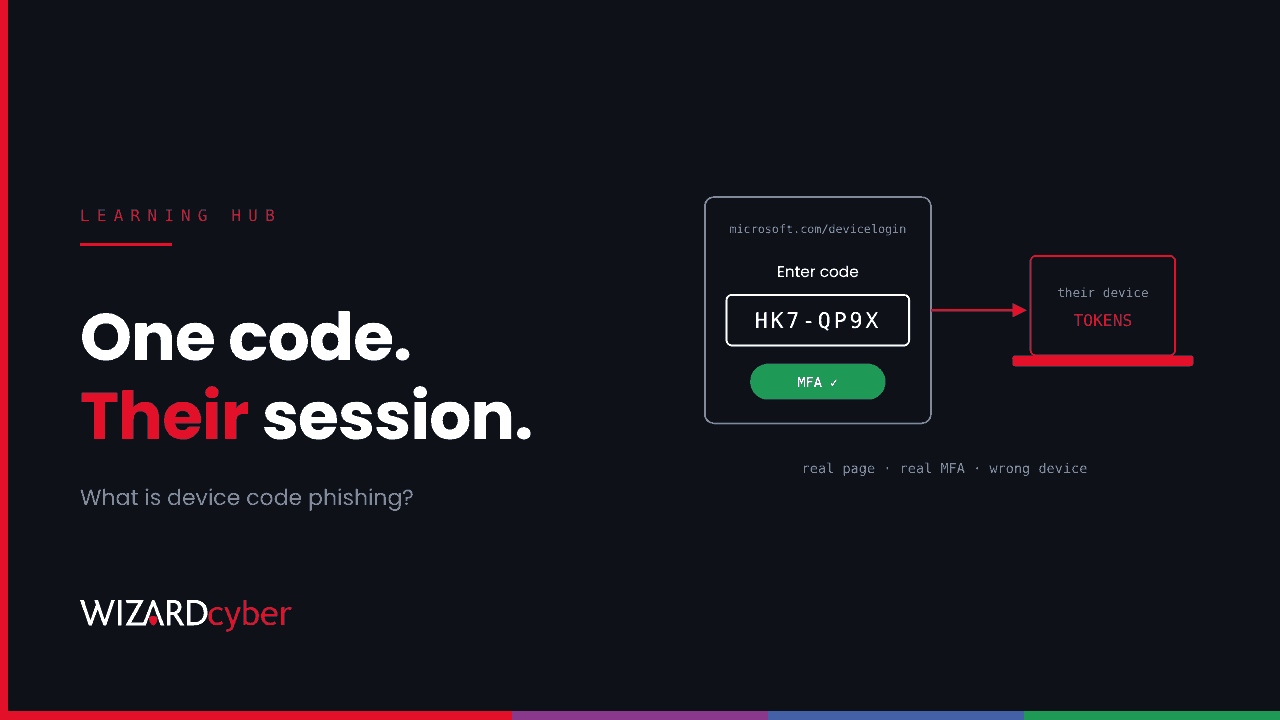
What Is Device Code Phishing? How It Works In Microsoft 365, And How To Block It
Device code phishing tricks users into signing in on Microsoft's real page for an attacker's device. How it works, how to detect it and how to block it.
 Fundamentals
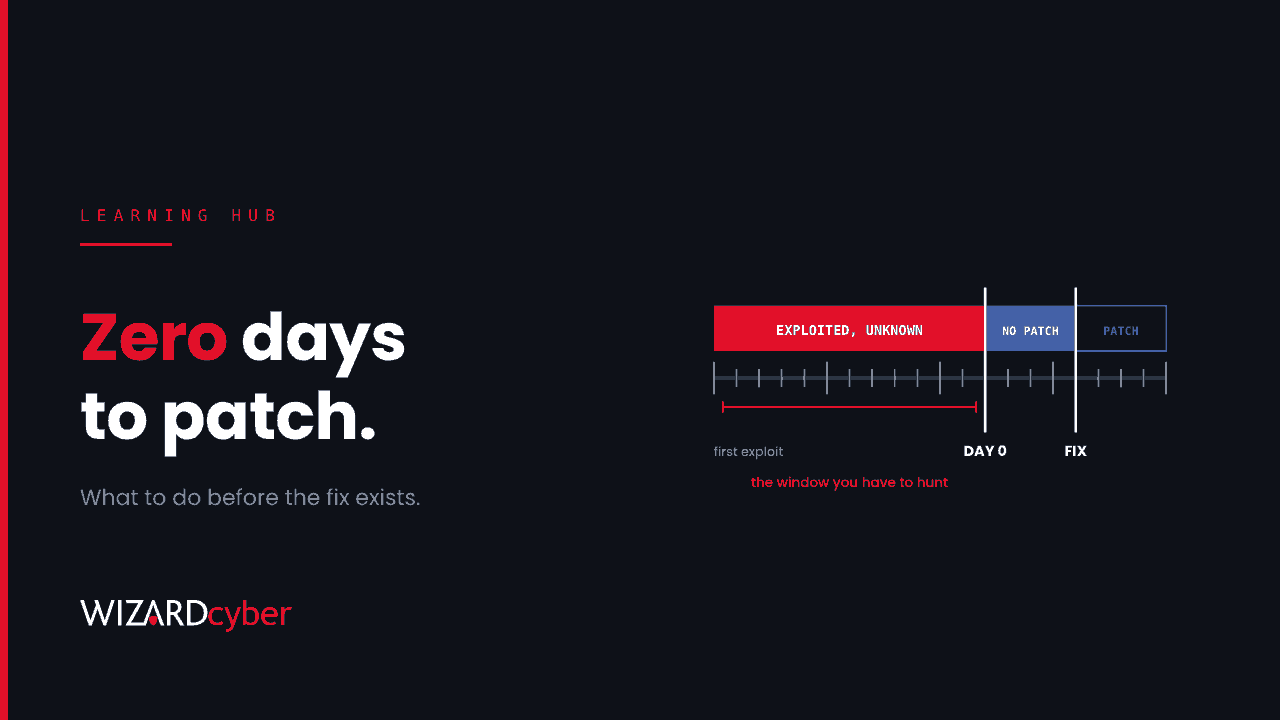
What Is A Zero-Day Attack? How Zero-Days Work, And What You Can Do Before The Patch Exists
A zero-day attack exploits a flaw before a fix exists. How zero-days differ from n-days, why they matter, and what to do in the first 72 hours.
 Fundamentals
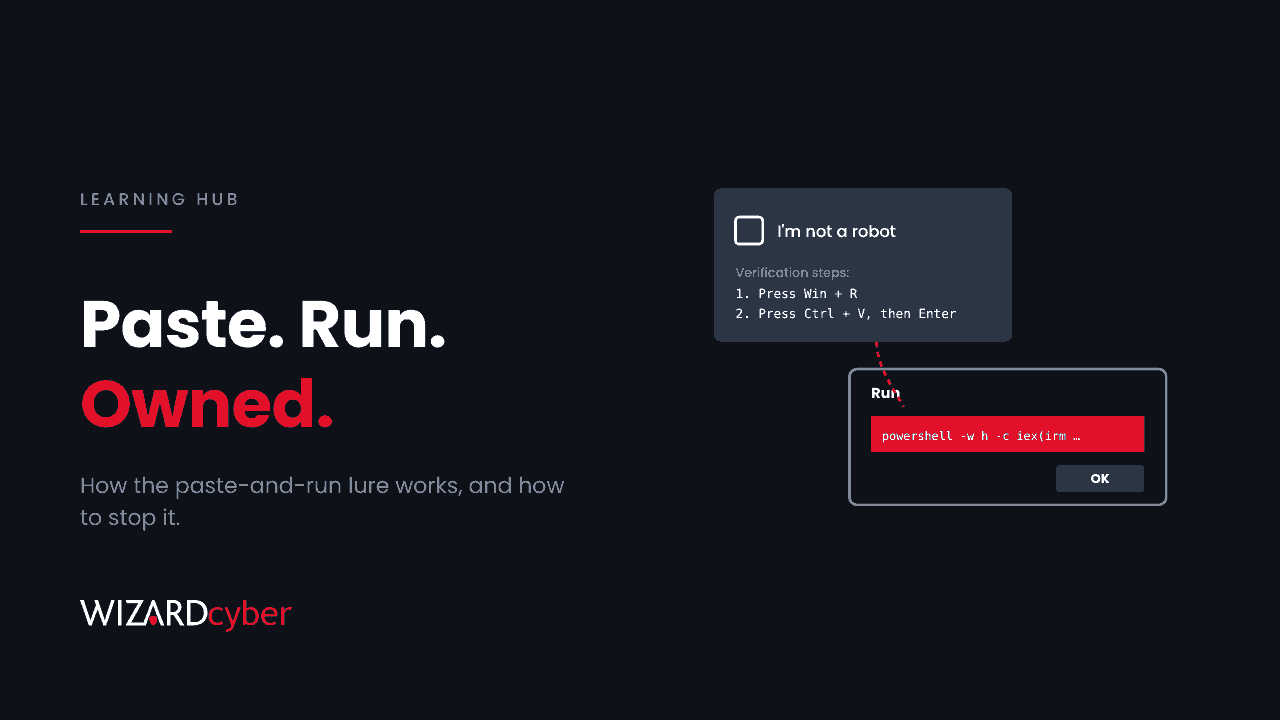
What Is ClickFix? How The Paste-And-Run Lure Works, And How To Stop It
ClickFix tricks people into pasting and running an attacker's command themselves. How the lure works, why it beats email filters, and how to stop it.
 Microsoft Security
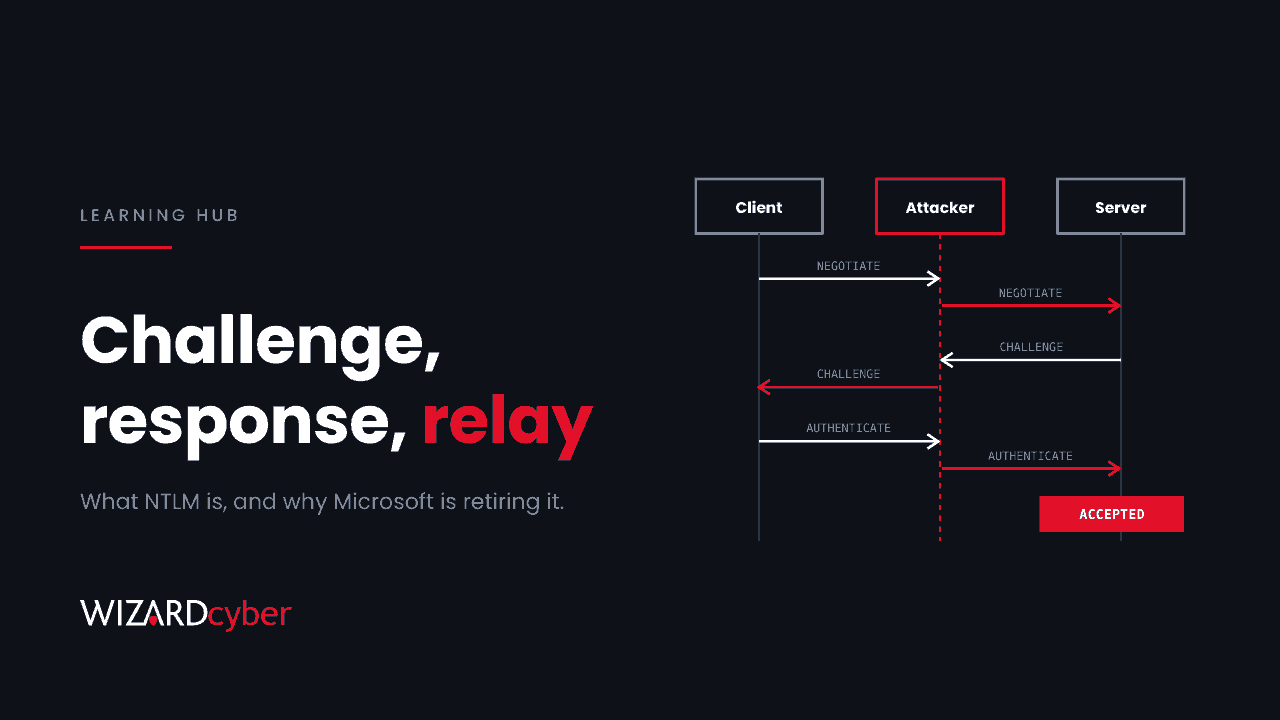
What Is NTLM? How It Works, Why Microsoft Is Retiring It, And How Attackers Abuse It
NTLM is Windows' older challenge-response authentication. How it works, how it differs from Kerberos, how attackers abuse it, and how to find and reduce it.
 Fundamentals
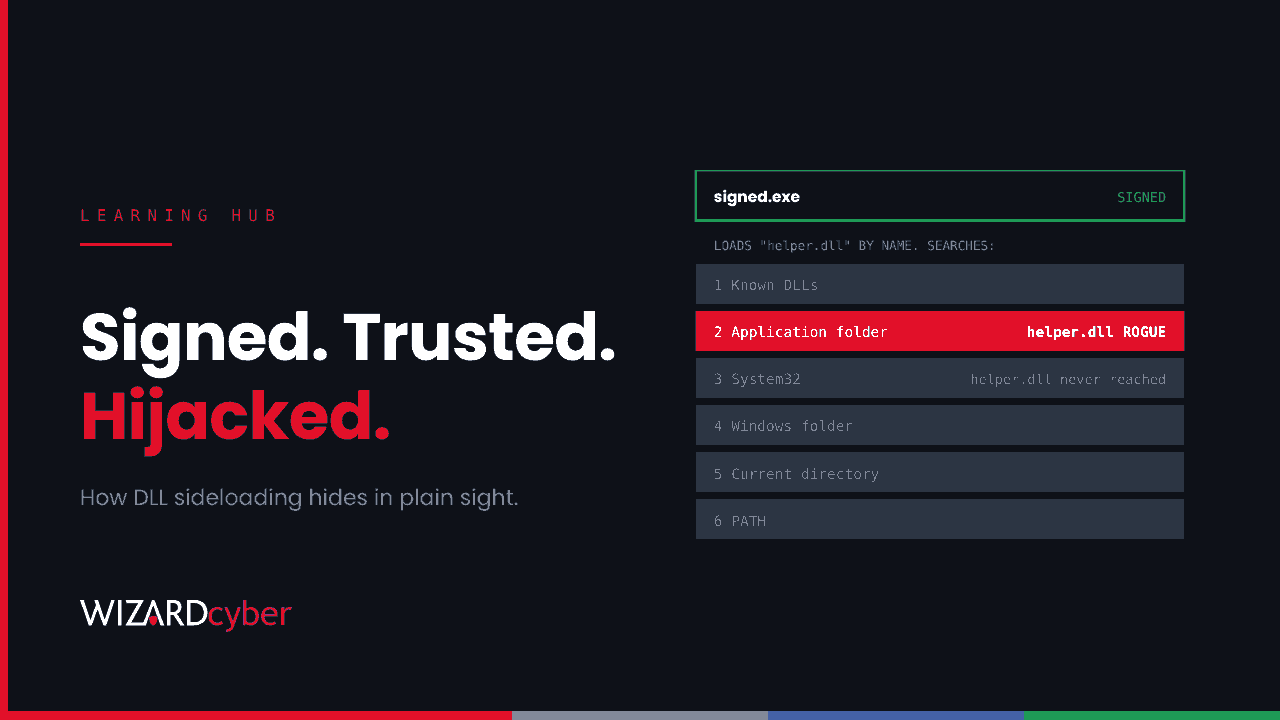
What Is DLL Sideloading? How Attackers Hide Inside Signed Software
DLL sideloading gets a trusted, signed program to load an attacker's code. How it works, how it differs from DLL hijacking, and how to detect and stop it.
 Microsoft Security
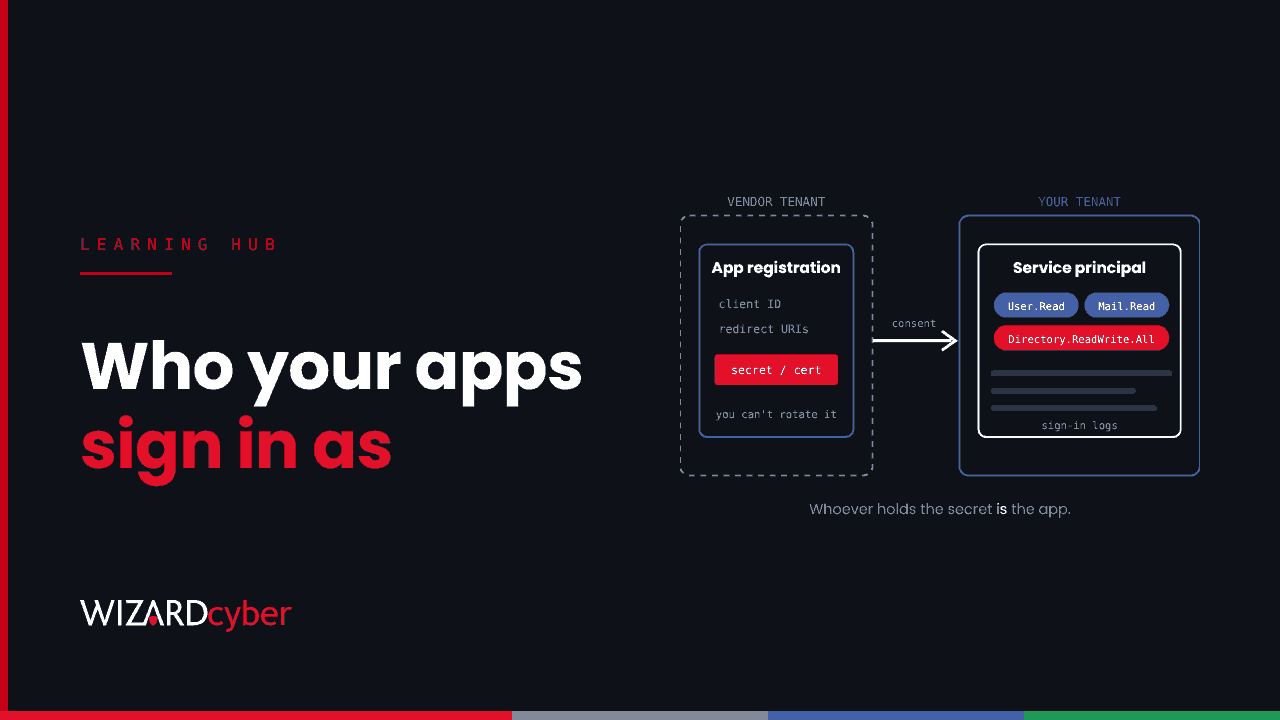
What Is A Service Principal? App Registrations, Enterprise Apps And How To Secure Them In Entra
A service principal is an app's identity in your Entra tenant. How it relates to app registrations, where secrets live, and how to secure and monitor them.
 Fundamentals
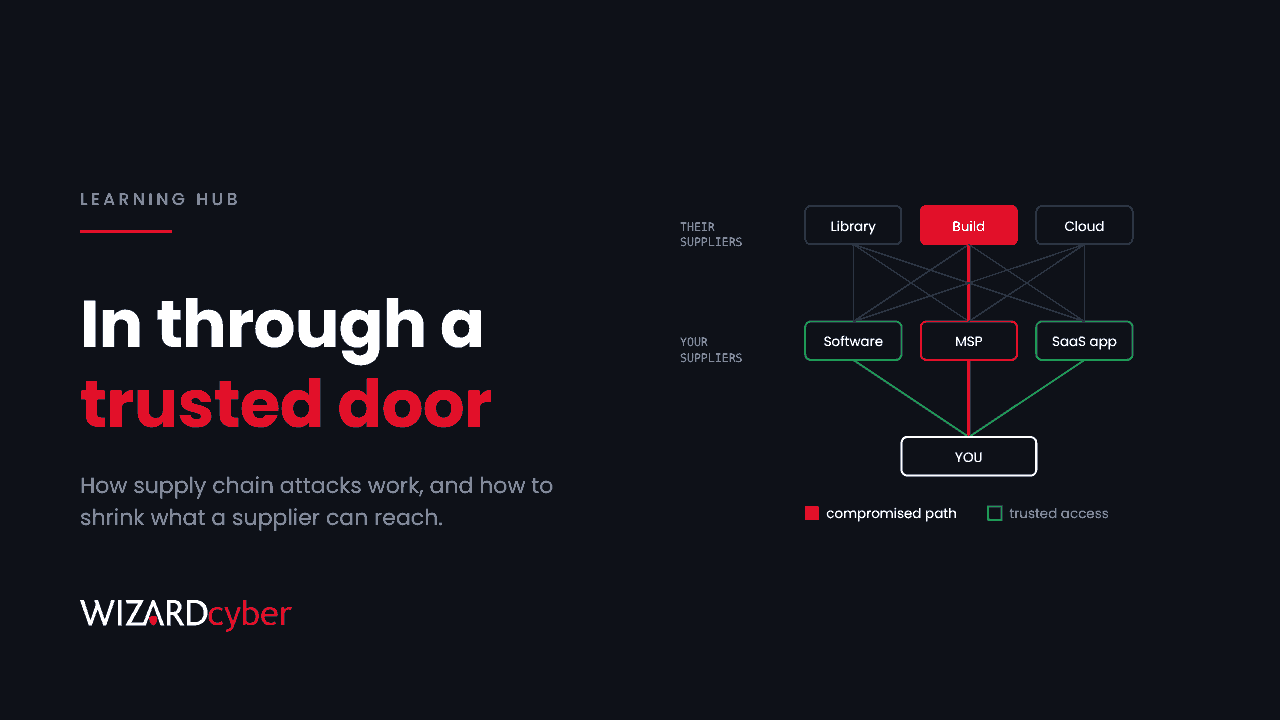
What Is A Supply Chain Attack? Types, Real Examples And How To Reduce Your Exposure
A supply chain attack reaches you through a supplier you trust. The main types, real examples, and the practical steps that reduce your exposure.
 Microsoft Security
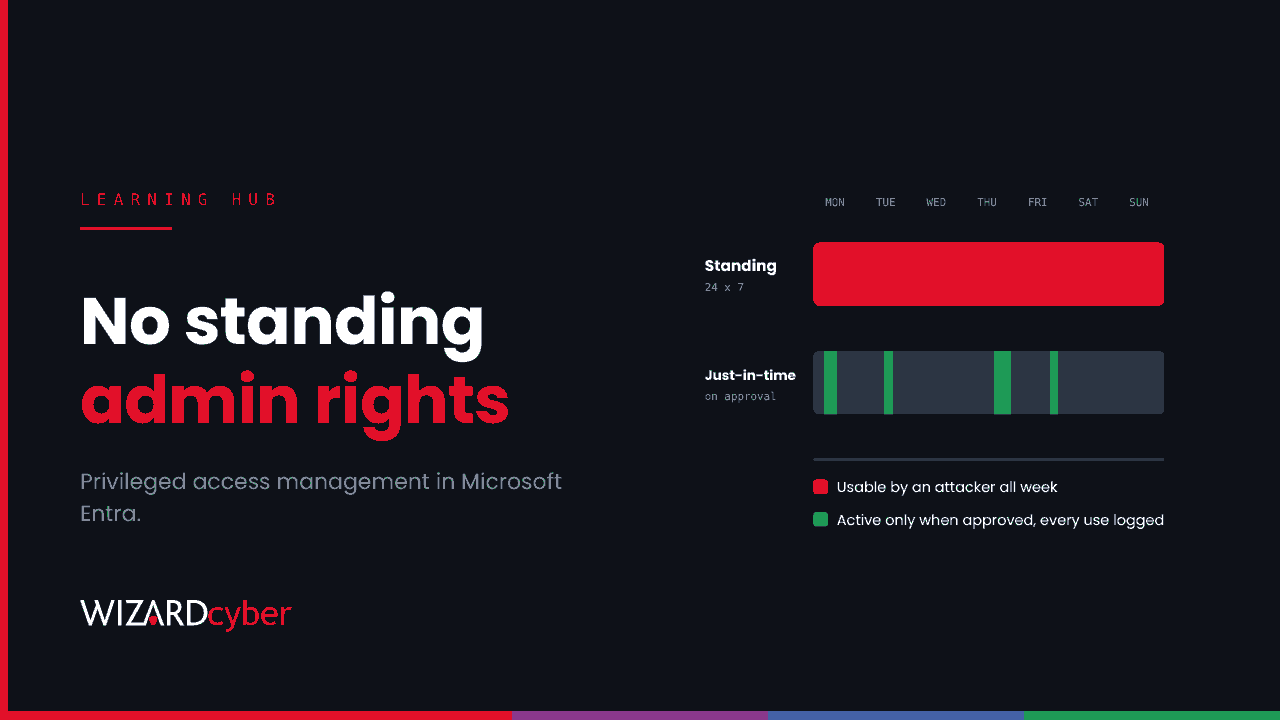
What Is Privileged Access Management (PAM)? How It Works In Microsoft Entra, And Where It Fails
Privileged access management controls who holds admin rights, when and how. How PAM works in Microsoft Entra with PIM, and where it usually fails.
 Microsoft Security
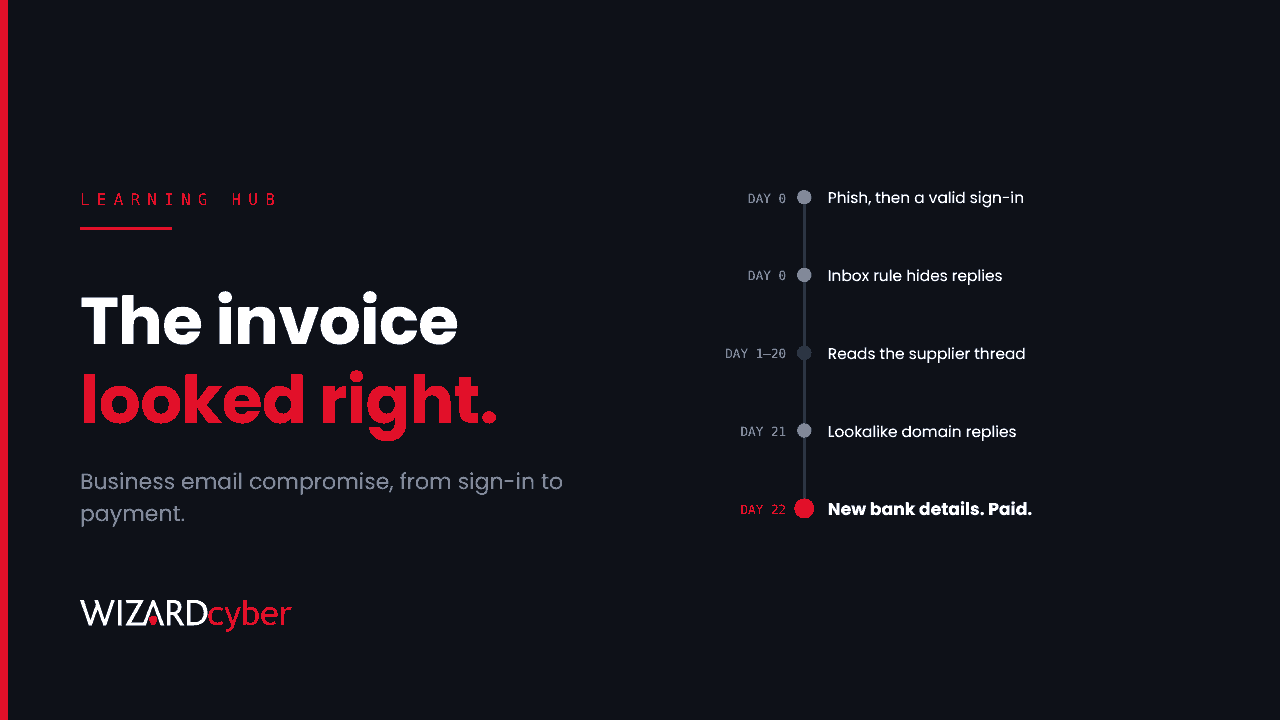
What Is Business Email Compromise (BEC)? How It Works And How To Stop It In Microsoft 365
Business email compromise uses a hijacked or spoofed mailbox to divert payments. How BEC works, the signs in Microsoft 365, and how to stop it.
 Microsoft Security
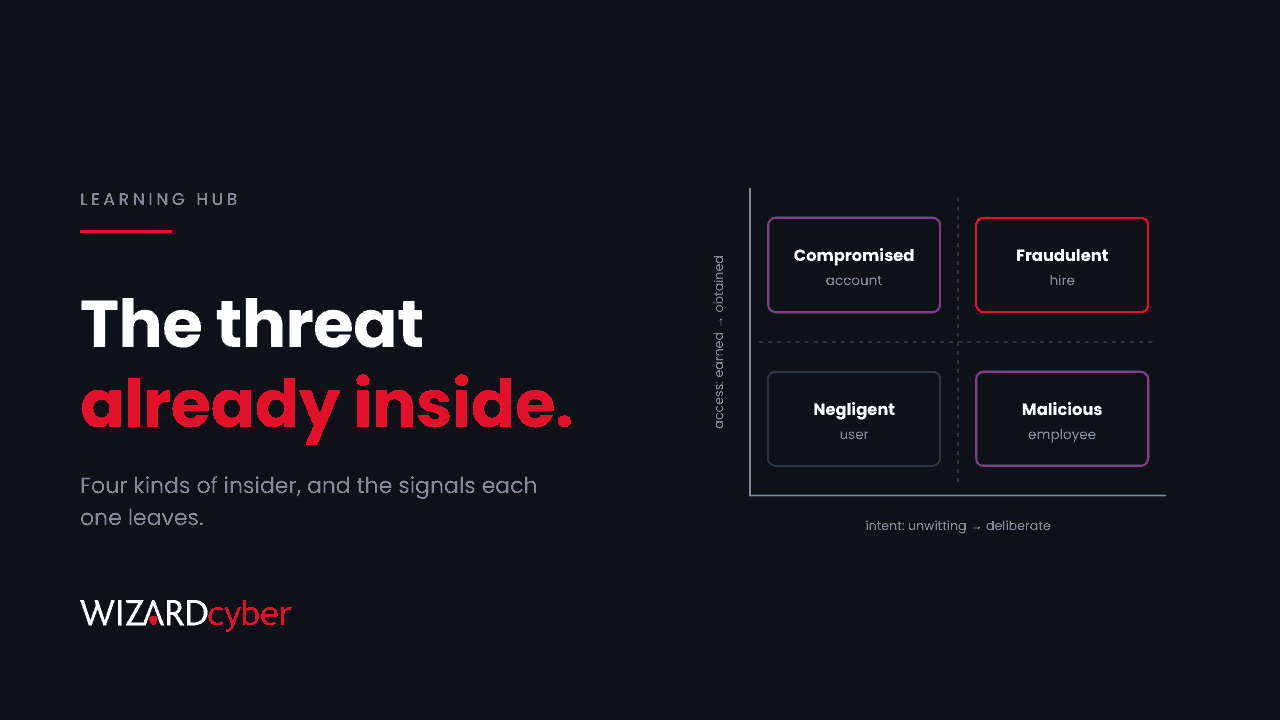
What Is An Insider Threat? Types, Warning Signs And How To Detect Them In Microsoft 365
An insider threat is harm caused through legitimate access. The four types, the warning signs, and how to detect insider risk in Microsoft 365.
 AI Driven Security Operations
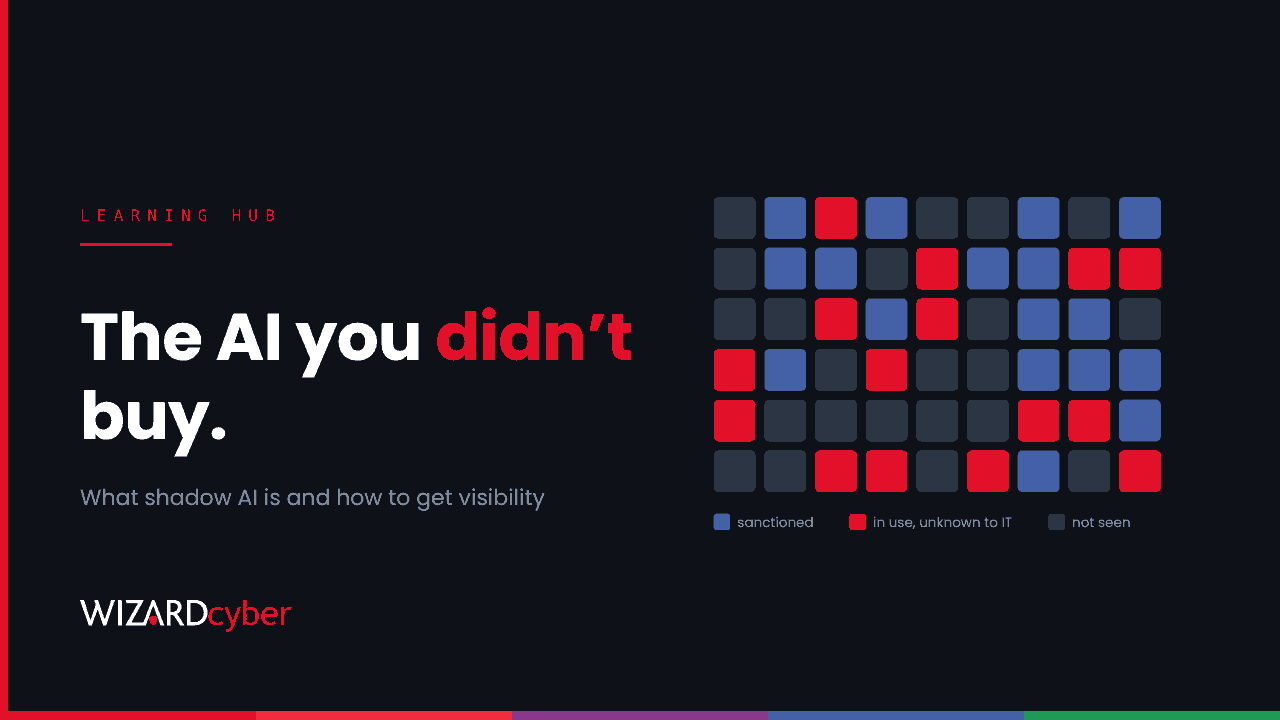
What Is Shadow AI? Risks, Examples And How To Get Visibility
Shadow AI is AI used at work without IT's knowledge or approval. The risks, common examples, and how to find and govern it in Microsoft 365.
 Microsoft Security
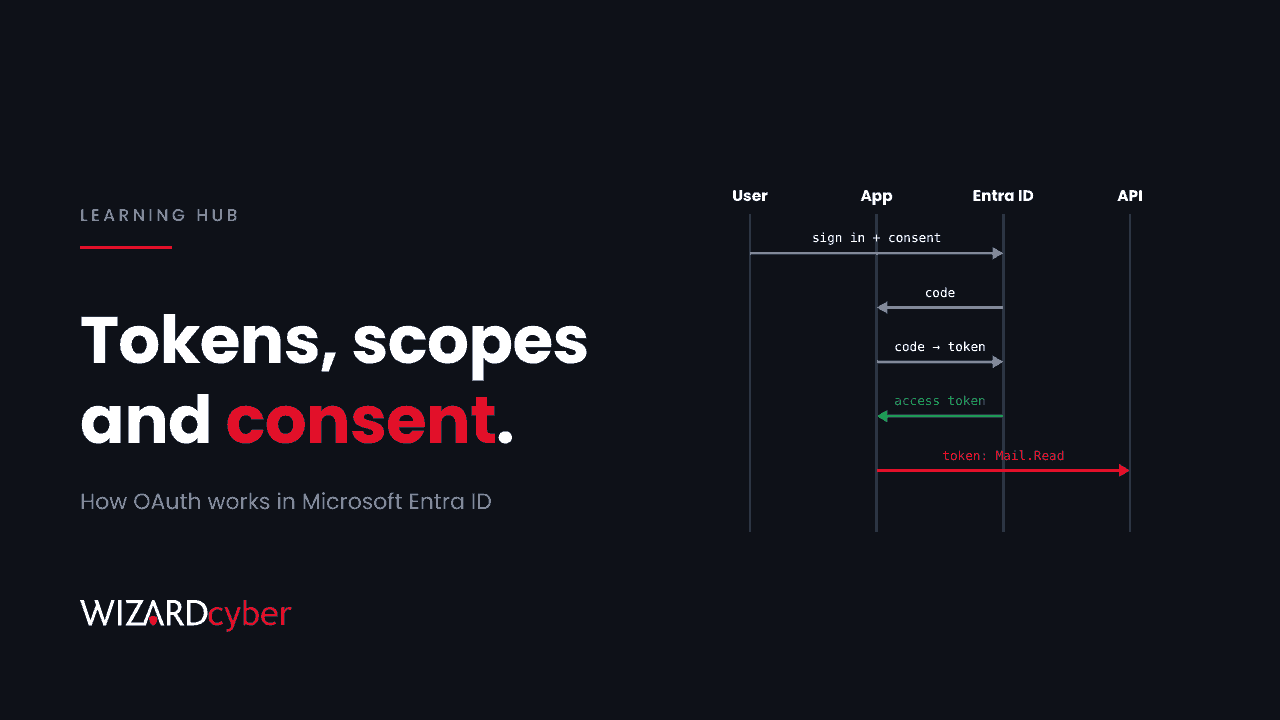
What Is OAuth? How It Works In Microsoft Entra ID, And How Attackers Abuse It
OAuth lets apps access data on your behalf without your password. How tokens, scopes and consent work in Entra ID, and how attackers abuse them.
 Microsoft Security
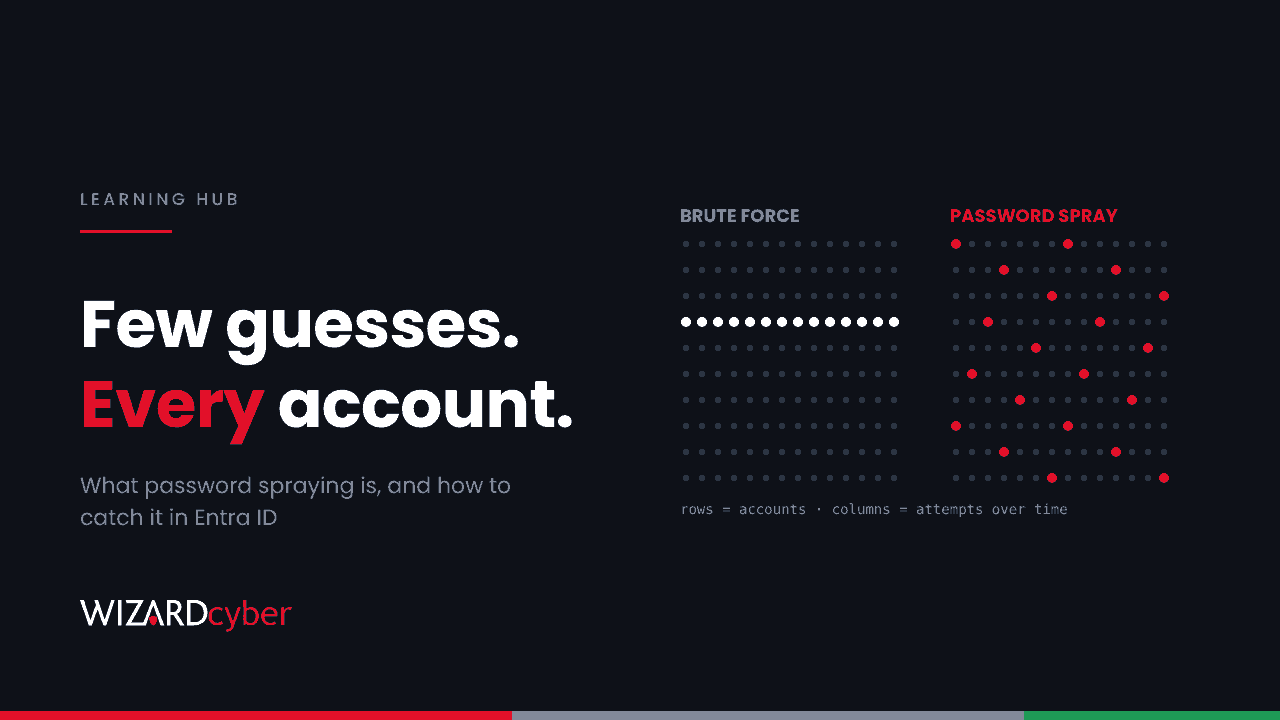
What Is Password Spraying? How It Works And How To Detect It In Microsoft Entra ID
Password spraying tries a few common passwords across many accounts to dodge lockouts. How it works, why MFA gaps matter and how to spot it in Entra ID.
Microsoft SecurityMicrosoft 365 E5 vs E7: What the New Tier Actually Adds
Microsoft 365 E7 sits above E5 and bundles Copilot, Agent 365 and the Entra Suite. What the step up actually contains, who it is for, and the question to ask before buying it.
 XDR
What Is Microsoft XDR? Defender and Sentinel Explained
What Microsoft XDR is, and how Defender and Sentinel work together to deliver unified detection and response across identities, endpoints, email and cloud.
 AI Driven Security Operations
What Is Context Memory In AI Security Operations?
Context memory lets AI security tools retain knowledge across sessions and incidents. See why it matters and how Microsoft implements it.
 Internet of Things
Passive Vs. Active IoT Monitoring: Why Non-Intrusive Matters In Operational Environments
Learn why passive IoT monitoring provides non-intrusive security visibility for OT environments without disrupting critical operations.
 AI Driven Security Operations
What Is AI-Augmented SOC?
Learn what an AI-augmented SOC is, how AI enhances analyst workflows, and why it matters for modern security operations.
 Internet of Things
How A Managed IoT SOC Works: Detection, Triage, And Response Explained
Learn how a managed IoT SOC provides 24/7 detection, specialist triage and operationally aware response for IoT environments.
 AI Driven Security Operations
Threat Hunting In The Age Of AI: Tools, Techniques, And Use Cases
Learn how AI threat hunting enhances security operations with continuous monitoring, behavioral analytics, and faster threat detection.
 AI Driven Security Operations
SecOps Automation: How AI Is Reshaping Security Operations Workflows
Discover how AI-powered SecOps automation streamlines security workflows, reduces analyst workload, and accelerates response.
 AI Driven Security Operations
Real-World Agentic AI Use Cases In Cybersecurity
Explore real-world agentic AI cybersecurity use cases, from autonomous triage to threat hunting and incident response.
 AI Driven Security Operations
Microsoft Copilot For Security: What It Is And How It Fits Into The AI SOC
Learn how Microsoft Copilot for Security helps SOC analysts investigate threats faster with AI-powered guidance and automation.
 Internet of Things
What Is IoT Security Monitoring And Why Does 24/7 Coverage Matter?
Learn why IoT security monitoring and 24/7 visibility are essential for detecting threats and protecting connected devices.
 AI Driven Security Operations
Multi-Agent Security Operations: How AI Agent Teams Are Transforming The SOC
Learn how multi-agent security operations use AI agent teams to improve SOC detection, investigation, and response.
 Internet of Things
BMS Vulnerabilities: How HVAC, Access Control, And Lighting Systems Get Hacked
Learn how attackers exploit BMS vulnerabilities in HVAC, access control, and lighting systems, and why these systems are targeted.
 AI Driven Security Operations
What Is A Managed AI SOC?
Learn what a Managed AI SOC is, how it differs from a traditional SOC, and why organizations adopt AI-driven managed security.
 AI Driven Security Operations
What Is Investigation Automation?
Learn how investigation automation accelerates incident response using AI to gather evidence, analyse threats, and reduce MTTR.
 AI Driven Security Operations
AI Analyst Assistants In The SOC: How AI Augments Human Security Teams
Discover how AI analyst assistants help SOC teams investigate faster, reduce workload, and improve security operations.
 AI Driven Security Operations
Microsoft Sentinel And AI: How Microsoft Is Bringing Artificial Intelligence To Security Operations
How Microsoft Sentinel uses AI for detection, investigation, and response, and what it means for modern security operations.
 AI Driven Security Operations
How To Build An AI SOC: A Practical Guide For Security Teams
A practical, step-by-step guide to building an AI SOC, from data foundations to agentic response and governance.
 AI Driven Security Operations
What Is Security Automation And Orchestration? SOAR Explained
A clear explanation of SOAR, how security orchestration and automation work, and why SOAR is essential in modern SOCs.
 AI Driven Security Operations
AI Agent Vs. Agentic System: What Is The Difference In Security Operations?
Learn the difference between AI agents and agentic systems, and why it matters for designing effective AI-driven security operations.
 AI Driven Security Operations
What Is An AI SOC Agent?
Learn what an AI SOC agent is, how it works, and how AI agents support triage, investigation, and response.
 AI Driven Security Operations
What Is Agentic Defense?
Learn what agentic defense is, how agentic AI autonomously stops attacks, and why it matters for modern SOCs.
 AI Driven Security Operations
What Is Automated Incident Response?
Learn what automated incident response is, how it works in modern SOCs, and how automation reduces response time and risk.
 AI Driven Security Operations
What Is Autonomous Threat Investigation?
Learn how autonomous threat investigation uses AI to gather evidence, reconstruct attacks, and accelerate SOC response.
 Incident Response
Why Incident Response Fails — And How To Fix It
Explore why incident response fails and how to fix process, ownership, and execution gaps before a real incident hits.
 AI Driven Security Operations
What Is Agentic AI In Cybersecurity?
Understand agentic AI in cybersecurity—how autonomous systems investigate threats, act dynamically, and augment SOC operations.
 AI Driven Security Operations
What Is AI-Powered Alert Triage?
Learn how AI-powered alert triage reduces false positives, prioritises real threats, and cuts SOC detection times.
 Microsoft Security
Microsoft Defender XDR Explained
Understand Microsoft Defender XDR and how it correlates identity, endpoint, email, and cloud signals into incidents for SOC response.
 AI Driven Security Operations
What Are SOC Tiers? How Security Operations Teams Are Structured
Learn how SOC tiers are structured, from Tier 1 alert triage to Tier 3 threat hunting, and how AI is reshaping SOC roles.
 AI Driven Security Operations
SOC Metrics That Matter In The Age Of AI: MTTD, MTTR, And How AI Is Improving Them
Understand key SOC metrics like MTTD and MTTR, and how AI reduces detection and response times while improving efficiency.
 AI Driven Security Operations
SOC Challenges: Why Traditional Security Operations Are Struggling To Keep Up
Explore the key challenges facing traditional SOCs, including alert overload, skills shortages, tool sprawl, and slow detection and response.
 AI Driven Security Operations
What Is AI Threat Detection?
AI threat detection uses behavioral analytics and machine learning to identify attacks that traditional tools miss. Learn why it matters.
 AI Driven Security Operations
What Is AI Detection Engineering?
Learn what AI detection engineering is and how it improves traditional threat detection, rule creation, and SOC coverage.
 AI Driven Security Operations
What Is AI Threat Hunting?
AI threat hunting uses machine learning and behavioral analysis to proactively find hidden threats that bypass detection tools.
 AI Driven Security Operations
What Is SOC Automation?
Learn what SOC automation is, how it reduces analyst workload, accelerates response, and improves security operations at scale.
 AI Driven Security Operations
What Is An AI-Powered SOC?
An AI-powered SOC embeds AI across detection, investigation, and response for faster, scalable security operations at scale.
 AI Driven Security Operations
What Is An Autonomous SOC?
An autonomous SOC uses AI to detect, investigate, and respond to security incidents with minimal human intervention.
 AI Driven Security Operations
What Is An AI SOC: AI In Modern Security Operations
Learn how AI transforms security operations by improving threat detection, investigations, and response without replacing analysts.
Incident Response
Incident Response Roles And Responsibilities Explained
Learn the key incident response roles, responsibilities, and decision authority needed for fast, coordinated response.
 Microsoft Security
How Microsoft Security Powers Modern Security Operations
Discover how Microsoft Security powers modern SOC operations with incident-based detection, automation, and unified response.
 Internet of Things
How Smart Buildings Work: From HVAC To Access Control Systems
Learn how smart buildings work, from HVAC and access control to BMS architecture and why it matters for security.
 XDR
Why Microsoft XDR Outperforms Point Security Tools
Learn why Microsoft XDR outperforms point security tools with unified detection, correlation, and coordinated response.
 Microsoft Security
Using Microsoft Security To Improve Cyber Resilience
Learn how Microsoft Security improves cyber resilience through early detection, rapid response, and coordinated recovery.
 Internet of Things
Lateral Movement In IoT Environments: How Attackers Pivot From IT To OT
How attackers use lateral movement to pivot from IT into IoT and OT environments, and why this threat is so difficult to detect.
 Incident Response
Incident Classification: Severity Levels And Response Prioritization
Learn how incident classification and severity levels help prioritize response and apply the right actions at the right time.
 Microsoft Security
 Vs Third-Party Tools: Do You Need Both?
Explore whether Microsoft Security alone is enough or when third-party tools add value, and how to build a balanced security stack.
 Internet of Things
IT/OT Convergence: Why Connecting Corporate And Operational Networks Creates New Risks
Learn how IT/OT convergence increases cyber risk, enables lateral movement, and what controls reduce exposure in connected networks safely.
 Microsoft Sentinel
Sentinel Data Connectors Explained: How Logs Flow Into Your SIEM
Understand how Microsoft Sentinel data connectors ingest, normalize, and stream logs into your SIEM to power detection and investigations.
 Internet of Things
Botnet Attacks And IoT: How Your Devices Can Be Weaponised
Learn how compromised IoT devices are recruited into botnets, the risks this creates, and how organizations can detect and prevent it.
 XDR
What Does XDR Actually Monitor? Endpoints, Identity, Cloud, And Network Explained
Learn what XDR monitors across endpoints, identity, email, cloud, and networks to detect modern multi-stage attacks.
 Microsoft Sentinel
Sentinel Detection Rules Explained: How Microsoft Sentinel Identifies Threats
Learn how Microsoft Sentinel detection rules use KQL, analytics, and ML to identify threats, reduce alert noise, and improve SOC visibility.
 Microsoft Security
Why Organizations Choose Managed Microsoft Security Services
Learn why organizations choose managed Microsoft Security services for 24/7 coverage, faster response, and predictable outcomes.
 Incident Response
How To Triage Security Incidents Effectively
Learn how effective incident triage helps validate threats, prioritize severity, and trigger the right response at the right time.
 Microsoft Security
Managed Microsoft Security: What Organizations Need To Know
Understand what managed Microsoft Security means, how it works, and when organizations choose it for 24/7 protection and faster response.
 Internet of Things
IoT Ransomware: How Attacks On Connected Devices Are Evolving
Learn how ransomware groups exploit IoT devices as entry points, pivot points, and targets to cause operational disruption.
 Internet of Things
Nation-State Threats Targeting IoT And Industrial Devices
Understand how nation-state actors target IoT and industrial devices and what this means for critical infrastructure security.
 Internet of Things
In-House Vs. Managed Security For Smart Buildings And BMS
Compare in-house and managed security models for smart buildings and BMS, including skills, cost, coverage, and operational trade-offs.
 Internet of Things
What A SOC Looks Like For OT, IoT, And Smart Building Environments
Learn how SOCs for OT, IoT, and smart buildings differ from IT SOCs, including monitoring tools, analyst skills, and response models.
 Microsoft Sentinel
What Is Microsoft Sentinel? Architecture, Detection, And Security Operations Explained
Learn what Microsoft Sentinel is, how its architecture works, and how it supports modern threat detection and security operations.
 Microsoft Sentinel
Sentinel Detection Rules Explained: How Microsoft Sentinel Identifies Threats
Learn how Microsoft Sentinel detection rules turn security telemetry into alerts, incidents, and actionable threat insights.
 Microsoft Sentinel
What Is Impossible Travel Detection In Microsoft Sentinel?
Learn how impossible travel detection works in Microsoft Sentinel, including how it identifies identity compromise and its limitations.
 Microsoft Sentinel
Sentinel Threat Hunting Techniques
Learn how threat hunting in Microsoft Sentinel helps security teams proactively uncover hidden threats beyond automated detections.
 Internet of Things
How Smart Building Threat Detection And Monitoring Works
How smart building threat detection and monitoring identifies abnormal behavior using passive, protocol-aware security monitoring.
 Internet of Things
Why Smart Building Security Requires 24/7 Monitoring
Why smart building security requires 24/7 monitoring to detect threats quickly and protect always-on building systems.
 Microsoft Sentinel
Best Practices For Sentinel SOC Monitoring
Best practices for SOC monitoring in Microsoft Sentinel, focusing on alert quality, triage consistency, automation, and response efficiency.
 Internet of Things
Why Traditional IT Security Fails In Smart Building Environments
Why IT security fails in smart buildings and what security teams must do to protect building automation systems securely.
 Internet of Things
Securing Smart Buildings: A Cybersecurity Framework For Facilities Teams
Framework to help facilities teams secure smart buildings, reduce cyber risk, and protect BMS, HVAC, and access systems.
 Internet of Things
OT And BMS Convergence: Why Your Building's Network Is A Security Blind Spot
OT and BMS convergence creates blind spots where building networks go unmonitored, exposing organizations to lateral movement risk.
 Internet of Things
What Is Smart Building Security? A Beginner's Guide
Smart building security protects building systems from cyber threats disrupting operations, safety, and business continuity.
 Internet of Things
IoT Vs. OT Vs. IT Security: What's The Difference?
Understand the key differences between IT, OT, and IoT security, and why each domain requires a different approach in practice.
 Internet of Things
What Is A Building Management System (BMS) And Why Does It Need Cybersecurity?
Learn what a Building Management System (BMS) is, how it works, and why BMS platforms are a growing cybersecurity risk.
 Internet of Things
Smart Building Security: The Cyber Risks Of Connected Facilities
Explore key cybersecurity risks in smart buildings, from IoT exposure to IT lateral movement, and how to secure connected facilities.
 Internet of Things
The IoT Attack Surface: How Many Devices Are Really At Risk?
Explore why the IoT attack surface is larger than most organizations realize and how unknown devices increase security risk.
 Internet of Things
Why IoT Devices Are A Prime Target For Cybercriminals
Learn why IoT devices are prime targets for cybercriminals, how attackers exploit them, and the risks this creates for businesses.
 Internet of Things
What Is IoT Security? A Beginner's Guide For Businesses
Learn what IoT security is, why it matters for businesses, and how to protect connected devices across IT, OT, and IoT environments.
 Internet of Things
The Most Common IoT Vulnerabilities And How Attackers Exploit Them
Explore the most common IoT vulnerabilities, how attackers exploit them, and the controls organizations use to reduce exposure.
 Microsoft Security
How Attackers Abuse Identity — And How Microsoft Security Detects It
Learn how attackers abuse identity and how Microsoft Security detects credential theft, token abuse, and privilege misuse early.
 Microsoft Security
Conditional Access, MFA, And Identity Protection Explained
Learn how Conditional Access, MFA, and Identity Protection secure access in Microsoft Entra with risk-based policy.
 Microsoft Security
Identity Is The New Perimeter: Why Microsoft Puts Identity First
Why identity is the new perimeter and how Microsoft Security protects access, detects abuse, and enables Zero Trust.
 Microsoft Security
Identity Threat Detection And Response (ITDR) With Microsoft Security
Learn how Microsoft Security delivers ITDR by correlating identity signals with endpoint, email, and cloud detection.
 Microsoft Security
What Is Microsoft Security? An Overview Of Microsoft’s Security Platform
An overview of Microsoft Security, its unified platform approach, and how it protects identities, endpoints, cloud, and data.
 Microsoft Security
 Explained: From Identity To Cloud To SOC
How Microsoft Security connects identity, endpoint, cloud, and SOC capabilities to detect threats across the full attack path.
 Microsoft Security
How Microsoft Security Supports A Zero Trust Architecture
How Microsoft Security applies Zero Trust principles across identity, access, devices, detection, and SOC operations.
 Microsoft Security
Microsoft Entra ID Security: Protecting Identities In A Cloud-First World
Discover how Microsoft Entra ID secures identities with MFA, Conditional Access, and real-time threat detection.
 Microsoft Security
Understanding The Microsoft Security Stack: A Unified Approach
Learn how the Microsoft Security stack unifies identity, endpoint, cloud, and SOC operations for coordinated detection and response.
 Incident Response
Common Incident Response Mistakes (and How To Avoid Them)
Learn the most common incident response mistakes and how to avoid delays, confusion, and increased business impact.
 Incident Response
 Vs SOC Vs XDR: How They Work Together
Learn how incident response, SOC operations, and XDR work together to detect, contain, and resolve security incidents.
 Incident Response
NIST Incident Response Framework: Phases, Roles, And Practical Guidance
Understand the NIST incident response framework, its four phases, roles, and how to apply it in modern security operations.
 Incident Response
How To Build An Effective Incident Response Plan
Learn how to create an incident response plan, define roles, and establish procedures for faster, consistent responses.
 Incident Response
What Is Incident Response? Process, Frameworks, And Best Practices
Learn what incident response is, why it matters, and how frameworks and best practices help contain and recover from attacks.
 Incident Response
What Is An Incident Response Policy And Why Every Organization Needs One
What an incident response policy is, how it differs from a response plan, and why it’s essential for governance and compliance.
 MXDR Security
What Is Managed XDR (MXDR) And Why Organizations Are Adopting It
What managed XDR is, how it differs from MDR and SOC-as-a-service, and the questions worth asking a provider before you sign anything.
 XDR
How XDR Reduces Mean Time To Detect (MTTD) And Respond (MTTR)
Learn how XDR helps reduce MTTD and MTTR by improving detection speed, investigation, and automated response
 XDR
How XDR Works: From Detection To Automated Response
Learn how XDR works across telemetry, detection, investigation, and automated response to stop modern cyberattacks faster.
 XDR
Why XDR Matters: Solving The Limitations Of SIEM And EDR
Discover why XDR matters and how it overcomes the detection and response limitations of traditional SIEM and EDR tools.
 XDR
What Is XDR (Extended Detection And Response)?
What XDR is, why the category exists, how it differs from EDR, SIEM and MDR, and what it costs to run once the licence is bought.
 Security Operations Center
4 Essential Security Operations Center Frameworks Every SOC Should Use
Explore the four core SOC frameworks—NIST CSF, MITRE ATTCK, Cyber Kill Chain, and Unified Kill Chain—and learn how they guide stronger detection, response, and security maturity.
 Security Operations Center
SOC As A Service: The Smarter Way To Secure Your Business
SOC as a Service delivers 24/7 threat monitoring, expert analysis, and fast response—without the cost and complexity of running your own SOC. Learn how managed SOC protects your business.
 Security Operations Center
In-House SOC Vs. Managed SOC — Which Is Right For You?
Find out whether an in-house SOC, a managed SOC, or a hybrid model is right for your organization. Compare costs, capabilities, and long-term benefits to make the best decision for your security strategy.
 Security Operations Center
How To Build A Modern SOC — People, Process, And Technology
Discover how modern SOCs combine people, process, and technology to deliver cloud-native, automated, and intelligence-driven protection across your entire environment.
 Security Operations Center
What Is A Security Operations Center (SOC)?
A Security Operations Center (SOC) is the hub for monitoring, detecting, and responding to cyber threats. Learn how SOCs work, their models, components, and why they are vital for modern security.
Nothing matches that.